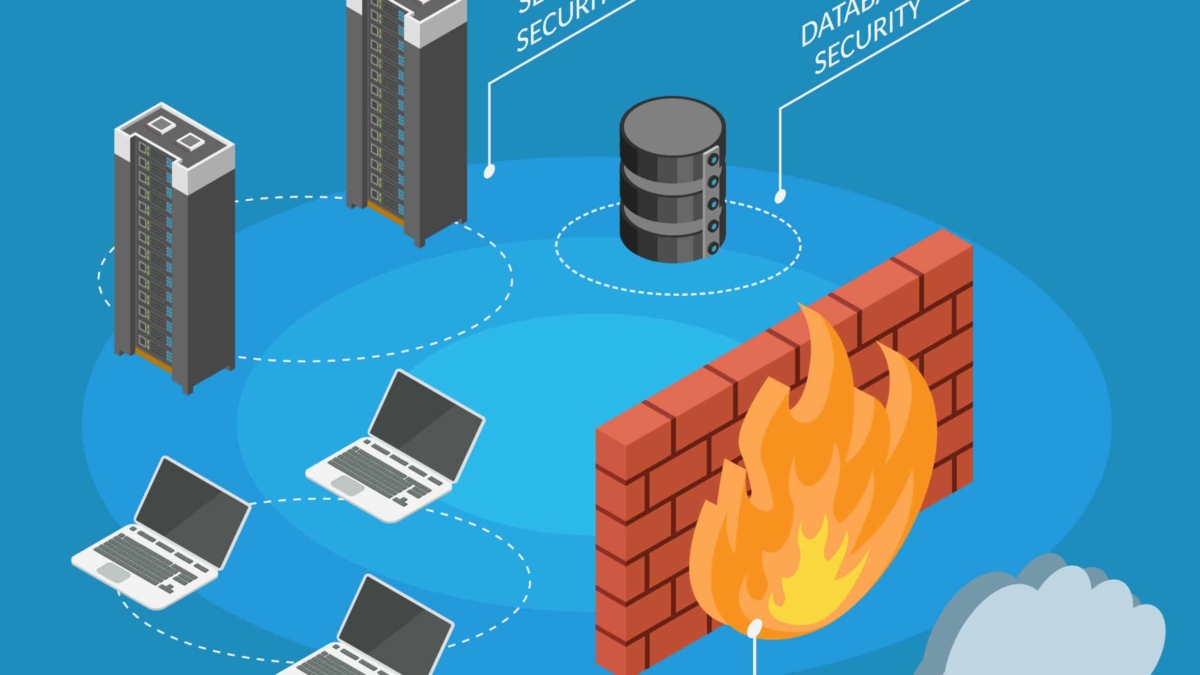
Enterprise Isometric Internet security firewall protection information

Network Security Components

ENGINEERING GUIDE · NETWORK SECURITY

Network Security Components — From Isolated Controls to an Integrated Security Fabric

Modern network security is not a single appliance or perimeter. It is a coordinated system of identity, access control, segmentation, inspection, endpoint protection, cloud controls, telemetry and response. The engineering challenge is understanding how these components work together to make — and validate — security decisions.

!
Engineering Observation A security component is only useful when we understand the decision it makes, the evidence it uses, where it is enforced, and how it connects to the rest of the architecture.
01 · IDENTITY

Establish Trust

Determine who or what is requesting access and establish the context required for a security decision.

02 · CONTROL

Enforce Policy

Apply authentication, authorization, ACLs, firewalls and segmentation to control permitted communication.

03 · INSPECT

Detect Threats

Inspect traffic, applications, endpoints and behaviour using IDS/IPS, NDR, WAF and endpoint controls.

04 · CORRELATE

Drive Response

Combine identity, network, endpoint and application telemetry so suspicious behaviour can be investigated and acted upon.

Security Decision Flow
IDENTITY
→
ACCESS
→
SEGMENT
→
INSPECT
→
PROTECT
→
OBSERVE
→
RESPOND
Engineering View

A security architecture is a decision system, not simply a collection of security appliances.

Identity Device Network Application Data Telemetry
Core Engineering Question

Can we prove that every security decision is intentional, visible and connected to the rest of the defence system?

Components Covered
Firewalls IDS / IPS NDR Identity NAC Segmentation EDR / XDR DLP VPN ZTNA SWG DNS Security CASB SIEM SOAR SASE
Interactive Security Architecture

Network Security Components

Security is not a single firewall. Modern protection combines identity, segmentation, inspection, endpoint controls and centralized intelligence. Select a layer to see its role in the security architecture.

Architecture Status
● DEFENDED
01
ID
Identity
Authentication, MFA and authorization
02
AC
Access Control
AAA, NAC and policy enforcement
03
FW
Firewall
Stateful inspection and filtering
04
SG
Segmentation
Macro and micro-segmentation
05
ID
IDS / IPS
Detection and threat prevention
06
EP
Endpoint
EDR, malware and workload security
07
SI
SIEM / SOAR
Correlation, visibility and response
Selected Component
Identity Security
Identity becomes the first security decision. Authentication verifies who or what is requesting access, while authorization determines what that identity is permitted to access.
MFA AAA Zero Trust Authorization
Security Mode
Protection Coverage 86%
Identity
OK
Firewall
ON
IDS
ON
SIEM
LIVE
Interactive Network Security Component

Firewall & Security Placement Explorer

Security controls work best when each layer protects a different part of the attack surface. Explore where firewalls, IDS/IPS, segmentation and application controls fit into a modern security architecture.
External
→
Perimeter
→
Internal
→
Workload
REQUEST
INSPECT
ENFORCE
WORKLOAD
FW
Firewall
Policy enforcement point

Controls traffic according to security policy and creates an enforcement boundary between trusted and untrusted zones.

Primary role Allow / deny traffic
Visibility Flows, sessions and policy
Placement Internet / internal boundary
Security value Defense in depth
SECURITY DECISION
A firewall should enforce the policy at the boundary where traffic crosses security zones.

Why placement matters

A single perimeter firewall cannot provide complete protection once an attacker reaches the internal network. Additional controls reduce lateral movement and protect individual workloads and applications.

MACRO

Protects larger network zones such as Internet, DMZ, user and server segments.

MICRO

Applies granular controls around individual workloads, applications or identities.

INTERACTIVE SECURITY ARCHITECTURE

How the Security Components Connect

Select an architectural layer to see the security decision it makes, the evidence it requires and the controls commonly deployed there.

ARCHITECTURE ACTIVE
Security Decision Chain · Select a Layer
LAYER 01 · TRUST

Identity Security

Identity establishes the context behind a connection. Modern security decisions increasingly consider the identity, device and session rather than relying only on network location.

Who is requesting access?
Identity, authentication state, device and session context
Authentication establishes identity; authorization determines what that identity may access.
MFA AAA RBAC ZTNA
Architecture Model
LAYERED
Primary Objective
CONTROL
Evidence Model
CORRELATED
SECTION 01 · DEFINE · TRUST BOUNDARY LAB

Map the Security Decision

A security architecture starts by understanding the relationship between the requester, the identity context, the destination and the boundary where policy is enforced. Change the variables and observe how the decision path changes.

Source
Identity Context
Destination
Boundary
Engineering Principle

Trust should be explicit. The network location alone should not automatically determine whether a request is safe.

01 · Source
Remote User Request origin
→
02 · Identity
Trusted Identity Authentication context
→
03 · Boundary
Identity-Aware Access Policy enforcement
→
04 · Destination
Internal Application Requested resource
Authenticated
Trusted posture
Application resource
Identity-aware enforcement
Low contextual risk
Least privilege
ALLOW
Identity, device and destination context provide sufficient evidence for the requested application access.
Decision Confidence 88%
16:00:01 [ARCH] Security decision engine initialised.
16:00:02 [AUTH] Identity context available.
16:00:03 [POLICY] Waiting for scenario evaluation.
ENGINEERING MODEL · NETWORK SECURITY

Security Is a System of Connected Decisions

Modern network security is not one firewall or one perimeter. It is a coordinated system in which identity, access, segmentation, inspection, protection and telemetry work together to control communication and reduce the attack surface.

01 · IDENTITY Establish Trust Understand who or what is requesting access and the context surrounding the request.
02 · CONTROL Enforce Policy Apply authentication, authorization, firewall and access policies at the appropriate boundary.
03 · INSPECT Understand Traffic Inspect network and application behaviour to identify unwanted or suspicious activity.
04 · CORRELATE Drive Response Combine security evidence so decisions can be investigated, explained and acted upon.
Identity
→
Access
→
Segmentation
→
Inspection
→
Protection
→
Telemetry
→
Response
01 · DEFINE · SECURITY ARCHITECTURE

Security Architecture & Trust Boundaries

Security begins by defining what is trusted, what is exposed, what is being accessed and where security decisions are enforced. The objective is not simply to deploy more controls, but to place the right control at the right point in the communication path.

A modern environment may contain users, endpoints, workloads, cloud services, branches and applications distributed across multiple networks. These systems cannot be protected effectively by treating the traditional Internet edge as the only security boundary.

Instead, security architecture creates a series of decision points. Identity establishes context, access controls determine whether communication should proceed, segmentation limits the reachable attack surface, and inspection and protection controls examine what happens after access has been permitted.

The security decision path

From request to protected workload
01 Identity Who is requesting?
→
02 Access What is permitted?
→
03 Segmentation Where can it go?
→
04 Inspection What is happening?
→
05 Protection What must be protected?
→
06 Telemetry What evidence exists?

Where are the trust boundaries?

A trust boundary is the point where the security assumptions about a connection, identity, device or workload change. The boundary may exist between the Internet and an organization, between a user and an application, between network segments or directly around an individual workload.

01 · EXPOSURE External Environment Internet users, remote systems, third-party services and other untrusted sources represent the outer attack surface.
02 · ACCESS Identity & Policy Authentication, authorization and contextual policy determine whether a request should receive access.
03 · ENFORCEMENT Security Boundary Firewalls, segmentation, access controls and inspection points enforce the architecture's security policy.
04 · ASSET Application & Data The final objective is protecting workloads, applications and data while preserving legitimate communication.

Four questions every architecture should answer

01
Who is requesting? Identify the user, device, workload or service and establish the relevant context.
02
What should be allowed? Determine which application, destination, service or resource the requester is permitted to access.
03
Where is it enforced? Place enforcement at an appropriate network, identity, workload or application boundary.
04
How do we know? Generate sufficient telemetry to explain the decision and investigate unexpected behaviour.
Engineering evidence
A security boundary must have a decision behind it

Simply placing a firewall, NAC system or segmentation control between two networks does not automatically create effective security. The architecture should identify what the boundary protects, what policy governs communication across it, what evidence supports the decision and what happens when the expected behaviour changes.

Security components form layers, not isolated products

Identity Layer
Establish context
Authentication, MFA, authorization and identity-aware policy establish who or what is requesting access.
Network Layer
Control reachability
Firewalls, ACLs, NAC and segmentation restrict which systems, networks and services can communicate.
Workload Layer
Protect the asset
Endpoint, application, workload and data controls provide protection closer to the resource being accessed.
Inspection Layer
Understand behaviour
IDS/IPS, NDR and application-aware inspection provide deeper visibility into traffic and behaviour.
Data Layer
Protect information
Encryption, DLP and application controls help protect sensitive data as it moves through the environment.
Intelligence Layer
Correlate evidence
Telemetry, SIEM and response workflows connect individual security signals into an operational picture.
Section 01 · Engineering Principle
A security architecture is a decision system, not a collection of appliances.

The strongest architectures make the security decision path explicit: identify the requester, understand the resource, determine the required level of trust, enforce policy at the appropriate boundary and generate evidence that allows the outcome to be verified. The remaining security components in this guide build on that foundation.

01 · DEFINE · SECURITY ARCHITECTURE

Security Architecture & Trust Boundaries

Step through a security decision from identity to enforcement and observe where trust is established, where policy is applied and where evidence is generated.
Ready
Live Security Decision Path
0 / 6
◉
USER
Identity
Request
◎
IDENTITY
Authentication
Trust
◇
ACCESS
Policy
Authorization
▣
WORKLOAD
Application
Data
Architecture principle: security is not one control. A request moves through multiple decision points where identity, context, policy and enforcement can each change the outcome.
Architecture Inspector
Click an architecture component to inspect its security responsibility.
Security Role
Current decision
Identity Unknown
Device trust Unknown
Authorization Pending
Enforcement Pending
Evidence None
Control Health
Live
IDENTITY
Authentication
READY
ACCESS
Authorization
READY
ENFORCEMENT
Policy control
READY
Decision Evidence
Live
Signal Value
Identity Pending
Device Pending
Policy Pending
Outcome Pending
Security Decision Timeline
Identity → enforcement
01
IDENTITY
User presents an identity to begin the access request.
02
AUTH
Authentication verifies whether the claimed identity can be trusted.
03
CONTEXT
Device and request context are evaluated before authorization.
04
POLICY
Authorization determines what the authenticated identity is permitted to access.
05
ENFORCE
A network, application or workload control enforces the decision.
06
EVIDENCE
Telemetry records the decision so it can be investigated later.
Architecture Telemetry
Live interpretation
Current Event
Press Step Forward to begin
Investigation Progress
Engineering takeaway: a security architecture should connect identity, policy, enforcement and telemetry rather than treating each control as an isolated product.
ENGINEERING MODEL · ACCESS CONTROL

Control Who Can Communicate With What

Access control turns security architecture into enforceable policy. Authentication establishes identity, authorization determines what that identity may access, and network controls enforce those decisions at appropriate boundaries.

01 · AUTHENTICATE Verify identity Establish that the user, device, workload or service is who it claims to be.
02 · AUTHORIZE Determine access Decide which resources, applications and services the requester is permitted to use.
03 · ENFORCE Apply policy Use ACLs, firewalls, NAC and other controls to enforce the security decision.
04 · ACCOUNT Record evidence Maintain useful audit and telemetry information so access decisions can be investigated later.
Identity
→
Policy
→
Firewall / ACL
→
Application
→
Audit
02 · CONTROL · ACCESS & FIREWALL ENFORCEMENT

Access Control & Firewall Enforcement

Once the security architecture defines its trust boundaries, the next requirement is enforcement. Access control determines who or what may communicate with a resource, while firewalls and related controls enforce that policy against actual network traffic.

This distinction is important. Authentication answers whether an identity has been established. Authorization answers what that identity is allowed to do. Enforcement is the point where the resulting policy is applied to a real connection, request or flow.

Effective access control therefore combines identity, context, policy and enforcement rather than relying on a single allow or deny rule.

From identity to enforcement

The access-control decision path
01 Identity User / Device / Workload
→
02 Authentication Establish identity
→
03 Authorization Determine permission
→
04 Enforcement Apply policy
→
05 Telemetry Record outcome

Authentication, authorization and accounting

AAA provides a useful conceptual model for access control. Authentication establishes identity, authorization determines permitted actions and accounting records relevant activity for auditing and investigation.

A · AUTHENTICATION
Who are you?
Credentials, certificates, MFA and other mechanisms can establish the identity of a user, device or service.
A · AUTHORIZATION
What can you do?
Policy determines which resources, applications, services or actions the authenticated identity is permitted to access.
A · ACCOUNTING
What happened?
Access and activity records provide evidence for auditing, troubleshooting and security investigation.

Where firewalls fit

Firewalls provide an enforcement point for network security policy. They can evaluate characteristics such as source and destination, protocol, ports, connection state and, depending on the platform, application or user context.

The important engineering question is not simply whether a firewall is present. It is whether the firewall is positioned where the required decision can actually be made and whether its policy matches the intended trust boundary.

Network enforcement
Packet & state policy
ACLs and stateful firewalls can control traffic according to addresses, protocols, ports and connection state.
Context-aware control
Identity & application
Modern platforms may combine network attributes with identity, application and other contextual information when enforcing policy.
Application boundary
WAF protection
A web application firewall focuses specifically on HTTP and HTTPS application-layer requests rather than acting as a general network firewall.

Good security policy is explicit

A well-designed policy should make its intent clear. The engineer should be able to identify the source, destination, service, identity or context where relevant, the expected action and the reason the communication is permitted.

01
Least privilege

Permit only the access required for the intended function. Broad connectivity should not become the default simply because it is operationally convenient.

02
Explicit policy

Rules should describe an intentional security requirement rather than becoming an accumulation of undocumented exceptions.

03
Context matters

Identity, device posture, application, location and risk can provide useful context beyond a simple source and destination address.

04
Evidence matters

Access decisions should generate sufficient telemetry to determine what was permitted, denied and why the decision occurred.

Engineering evidence
An allow rule is a security decision

Every permitted connection creates an exposure. The engineering task is therefore to understand why that connection is allowed, what boundary controls it, what identity or context is associated with it and how the resulting activity will be observed. Security policy should be explainable before it is deployed.

Access control becomes stronger when the layers agree

Identity should not have to operate independently from network policy. Authentication and authorization establish context, while firewalls, ACLs, NAC and segmentation provide enforcement. Endpoint and application controls add further protection closer to the resource.

This creates a layered model in which a single failure does not automatically provide unrestricted access to the rest of the environment. The architecture becomes progressively more difficult to bypass because different controls make different decisions at different points.

Section 02 · Engineering Principle
Authentication establishes identity. Authorization defines permission. Enforcement controls the communication.

Effective access control connects those three concepts with useful telemetry. The goal is not simply to create more rules, but to ensure that every important communication has an intentional policy, an appropriate enforcement point and enough evidence to explain the resulting decision.

02 · CONTROL · ACCESS & FIREWALL ENFORCEMENT

Access Control & Firewall Policy Builder

Build a security decision from identity, device context and destination. Step through the policy chain and see where authorization becomes enforcement.
Policy Ready
Live Policy Evaluation
0 / 6
Identity
Who is requesting access?
Device Trust
Can the endpoint be trusted?
Destination
What is being accessed?
◉
IDENTITY
Authentication
◇
CONTEXT
Device / Risk
▤
POLICY
Authorization
◈
FIREWALL
ACL / State
PENDING
Waiting for policy evaluation
Configure the request and press Step Forward.
Decision Inspector
Live
Identity Pending
Authentication Pending
Device Pending
Destination Pending
Decision Pending
Control Stack
Security enforcement
AAA / Identity
READY
Authentication verifies the security principal.
Authorization
READY
Identity and context are evaluated against policy.
Firewall / ACL
READY
The resulting decision is enforced on traffic.
Policy Evaluation Timeline
Identity → enforcement
01
IDENTITY
The request arrives with a claimed identity.
02
AUTH
Authentication verifies the identity.
03
CONTEXT
Device posture and destination are evaluated.
04
POLICY
Authorization calculates permit or deny.
05
FIREWALL
Firewall or ACL enforcement applies the decision.
06
OUTCOME
Access is either permitted or blocked.
Policy Telemetry
Live interpretation
Current Event
Configure a request and press Step Forward
Evaluation Progress
Engineering takeaway: authentication establishes identity; authorization determines permission; enforcement makes that decision real.
ENGINEERING MODEL · NETWORK SEGMENTATION

Contain the Attack Surface

Segmentation limits how far a user, device, workload or compromised system can communicate. Instead of treating the network as one trusted space, security boundaries divide it into controlled zones with explicit communication requirements.

01 · DEFINE Create zones Group systems according to function, trust level, sensitivity or business requirement.
02 · LIMIT Reduce reachability Prevent systems from communicating simply because they share network connectivity.
03 · CONTROL Permit required flows Define which applications, services and workloads are allowed to communicate across boundaries.
04 · CONTAIN Limit compromise A compromised system should have limited paths to other sensitive resources.
User Zone
→
Application Zone
→
Data Zone
→
Management Zone
03 · SEGMENT · CONTAIN THE ATTACK SURFACE

Network Segmentation & Workload Boundaries

Access control determines whether communication is permitted. Segmentation determines how much of the environment a system can reach in the first place. By creating explicit boundaries between systems with different trust, sensitivity or operational roles, the potential impact of a compromise can be reduced.

A flat network creates unnecessary reachability. If every endpoint, server and workload can communicate freely with every other system, a compromised device may have many possible paths toward more valuable resources.

Segmentation changes that model by introducing controlled boundaries. Communication between zones becomes intentional rather than an automatic consequence of network connectivity.

The segmentation model

Controlled communication between security zones
01 · USER User / Endpoint Zone Workstations, managed devices and user-facing systems that require controlled access to applications.
→
02 · APPLICATION Application Zone Business applications and services exposed only through the communication paths they actually require.
→
03 · DATA Data / Sensitive Zone Databases and sensitive resources protected behind additional policy and tightly controlled access paths.

Macro-segmentation and micro-segmentation

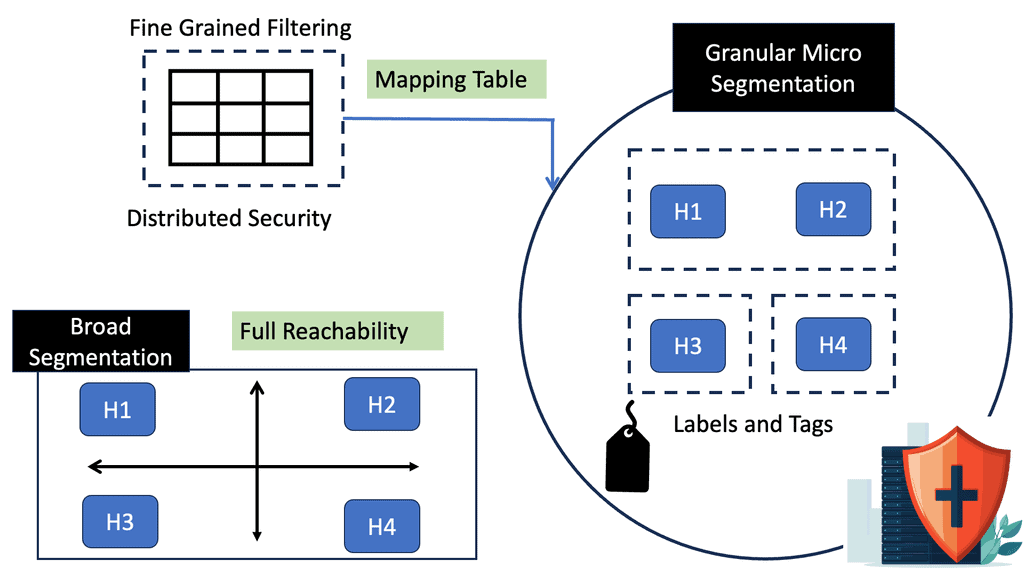
Segmentation can operate at different levels. Macro-segmentation creates larger security zones such as user, server, management and data networks. Micro-segmentation applies more granular policy around individual workloads, applications or groups of systems.

Macro-segmentation
Separate major trust zones
Large security boundaries provide a straightforward way to separate environments according to function, sensitivity or trust.
Example: User → Server → Database → Management
Micro-segmentation
Control workload-to-workload access
More granular controls can restrict communication between individual workloads or application tiers even when those workloads share an underlying network or cluster.
Example: Web Tier → API Tier → Database Tier

East-west traffic matters

Traditional perimeter security focuses heavily on north-south traffic entering or leaving an environment. Modern workloads also generate large amounts of east-west traffic between systems inside the environment.

If internal communication is implicitly trusted, an attacker who gains access to one workload may be able to move laterally toward other systems. Segmentation introduces additional policy decisions into this internal communication path.

Example workload boundary model
Tier 01 Web Front End Public-facing application component with controlled downstream access.
Tier 02 Application API Business logic reachable only from explicitly permitted application sources.
Tier 03 Database Sensitive data service with narrowly defined application access.
Tier 04 Management Administrative systems isolated from normal application traffic.

Segmentation requires explicit policy

01 · SOURCE Who initiates? Identify the system, workload, user or service generating the communication.
02 · DESTINATION What is reached? Determine which zone, workload, application or data resource is being accessed.
03 · SERVICE What is required? Define the protocol, port, application or service that actually needs to communicate.
04 · DECISION Should it cross? Permit only the communication required by the application's intended architecture.

Designing useful boundaries

01
Separate by sensitivity

Systems holding more sensitive information should not automatically inherit the same connectivity as ordinary workloads.

02
Separate by function

User, application, database and management systems often have different communication requirements and should be treated accordingly.

03
Minimise lateral paths

Restrict unnecessary east-west communication so compromise of one system does not automatically expose neighbouring workloads.

04
Make exceptions visible

Required cross-zone communication should be documented, intentional and observable rather than hidden inside broad connectivity rules.

Engineering evidence
Segmentation reduces reachability — it does not replace inspection

A segmentation boundary limits where traffic can travel, but it does not automatically determine whether permitted traffic is malicious. Segmentation therefore works alongside firewalls, identity controls, inspection and endpoint protection rather than replacing them.

Section 03 · Engineering Principle
Containment begins by controlling reachability.

A well-segmented environment assumes that connectivity should be intentional. Macro-segmentation establishes major trust boundaries, while micro-segmentation can provide more granular workload controls. Together they reduce unnecessary lateral paths and limit the potential impact of a compromised system.

ENGINEERING MODEL · THREAT INSPECTION

Inspect the Traffic That Crosses Your Boundaries

Segmentation controls where traffic can travel. Inspection determines what that traffic is doing. Modern security architectures combine prevention, detection, behavioural analysis and application-aware controls at appropriate points in the traffic path.

01 · FILTER Enforce policy Firewalls determine whether traffic matches an explicitly permitted communication policy.
02 · DETECT Identify threats IDS and NDR analyse traffic and behaviour for indicators of malicious or abnormal activity.
03 · PREVENT Block activity IPS can actively prevent traffic when configured detection and policy conditions are met.
04 · PROTECT Inspect applications WAF controls HTTP and HTTPS application traffic using application context rather than treating all traffic as generic packets.
Traffic
→
Policy
→
Detection
→
Prevention
→
Evidence
03 · SEGMENT · CONTAIN THE ATTACK SURFACE

Network Segmentation Investigation Lab

Follow a communication attempt across identity, access and workload boundaries. Change the segmentation policy and observe where the traffic is allowed or stopped.

SCENARIO Employee → Application
SEGMENTATION ENFORCED
STEP 0 / 6
LIVE SEGMENTATION TOPOLOGY Waiting for traffic
USER / ACCESS ZONE
WORKLOAD ZONE
USER
Employee
Trusted device
NAC
Identity + posture
SEGMENT
Policy enforced
WORKLOAD
Application zone
Traffic path: waiting for inspection
EVENT TIMELINE 0 events
ENGINEERING EVIDENCE LIVE READOUT
Current Event No event processed.
Security Principle Segmentation limits unnecessary communication paths.
Investigation Finding No finding yet.
04 · INSPECT · DETECT & PREVENT THREATS

Threat Inspection: IDS, IPS, NDR & WAF

Network inspection adds another layer of security between connectivity and trust. A firewall can enforce whether communication is permitted, while detection and prevention technologies examine permitted traffic for indicators of attack, abnormal behaviour or application-level exploitation.

These controls perform different jobs. IDS primarily detects and alerts. IPS can actively block or prevent traffic when its detection and policy conditions are met. NDR focuses on network behaviour and communication patterns, while a WAF is designed specifically to protect web applications at the HTTP and HTTPS application layer.

The inspection pipeline

From connectivity to security evidence
01 · FLOW Traffic arrives A user, workload or external system initiates communication toward a permitted destination.
→
02 · POLICY Firewall decision Network policy determines whether the communication should be allowed, denied or otherwise handled.
→
03 · DETECT Threat analysis IDS, IPS or NDR can evaluate traffic, protocols and behavioural indicators.
→
04 · EVIDENCE Record the signal Alerts, flow records and other telemetry provide evidence for investigation and correlation.

Detection is not the same as prevention

IDS · Detect
Identify suspicious activity
An intrusion detection system analyses traffic or events and generates alerts when configured indicators or behavioural conditions are observed.
IPS · Prevent
Act on detected threats
An intrusion prevention system can take an enforcement action against traffic when a detection matches configured prevention policy.
NDR · Behaviour
Understand communication patterns
Network detection and response looks for suspicious communication behaviour and relationships across network activity rather than relying only on individual signatures.

Where the inspection technologies fit

IDS
Intrusion Detection

Useful when visibility and alerting are required without the inspection system directly blocking the traffic path.

IPS
Intrusion Prevention

Adds an enforcement capability where detected traffic can be blocked or otherwise prevented according to policy.

NDR
Network Detection & Response

Builds a broader view of network behaviour, helping analysts identify unusual relationships, lateral movement and anomalous communication.

WAF
Web Application Firewall

Applies application-layer controls to HTTP and HTTPS traffic, protecting web applications from classes of application attacks.

Application-layer inspection

Network controls and application controls operate at different levels. A firewall may determine whether a connection between two systems is permitted, while a WAF can inspect the HTTP request itself and apply application-specific security rules.

Client Browser or application initiating the HTTP(S) request.
Web Application Firewall Inspects application-layer requests and applies web security policy before forwarding permitted traffic.
Application Web service receiving the request after policy evaluation.

Engineering inspection principles

01 · VISIBILITY Inspect the right traffic Place controls where meaningful traffic can be observed without creating unnecessary blind spots.
02 · CONTEXT Use more than packets Useful detection can combine addresses, ports, protocols, identities, application context and behavioural patterns.
03 · ACTION Match response to confidence Detection, alerting and blocking should be aligned with the confidence of the finding and the operational risk.
04 · EVIDENCE Preserve the signal Inspection becomes more valuable when its alerts and telemetry can be correlated with identity, endpoint and other security evidence.
Engineering evidence
Inspection only works when the traffic and context are visible

A security control cannot reliably detect what it cannot observe. Encrypted traffic, distributed workloads, cloud services and changing application architectures therefore make visibility, telemetry and appropriate inspection placement critical parts of the design.

Section 04 · Engineering Principle
Allowing traffic does not mean trusting it.

Firewalls control communication policy, IDS provides detection, IPS adds prevention, NDR analyses network behaviour and WAF protects application-layer traffic. Used together, these controls provide multiple inspection points between connectivity and the final security decision.

04 · INSPECT · DETECT & PREVENT THREATS

Threat Inspection Pipeline

Follow a traffic flow through multiple security inspection layers. Each control answers a different question: can the traffic pass, does it contain a known threat, does its behaviour look suspicious, and is the application request safe?

TRAFFIC Web Request
INSPECTION READY
STAGE 0 / 6
LIVE INSPECTION PIPELINE Waiting for traffic
SOURCE
User / Device
FIREWALL
Policy / State
IDS / IPS
Threat signatures
NDR
Behaviour
WAF
HTTP / App
Traffic path: waiting for inspection
INSPECTION TIMELINE 0 events
ENGINEERING EVIDENCE LIVE READOUT
Current Event No inspection event processed.
Control Function Waiting for traffic.
Investigation Finding No threat finding yet.
ENGINEERING MODEL · ENDPOINT & DATA PROTECTION

Protect the Endpoint and the Data It Handles

Network controls cannot provide complete protection once a workload, endpoint or application becomes the target. Security therefore extends to the systems themselves, the data they process and the cryptographic controls protecting information in transit and at rest.

01 · ENDPOINT Protect the device EPP and EDR provide prevention, detection and investigation capabilities directly on endpoints and workloads.
02 · DATA Control sensitive information DLP and data-aware policies help reduce inappropriate movement or exposure of sensitive information.
03 · TRANSIT Encrypt communication TLS, VPNs and other cryptographic mechanisms protect information while it moves between systems.
04 · ASSURE Validate posture Security controls should provide evidence that endpoints and data protections remain appropriately configured.
Endpoint
→
Application
→
Data
→
Encryption
→
Evidence
05 · PROTECT · ENDPOINTS, DATA & ENCRYPTION

Endpoint, Data & Encryption Protection

Network security does not end at the network boundary. The endpoint executes the workload, the application processes the information and the data itself may remain valuable even when network controls are operating correctly. Protection therefore needs to extend across the systems and information being defended.

Endpoint protection provides controls close to the workload. EPP can provide preventative protection, while EDR provides telemetry and investigation capabilities for suspicious endpoint activity. XDR can extend correlation across multiple security domains where supported.

Data protection adds another perspective. DLP can help identify and control inappropriate movement of sensitive information, while encryption protects information from unauthorised disclosure when data is stored or transmitted.

The protection stack

Protection follows the workload and the information
01 · DEVICE Endpoint Establish a security control point close to the system executing the workload.
→
02 · APPLICATION Process Monitor application and process activity that may indicate compromise or misuse.
→
03 · DATA Information Apply appropriate controls to sensitive information regardless of where the data is processed.
→
04 · EVIDENCE Telemetry Feed endpoint and data security signals into wider investigation and correlation workflows.

Endpoint protection is a local security boundary

EPP · Endpoint Protection Platform
Prevent common endpoint threats
Endpoint protection can provide preventative controls against malware and other known threats, alongside additional host security capabilities.
Prevention happens close to the workload rather than relying entirely on network inspection.
EDR · Endpoint Detection & Response
Investigate what the endpoint is doing
EDR collects endpoint telemetry that can help security teams investigate processes, files, connections and other indicators of suspicious activity.
Detection becomes more useful when endpoint evidence can be correlated with network and identity signals.

Endpoint controls should produce evidence

01 · POSTURE Is the device protected? Security status, configuration and protection state provide useful context for access decisions.
02 · PROCESS What is executing? Process activity can reveal behaviour that is invisible from network addresses alone.
03 · CONNECTION Where is it communicating? Endpoint connection telemetry can be correlated with network and application activity.
04 · RESPONSE Can it be contained? Security operations may need to isolate or otherwise contain a compromised endpoint.

Encryption protects information in transit

Encryption changes the security properties of communication by making captured traffic substantially less useful to an unauthorised observer. TLS is commonly used to protect application sessions, while VPN technologies can create encrypted tunnels across otherwise untrusted networks.

Simplified encrypted communication model
Source Application or endpoint generating the protected information.
→
TLS / VPN Protection Cryptographic protection is applied to the communication path according to the protocol and architecture being used.
→
Destination Intended application or endpoint receives the protected session.

Encryption is not the same as access control. A correctly encrypted connection can still be made by an unauthorised identity if authentication and authorization controls are weak. Encryption protects the information in transit; identity and policy determine who should be allowed to access it.

Protecting sensitive data

CLASSIFY Know what matters Security policy becomes more useful when sensitive information can be identified and assigned appropriate handling requirements.
CONTROL Limit movement DLP and access controls can help prevent sensitive information from being transferred through inappropriate channels.
PROTECT Use encryption Encryption can protect information during transport and, where implemented, while stored.
Engineering evidence
Security must follow the data, not just the network

Modern applications move across endpoints, data centres, cloud platforms and remote access environments. A security architecture that protects only the network path can therefore miss activity occurring directly on the endpoint or around the data itself.

Section 05 · Engineering Principle
Protect the system, the information and the communication between them.

Endpoint security provides local protection and telemetry. DLP helps control sensitive information, while encryption protects data during transport and storage when appropriately implemented. Together these controls extend the security architecture beyond the network boundary and closer to the actual workload and data.

05 · PROTECT · ENDPOINTS, DATA & ENCRYPTION

Endpoint & Data Protection Console

Security does not stop at the network boundary. Follow an endpoint and the data it handles through device posture, process activity, data protection, encryption and security evidence.

ASSET Managed Endpoint
PROTECTION READY
STAGE 0 / 6
PROTECTION STACK Waiting for asset
01 · ENDPOINT POSTURE
Device state, patching, security controls
READY
02 · PROCESS CONTROL
Process behaviour and endpoint detection
READY
03 · DATA PROTECTION
Classification, access and DLP controls
READY
04 · ENCRYPTION
TLS / VPN protection for data in transit
READY
05 · SECURITY EVIDENCE
Logs, telemetry and response context
READY
PROTECTION TIMELINE 0 events
ENGINEERING EVIDENCE LIVE READOUT
Current Control No control evaluated.
Security Function Waiting for the protection workflow.
Investigation Finding No finding yet.
ENGINEERING MODEL · CLOUD & REMOTE ACCESS

Secure Access Across a Distributed Environment

Users, applications and workloads increasingly connect from locations outside the traditional enterprise perimeter. Secure access therefore needs to combine identity, device context, encrypted connectivity and application-aware security controls.

01 · IDENTITY Verify the user Authentication establishes who is requesting access before a protected service is exposed.
02 · ACCESS Reach the application ZTNA and other access controls can restrict users to the applications they are authorised to use.
03 · PROTECT Secure the session VPN, TLS, SWG and DNS security provide protection around remote communication and internet access.
04 · CORRELATE Keep the evidence Access and security events should feed broader monitoring and investigation workflows.
User / Workload
→
Identity
→
Access Policy
→
Cloud / App
→
Telemetry
06 · CONNECT · SECURE CLOUD & REMOTE ACCESS

Secure Cloud, Internet & Remote Access

The traditional enterprise perimeter becomes less useful when users work remotely, applications move into cloud platforms and services are consumed directly from the internet. Security controls therefore need to follow the identity, device and application rather than assuming that everything important exists behind one physical firewall.

VPN remains useful when an encrypted tunnel to a private network is the appropriate access model. Zero Trust Network Access takes a different approach by providing identity- and application-aware access without necessarily placing the user onto the entire network.

The secure access journey

Identity and policy follow the connection
01 · REQUEST User or workload A user, endpoint or workload requests access to an internal, cloud-hosted or internet service.
→
02 · IDENTITY Verify context Authentication and policy establish whether the requesting identity should receive access.
→
03 · CONTROL Apply access policy ZTNA, VPN or other controls determine the permitted connectivity model.
→
04 · SERVICE Reach the application Access is provided to the intended service rather than assuming unrestricted network trust.

VPN and ZTNA solve different access problems

VPN · Encrypted Network Connectivity
Create a protected tunnel
A VPN can provide encrypted connectivity across an untrusted network and, depending on its design, provide access to a private network or defined network resources.
Typical model: Remote user → VPN tunnel → Private network
ZTNA · Application-Aware Access
Connect the user to the service
ZTNA can use identity and contextual policy to provide access to authorised applications without necessarily exposing the underlying network to the user.
Typical model: User → Identity Policy → Application

Cloud security is a collection of control functions

Cloud and internet security is rarely one product. Different control functions address different parts of the access path, including web traffic, DNS resolution, SaaS usage and identity-aware application access.

01 · SWG Secure Web Gateway Applies security policy to web access and can provide inspection, filtering and visibility for internet-bound traffic.
02 · DNS DNS Security Uses DNS requests as a policy and detection point, including blocking known malicious or inappropriate destinations where configured.
03 · CASB Cloud Access Security Broker Provides visibility and policy controls around the use of cloud applications and services.
04 · SASE Distributed Security Model SASE combines networking and security functions as a cloud-delivered architectural model for distributed users and locations.

Choosing the control point

Scenario
Primary question
Useful control
Security focus
Remote private access
Should this user reach the private environment?
VPN / ZTNA
Identity + access policy
Internet browsing
Should this destination be reachable?
SWG / DNS security
Web + destination policy
SaaS usage
How is the cloud service being used?
CASB
Application + data policy
Distributed workforce
Where should security policy execute?
SASE functions
Distributed enforcement

SASE as an architectural model

User / Branch Distributed users, branch locations and devices generating network requests.
SASE Security Functions Networking and security capabilities delivered closer to distributed users and applications, according to the architecture.
Cloud / Internet SaaS, public cloud and internet applications accessed through the controlled service path.

Secure access principles

01 · IDENTITY Start with the requester Access decisions should establish who or what is requesting the service before assuming trust.
02 · APPLICATION Expose what is required Where possible, access should be scoped to the application or service rather than unnecessarily exposing an entire network.
03 · CONTEXT Use more than credentials Device state, location, risk and other contextual signals can improve the quality of an access decision.
04 · TELEMETRY Record the decision Authentication, access and security events should remain available for monitoring and investigation.
Engineering evidence
The perimeter has moved closer to the user and application

Distributed applications and remote users do not eliminate network security. They change where security decisions need to occur. Identity, device context, application policy, web controls and cloud-delivered enforcement increasingly operate alongside traditional network boundaries.

Section 06 · Engineering Principle
Secure access should follow the user, device and application.

VPN provides an important encrypted connectivity model, while ZTNA can provide more granular application-aware access. SWG, DNS security, CASB and SASE extend policy into internet and cloud environments. Together, these controls adapt the security architecture to a distributed environment rather than relying on a single fixed perimeter.

06 · CONNECT · CLOUD & REMOTE ACCESS

Secure Cloud & Remote Access Journey

Follow a user or device from the initial access request through identity verification, device context, access policy, security services, application access and telemetry.

ACTOR Employee
ACCESS PENDING
STAGE 0 / 6
SECURE ACCESS PATH Waiting for access request
01 · TRUST
IDENTITY
Verify who is requesting access.
READY
02 · CONTEXT
DEVICE
Evaluate device posture and trust.
READY
03 · DECISION
ACCESS POLICY
Determine what the actor may reach.
READY
04 · PROTECT
SECURITY SERVICE
Apply VPN, ZTNA, SWG or related controls.
READY
05 · RESOURCE
APPLICATION
Reach the permitted cloud or internal service.
READY
06 · EVIDENCE
TELEMETRY
Record the access decision and session evidence.
READY
ACCESS TIMELINE 0 events
ENGINEERING EVIDENCE LIVE READOUT
Current Stage No access stage evaluated.
Security Function Waiting for the access workflow.
Investigation Finding No finding yet.
ENGINEERING MODEL · SECURITY INTELLIGENCE

Turn Security Signals Into Evidence

Individual security controls see different parts of an event. Identity systems see authentication, firewalls see connections, endpoints see processes and DNS controls see destinations. Security intelligence connects those signals so an investigation can understand the wider behaviour.

01 · COLLECT Gather telemetry Capture identity, network, endpoint, application and cloud security events.
02 · CORRELATE Connect the signals Relate events by identity, device, address, application, time and other useful context.
03 · INVESTIGATE Understand behaviour Determine whether apparently separate events form a meaningful security pattern.
04 · RESPOND Drive action Use validated findings to support analyst decisions or appropriate automated workflows.
Identity
+
Network
+
Endpoint
+
Application
→
Security Evidence
07 · CORRELATE · SECURITY INTELLIGENCE

SIEM, SOAR & Cross-Layer Security Intelligence

A modern security architecture produces enormous amounts of telemetry. The challenge is not simply collecting more events. It is connecting the right evidence so analysts can distinguish isolated activity from a meaningful attack pattern and then respond appropriately.

SIEM platforms provide centralised collection, search and correlation of security telemetry. SOAR extends the operational model by orchestrating response workflows and actions. Neither replaces the underlying security controls; both depend on the quality and context of the evidence they receive.

One event rarely tells the whole story

Different controls observe different parts of the same activity
IDENTITY Authentication Login attempts, MFA events, identity changes and access decisions.
NETWORK Connections Flows, firewall events, DNS activity and network security alerts.
ENDPOINT Processes Process execution, files, connections and endpoint detection telemetry.
APPLICATION Service activity Application authentication, errors, transactions and security events.
Raw Events Individual observations from separate control points.
→
Correlation Connect events using identity, asset, address, time and behavioural context.
→
Security Finding A contextualised event suitable for investigation.

SIEM and SOAR have different responsibilities

SIEM · Security Information & Event Management
Build the evidence picture
SIEM provides a central platform for collecting, searching and correlating security telemetry. It can help analysts identify relationships between events that would otherwise remain distributed across individual systems.
Primary role: collect → normalise → correlate → investigate
SOAR · Security Orchestration, Automation & Response
Orchestrate the response
SOAR can coordinate predefined workflows across security tools, reducing repetitive analyst tasks and helping execute approved response procedures.
Primary role: validate → orchestrate → execute → record

Security telemetry spans multiple layers

01 · IDENTITY Who? User, service account, authentication and authorization context.
02 · DEVICE What system? Endpoint identity, posture, process and security state.
03 · NETWORK Where? Source, destination, protocol, flow and network security context.
04 · APPLICATION What service? Application behaviour, transactions and service-level security events.
05 · TIME When? Temporal relationships can reveal sequences that isolated events hide.

Correlation turns separate events into an investigation

Example: a suspicious remote access sequence
09:14:02 Identity event Successful authentication from an unusual location.
09:14:18 Network event New connection established to an internal service.
09:14:41 Endpoint event Previously unseen process begins making outbound connections.
09:15:07 DNS event Endpoint resolves a newly observed external destination.
Correlation result: these events become more significant when linked by the same identity, endpoint and time window. The result is an investigation lead rather than four unrelated alerts.

Automation should follow validated evidence

01 · DETECT Generate the finding Correlation identifies behaviour that meets the defined detection criteria.
02 · VALIDATE Establish confidence Analysts or additional automated checks determine whether the finding is sufficiently reliable for action.
03 · RESPOND Execute the workflow Approved actions can then be orchestrated across identity, endpoint, network or other security systems.
Engineering evidence
More telemetry does not automatically mean better security

Effective security intelligence depends on useful context, consistent timestamps, meaningful asset and identity relationships, appropriate retention and well-tuned detection logic. A large event store without correlation can simply create a larger investigation queue.

Section 07 · Engineering Principle
Collect broadly, correlate intelligently and automate carefully.

SIEM provides the evidence and correlation layer while SOAR can orchestrate response workflows. The strongest architecture connects identity, endpoint, network and application telemetry so that security decisions are based on a contextual view of behaviour rather than an isolated alert.

07 · CORRELATE · SECURITY INTELLIGENCE

SIEM & SOAR Correlation Engine

Security events become useful when they are correlated across identity, network, endpoint and application layers. Build the evidence chain, calculate incident confidence and select an appropriate response.

SIGNALS 0 / 4
CONFIDENCE LOW
INCIDENT OPEN
SECURITY SIGNALS Waiting for telemetry
IDENTITY
Unusual Authentication
Authentication occurs from an unusual context or location.
WAIT
NETWORK
Suspicious Traffic
Network telemetry identifies unusual communication behaviour.
WAIT
ENDPOINT
Process Anomaly
Endpoint telemetry reports an unexpected process or execution chain.
WAIT
APPLICATION
Resource Access
Application telemetry shows access to a sensitive resource.
WAIT
CORRELATION CHAIN Confidence: LOW
Identity —
Network —
Endpoint —
Application —
CORRELATION TIMELINE 0 events
ENGINEERING EVIDENCE LIVE READOUT
Current Finding No correlated finding yet.
SIEM Function Collect and correlate security telemetry across layers.
SOAR Function No response workflow selected.
ENGINEERING MODEL · INTEGRATED SECURITY ARCHITECTURE

Validate the Security Architecture as a System

Security controls become more effective when they operate as a connected architecture rather than isolated point solutions. Validation asks whether identity, enforcement, segmentation, inspection, endpoint protection, telemetry and response work together as one security decision system.

01 · CONNECT
Integrate Controls Connect identity, policy, enforcement and telemetry.
02 · OBSERVE
Collect Evidence Make security decisions visible across the architecture.
03 · CORRELATE
Understand Context Combine signals instead of treating every alert independently.
04 · VALIDATE
Prove the Design Test whether the controls actually produce the intended outcome.
IDENTITY → ACCESS → SEGMENT → INSPECT → PROTECT → OBSERVE → RESPOND
Engineering Principle A security architecture should be evaluated as a decision chain, not as a collection of products.
Validation Question Can we prove that a security event is detected, understood, enforced and responded to across the complete control path?
08 · VALIDATE · INTEGRATED SECURITY ARCHITECTURE

Integrated Security Architecture

A mature security architecture connects individual controls into a decision and evidence chain. The objective is not to eliminate every point solution, but to ensure that identity, enforcement, detection, telemetry and response operate together.

SECURITY DECISION CHAIN
IDENTITY Who is the user, device or workload?
ACCESS CONTROL What is this identity permitted to reach?
SEGMENTATION Which trust boundary contains the resource?
INSPECTION Does the traffic or request contain suspicious behaviour?
PROTECTION Are endpoint, application and data controls active?
TELEMETRY Can the architecture produce evidence of the decision?
RESPONSE Can the appropriate action be executed and validated?
ARCHITECTURE PRINCIPLES
Least Privilege Grant only the access required for the task and context.
Explicit Policy Make security decisions intentional and explainable.
Continuous Visibility Capture telemetry across identity, network, endpoint and application layers.
Evidence-Based Response Use correlated evidence before escalating or containing an event.
Point Solutions Individual controls can provide strong protection, but disconnected systems increase integration and visibility gaps.
Integrated Architecture Controls remain specialised while sharing identity, telemetry, policy context and response workflows.
Engineering Test

If an attack crosses several security layers, can the organisation trace the event from initial identity signal through enforcement, detection, correlation and response?

The objective is integration, not simply accumulation.

Adding more security products does not automatically create a stronger architecture. The engineering question is whether each control has a defined role, produces useful evidence and connects to the controls responsible for the next security decision.

08 · VALIDATE · INTEGRATED SECURITY ARCHITECTURE

Integrated Security Assurance Console

Validate whether the complete security architecture can establish identity, enforce access, contain trust boundaries, inspect activity, protect assets, generate evidence and trigger an appropriate response.

CONTROLS 0 / 7
ASSURANCE 0%
ARCHITECTURE UNVALIDATED
END-TO-END CONTROL CHAIN Validation not started
01
Identity & Trust
Establish who or what is requesting access.
WAIT
02
Access Enforcement
Apply authentication, authorization and policy.
WAIT
03
Segmentation
Constrain communication within the intended trust boundary.
WAIT
04
Inspection & Detection
Inspect traffic, requests and behaviour for threats.
WAIT
05
Endpoint & Data Protection
Protect the endpoint, application and information.
WAIT
06
Telemetry & Correlation
Produce evidence and correlate events across layers.
WAIT
07
Response & Recovery
Execute, validate and recover from the security decision.
WAIT
ARCHITECTURE ASSURANCE 0%
Validate each layer to determine whether the architecture forms a complete security decision and evidence chain.
VALIDATION TIMELINE 0 events
ENGINEERING EVIDENCE LIVE READOUT
Current Finding No controls validated yet.
Architecture Test Can the security chain be traced from identity to response?
Final Assurance Architecture validation pending.
```
☕
Support Network Insight
Help support independent engineering guides, interactive networking tools, and future learning labs.
Support Network Insight ```
Interactive Security Fabric

Point Solutions vs Integrated Security

Modern security requires more than isolated tools. Explore how identity, device posture, segmentation, threat detection and security analytics combine to produce a stronger security decision.
Unified security decision
Identity
→
Device
→
Network
→
Threat
→
Intelligence
→
Enforcement
Combined Security Risk
LOW · 18%
ID
Identity
Identity security signal

Identity provides context about who is requesting access and whether authentication requirements have been satisfied.

Signal User + MFA
Question Who is requesting access?
Control Authentication
Value Identity-aware policy
CURRENT DECISION
Identity signal is healthy. Continue evaluating device and network context.

Why correlation matters

A single security product sees only part of the story. Correlating identity, device, network and threat telemetry creates a much stronger basis for enforcement.
IDENTITY Who is accessing the resource?
DEVICE Is the endpoint trusted and healthy?
NETWORK Is the requested communication permitted?
THREAT Is there evidence of malicious activity?
SIEM / SOAR Can multiple signals be correlated and acted upon?

Zero Trust Networking

Zero Trust Networking

In today's increasingly digital world, where cyber threats are becoming more sophisticated, traditional security measures are no longer enough to protect sensitive data and networks. This has led to the rise of a revolutionary approach known as zero trust networking. In this blog post, we will explore the concept of zero trust networking, its key principles, implementation strategies, and the benefits it offers to organizations.

Zero trust networking is a security framework that challenges the traditional perimeter-based security model. Unlike the traditional approach, which assumes that everything inside a network is trustworthy, zero trust networking operates on the principle of "never trust, always verify." It assumes that both internal and external networks are potentially compromised and requires continuous authentication and authorization for every user, device, and application attempting to access resources.

1. Least Privilege: Granting users the minimum level of access required to perform their tasks, reducing the risk of unauthorized access or lateral movement within the network.

2. Microsegmentation: Dividing the network into smaller, isolated segments, allowing granular control and containment of potential threats.

3. Continuous Authentication: Implementing multi-factor authentication and real-time monitoring to ensure ongoing verification of users and devices.

1. Identifying Critical Assets: Determine which assets require protection and prioritize them accordingly.<br
2. Mapping Data Flow: Understand how data moves within the network and identify potential vulnerabilities or points of compromise.

3. Architecture Design: Develop a comprehensive network architecture that incorporates microsegmentation, access controls, and continuous monitoring.

4. Implementing Technologies: Utilize technologies such as identity and access management (IAM), network segmentation tools, and security analytics to enforce zero trust principles.

1. Enhanced Security: By adopting a zero trust approach, organizations significantly reduce the risk of unauthorized access and data breaches.

2. Improved Compliance: Organizations can better meet regulatory requirements by implementing strict access controls and continuous monitoring.

3. Greater Flexibility: Zero trust networking enables organizations to securely embrace cloud services, remote work, and bring-your-own-device (BYOD) policies.

Zero trust networking represents a paradigm shift in network security. By eliminating the assumption of trust and implementing continuous verification, organizations can fortify their networks against evolving cyber threats. Embracing zero trust networking not only enhances security but also enables organizations to adapt to the changing digital landscape while protecting their valuable assets.

</br

ZERO TRUST NETWORKING • INTERACTIVE LAB 01

Zero Trust Access Decision Lab

Explore how Zero Trust evaluates identity, device posture, context and resource sensitivity before granting access.

Learning Objective
Evaluate an access request through a Zero Trust decision pipeline and understand how contextual signals change the final enforcement decision.
Access Request Scenario
Zero Trust Decision Pipeline
↗
Access Request
Waiting
◎
Identity
Waiting
▣
Device
Waiting
◌
Context
Waiting
◆
Policy
Waiting
△
Risk Engine
Waiting
✓
Decision
Waiting
⬢
Enforcement
Waiting
Policy Decision
NOT EVALUATED
— / 100 risk
Configure the access request and click Evaluate Access Request.
Decision Evidence
Identity —
Device —
Context —
Resource —
Zero Trust Decision Console
[SYSTEM] Decision engine ready.
[POLICY] Awaiting access request.
Engineering Takeaway
Zero Trust replaces implicit network trust with an explicit contextual access decision. Identity alone is not enough.

Highlights: Zero Trust Networking

**Understanding Zero Trust Networking**

In today’s digital landscape, where cyber threats are ever-evolving, traditional security models are often inadequate. Enter Zero Trust Networking, a revolutionary approach that challenges the “trust but verify” mindset. Instead, Zero Trust operates on a “never trust, always verify” principle. This model assumes that threats can originate both outside and inside the network, leading to a more robust security posture. By scrutinizing every access request and continuously validating user permissions, Zero Trust Networking aims to protect organizations from data breaches and unauthorized access.

**Key Components of Zero Trust**

Implementing a Zero Trust Network involves several key components. First, identity verification becomes paramount. Every user and device must be authenticated and authorized before accessing any resource. This can be achieved through strong multi-factor authentication mechanisms. Secondly, micro-segmentation plays a critical role in limiting lateral movement within the network. By dividing the network into smaller, isolated segments, Zero Trust ensures that even if one segment is compromised, the threat is contained. Finally, continuous monitoring and analytics are essential. By keeping a watchful eye on user behavior and network activity, anomalies can be detected and addressed swiftly.

**Benefits of Adopting Zero Trust**

Adopting a Zero Trust model offers numerous benefits for organizations. One of the most significant advantages is the enhanced security posture it provides. By reducing the attack surface and limiting access to only what is necessary, organizations can significantly decrease the likelihood of a breach. Moreover, Zero Trust enables compliance with stringent regulatory requirements by ensuring that data access is strictly controlled and monitored. Additionally, with the rise of remote work and cloud-based services, Zero Trust offers a flexible and scalable security solution that adapts to changing business needs.

**Challenges in Implementing Zero Trust**

Despite its advantages, transitioning to a Zero Trust Network is not without challenges. Organizations may face resistance from employees accustomed to traditional access models. The initial setup and configuration of Zero Trust can also be complex and resource-intensive. Furthermore, maintaining continuous visibility and control over every device and user can strain IT resources. However, these challenges can be mitigated by gradually implementing Zero Trust principles, starting with high-risk areas, and leveraging automation and advanced analytics.

Zero Trust Networking Through Behaviour‑Driven Trust

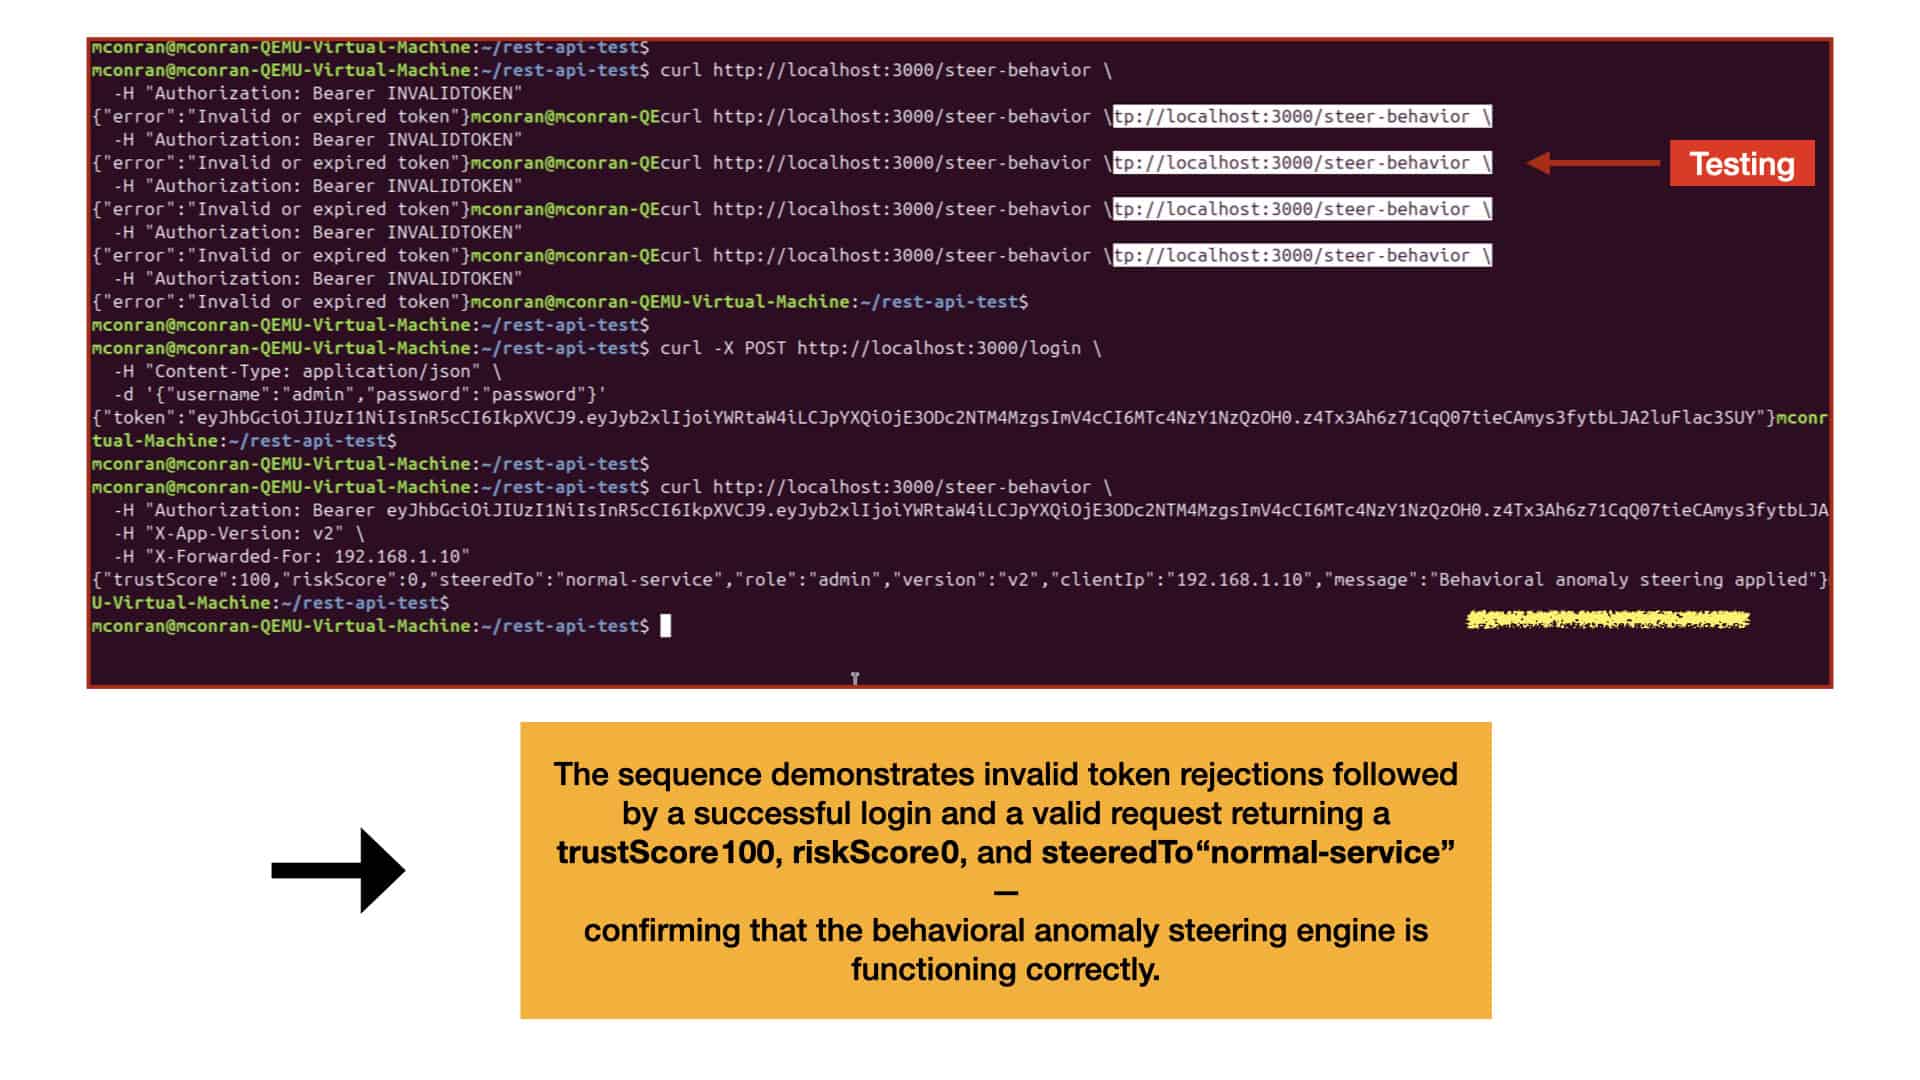
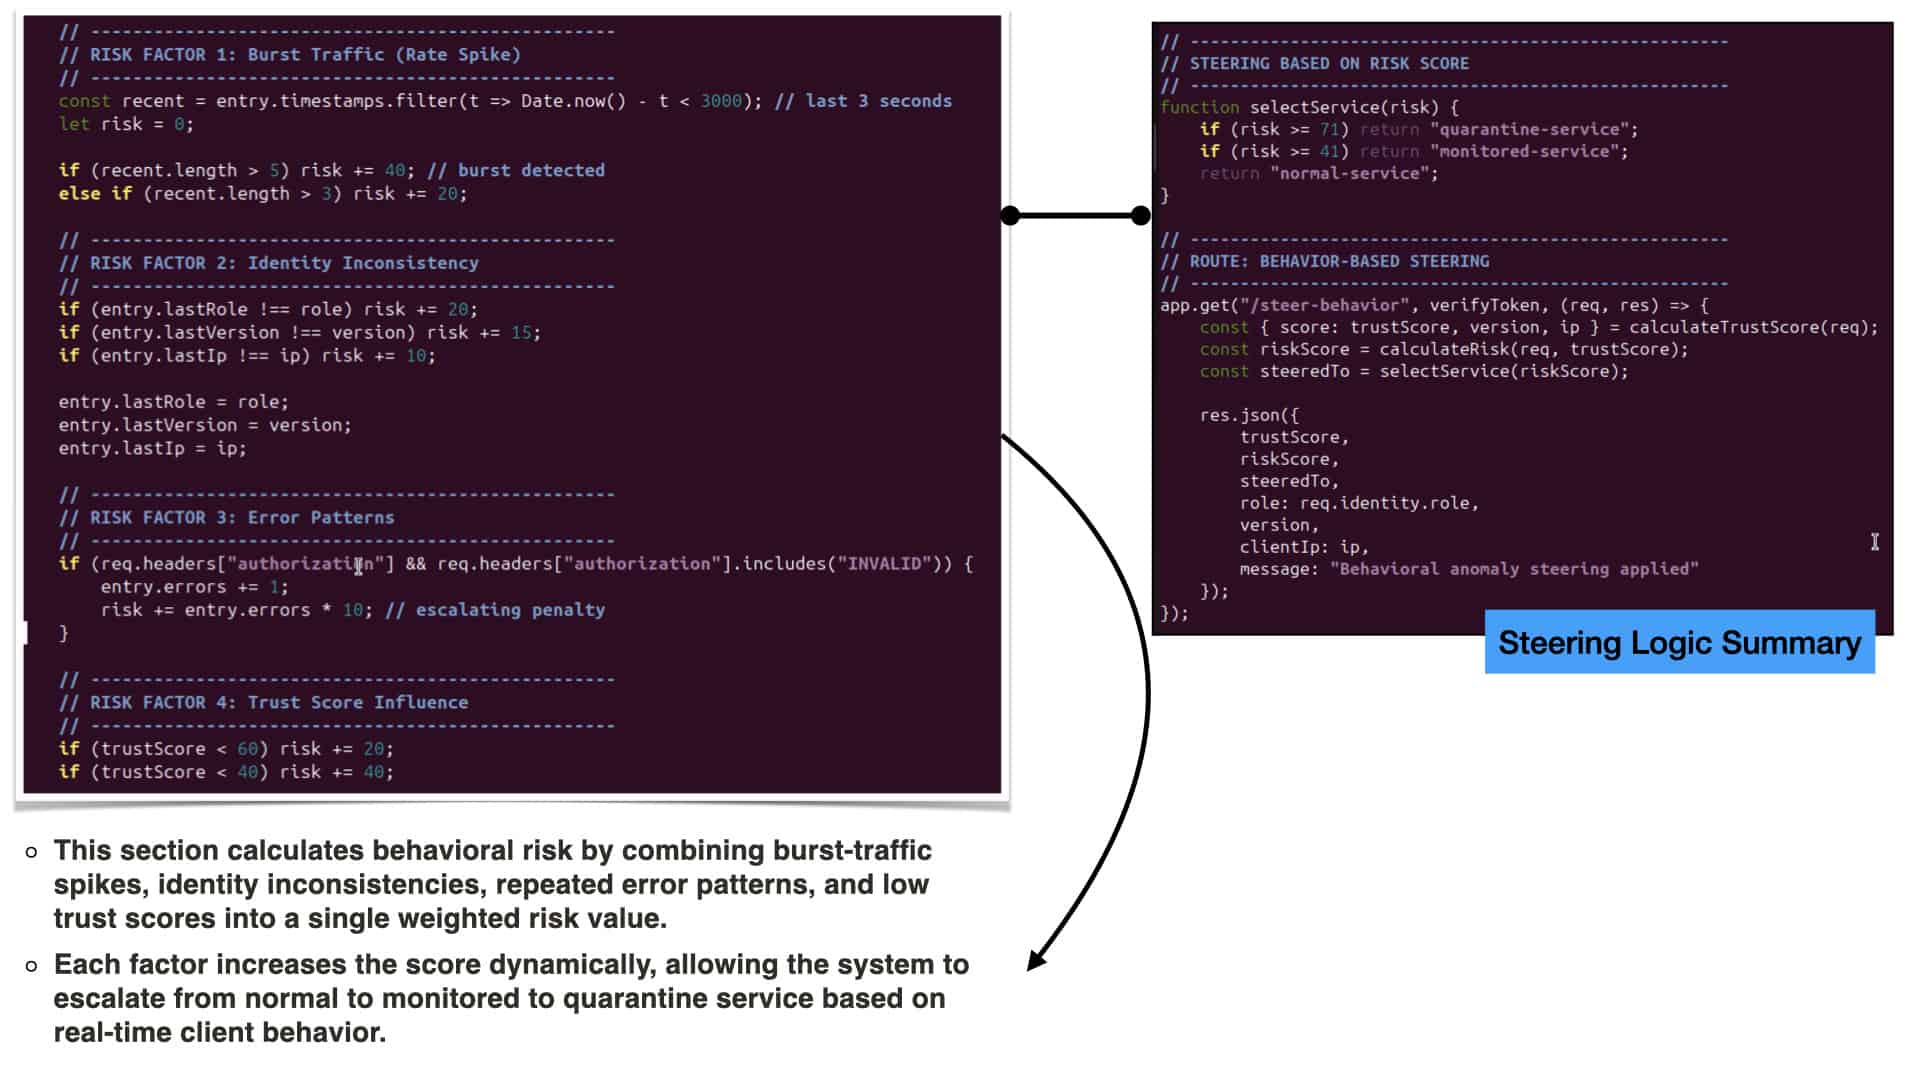
This lab demonstrates how zero trust networking becomes stronger when every client request is evaluated using behavioural signals rather than relying solely on identity or tokens. By analysing request frequency, metadata consistency, and error patterns, the system builds a dynamic trust profile for each client. This ensures that zero trust networking continuously validates every action, enforcing “never trust, always verify” at all times

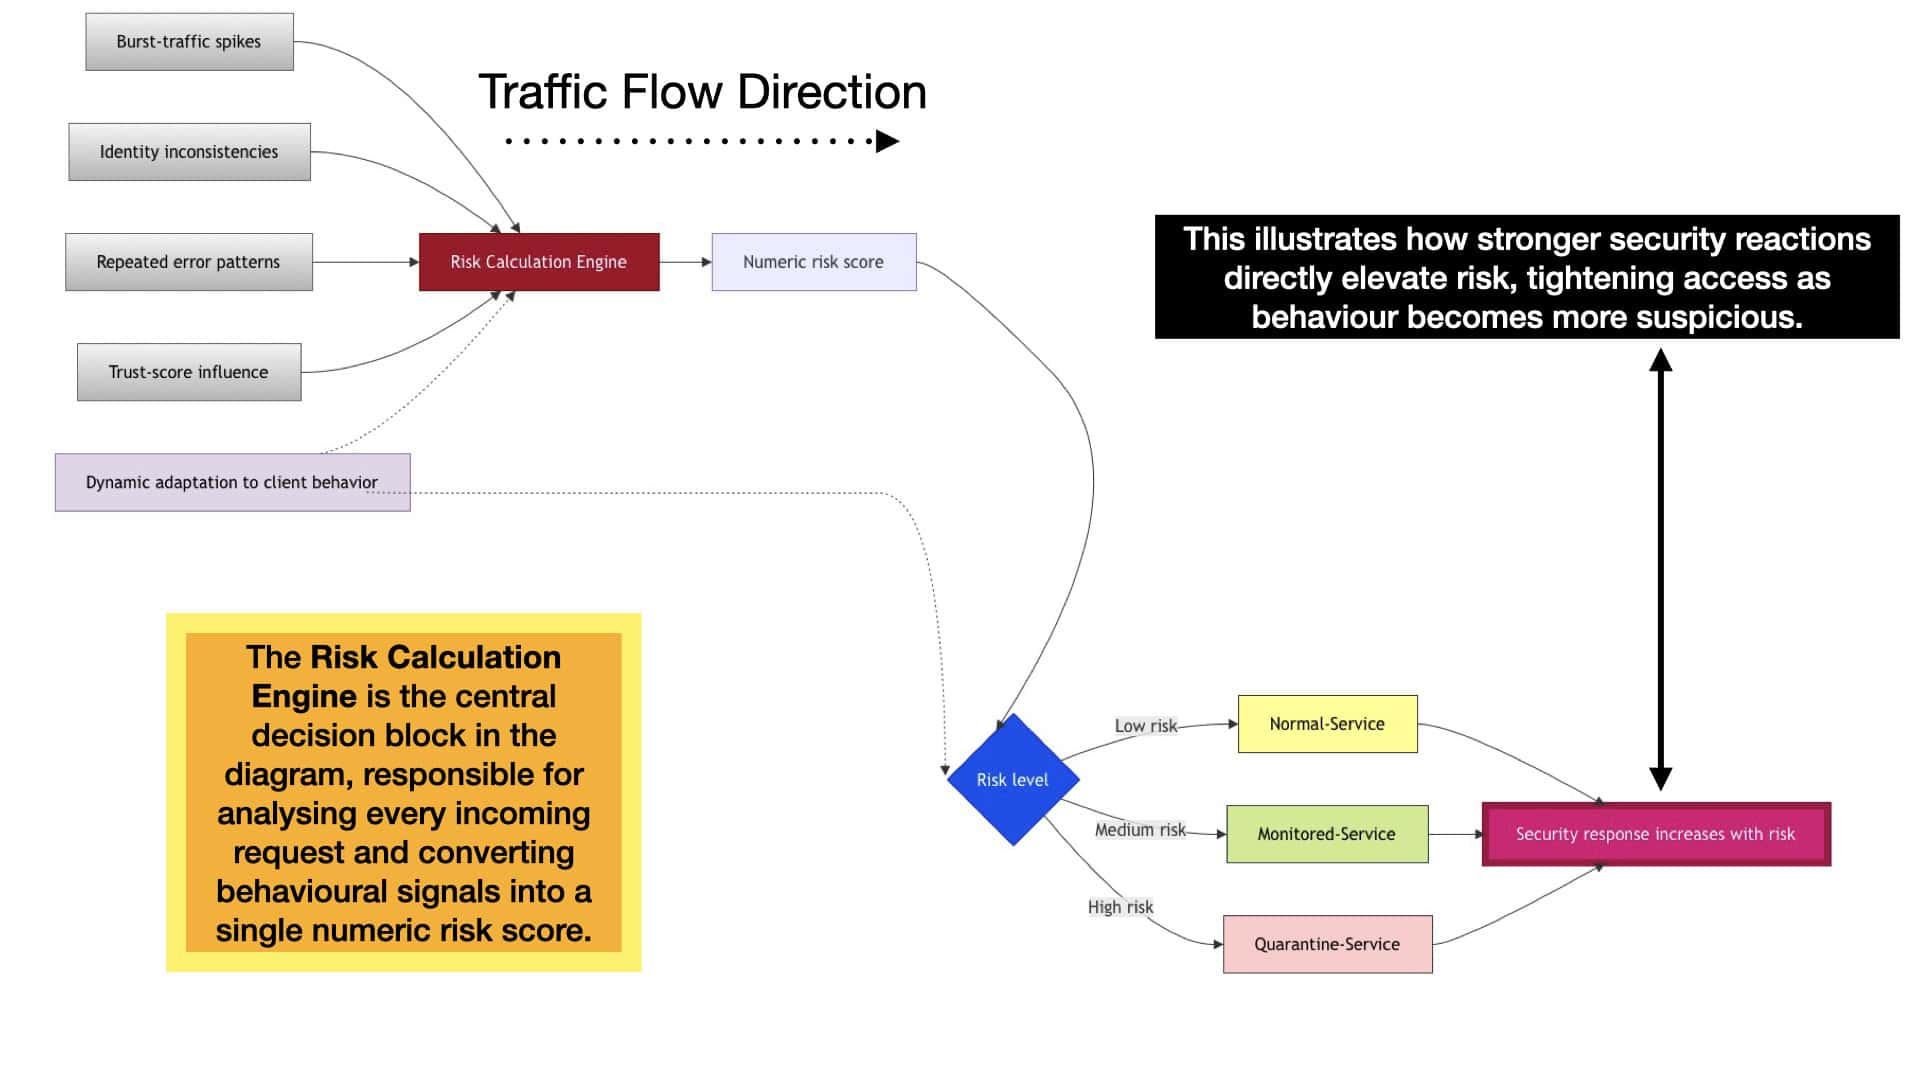
The risk engine applies weighted rules to burst‑traffic spikes, identity mismatches, repeated failures, and trust‑score influence to generate a single risk value. This multi‑factor scoring model reflects how zero trust networking depends on combining diverse indicators to detect anomalies early. As risk increases, the system escalates its security posture, shifting from normal to monitored to quarantine service to protect critical assets.

Once the risk score is computed, the steering engine selects the appropriate response path. Low‑risk behaviour is routed normally, medium‑risk behaviour is monitored, and high‑risk behaviour is quarantined. This adaptive routing illustrates how zero trust networking enforces dynamic segmentation, ensuring that suspicious behaviour triggers stronger controls while legitimate traffic continues without interruption.


Understanding Zero Trust Networking

Zero-trust networking is a security model that challenges the traditional perimeter-based approach. It operates on the principle of “never trust, always verify.” Every user, device, or application trying to access a network is treated as potentially malicious until proven otherwise. Zero-trust networking aims to reduce the attack surface and prevent lateral movement within a network by eliminating implicit trust.

Several components are crucial to implementing zero-trust networking effectively. These include:

1. Identity and Access Management (IAM): IAM solutions play a vital role in zero-trust networking by ensuring that only authenticated and authorized individuals can access specific resources. Multi-factor authentication, role-based access control, and continuous monitoring are critical features of IAM in a zero-trust architecture.

2. Microsegmentation: Microsegmentation divides a network into smaller, isolated segments, enhancing security by limiting lateral movement. Each segment has its security policies and controls, preventing unauthorized access and reducing the potential impact of a breach.

Endpoint Security: Networking

Understanding ARP (Address Resolution Protocol)

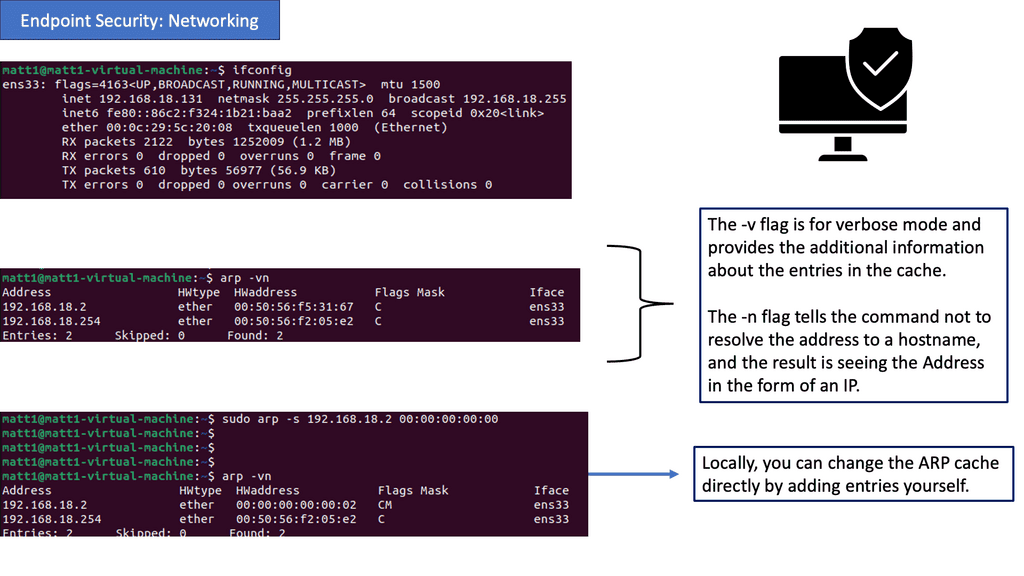
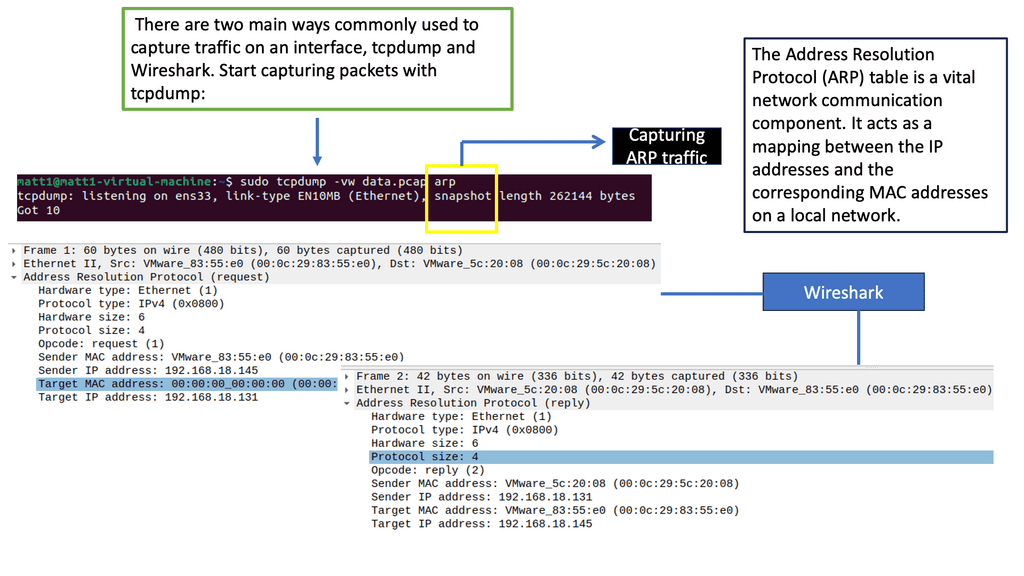
– ARP plays a vital role in establishing communication between devices within a network. It resolves IP addresses into MAC addresses, facilitating data transmission. Network administrators can identify potential spoofing attempts or unauthorized entities trying to gain access by examining ARP tables. Understanding ARP’s inner workings is crucial for implementing effective endpoint security measures.

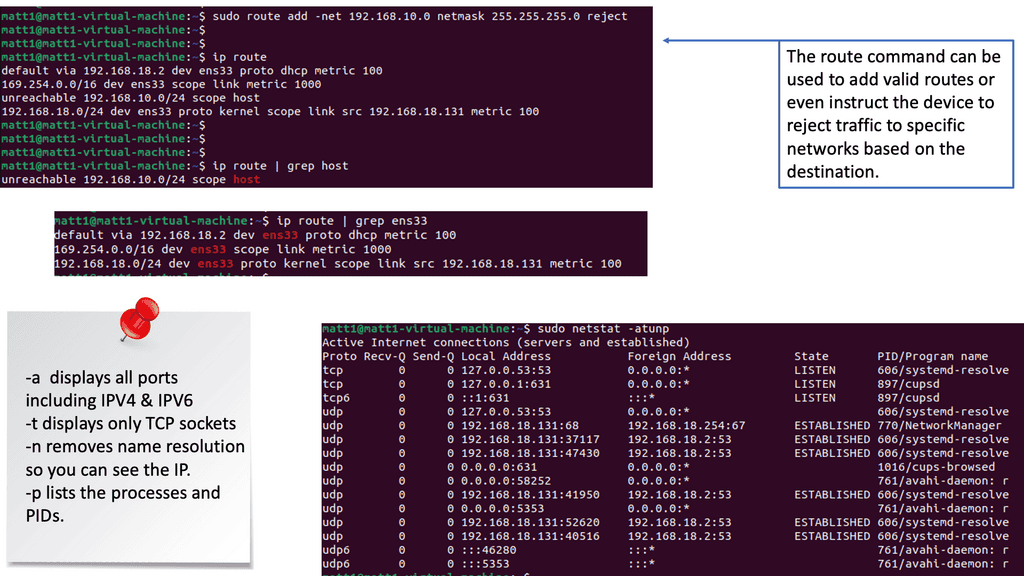
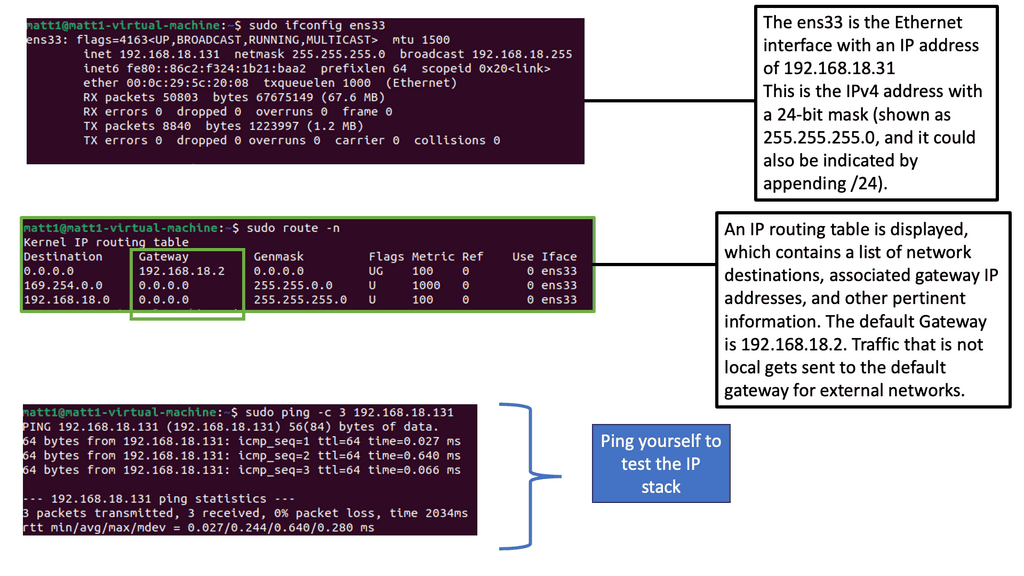
– Route tables are at the core of network routing decisions. They determine the path that data packets take while traveling across networks. Administrators can ensure that data flows securely and efficiently by carefully configuring and monitoring route tables. We will explore techniques to secure route tables, including access control lists (ACLs) and route summarization.

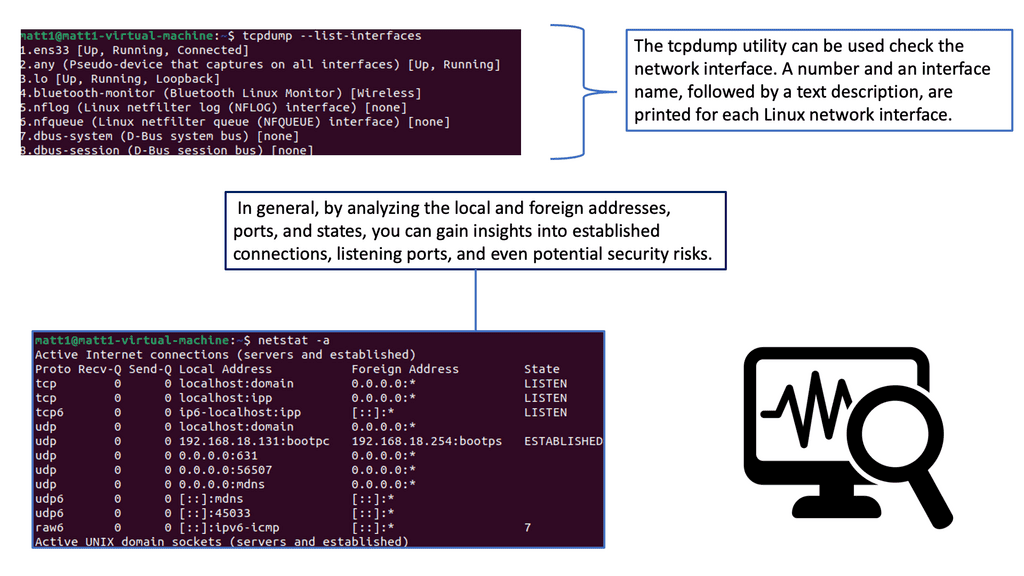
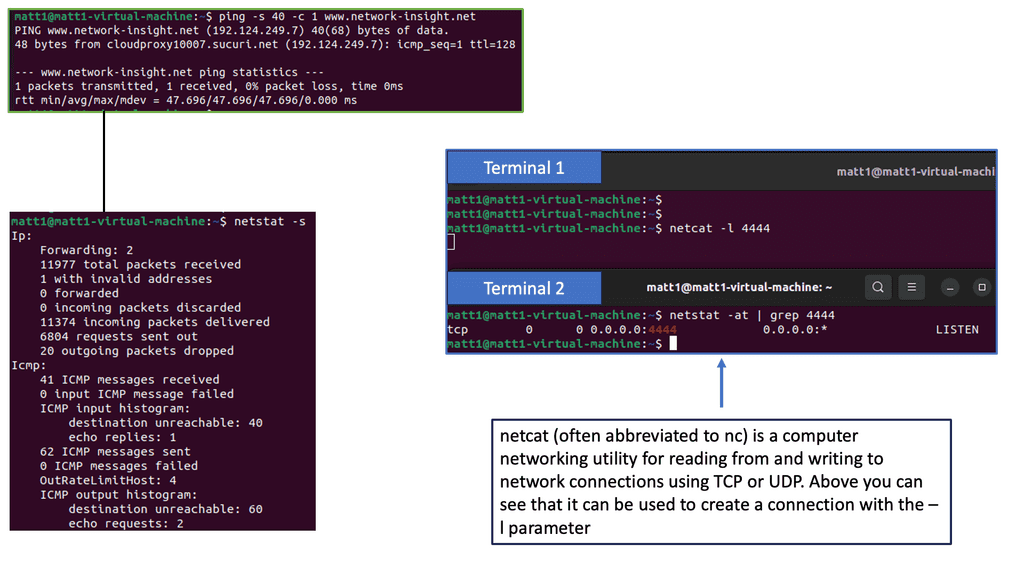
– Netstat, short for “network statistics,” is a powerful command-line tool that provides valuable insights into network connections and interface statistics. It enables administrators to monitor active connections, detect suspicious activities, and identify potential security breaches. We will uncover various netstat commands and their practical applications in enhancing endpoint security.

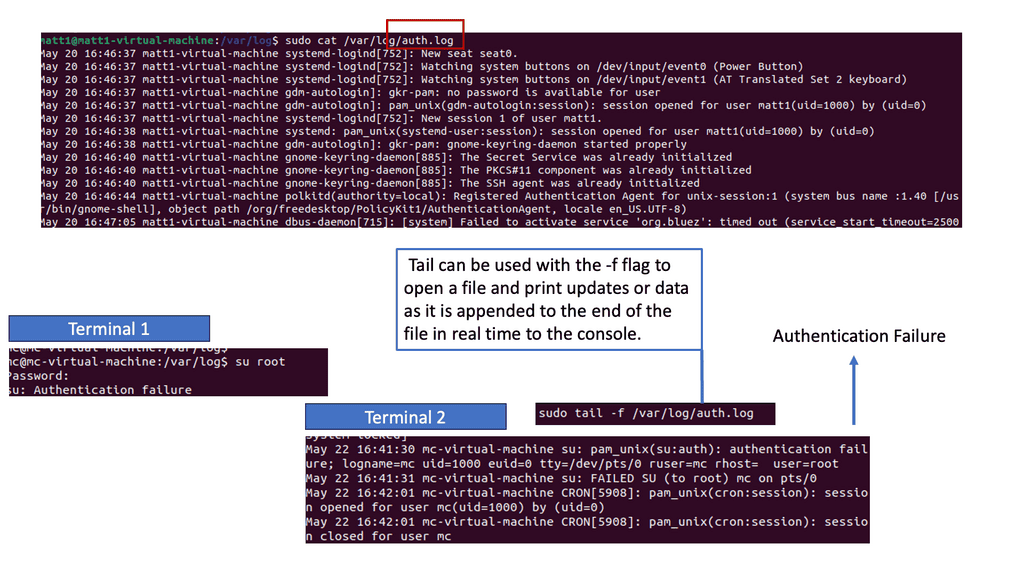
Example: Detecting Authentication Failures in Logs

Understanding Syslog

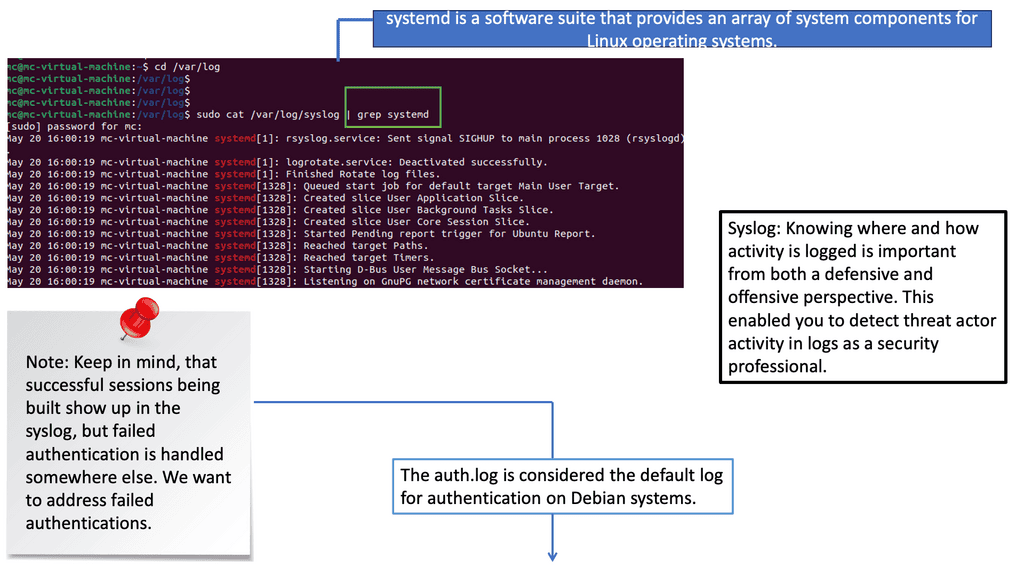
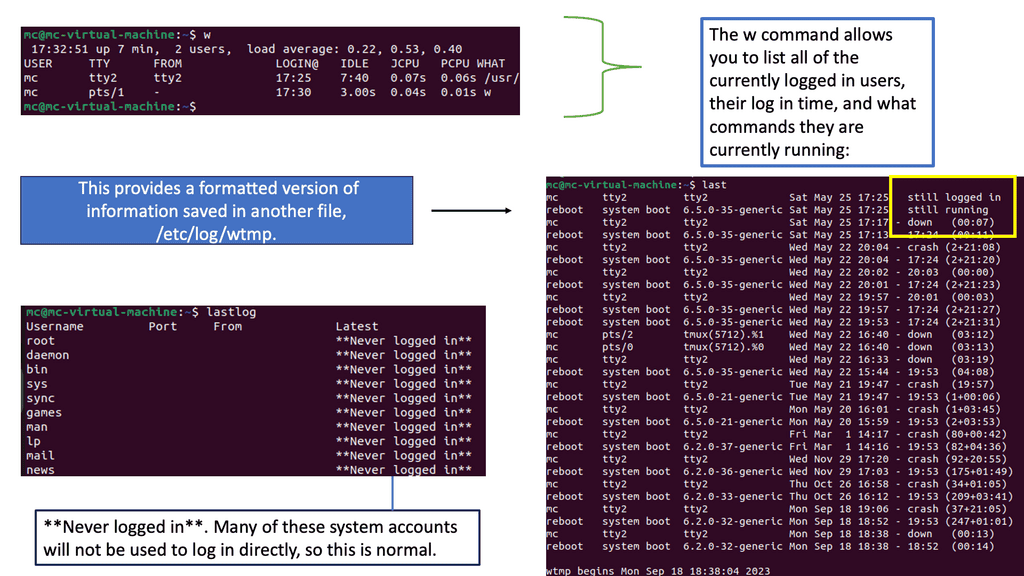
– Syslog, a standard protocol for message logging, provides a centralized mechanism to collect and store log data. It is a repository of vital information, capturing events from various systems and devices. By analyzing syslog entries, security analysts can gain insights into network activities, system anomalies, and potential security incidents. Understanding the structure and content of syslog messages is crucial for practical log analysis.

– Auth.log, a log file specific to Unix-like systems, records authentication-related events such as user logins, failed login attempts, and privilege escalations. This log file is a goldmine for detecting unauthorized access attempts, brute-force attacks, and suspicious user activities. Familiarizing oneself with the format and patterns within auth.log entries can significantly enhance the ability to identify potential security breaches.

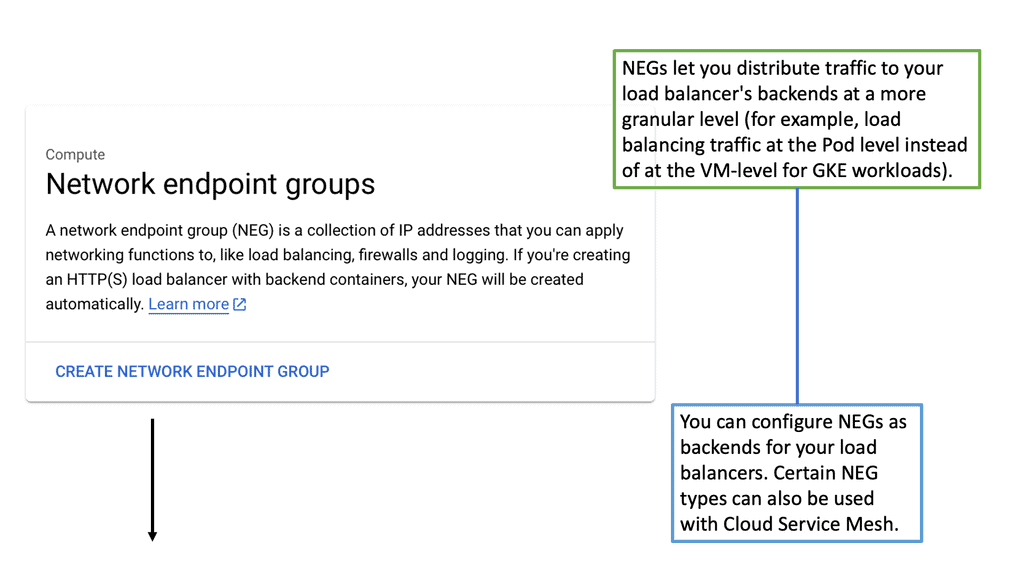
Example Technology: Network Endpoint Groups

**Understanding Network Endpoint Groups**

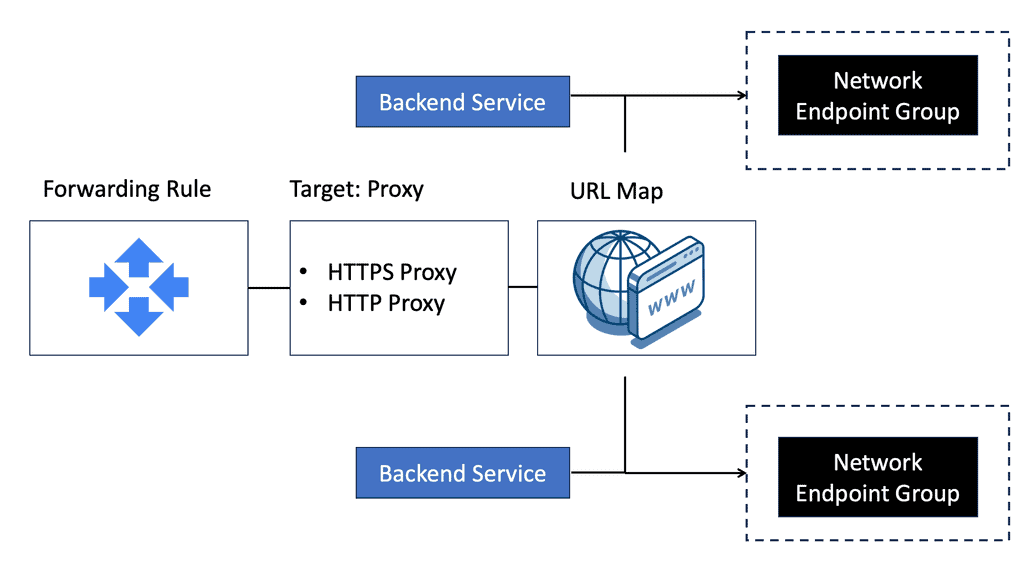
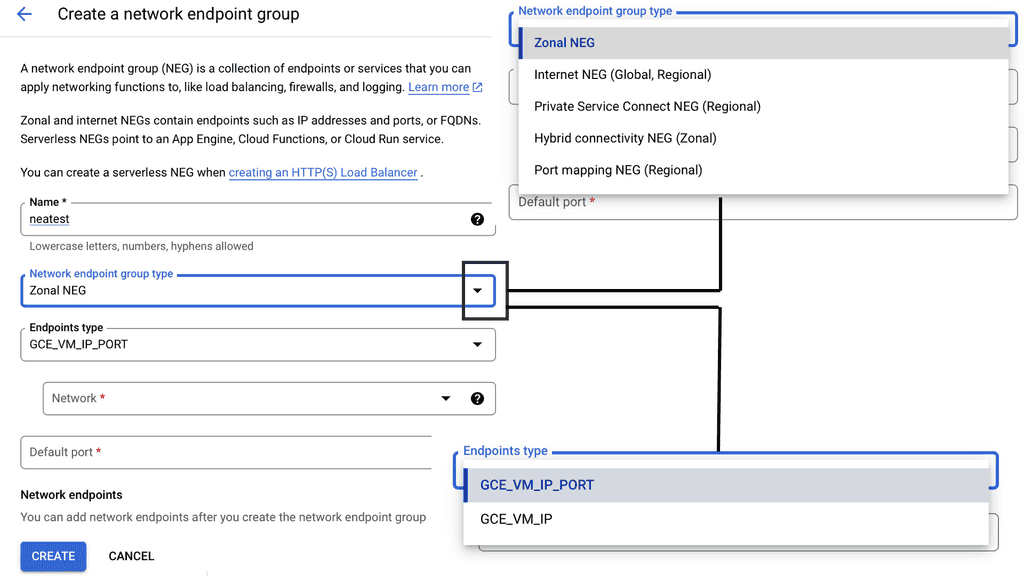
Network Endpoint Groups are a collection of network endpoints within Google Cloud, each representing an IP address and optionally a port. This concept allows you to define how traffic should be distributed across different services, whether they are hosted on Google Cloud or external services. NEGs enable better load balancing, seamless integration with Google Cloud services, and the ability to connect with legacy systems or third-party services outside your direct cloud environment.

**Benefits of Using Network Endpoint Groups**

The adoption of NEGs offers multiple benefits:

1. **Scalability**: NEGs provide a scalable solution to manage large volumes of traffic efficiently. You can dynamically add or remove endpoints as demand fluctuates, ensuring optimal performance and cost-effectiveness.

2. **Flexibility**: With NEGs, you have the flexibility to direct traffic to different types of endpoints, including Google Cloud VMs, serverless applications, and external services. This flexibility supports a wide range of application architectures.

3. **Enhanced Load Balancing**: NEGs work seamlessly with Google Cloud Load Balancing, allowing for sophisticated traffic management. You can configure traffic policies that suit your specific needs, ensuring reliability and performance.

**Implementing Network Endpoint Groups in Your Infrastructure**

Implementing NEGs is straightforward with Google Cloud’s intuitive interface. Begin by defining your endpoints, which could include Google Compute Engine instances, Google Kubernetes Engine pods, or even external endpoints. Next, configure your load balancer to direct traffic to your NEGs. This setup ensures that your applications benefit from consistent performance and availability, regardless of where your endpoints are located.

**Best Practices for Managing Network Endpoint Groups**

To maximize the effectiveness of NEGs, consider the following best practices:

– **Regularly Monitor and Update**: Keep a close eye on endpoint performance and update your NEGs as your infrastructure evolves. This proactive approach helps maintain optimal resource utilization.

– **Security Considerations**: Implement proper security measures, including network policies and firewalls, to protect your endpoints from potential threats.

– **Integration with CI/CD Pipelines**: Integrating NEGs with your continuous integration and continuous deployment pipelines ensures that your network configurations evolve alongside your application code, reducing manual overhead and potential errors.

network endpoint groups

Transitioning to a zero-trust networking model requires careful planning and execution. Here are a few strategies to consider:

1. Comprehensive Network Assessment: Begin by thoroughly assessing your existing network infrastructure, identifying vulnerabilities and areas that need improvement.

2. Phased Approach: Implementing zero-trust networking across an entire network can be challenging. Consider adopting a phased approach, starting with critical assets and gradually expanding to cover the whole network.

3. User Education: Educate users about the principles and benefits of zero-trust networking. Emphasize the importance of strong authentication, safe browsing habits, and adherence to security policies.

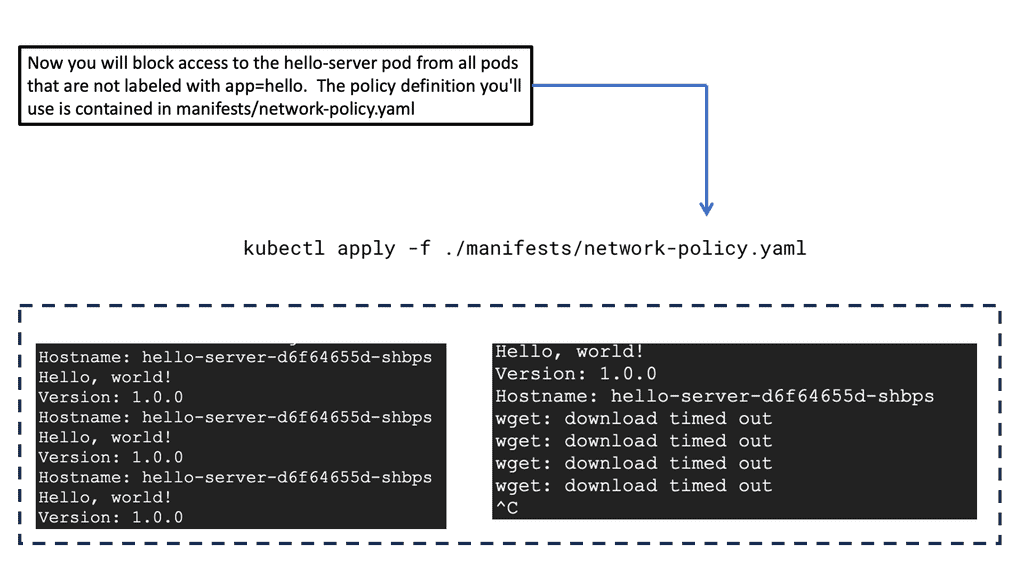
Google Cloud – GKE Network Policy

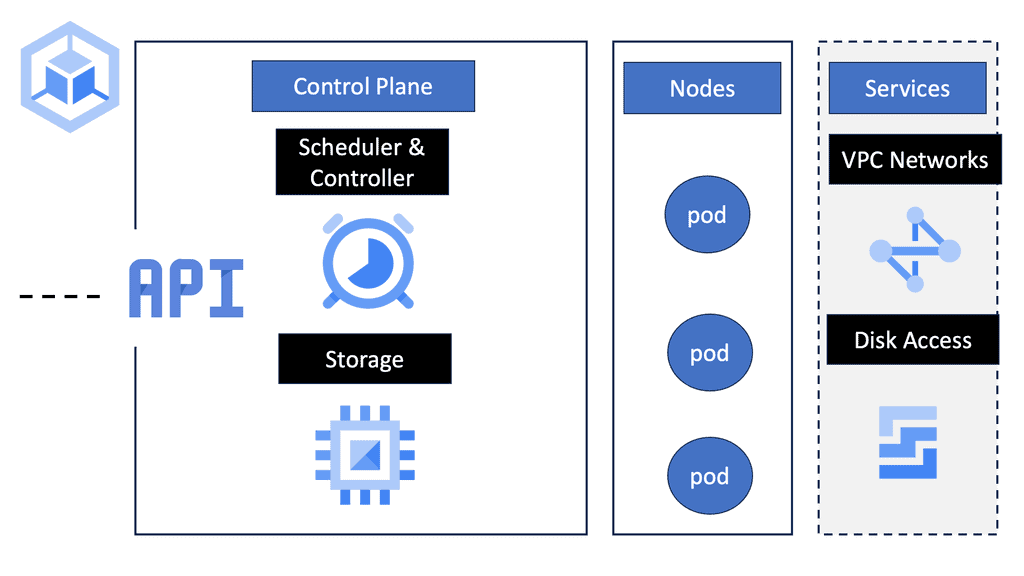
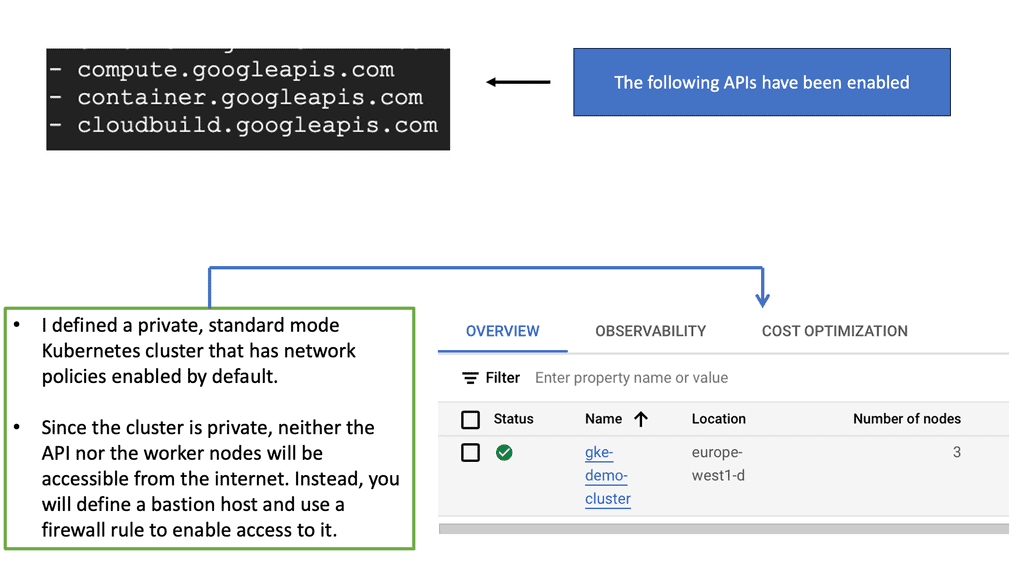
Google Kubernetes Engine (GKE) offers a robust platform for deploying, managing, and scaling containerized applications. One of the essential tools at your disposal is Network Policy. This feature allows you to define how groups of pods communicate with each other and other network endpoints. Understanding and implementing Network Policies is a crucial step towards achieving zero trust networking within your Kubernetes environment.

## The Basics of Network Policies

Network Policies in GKE are essentially rules that define the allowed connections to and from pods. These policies are based on the Kubernetes NetworkPolicy API and provide fine-grained control over the communication within a Kubernetes cluster. By default, all pods in GKE can communicate with each other without restrictions. However, as your applications grow in complexity, this open communication model can become a security liability. Network Policies allow you to enforce restrictions, enabling you to specify which pods can communicate with each other, thereby reducing the attack surface.

## Implementing Zero Trust Networking

Zero trust networking is a security concept that assumes no implicit trust, and everything must be verified before gaining access. Implementing Network Policies in GKE is a core component of adopting a zero trust approach. By default, zero trust networking assumes that threats could originate from both outside and inside the network. With Network Policies, you can enforce strict access controls, ensuring that only the necessary pods and services can communicate, effectively minimizing the potential for lateral movement in the event of a breach.

## Best Practices for Network Policies

When designing Network Policies, it’s crucial to adhere to best practices to ensure both security and performance. Start by defining a default-deny policy, which blocks all traffic, and then create specific allow rules for necessary communications. Regularly review and update these policies to accommodate changes in your applications and infrastructure. Utilize namespaces effectively to segment different environments (e.g., development, staging, production) and apply specific policies to each, ensuring that only essential communications are permitted within and across these boundaries.

## Monitoring and Troubleshooting

Implementing Network Policies is not a set-and-forget task. Continuous monitoring is essential to ensure that policies are functioning correctly and that no unauthorized traffic is allowed. GKE provides tools and integrations to help you monitor network traffic and troubleshoot any connectivity issues that arise. Consider using logging and monitoring solutions like Google Cloud’s Operations Suite to gain insights into your network traffic and policy enforcement, allowing you to identify and respond to potential issues promptly.

Kubernetes network policy

Googles VPC Service Controls

**The Role of Zero Trust Network Design**

VPC Service Controls align perfectly with the principles of a zero trust network design, an approach that assumes threats could originate from inside or outside the network. This design necessitates strict verification processes for every access request. VPC Service Controls help enforce these principles by allowing you to define and enforce security perimeters around your Google Cloud resources, such as APIs and services. This ensures that only authorized requests can access sensitive data, even if they originate from within the network.

**Implementing VPC Service Controls on Google Cloud**

Implementing VPC Service Controls is a strategic move for organizations leveraging Google Cloud services. By setting up service perimeters, you can protect a wide range of Google Cloud services, including Cloud Storage, BigQuery, and Cloud Pub/Sub. These perimeters act as virtual barriers, preventing unauthorized transfers of data across the defined boundaries. Additionally, VPC Service Controls offer features like Access Levels and Access Context Manager to fine-tune access policies based on contextual attributes, such as user identity and device security status.

VPC Security Controls

Zero Trust with IAM

**Understanding Google Cloud IAM**

Google Cloud IAM is a critical security component that allows organizations to manage who has access to specific resources within their cloud infrastructure. It provides a centralized system for defining roles and permissions, ensuring that only authorized users can perform certain actions. By adhering to the principle of least privilege, IAM helps minimize potential security risks by limiting access to only what is necessary for each user.

**Implementing Zero Trust with Google Cloud**

Zero trust is a security model that assumes threats could be both inside and outside the network, thus requiring strict verification for every user and device attempting to access resources. Google Cloud IAM plays a pivotal role in realizing a zero trust architecture by providing granular control over user access. By leveraging IAM policies, organizations can enforce multi-factor authentication, continuous monitoring, and strict access controls to ensure that every access request is verified before granting permissions.

**Key Features of Google Cloud IAM**

Google Cloud IAM offers a range of features designed to enhance security and simplify management:

– **Role-Based Access Control (RBAC):** Allows administrators to assign specific roles to users, defining what actions they can perform on which resources.

– **Custom Roles:** Provides the flexibility to create roles tailored to the specific needs of your organization, offering more precise control over permissions.

– **Audit Logging:** Facilitates the tracking of user activity and access patterns, helping in identifying potential security threats and ensuring compliance with regulatory requirements.

Google Cloud IAM

API Service Networking 

**The Role of Google Cloud in Service Networking**

Google Cloud has emerged as a leader in providing robust service networking solutions that leverage its global infrastructure. With tools like Google Cloud’s Service Networking API, businesses can establish secure connections between their various services, whether they’re hosted on Google Cloud, on-premises, or even in other cloud environments. This capability is crucial for organizations looking to build scalable, resilient, and efficient architectures. By utilizing Google Cloud’s networking solutions, businesses can ensure their services are interconnected in a way that maximizes performance and minimizes latency.

**Embracing Zero Trust Architecture**

Incorporating a Zero Trust security model is becoming a standard practice for organizations aiming to enhance their cybersecurity posture. Zero Trust operates on the principle that no entity, whether inside or outside the network, should be automatically trusted. This approach aligns perfectly with Service Networking APIs, which can enforce stringent access controls, authentication, and encryption for all service communications. By adopting a Zero Trust framework, businesses can mitigate risks associated with data breaches and unauthorized access, ensuring their service interactions are as secure as possible.

**Advantages of Service Networking APIs**

Service Networking APIs offer numerous advantages for businesses navigating the complexities of modern IT environments. They provide the flexibility to connect services across hybrid and multi-cloud setups, ensuring that data and applications remain accessible regardless of their physical location. Additionally, these APIs streamline the process of managing network configurations, reducing the overhead associated with manual network management tasks. Furthermore, by facilitating secure and efficient connections, Service Networking APIs enable businesses to focus on innovation rather than infrastructure challenges.

Service Networking API

Zero Trust with Private Service Connect

**Understanding Google Cloud’s Private Service Connect**

At its core, Private Service Connect is designed to simplify service connectivity by allowing you to create private and secure connections to Google services and third-party services. This eliminates the need for public IPs while ensuring that your data remains within Google’s protected network. By utilizing PSC, businesses can achieve seamless connectivity without compromising on security, a crucial aspect of modern cloud infrastructure.

**The Role of Private Service Connect in Zero Trust**

Zero trust is a security model centered around the principle of “never trust, always verify.” It assumes that threats could be both external and internal, and hence, every access request should be verified. PSC plays a critical role in this model by providing a secure pathway for services to communicate without exposing them to the public internet. By integrating PSC, organizations can ensure that their cloud-native applications follow zero-trust principles, thereby minimizing risks and enhancing data protection.

**Benefits of Adopting Private Service Connect**

Implementing Private Service Connect offers several advantages:

1. **Enhanced Security**: By eliminating the need for public endpoints, PSC reduces the attack surface, making your services less vulnerable to threats.

2. **Improved Performance**: With direct and private connectivity, data travels through optimized paths within Google’s network, reducing latency and increasing reliability.

3. **Simplicity and Scalability**: PSC simplifies the network architecture by removing the complexities associated with managing public IPs and firewalls, making it easier to scale services as needed.

private service connect

Network Connectivity Center

### The Importance of Zero Trust Network Design

Zero Trust is a security model that requires strict verification for every person and device trying to access resources on a private network, regardless of whether they are inside or outside the network perimeter. This approach significantly reduces the risk of data breaches and unauthorized access. Implementing a Zero Trust Network Design with NCC ensures that all network traffic is continuously monitored and verified, enhancing overall security.

### How NCC Enhances Zero Trust Security

Google Network Connectivity Center provides several features that align with the principles of Zero Trust:

1. **Centralized Management:** NCC offers a single pane of glass for managing all network connections, making it easier to enforce security policies consistently across the entire network.

2. **Granular Access Controls:** With NCC, organizations can implement fine-grained access controls, ensuring that only authorized users and devices can access specific network resources.

3. **Integrated Security Tools:** NCC integrates with Google Cloud’s suite of security tools, such as Identity-Aware Proxy (IAP) and Cloud Armor, to provide comprehensive protection against threats.

### Real-World Applications of NCC

Organizations across various industries can benefit from the capabilities of Google Network Connectivity Center. For example:

– **Financial Services:** A bank can use NCC to securely connect its branch offices and data centers, ensuring that sensitive financial data is protected at all times.

– **Healthcare:** A hospital can leverage NCC to manage its network of medical devices and patient records, maintaining strict access controls to comply with regulatory requirements.

– **Retail:** A retail chain can utilize NCC to connect its stores and warehouses, optimizing network performance while safeguarding customer data.

Zero Trust with Cloud Service Mesh

What is a Cloud Service Mesh?

A Cloud Service Mesh is essentially a network of microservices that communicate with each other. It abstracts the complexity of managing service-to-service communications, offering features like load balancing, service discovery, and traffic management. The mesh operates transparently to the application, meaning developers can focus on writing code without worrying about the underlying network infrastructure. With built-in observability, it provides deep insights into how services interact, helping to identify and resolve issues swiftly.

#### Advantages of Implementing a Service Mesh

1. **Enhanced Security with Zero Trust Network**: A Service Mesh can significantly bolster security by implementing a Zero Trust Network model. This means that no service is trusted by default, and strict verification processes are enforced for each interaction. It ensures that communications are encrypted and authenticated, reducing the risk of unauthorized access and data breaches.

2. **Improved Resilience and Reliability**: By offering features like automatic retries, circuit breaking, and failover, a Service Mesh ensures that services remain resilient and reliable. It helps in maintaining the performance and availability of applications even in the face of network failures or high traffic volumes.

3. **Simplified Operations and Management**: Managing a microservices architecture can be overwhelming due to the sheer number of services involved. A Service Mesh simplifies operations by providing a centralized control plane, where policies can be defined and enforced consistently across all services. This reduces the operational overhead and makes it easier to manage and scale applications.

#### Real-World Applications of Cloud Service Mesh

Several industries are reaping the benefits of implementing a Cloud Service Mesh. In the financial sector, where security and compliance are paramount, a Service Mesh ensures that sensitive data is protected through robust encryption and authentication mechanisms. In e-commerce, it enhances the customer experience by ensuring that applications remain responsive and available even during peak traffic periods. Healthcare organizations use Service Meshes to secure sensitive patient data and ensure compliance with regulations like HIPAA.

#### Key Considerations for Adoption

While the benefits of a Cloud Service Mesh are evident, there are several factors to consider before adoption. Organizations need to assess their existing infrastructure and determine whether it is compatible with a Service Mesh. They should also consider the learning curve associated with adopting new technologies and ensure that their teams are adequately trained. Additionally, it’s crucial to evaluate the cost implications and ensure that the benefits outweigh the investment required.

Example Product: Cisco Secure Workload

### What is Cisco Secure Workload?

Cisco Secure Workload, formerly known as Cisco Tetration, is a security solution that provides visibility and micro-segmentation for applications across your entire IT environment. It leverages machine learning and advanced analytics to monitor and protect workloads in real-time, ensuring that potential threats are identified and mitigated before they can cause harm.

### Key Features of Cisco Secure Workload

1. **Comprehensive Visibility**: Cisco Secure Workload offers unparalleled visibility into your workloads, providing insights into application dependencies, communication patterns, and potential vulnerabilities. This holistic view is crucial for understanding and securing your IT environment.

2. **Micro-Segmentation**: By implementing micro-segmentation, Cisco Secure Workload allows you to create granular security policies that isolate workloads, minimizing the attack surface and preventing lateral movement by malicious actors.

3. **Real-Time Threat Detection**: Utilizing advanced machine learning algorithms, Cisco Secure Workload continuously monitors your environment for suspicious activity, ensuring that threats are detected and addressed in real-time.

4. **Automation and Orchestration**: With automation features, Cisco Secure Workload simplifies the process of applying and managing security policies, reducing the administrative burden on your IT team while enhancing overall security posture.

### Benefits of Implementing Cisco Secure Workload

– **Enhanced Security**: By providing comprehensive visibility and micro-segmentation, Cisco Secure Workload significantly enhances the security of your IT environment, reducing the risk of breaches and data loss.

– **Improved Compliance**: Cisco Secure Workload helps organizations meet regulatory requirements by ensuring that security policies are consistently applied and monitored across all workloads.

– **Operational Efficiency**: The automation and orchestration features of Cisco Secure Workload streamline security management, freeing up valuable time and resources for your IT team to focus on other critical tasks.

– **Scalability**: Whether you have a small business or a large enterprise, Cisco Secure Workload scales to meet the needs of your organization, providing consistent protection as your IT environment grows and evolves.

### Practical Applications of Cisco Secure Workload

Cisco Secure Workload is versatile and can be applied across various industries and use cases. For example, in the financial sector, it can protect sensitive customer data and ensure compliance with stringent regulations. In healthcare, it can safeguard patient information and support secure communication between medical devices. No matter the industry, Cisco Secure Workload offers a robust solution for securing critical workloads and data.

**Challenges to Consider**

While zero-trust networking offers numerous benefits, implementing it can pose particular challenges. Organizations may face difficulties redesigning their existing network architectures, ensuring compatibility with legacy systems, and managing the complexity associated with granular access controls. However, these challenges can be overcome with proper planning, collaboration, and tools.

One of the main challenges customers face right now is that their environments are changing. They are moving to cloud and containerized environments, which raises many security questions from an access control perspective, especially in a hybrid infrastructure where traditional data centers with legacy systems are combined with highly scalable systems.

An effective security posture is all about having a common way to enforce a policy-based control and contextual access policy around user and service access.

When organizations transition into these new environments, they must use multiple tool sets, which are not very contextual in their operations. For example, you may have Amazon Web Services (AWS) security groups defining IP address ranges that can gain access to a particular virtual private cloud (VPC).

This isn’t granular or has any associated identity or device recognition capability. Also, developers in these environments are massively titled, and we struggle with how to control them.

Example Technology: What is Network Monitoring?

Network monitoring involves observing and analyzing computer networks for performance, security, and availability. It consists in tracking network components such as routers, switches, servers, and applications to ensure they function optimally. Administrators can identify potential issues, troubleshoot problems, and prevent downtime by actively monitoring network traffic.

Network monitoring tools provide insights into network traffic patterns, allowing administrators to identify potential security breaches, malware attacks, or unauthorized access attempts. By monitoring network activity, administrators can implement robust security measures and quickly respond to any threats, ensuring the integrity and safety of their systems.

  • An authenticated network flow must be processed before it can be processed

Whenever a zero-trust network receives a packet, it is considered suspicious. Before data can be processed within them, they must be rigorously inspected. Strong authentication is our primary method for accomplishing this.

Authentication is required for network data to be trusted. It is possibly the most critical component of a zero-trust network. In the absence of it, we must trust the network.

  • All network flows SHOULD be encrypted before transmission

It is trivial to compromise a network link that is physically accessible to unsafe actors. Bad actors can infiltrate physical networks digitally and passively probe for valuable data by digitally infiltrating them.

When data is encrypted, the attack surface is reduced to the device’s application and physical security, which is the device’s trustworthiness.

  • The application-layer endpoints MUST perform authentication and encryption.

Application-layer endpoints must communicate securely to establish zero-trust networks since trusting network links threaten system security. When middleware components handle upstream network communications (for example, VPN concentrators or load balancers that terminate TLS), they can expose these communications to physical and virtual threats. To achieve zero trust, every endpoint at the application layer must implement encryption and authentication.

**The Role of Segmentation**

Security consultants carrying out audits will see a common theme. There will always be a remediation element; the default line is that you need to segment. There will always be the need for user and micro-segmentation of high-value infrastructure in sections of the networks. Micro-segmentation is hard without Zero Trust Network Design and Zero Trust Security Strategy.

User-centric: Zero Trust Networking (ZTN) is a dynamic and user-centric method of microsegmentation for zero trust networks, which is needed for high-value infrastructure that can’t be moved, such as an AS/400. You can’t just pop an AS/400 in the cloud and expect everything to be ok. Recently, we have seen a rapid increase in using SASE, a secure access service edge. Zero Trust SASE combines network and security functions, including zero trust networking but offering from the cloud.

Example: Identifying and Mapping Networks

To troubleshoot the network effectively, you can use a range of tools. Some are built into the operating system, while others must be downloaded and run. Depending on your experience, you may choose a top-down or a bottom-up approach.


ZERO TRUST NETWORKING • BEHAVIOUR-DRIVEN TRUST

Adaptive Risk & Traffic Flow

Zero Trust does not assume that an authenticated session remains trusted. Behaviour, identity signals and destination sensitivity can continuously change the treatment of traffic.

Learning Objective
Change behavioural signals and observe how a Zero Trust risk engine moves traffic between normal, monitored and quarantine states.
Behavioural Signals
Current Risk Score
—
NOT EVALUATED
LOW MEDIUM HIGH
Traffic —
Identity —
Authentication —
Destination —
Adaptive Traffic Decision
↗
Traffic Request
Waiting
◌
Signals
Waiting
△
Risk Engine
Waiting
◆
Policy
Waiting
⬢
Traffic Action
Waiting
Adaptive Decision
READY
Policy Explanation
Change the behavioural signals and evaluate the request.
Risk Decision Console
[SYSTEM] Risk engine ready.
[POLICY] Awaiting behavioural telemetry.
Engineering Takeaway
Zero Trust can continuously change the treatment of traffic as risk changes.

Zero Trust Networking

Traditional network security

Traditional network security architecture breaks different networks (or pieces of a single network) into zones contained by one or more firewalls. Each zone is granted some level of trust, determining the network resources it can reach. This model provides solid defense in depth. For example, resources deemed riskier, such as web servers that face the public internet, are placed in an exclusion zone (often termed a “DMZ”), where traffic can be tightly monitored and controlled.

Critical Principles of Zero Trust Networking:

1. Least Privilege: Zero trust networking enforces the principle of least privilege, ensuring that users and devices have only the necessary permissions to access specific resources. Limiting access rights significantly reduces the potential attack surface, making it harder for malicious actors to exploit vulnerabilities.

2. Microsegmentation: Zero trust networking leverages microsegmentation to divide the network into smaller, isolated segments or zones. Each segment is an independent security zone with access policies and controls. This approach minimizes lateral movement within the network, preventing attackers from traversing and compromising sensitive assets.

3. Continuous Authentication: In a zero-trust networking environment, continuous authentication is pivotal in ensuring secure access. Traditional username and password credentials are no longer sufficient. Instead, multifactor authentication, behavioral analytics, and other advanced authentication mechanisms are implemented to verify the legitimacy of users and devices consistently.

Benefits of Zero Trust Networking:

1. Enhanced Security: Zero trust networking provides organizations with an enhanced security posture by eliminating the assumption of trust. This approach mitigates the risk of potential breaches and reduces the impact of successful attacks by limiting lateral movement and isolating critical assets.

2. Improved Compliance: With the growing number of stringent data protection regulations, such as GDPR and CCPA, organizations are under increased pressure to ensure data privacy and security. Zero trust networking helps meet compliance requirements by implementing granular access controls, auditing capabilities, and data protection measures.

3. Increased Flexibility: Zero-trust networking enables organizations to embrace modern workplace trends, such as remote work and cloud computing, without compromising security. It facilitates secure access from any location or device by focusing on user and device authentication rather than network location.

Example – What is Port Knocking?

Port knocking is an externally opening specific ports on a computer or network by sending a series of connection attempts to predefined closed ports. This sequence of connection attempts serves as a “knock” that triggers the firewall to allow access to desired services or ports.

To understand the mechanics of port knocking, imagine a locked door with a secret knock. Similarly, a server with port knocking enabled will have closed ports acting as a locked door. Only when the correct sequence of connection attempts is detected will the desired ports be opened, granting access to the authorized user.

Microsegmentation for Zero Trust Networks

Suppose we roll back the clock. VLANs were never used for segmentation. Their sole purpose was to divide broadcast domains and improve network performance. The segmentation piece came much later on. Access control policies were carried out on a port-by-port and VLAN-by-VLAN basis. This would involve the association of a VLAN with an IP subnet to enforce subnet control, regardless of who the users were.

Also, TCP/IP was designed in a “safer” world based on an implicit trust mode of operation. It has a “connect first and then authenticate second” approach. This implicit trust model can open you up to several compromises. Zero Trust and Zero Trust SDP change this model to “authenticate first and then connect.”

It is based on the individual user instead of the more traditional IP addresses and devices. In addition, firewall rules are binary and static. They state that this IP block should have access to this network (Y/N). That’s not enough, as today’s environment has become diverse and distributed.

Let us face it. Traditional constructs have not kept pace or evolved with today’s security challenges. The perimeter is gone, so we must keep all services ghosted until efficient contextual policies are granted.

Trust and Verify Model vs. Zero Trust Networking (ZTN)

If you look at how VPN has worked, you have this trust and verify model, connect to the network, and then you can be authorized. The problem with this approach is that you can already see much of the attack surface from an external perspective. This can potentially be used to move laterally around the infrastructure to access critical assets.

Zero trust networking capabilities are focused more on a contextual identity-based model. For example, who is the user, what are they doing, where are they coming in from, is their endpoint up to date from threat posture perspectives, and what is the rest of your environment saying about these endpoints?

Once all this is done, they are entitled to communicate, like granting a conditional firewall rule based on a range of policies, not just a Y/N. For example, has there been a malware check at the last minute, a 2-factor authentication process, etc.?

I envision a Zero Trust Network ZTN solution with several components. A client will effectively communicate with a controller and then a gateway. The gateway acts as the enforcement point used to segment the infrastructure you seek to protect logically. The enforcement point could be in front of a specific set of applications or subnets you want to segment.

Zero-trust networking provides a proactive and comprehensive security approach in a rapidly evolving threat landscape. By embracing the principles of least privilege, microsegmentation, and continuous authentication, organizations can enhance their security posture and protect their critical assets from internal and external threats. As technology advances, adopting zero-trust networking is not just a best practice but a necessity in today’s digital age.


Zero Trust Networking · Block 3

Segmentation & Policy Enforcement

Apply identity, device posture, resource sensitivity and privilege controls to determine whether traffic crosses a Zero Trust policy boundary.

Learning Objective
Understand how Zero Trust segmentation converts contextual security signals into an explicit allow or deny enforcement decision.
Policy Inputs
Segmentation Decision
AWAITING EVALUATION
Configure the policy inputs and evaluate the request.
Evidence will appear here after the policy engine evaluates the request.
Enforcement Path
User / Device
Identity + posture
→
Policy Boundary
Segmentation engine
→
Protected Resource
Application / database / asset
Policy Evaluation Console
[SYSTEM] Zero Trust segmentation engine ready. [SYSTEM] Awaiting access request.
Engineering Takeaway
Zero Trust segmentation does not simply ask whether a user is authenticated. It evaluates identity, device posture, requested resource and privilege together. The policy boundary then determines exactly which traffic is permitted to cross into the protected zone.
Docker Container Diagram

Container Based Virtualization

Container Based Virtualization

Container-based virtualization, or containerization, is a popular technology revolutionizing how we deploy and manage applications. In this blog post, we will explore what container-based virtualization is, why it is gaining traction, and how it differs from traditional virtualization techniques.

Container-based virtualization is a lightweight alternative to traditional methods such as hypervisor-based virtualization. Unlike virtual machines (VMs), which require a separate operating system (OS) instance for each application, containers share the host OS. This means containers can be more efficient regarding resource utilization and faster to start and stop.

Container-based virtualization, also known as operating system-level virtualization, is a lightweight virtualization method that allows multiple isolated user-space instances, known as containers, to run on a single host operating system. Unlike traditional virtualization techniques, which rely on hypervisors and full-fledged guest operating systems, containerization leverages the host operating system's kernel to provide resource isolation and process separation. This streamlined approach eliminates the need for redundant operating system installations, resulting in improved performance and efficiency.

Enhanced Portability: Containers encapsulate all the dependencies required to run an application, making them highly portable across different environments. Developers can package their applications with all the necessary libraries, frameworks, and configurations, ensuring consistent behavior regardless of the underlying infrastructure.

Scalability and Resource Efficiency: Containers enable efficient resource utilization by sharing the host's operating system and kernel. With their lightweight nature, containers can be rapidly provisioned, scaled up or down, and migrated across hosts, ensuring optimal resource allocation and responsiveness.

Isolation and Security: Containers provide isolation at the process level, ensuring that each application runs in its own isolated environment. This isolation prevents interference and minimizes security risks, making container-based virtualization an attractive choice for multi-tenant environments and cloud-native applications.

Container-based virtualization has gained significant traction across various industries and use cases. Some notable examples include:

Microservices Architecture: Containerization seamlessly aligns with the principles of microservices, allowing applications to be broken down into smaller, independent services. Each microservice can be encapsulated within its own container, enabling rapid development, deployment, and scaling.

DevOps and Continuous Integration/Continuous Deployment (CI/CD): Containers play a crucial role in modern DevOps practices, streamlining the software development lifecycle. With container-based virtualization, developers can easily package, test, and deploy applications across different environments, ensuring consistency and reducing deployment complexities.

Hybrid and Multi-Cloud Environments: Containers facilitate hybrid and multi-cloud strategies by abstracting away the underlying infrastructure dependencies. Applications can be packaged as containers and seamlessly deployed across different cloud providers or on-premises environments, enabling flexibility and avoiding vendor lock-in.

Container Virtualization Lab

Containers vs VMs: What Actually Changes?

Experiment with the virtualization boundary. See how workload density, isolation and resource overhead change when the same application set is deployed as containers or virtual machines.

4
Medium
Virtualization Boundary Ready
Physical / Cloud Host
Hypervisor layer
Shared host operating-system kernel
Workloads 4
Resource Overhead Low
Isolation Process
Density High
[ready] Architecture waiting for evaluation.
Engineering Insight

Containers generally reduce per-workload overhead by sharing the host kernel, while VMs provide a stronger virtualization boundary by virtualizing complete guest operating systems.

Conceptual simulation for learning. Real isolation, performance and security depend on the runtime, kernel configuration, hardware, workload and deployment architecture.

Highlights: Container Based Virtualization

What is Container-Based Virtualization?

Container-based virtualization, also known as operating-system-level virtualization, is a lightweight approach to virtualization that allows multiple isolated containers to run on a single host operating system. Unlike traditional virtualization techniques, containerization does not require a full-fledged operating system for each container, resulting in enhanced efficiency and performance.

Unlike traditional hypervisor-based virtualization, which relies on full-fledged virtual machines, containerization offers a more lightweight and efficient approach. Containers share the host OS kernel, resulting in faster startup times, reduced resource overhead, and improved overall performance.

Benefits:

Increased Resource Utilization: By sharing the host operating system, containers can efficiently use system resources, leading to higher resource utilization and cost savings.

Rapid Deployment and Scalability: Containers offer fast deployment and scaling capabilities, enabling developers to quickly build, deploy, and scale applications in seconds. This agility is crucial in today’s fast-paced development environments.

Isolation and Security: Containers provide a high level of isolation between applications, ensuring that one container’s activities do not affect others. This isolation enhances security and minimizes the risk of system failures.

Use Cases:

Microservices Architecture: Containerization plays a vital role in microservices architecture. Developers can independently develop, test, and deploy services by encapsulating each microservice within its container, increasing flexibility and scalability.

Cloud Computing: Container-based virtualization is widely used in cloud computing platforms. It allows users to deploy applications seamlessly across different cloud environments, making migrating and managing workloads easier.

DevOps and Continuous Integration/Continuous Deployment (CI/CD): Containerization is a crucial enabler of DevOps practices. With container-based virtualization, developers can ensure consistency in development, testing, and production environments, enabling smoother CI/CD workflows.

**Container Management and Orchestration**

Managing containers at scale necessitates the use of orchestration tools, with Kubernetes being one of the most popular options. Kubernetes automates the deployment, scaling, and management of containerized applications, providing a robust framework for managing large clusters of containers. It handles tasks like load balancing, scaling applications up or down based on demand, and ensuring the desired state of the application is maintained, making it indispensable for organizations leveraging container-based virtualization.

**Security Considerations in Containerization**

While containers offer numerous advantages, they also introduce unique security challenges. The shared kernel architecture, while efficient, necessitates stringent security measures to prevent vulnerabilities. Ensuring that container images are secure, implementing robust access controls, and regularly updating and patching container environments are critical steps in safeguarding containerized applications. Tools and best practices specifically designed for container security are vital components of a comprehensive security strategy.

Container Networking

Docker Networks

Container networking refers to the communication and connectivity between containers within a containerized environment. It allows containers to interact with each other and external networks and services. Isolating network resources for each container enables secure and efficient data exchange.

In this section, we will explore some essential concepts in container networking:

1. Network Namespaces: Container runtimes use network namespaces to create isolated container network environments. Each container has its network namespace, providing separation and isolation.

2. Bridge Networks: Bridge networks serve as a virtual bridge connecting containers within the same host. They enable container communication by assigning unique IP addresses and facilitating network traffic routing.

3. Overlay Networks: Overlay networks connect containers across multiple hosts or nodes in a cluster. They provide a seamless communication layer, allowing containers to communicate as if they were on the same network.

Docker Default Networking

Docker default networking is an essential feature that enables containerized applications to communicate with each other and the outside world. By default, Docker provides three types of networks: bridge, host, and none. These networks serve different purposes and have distinct characteristics.

– The bridge network is Docker’s default networking mode. It creates a virtual network interface on the host machine, allowing containers to communicate with each other through this bridge. By default, containers connected to the bridge network can reach each other using their IP addresses.

– The host network mode allows containers to bypass the isolation provided by Docker networking and use the host machine’s network directly. When a container uses the host network, it shares the same network namespace as the host, resulting in improved network performance but sacrificing the container’s isolation.

– The non-network mode completely isolates the container from network access. Containers using this mode have no network interfaces and cannot communicate with the outside world or other containers. This mode is useful for scenarios where network access is not required.

Docker provides various options to customize default networking behavior. You can create custom bridge networks, define IP ranges, configure DNS resolution, and map container ports to host ports. Understanding these configuration options empowers you to design networking setups that align with your application requirements.

Application Landscape Changes

The application landscape has changed from a monolithic design to a design consisting of microservices. Today, applications are constantly developed. Patches usually patch only certain parts of the application, and the entire application is built from loosely coupled components instead of existing tightly coupled ones. The entire application stack is broken into components and spread over multiple servers and locations, all requiring cross-communication. For example, users connect to a presentation layer, the presentation layer then connects to some shopping cart, and the shopping cart connects to a catalog library.

These components are potentially stored on different servers, maybe different data centers. The application is built from several small parts, known as microservices. Each component or microservice can now be put into a lightweight container—a scaled-down VM. VMware and KVM are virtualization systems that allow you to run Linux kernels and operating systems on top of a virtualized layer, commonly known as a hypervisor. Because each VM is based on its operating system kernel in its memory space, this approach provides extreme isolation between workloads.

Containers differ fundamentally from shared kernel systems since they implement isolation between workloads entirely within the kernel. This is called operating system virtualization.

A major advantage of containers is resource efficiency since each isolated workload does not require a whole operating system instance. Sharing a kernel reduces the amount of indirection between isolated tasks and their real hardware. The kernel only manages a container when a process is running inside a container. Unlike a virtual machine, an actual machine has no second layer. The process would have to bounce into and out of privileged mode twice when calling the hardware or hypervisor in a VM, significantly slowing down many operations.

Traditional Deployment Models

So, how do containers facilitate virtualization? Traditional application deployment was based on a single-server approach. As a result, one application was installed per physical server, wasting server resources, and components such as RAM and CPU were never fully utilized. There was also considerable vendor lock-in, making moving applications from one hardware vendor to another hard.

Then, the world of hypervisor-based virtualization was introduced, and the concept of a virtual machine (VM) was born. Soon after, we had container-based applications. Container-based virtualization introduced container networking, and new principles arose for security around containers, specifically, Docker container security.

container security

Introducing hypervisors

We still deployed physical servers but introduced hypervisors on the physical host, enabling the installation of multiple VMs on a single server. Each VM is isolated from its operating system. Hypervisor-based virtualization introduced better resource pooling as one physical server could now be divided into multiple VMs, each hosting a different application type. This was years better than single-server deployments and opened the doors to open networking. 

The VM deployment approach increased agility and scalability, as applications within a VM are scaled by simply spinning up more VMs on any physical host. While hypervisor-based virtualization was a step in the right direction, a guest operating system for each application is pretty intensive. Each VM requires RAM, CPU, storage, and an entire guest OS, all-consuming resources.

Introducing Virtualization

Another advantage of virtualization is the ability to isolate applications or services. Each virtual machine operates independently, with its resources and configurations. This enhances security and stability, as issues in one virtual machine do not affect others. It also allows for easy testing and development, as virtual machines can be quickly created and discarded.

Virtualization also offers improved disaster recovery and business continuity. By encapsulating the entire virtual machine, including its operating system, applications, and data, into a single file, organizations can quickly back up, replicate, and restore virtual machines. This ensures that critical systems and data are protected and can rapidly recover during a failure or disaster.

Furthermore, virtualization enables workload balancing and dynamic resource allocation. Virtual machines can be dynamically migrated between physical servers to optimize resource utilization and performance. This allows for better utilization of computing resources and the ability to respond to changing workload demands.

Container Orchestration

**What is Google Kubernetes Engine?**

Google Kubernetes Engine is a managed environment for deploying, managing, and scaling containerized applications using Google infrastructure. GKE is built on Kubernetes, an open-source container orchestration system that automates the deployment, scaling, and management of containerized applications. With GKE, developers can focus on building applications without worrying about the complexities of managing the underlying infrastructure.

**The Benefits of Container-Based Virtualization**

Container-based virtualization is a game-changer in the world of cloud computing. Unlike traditional virtual machines, containers are lightweight and share the host system’s kernel, leading to faster start-up times and reduced overhead. GKE leverages this technology to offer seamless scaling and efficient resource utilization. This means businesses can run more applications on fewer resources, reducing costs and improving performance.

**GKE Features: What Sets It Apart?**

One of GKE’s standout features is its ability to auto-scale, which ensures that applications can handle varying loads by automatically adjusting the number of running instances. Additionally, GKE provides robust security features, including vulnerability scanning and automated updates, safeguarding your applications from potential threats. The integration with other Google Cloud services also enhances its functionality, offering a comprehensive suite of tools for developers.

**Getting Started with GKE**

For businesses looking to harness the potential of Google Kubernetes Engine, getting started is straightforward. Google Cloud provides extensive documentation and tutorials, making it easy for developers to deploy their first applications. With its intuitive user interface and powerful command-line tools, GKE simplifies the process of managing containerized applications, even for those new to Kubernetes.

Google Kubernetes EngineUnderstanding Docker Swarm

Docker Swarm provides native clustering and orchestration capabilities for Docker. It allows you to create and manage a swarm of Docker nodes, forming a single virtual Docker host. By leveraging the power of swarm mode, you can seamlessly deploy and manage containers across a cluster of machines, enabling high availability, fault tolerance, and scalability.

One of Docker Swarm’s key features is its simplicity. With just a few commands, you can initialize a swarm, join nodes to the swarm, and deploy services across the cluster. Additionally, Swarm provides load balancing, automatic container placement, rolling updates, and service discovery, making it an ideal choice for managing and scaling containerized applications.

Scaling Services with Docker Swarm

To create a Docker Swarm, you need at least one manager node and one or more worker nodes. The manager node acts as the central control plane, handling service orchestration and managing the swarm’s state. On the other hand, Worker nodes execute the tasks assigned to them by the manager. Setting up a swarm allows you to distribute containers across the cluster, ensuring efficient resource utilization and fault tolerance.

One of Docker Swarm’s significant benefits is its ability to deploy and scale services effortlessly. With a simple command, you can create a service, specify the number of replicas, and let Swarm distribute the workload across the available nodes. Scaling a service is as simple as updating the desired number of replicas, and Swarm will automatically adjust the deployment accordingly, ensuring high availability and efficient resource allocation.

Docker Swarm is a native clustering and orchestration solution for Docker. It allows you to create and manage a swarm of Docker nodes, enabling the deployment and scaling of containers across multiple machines. With its simplicity and ease of use, Docker Swarm is an excellent choice for those looking to dive into container orchestration without a steep learning curve.

The Power of Kubernetes

Kubernetes, often called “K8s,” is an open-source container orchestration platform developed by Google. It provides a robust and scalable solution for managing containerized applications. With its advanced features, such as automatic scaling, load balancing, and self-healing capabilities, Kubernetes has gained widespread adoption in the industry.

Example Technology: Virtual Switching 

Understanding Open vSwitch

Open vSwitch, called OVS, is an open-source virtual switch that efficiently creates and manages virtual networks. It operates at the data link layer of the networking stack, enabling seamless communication between virtual machines, containers, and physical network devices. With extensibility in mind, OVS offers a wide range of features contributing to its popularity and widespread adoption.

– Flexible Network Topologies: One of the standout features of Open vSwitch is its ability to support a variety of network topologies. Whether a simple flat network or a complex multi-tiered architecture, OVS provides the flexibility to design and deploy networks that suit specific requirements. This level of adaptability makes it a preferred choice for cloud service providers, data centers, and enterprises seeking dynamic network setups.

– Virtual Network Overlays: Open vSwitch enables virtual network overlays, allowing multiple virtual networks to coexist and operate independently on the same physical infrastructure. By leveraging technologies like VXLAN, GRE, and Geneve, OVS facilitates the creation of isolated network segments that are transparent to the underlying physical infrastructure. This capability simplifies network management and enhances scalability, making it an ideal solution for cloud environments.

– Flow-based Forwarding: Flow-based forwarding is a powerful mechanism provided by Open vSwitch. It allows for fine-grained control over network traffic by defining flows based on specific criteria such as source/destination IP addresses, ports, protocols, and more. This granular control enables efficient traffic steering, load balancing, and network monitoring, enhancing performance and security.

Controlling Security

Understanding SELinux

SELinux, which stands for Security-Enhanced Linux, is a security framework built into the Linux kernel. It provides a fine-grained access control mechanism beyond traditional discretionary access controls (DAC). SELinux implements mandatory access controls (MAC) based on the principle of least privilege. This means that processes and users are granted only the bare minimum permissions required to perform their tasks, reducing the potential attack surface.

Container-based virtualization has revolutionized the way applications are deployed and managed. However, it also introduces new security challenges. This is where SELinux shines. By enforcing strict access controls on container processes and limiting their capabilities, SELinux helps prevent unauthorized access and potential exploits. It adds an extra layer of protection to the container environment, making it more resilient against attacks.

Container Networking Lab

How Does the Network Change the Container Boundary?

Change the network model and traffic requirement to see how containers gain connectivity, isolation and multi-host reachability. The simulation is conceptual: real implementations depend on the runtime, CNI, host networking and platform configuration.

Logical Network Path
Network Boundary
A
App Container Network namespace
⇄
Virtual Network Bridge / veth path
B
Target Container Application endpoint
Namespace Isolation Medium
Network Scope Single Host
Cross-Host Not Available
Port Mapping Not Required
Segmentation Shared Network
Connectivity Result Not tested
Network Reachability 0%
Isolation Strength 0%
Network Event Console
[ready] Experiment waiting for configuration.
Engineering Insight
Choose a network model and traffic scope, then run the test.
Educational simulation only. Network behaviour varies by container runtime, CNI/plugin, host configuration, routing, firewalling and orchestration platform.

Container Based Virtualization

The Traditional World

Before we address how containers facilitate virtualization, let’s address the basics. In the past, we could solely run one application per server. However, the open-systems world of Windows and Linux didn’t have the technologies to safely and securely run multiple applications on the same server.

So, whenever we needed a new application, we would buy a new server. We had the virtual machine (VM) to solve the waste of resources. With the VM, we had a technology that permitted us to safely and securely run applications on a single server. Unfortunately, the VM model also has additional challenges.

Migrating VMs

For example, VMs are slow to boot, and portability isn’t great — migrating and moving VM workloads between hypervisors and cloud platforms is more complicated than it needs to be. All of these factors drove the need for new container technology with container virtualization.

How do containers facilitate virtualization? We needed a lightweight tool without losing the scalability and agility benefits of the VM-based application approach. The lightweight tool is container-based virtualization, and Docker is at the forefront. The container offers a similar capability to object-oriented programming. It lets you build composable modular building blocks, making it easier to design distributed systems.

Docker Container Diagram
Diagram: Docker Container. Source Docker.

Container Networking

In the following example, we have one Docker host. We can list the available networks for these Docker hosts with the command docker network ls. These are not WAN or VPN networks; they are only Docker networks.

Docker networks are virtual networks that allow containers to communicate with each other and the outside world. They provide isolation, security, and flexibility to manage network traffic flow between containers. By default, when you create a new Docker container, it is connected to a default bridge network, which allows communication with other containers on the same host.

Notice the subnets assigned of 172.17.0.0/16. So, the default gateway ( exit point) is set to the docker0 bridge.

Docker networking
Diagram: Docker networking

Types of Docker Networks:

Docker offers various types of networks, each serving a specific purpose:

1. Bridge Network:

The bridge network is the default network that enables communication between containers on the same host. Containers connected to the bridge network can communicate using IP addresses or container names. It provides a simple way to connect containers without exposing them to the outside world.

2. Host Network:

In the host network mode, a container shares the network stack with the host, using its network interface directly. This mode provides maximum network performance as no network address translation (NAT) is involved. However, it also means the container is directly exposed to the host’s network, potentially introducing security risks.

3. Overlay Network:

The overlay network allows containers to communicate across multiple Docker hosts, even in different physical or virtual networks. It achieves this by encapsulating network packets and routing them to the appropriate destination. Overlay networks are essential for creating distributed and scalable applications.

4. Macvlan Network:

The Macvlan network mode allows containers to have MAC addresses and appear as separate devices. This mode is useful when assigning IP addresses to containers and making them accessible from the external network. It is commonly used when containers must be treated as physical devices.

5. None Network:

The non-network mode isolates a container from all networking. It effectively disables all networking capabilities and prevents the container from communicating with other containers or the outside world. This mode is typically used when networking is not required or desired.

Guide Container Networking

You can attach as many containers as you like to a bridge. They will be assigned IP addresses within the same subnet, meaning they can communicate by default. You can have a container with two Ethernet interfaces ( virtual interfaces ) connected to two different bridges on the same host and have connectivity to two networks simultaneously.

Also, remember that the scope is local when you are doing this, and even if the docker hosts are on the same underlying network but with different hosts, they won’t have IP reachability. In this case, you may need a VXLAN overlay network to connect containers on different docker hosts.

inspecting container networks
Diagram: Inspecting container networks

Container-based Virtualization

One critical benefit of container-based virtualization is its portability. Containers encapsulate the application and all its dependencies, allowing it to run consistently across different environments, from development to production. This portability eliminates the “it works on my machine” problem and makes it easier to maintain and scale applications.

  • Scalability

Another advantage of containerization is its scalability. Containers can be easily replicated and distributed across multiple hosts, making it straightforward to scale applications horizontally. Furthermore, container orchestration platforms, like Kubernetes, provide automated management and scaling of containers, simplifying the deployment and management of complex applications.

  • Security

Security is crucial to any virtualization technology, and container-based virtualization is no exception. Containers provide isolation between applications, preventing them from interfering with each other. However, it is essential to note that containers share the same kernel as the host OS, which means a compromised container can potentially impact other containers. Proper security measures, such as regular updates and vulnerability scanning, are essential to ensure the security of containerized applications.

  • Tooling

Container-based virtualization also offers various tools and platforms for application development and deployment. Docker, for example, is a popular containerization platform that provides a user-friendly interface for building, running, and managing containers. It simplifies container image creation and enables developers to package their applications and dependencies.

Understanding Kubernetes Networking Architecture

Kubernetes networking architecture comprises several crucial components that enable seamless communication between pods, services, and external resources. The fundamental building blocks of Kubernetes networking include pods, nodes, containers, and the Container Network Interface (CNI). r.

Network security is paramount to any Kubernetes deployment. Network policies provide a powerful tool to control ingress and egress traffic, enabling fine-grained access control between pods. Kubernetes has the concept of network policies and demonstrates how to define and enforce them to enhance the security posture of your Kubernetes cluster.  

Applications of Container-Based Virtualization:

1. DevOps and Continuous Integration/Continuous Deployment (CI/CD): Containerization enables developers to package applications, libraries, and configurations into portable and reproducible containers. This simplifies the deployment process and ensures consistency across different environments, facilitating faster software delivery.

2. Microservices Architecture: Container-based virtualization aligns well with the microservices architectural pattern. Organizations can develop, deploy, and scale each service independently using containers by breaking down complex applications into more minor, loosely coupled services. This approach enhances modularity, scalability, and fault tolerance.

3. Hybrid Cloud and Multi-Cloud Environments: Containers provide a unified platform for deploying applications across hybrid and multi-cloud environments. With container orchestration tools, organizations can leverage the benefits of multiple cloud providers while ensuring consistent deployment and management practices.

How do containers facilitate virtualization?

  • Container-Based Applications

Now, we have complex distributed software stacks based on microservices. Its base consists of loosely coupled components that may change and software that runs on various hardware, including test machines, in-house clusters, cloud deployments, etc. The web front end may include the following:

  • Ruby + Rail.
  • API endpoints with Python 2.7.
  • Stack website with Nginx.
  • A variety of databases.

We have a very complex stack on top of various hardware devices. While the traditional monolithic application will likely remain for some time, containers still exhibit the use case to modernize the operational model for conventional stacks. Both monolithic and container-based applications can live together.

The application’s complexity, scalability, and agility requirements have led us to the market of container-based virtualization. Container-based virtualization uses the host’s kernel to run multiple guest instances. Now, we can run multiple guest instances (containers), and each container will have its root file system, process, and network stack.

Containers allow you to package an application with all its parts in an isolated environment. They are a complete abstraction and do not need to run dependencies on the hosts. Docker, a type of container (first based on Linux Containers but now powered by runC), separates the application from infrastructure using container technologies. 

Similar to how VMs separate the operating system from bare metal, containers let you build a layer of isolation in software that reduces the burden of human communication and specific workflows. An excellent way to understand containers is to accept that they are not VMs—they are simple wrappers around a single Unix process. Containers contain everything they need to run (runtime, code, libraries, etc.).

Linux kernel namespaces

Isolation or variants of isolation have been around for a while. We have mount namespacing in 2.4 kernels and userspace namespacing in 3.8. These technologies allow the kernel to create partitions and isolate PIDs. Linux containers (Lxc) started in 2008, and Docker was introduced in Jan 2013, with a public release of 1.0 in 2014. We are now at version 1.9, which has some new networking enhancements.

Docker uses Linux kernel namespaces and control groups, providing an isolated workspace, which offers the starting grounds for the Docker security options. Namespaces offer an isolated workspace that we call a container. They help us fool the container.

We have PID for process isolation, MOUNT for storage isolation, and NET for network-level isolation. The Linux network subsystem has the correct information for additional Linux network information.

Container-based application: Container operations

Containers use schedulers. A scheduler starts containers on the correct host and then connects them. It also needs to manage container failover and handle container scalability when there is too much data to process for a single instance. Popular container schedulers include Docker Swarm, Apache Mesos, and Google Kubernetes.

The correct host is selected depending on the type of scheduler used. For example, Docker Swarm will have three strategies: spread, binpack, and random. Spread means node selection is based on the fewest containers, disregarding their states. Binpack selection is based on hosts with minimum resources, i.e., the most packed. Finally, random strategy selections are chosen randomly.

Containers are quick to start.

How do containers facilitate virtualization? First, they are quick. Starting a container is much faster than starting a VM—lightweight containers can be started in as little as 300ms. Initial tests on Docker revealed that a newly created container from an existing image takes up only 12 kilobytes of disk space.

A VM could take up thousands of megabytes. The container is lightweight, as its references point to a layered filesystem image. Container deployment is also swift and network-efficient.

Fewer data needs to travel across the network and storage fabrics. Elastic applications that have frequent state changes can be built more efficiently. Both Docker and Linux containers fundamentally change application consumption. 

As a side note, not all workloads are suitable for containers, and heavy loads like databases are put into VMs to support multi-cloud environments. 

Docker networking

Docker networking is an essential aspect of containerization that allows containers to communicate with each other and external networks. In this document, we will explore the different networking options available in Docker and how they can facilitate seamless communication between containers.

By default, Docker provides three networking options: bridge, host, and none. The bridge network is the default network created when Docker is installed. It allows containers to communicate with each other using IP addresses. Containers within the same bridge network can communicate with each other directly without the need for port mapping.

As the name suggests, the host network allows containers to share the network namespace with the host system. This means containers using the host network can directly access the host system’s interfaces. This option is helpful for scenarios where containers must bind to specific network interfaces on the host.

On the other hand, the non-network option completely isolates the container from the network. Containers using the none network cannot communicate with other containers or external networks. This option is useful when running a container in complete isolation.

Creating custom networks

In addition to these default networking options, Docker also provides the ability to create custom networks. Custom networks allow containers to communicate with each other, even if they are not in the same network namespace. Custom networks can be made using the `docker network create` command, specifying the desired driver (bridge, overlay, macvlan, etc.) and any additional options.

One of the main benefits of using custom networks is the ability to define network-level access control. Docker provides the ability to define network policies using network labels. These labels can control which containers can communicate with each other and which ports are accessible.

Closing Points on Docker networking

Networking is very different in Docker than what we are used to. Networks are domains that interconnect sets of containers. So, if you give access to a network, you can access all containers. However, you must specify rules and port mapping if you want external access to other networks or containers.

A driver backs every network, be it a bridge or overlay driver. These Docker-based drivers can be swapped out with any ecosystem driver. The team at Docker views them as pluggable batteries.

Docker utilizes the concept of scope—local (default) and Global. The local scope is a local network, and the global scope has visibility across the entire cluster. If your driver is a global scope driver, your network belongs to a global scope. A local scope driver corresponds to the local scope.

Containers and Microsegmentation

Microsegmentation is a security technique that divides a network into smaller, isolated segments, allowing organizations to create granular security policies. This approach provides enhanced control and visibility over network traffic, preventing lateral movement and limiting the impact of potential security breaches.

Microsegmentation offers organizations a proactive approach to network security, allowing them to create an environment more resilient to cyber threats. By implementing microsegmentation, organizations can enhance their security posture, minimize the risk of lateral movement, and protect their most critical assets. As the cyber threat landscape continues to evolve, microsegmentation is an effective strategy to safeguard network infrastructure in an increasingly interconnected world.

  • Docker and Micro-segmentation

Docker 0 is the default bridge. They have now extended into bundles of multiple networks, each with independent bridges. Different bridges cannot directly talk to each other. It is a private, isolated network offering micro-segmentation and multi-tenancy features.

The only way for them to communicate is via host namespace and port mapping, which is administratively controlled. Docker multi-host networking is a new feature in 1.9. A multi-host network comprises several docker hosts that form a cluster.

Several containers in each host form the cluster by pointing to the same KV (example -zookeeper) store. The KV store that you point to defines your cluster. Multi-host networking enables the creation of different topologies and lets the container belong to several networks. The KV store may also be another container, allowing you to stay in a 100% container world.

Final points on container-based virtualization

In recent years, container-based virtualization has become famous for deploying and managing applications. Unlike traditional virtualization, which relies on hypervisors to run multiple virtual machines on a single physical server, container-based virtualization leverages lightweight, isolated containers to run applications.

So, what exactly is container-based virtualization, and why is it gaining traction in the technology industry? In this blog post, we will explore the concept of container-based virtualization, its benefits, and how it differs from traditional virtualization.

Operating system-level virtualization

Container-based virtualization, also known as operating system-level virtualization, is a form of virtualization that allows multiple containers to run on a single operating system kernel. Each container is isolated from the others, ensuring that applications and their dependencies are encapsulated within their runtime environment. This isolation eliminates application conflicts and provides a consistent environment across deployment platforms.

Docker default networking 101
Diagram: Docker default networking 101

Critical advantages of container virtualization

One critical advantage of container-based virtualization is its lightweight nature. Containers are designed to be portable and efficient, allowing for rapid application deployment and scaling. Unlike virtual machines, which require an entire operating system to run, containers share the host operating system kernel, reducing resource overhead and improving performance.

Another benefit of container-based virtualization is its ability to facilitate microservices architecture. By breaking down applications into more minor, independent services, containers enable developers to build and deploy applications more efficiently. Each microservice can be encapsulated within its container, making it easier to manage and update without impacting other application parts.

Greater flexibility and scalability

Moreover, container-based virtualization offers greater flexibility and scalability. Containers can be easily replicated and distributed across hosts, allowing for seamless horizontal scaling. This ability to scale quickly and efficiently makes container-based virtualization ideal for modern, dynamic environments where applications must adapt to changing demands.

Container virtualization is not a complete replacement.
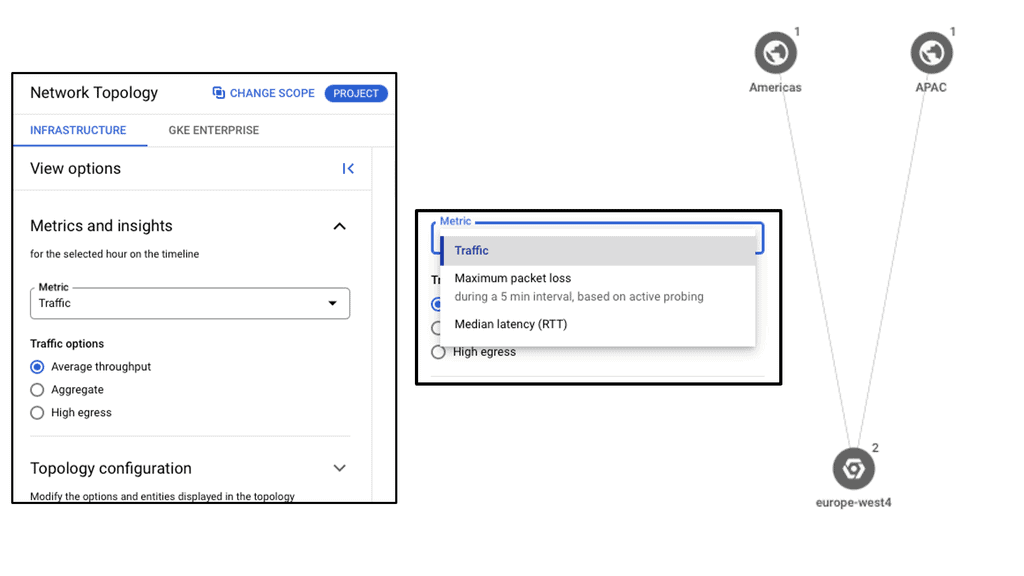
It’s important to note that container-based virtualization is not a replacement for traditional virtualization. Instead, it complements it. While traditional virtualization is well-suited for running multiple operating systems on a single physical server, container-based virtualization is focused on maximizing resource utilization within a single operating system.

In conclusion, container-based virtualization has revolutionized application deployment and management. Its lightweight nature, isolation capabilities, and scalability make it a compelling choice for modern software development and deployment. As technology continues to evolve, container-based virtualization will likely play a significant role in shaping the future of application deployment.
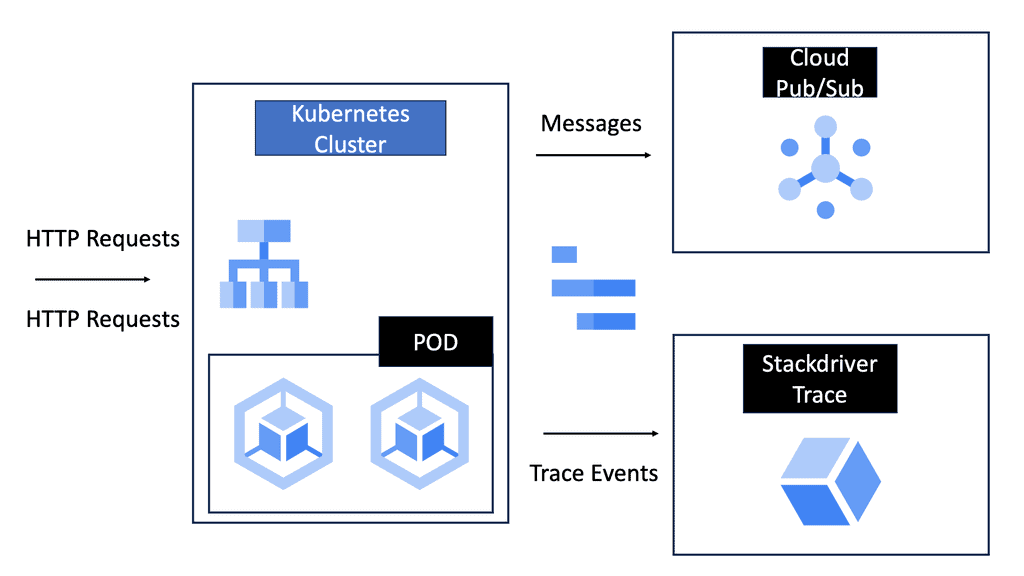
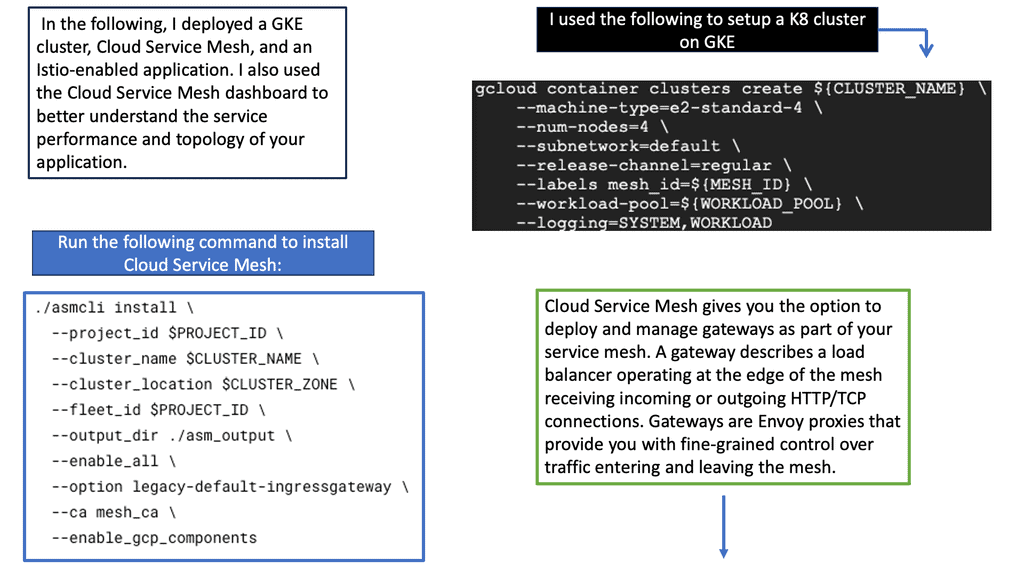
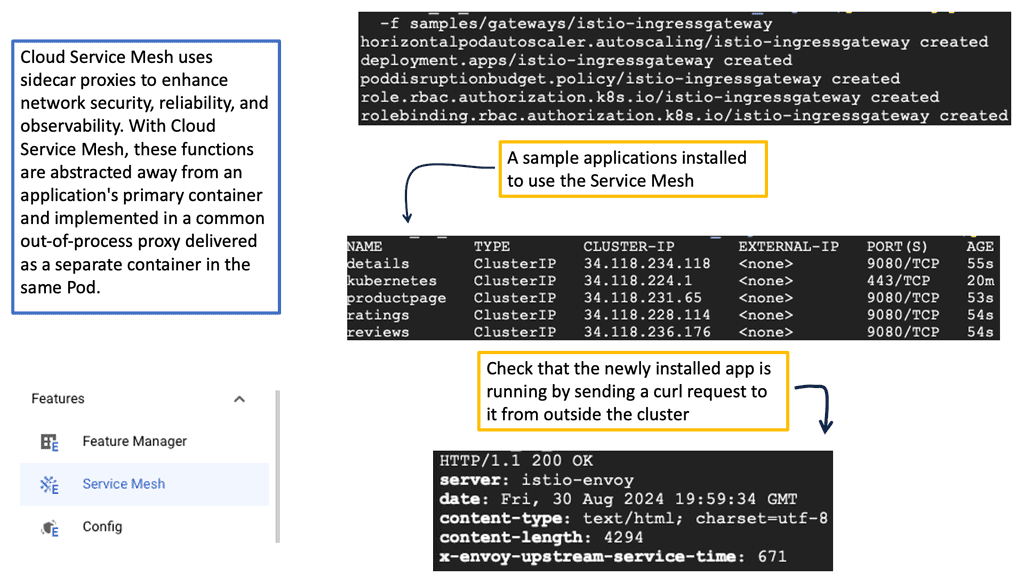
Container-based virtualization has transformed how we develop, deploy, and manage applications. Its lightweight nature, scalability, portability, and isolation capabilities make it an attractive choice for modern software development. By adopting containerization, organizations can achieve greater efficiency, agility, and cost savings in their software development and deployment processes. As container technologies continue to evolve, we can expect even more exciting possibilities in virtualization.
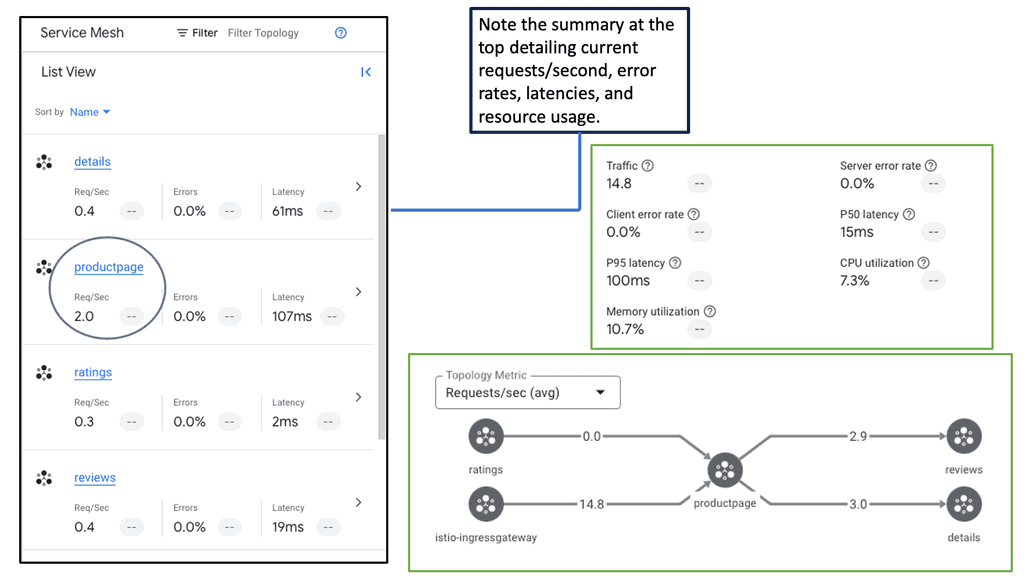
Google Cloud Data Centers

### What is a Cloud Service Mesh?

A cloud service mesh is essentially a network of microservices that manage and optimize communication between application components. It operates behind the scenes, abstracting the complexity of inter-service communication from developers. With a service mesh, you get a unified way to secure, connect, and observe microservices without changing the application code.

### Key Benefits of Using a Cloud Service Mesh

#### Improved Observability

One of the standout features of a service mesh is enhanced observability. By providing detailed insights into traffic flows, latencies, error rates, and more, it allows developers to easily monitor and debug their applications. Tools like Prometheus and Grafana can integrate with service meshes to offer real-time metrics and visualizations.

#### Enhanced Security

Security in a microservices environment can be complex. A cloud service mesh simplifies this by providing built-in security features such as mutual TLS (mTLS) for encrypted service-to-service communication. This ensures that data remains secure and tamper-proof as it travels across the network.

#### Simplified Traffic Management

With a service mesh, traffic management becomes a breeze. Advanced routing capabilities allow for blue-green deployments, canary releases, and circuit breaking, making it easier to roll out new features and updates without downtime. This level of control ensures that applications remain resilient and performant.
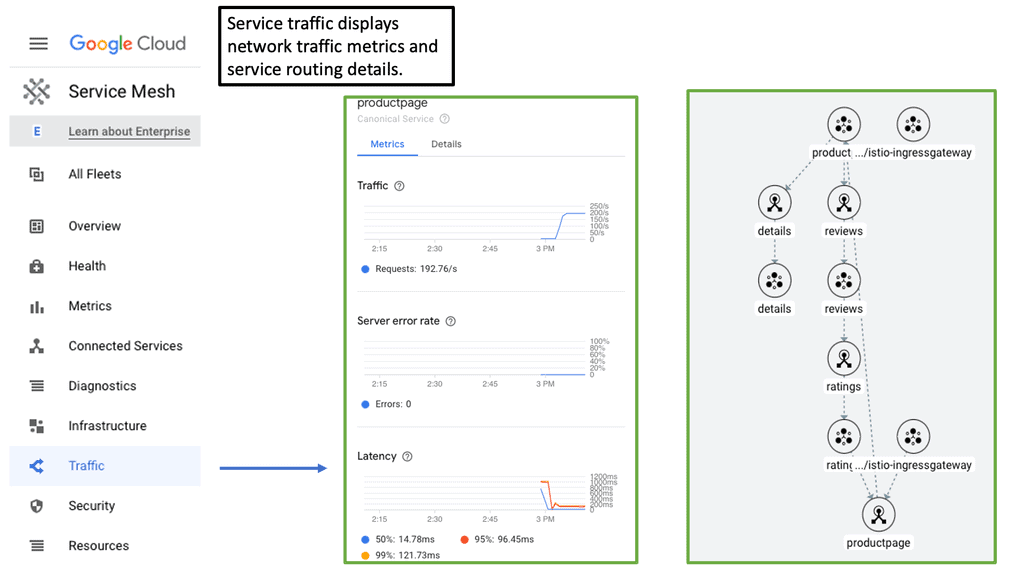
### The Role of Container Networking

Container networking is a critical aspect of cloud-native architectures, and a service mesh enhances it significantly. By decoupling the networking logic from the application code, a service mesh provides a standardized way to manage communication between containers. This not only simplifies the development process but also ensures consistent network behavior across different environments.
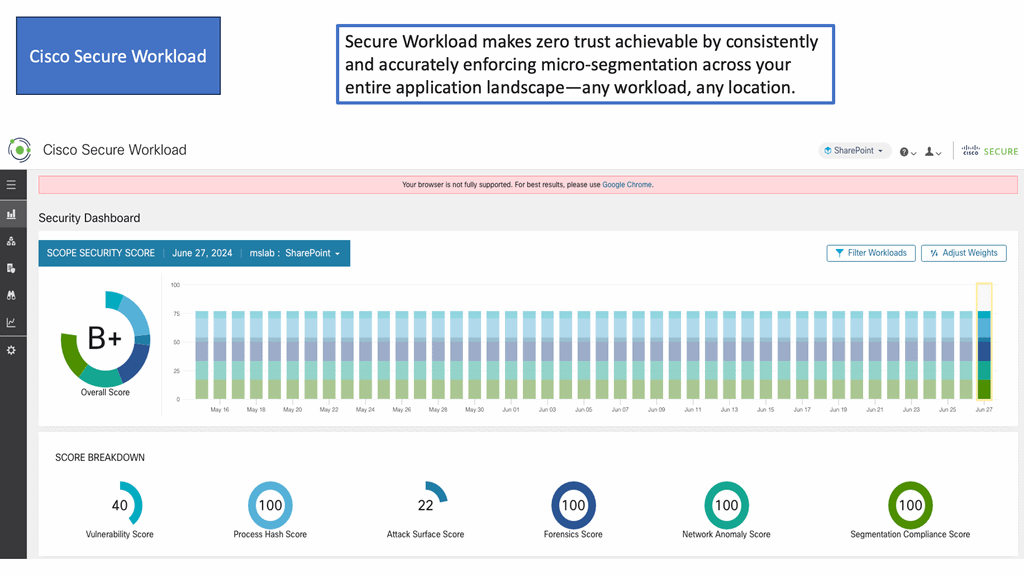
### Popular Cloud Service Mesh Solutions

Several service mesh solutions have emerged as leaders in the industry. Notable mentions include:

– **Istio:** One of the most popular service meshes, Istio offers a robust set of features for traffic management, security, and observability.

– **Linkerd:** Known for its simplicity and performance, Linkerd focuses on providing essential service mesh capabilities with minimal overhead.

– **Consul Connect:** Developed by HashiCorp, Consul Connect integrates seamlessly with other HashiCorp tools, offering a comprehensive solution for service discovery and mesh networking.

Architecture Challenge

Choose the Right Isolation Model

A modern application does not always need every workload to use the same isolation boundary. Read the requirements, choose an architecture, and decide where containers, networking and stronger isolation should be used.

Scenario

Modern Three-Tier Application

A platform team is deploying a public web tier, an internal API and a sensitive database. The platform needs rapid deployment and scaling, private east-west communication and controlled exposure to the Internet.

✓
Fast deployment and scaling Application components should remain lightweight and portable.
✓
Controlled Internet exposure Only the public web tier should have an externally reachable path.
✓
Private east-west traffic API and database communication should stay on private application networks.
✓
Stronger isolation where justified Sensitive workloads may require a stronger boundary than ordinary application containers.
Select an Architecture
Architecture Assessment 0 / 4

Web
→
Controlled Ingress
→
Private API
→
Protected DB
Architecture Decision Console
[ready] Challenge loaded.
[info] Four architecture patterns available.
[hint] Look for the balance between agility, exposure and isolation.
Engineering Insight

The important design question is not simply “containers or VMs?” It is which isolation boundary is appropriate for each workload and how networking controls exposure between application tiers.

Educational architecture challenge. Real production decisions also depend on threat model, runtime security, orchestration, compliance requirements, performance, operational maturity and workload characteristics.