
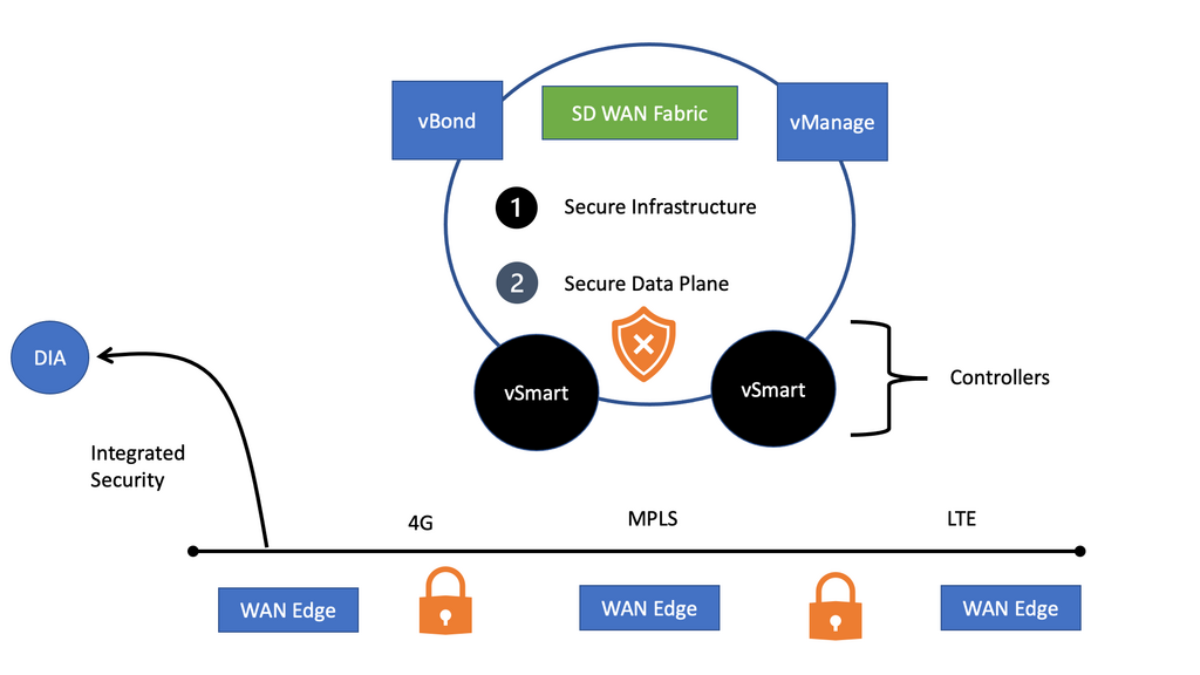
SD-WAN Security: From Secure Connectivity to Adaptive WAN Enforcement
SD-WAN changes the way enterprise networks connect branches, users, cloud services and applications. Instead of relying on a fixed private WAN and a central security perimeter, modern SD-WAN architectures can use multiple transports, encrypted overlays, application-aware routing, distributed Internet access and cloud-delivered security services.
This flexibility changes the security problem. Protecting the WAN is no longer simply about encrypting a tunnel or placing a firewall at the edge. The SD-WAN fabric itself must be secured, devices and controllers must be authenticated, traffic must be segmented, access must be policy-driven and application flows must be inspected according to their identity, destination, risk and security context.
We will examine SD-WAN security as an end-to-end engineering system: protecting the control and management planes, securing the encrypted overlay, applying identity and segmentation policy, inspecting Internet-bound traffic, and using telemetry to detect suspicious behaviour and respond to incidents.
Secure the fabric first, control who and what can communicate, inspect the traffic according to its context, and continuously observe the resulting behaviour.
Navigate the guide from secure fabric architecture through traffic protection, enforcement and continuous response.
SD-WAN Architecture & Secure Fabric
Understand how devices, controllers, management systems and secure overlays form the trusted SD-WAN fabric.
Explore Section → 02Encryption, Segmentation & Secure Traffic
Follow traffic through encrypted overlays, segmentation boundaries and application-aware forwarding decisions.
Explore Section → 03DIA & Integrated Security Enforcement
Examine local Internet breakout, firewalling, DNS, web security, IPS and cloud-delivered enforcement.
Explore Section → 04Visibility, Threat Detection & Response
Connect telemetry, security evidence, anomaly detection, investigation and adaptive response.
Explore Section →SD-WAN Architecture & Secure Fabric
SD-WAN Architecture & the Secure Fabric
Before securing application traffic, the SD-WAN fabric itself must be trusted. This section examines the control plane, management plane, data plane, device identity, encrypted overlays, segmentation and the mechanisms that allow distributed WAN components to participate securely in the fabric.
SD-WAN changes the WAN from a collection of relatively static connections into a software-controlled connectivity fabric. Multiple transports can be combined, application traffic can be steered according to policy and performance, and network behaviour can be coordinated from central management systems. That flexibility creates a different security problem: the organisation must secure not only the traffic crossing the WAN, but also the components that create, control and operate the fabric.
A secure SD-WAN therefore begins with the architecture itself. Before considering firewalls, DNS security or Internet inspection, the organisation must establish whether a device is trusted, whether its control-plane relationships are legitimate, whether management access is protected, and whether the resulting overlay can be relied upon to carry authorised traffic.
Secure the fabric before securing the flow. If an unauthorised device, compromised controller or poorly protected management interface can influence the fabric, downstream security controls may be operating on an untrusted foundation.
Why SD-WAN Changes the Security Model
Traditional WAN security often centred on fixed sites, known circuits, perimeter firewalls and relatively predictable traffic paths. SD-WAN introduces more variables. A branch may have broadband, MPLS, 5G or other transports. The preferred path for an application can change according to latency, loss, jitter, policy or availability. Internet traffic may break out locally rather than returning to a central data centre. Security functions may be integrated into the WAN edge, delivered from the cloud, or distributed across both.
The result is that security can no longer be treated as a single appliance positioned at the edge of the network. Security must be considered across the management plane, control plane and data plane, with clear trust relationships between them.
Management Plane
Controls administration, configuration, policy, software lifecycle, identity, RBAC and operational access to the SD-WAN environment.
Control Plane
Establishes the relationships and routing/policy information that allow SD-WAN devices to understand the overlay and make forwarding decisions.
Data Plane
Carries production traffic across the WAN using secure tunnels, segmentation and forwarding policies established by the control architecture.
These planes are related but should not be treated as interchangeable. A secure data-plane tunnel does not compensate for weak administrator authentication. Strong controller authentication does not automatically protect application traffic. Likewise, an encrypted overlay does not prevent a compromised endpoint from generating malicious traffic.
The SD-WAN Secure Fabric
At the architectural level, an SD-WAN fabric consists of WAN edges, management systems, control-plane components and the underlying transport networks that connect them. The exact architecture varies by platform, but the security objectives remain broadly consistent.
A new WAN edge should not simply become a trusted member of the fabric because it can reach a controller. The platform should establish device identity, validate the device's credentials or certificates, apply an onboarding policy and create only the control-plane relationships that the design permits.
This is particularly important in distributed environments. Branches may be deployed remotely, equipment may be replaced without an engineer physically visiting the site, and multiple transport networks may be available. Automated provisioning improves operational efficiency, but it also makes secure identity and onboarding fundamental architectural requirements.
Device Identity and Secure Onboarding
Device identity is one of the first security boundaries in an SD-WAN deployment. The organisation needs a reliable mechanism for determining whether a device is an approved WAN edge and whether it is permitted to establish relationships with the management and control infrastructure.
Certificate-based identity is commonly used in modern SD-WAN implementations, although the exact mechanism varies by vendor and deployment model. The important engineering principle is that identity should be cryptographically bound to the device and validated before it becomes a trusted participant in the fabric.
Secure onboarding should therefore address device registration, credential or certificate validation, authorised inventory, configuration assignment and lifecycle management. Decommissioned or compromised devices must also be capable of being removed from the trust model.
Control-Plane Protection
The control plane determines how the SD-WAN fabric understands reachability, policy and available paths. Compromise of this layer could therefore have consequences beyond a single device. An attacker capable of manipulating control information may influence where traffic is sent or which routes are considered available.
Control-plane protection should include authenticated relationships between participating components, protected management interfaces, appropriate cryptographic mechanisms and strict control over which devices are allowed to participate.
Operational monitoring is also important. A sudden change in controller relationships, unexpected peer formation or repeated authentication failures may indicate an attempt to interfere with the fabric rather than simply a normal routing event.
Management-Plane Security
The management plane deserves particular attention because it can provide centralised access to configuration and policy. A compromised management account may be more dangerous than the compromise of an individual branch device because the attacker could potentially change policy across many locations.
Management security should therefore include strong administrator authentication, multi-factor authentication where supported, role-based access control, protected management interfaces, logging and controlled administrative workflows. Privileged access should follow least-privilege principles rather than giving every operator unrestricted control of the entire fabric.
Encrypted Overlay Connectivity
Once the participating devices and control relationships are trusted, the next requirement is protecting the data plane. SD-WAN commonly creates logical overlay connectivity across one or more underlying transports. The transport itself may be private, public or a combination of both.
Encryption protects data while it is travelling between participating endpoints. IPsec is widely used for secure WAN tunnels, but the precise tunnel and control mechanisms depend on the SD-WAN implementation. The architectural principle is more important than assuming every platform operates identically: traffic crossing an untrusted or shared transport should receive appropriate cryptographic protection.
Encryption, however, should not be confused with complete traffic security. Encrypted traffic can still originate from a compromised endpoint, violate a segmentation policy or contain malicious activity. Encryption protects the confidentiality and integrity of the transport; it does not establish that the application or user generating the traffic is trustworthy.
Encryption protects the path. Policy protects the communication. A secure tunnel can carry traffic safely across the transport network while still carrying traffic that should have been blocked, restricted or inspected.
Transport Independence and Security
One of the strengths of SD-WAN is the ability to abstract the underlying WAN transports. An organisation may use MPLS, broadband, fibre, LTE, 5G or other connectivity options according to location and business requirements.
This should not be interpreted as “SD-WAN replaces MPLS with the Internet.” SD-WAN is better understood as a software-controlled architecture that can use multiple transports and make policy-driven decisions about how traffic uses them.
Security must therefore remain independent of the assumption that a particular transport is inherently trusted. A private circuit may reduce exposure to some threats, while a public Internet connection introduces a different risk profile, but neither transport should automatically be treated as a substitute for end-to-end security controls.
Application-Aware Connectivity
SD-WAN can evaluate application and path characteristics when determining how traffic should be forwarded. For example, an organisation may prefer a low-loss path for voice, select a high-bandwidth path for business applications, or move traffic away from a degraded transport.
Security policy can interact with these decisions. A sensitive application may require a particular segmentation boundary, a trusted path, inspection or additional controls. A guest application may be permitted to use direct Internet access while remaining isolated from corporate resources.
The important distinction is that path selection and security policy are related but not identical. Path selection answers where traffic should travel. Security policy answers whether the traffic is permitted and what controls should apply to it.
Segmentation as a Security Boundary
Segmentation provides another foundational security mechanism. SD-WAN platforms commonly support logical separation of traffic using constructs such as VPNs, VRFs or vendor-specific segmentation mechanisms.
The objective is not simply to create multiple routing tables. Segmentation should establish meaningful security boundaries between traffic classes that have different trust requirements.
Examples might include corporate users, guest devices, operational technology, payment systems, voice, management traffic and Internet-only services. Each segment can then have its own routing, security and access policy.
Effective segmentation also requires careful consideration of the points where traffic is allowed to cross between segments. If every segment can freely communicate through a central firewall or shared service, the segmentation boundary may provide less security value than expected.
Cisco SD-WAN provides examples of vendor-specific constructs such as OMP and TLOCs. These terms should not be treated as generic SD-WAN terminology. OMP is Cisco's overlay control/routing protocol, while TLOCs represent Cisco-specific transport-location constructs used in its SD-WAN architecture. Other platforms use different architectures and terminology.
The Role of Zero Trust
SD-WAN can support Zero Trust architectures, but SD-WAN itself should not automatically be described as Zero Trust. Zero Trust is a broader security approach based on continuously evaluating identity, device context, resource access and policy rather than assuming that network location creates trust.
An SD-WAN environment can contribute to this model by providing segmentation, identity-aware policy integration, application visibility and controlled connectivity. Additional identity, endpoint, security and policy systems may then provide the context required to make more granular access decisions.
This distinction is important because a trusted branch device should not automatically imply that every user, application or destination behind that device is trusted.
Secure Fabric Engineering Checklist
Before moving into detailed traffic-security controls, a secure SD-WAN design should be able to answer several fundamental questions.
- How is each SD-WAN edge uniquely identified?
- How is a new device authenticated before joining the fabric?
- How are control-plane relationships authenticated and protected?
- How are administrator identities protected?
- Which roles can modify global policy?
- How are management interfaces isolated and monitored?
- How is traffic protected across shared or untrusted transports?
- Which traffic classes require separate segmentation?
- How are compromised or decommissioned devices removed from the trust model?
- How are configuration and policy changes logged and investigated?
A secure SD-WAN starts with a trusted fabric. Device identity, management security, control-plane protection, encrypted connectivity and meaningful segmentation establish the foundation on which traffic-security policy can operate. Once that foundation exists, the next engineering question is no longer simply “Can these sites connect?” but “Which traffic is allowed to move between them, through which security boundaries, and under what conditions?”
SD-WAN Secure Fabric Explorer
Test the trust chain that allows an SD-WAN device to join the fabric, establish control-plane connectivity and participate in an encrypted overlay.
SD-WAN Architecture & Secure Fabric
Identity, Segmentation & Security Policy
Connectivity does not automatically mean permission. Modern SD-WAN security can use identity, device posture, application classification, segmentation and risk context to determine which flows should be permitted, inspected, restricted or blocked.
Once the SD-WAN fabric itself is trusted, the next security challenge is controlling what moves through it. Modern WAN traffic is no longer defined simply by source site and destination site. Applications, users, devices, segments, performance conditions and security policy can all influence how a flow should be handled.
This makes traffic security a combination of encryption, segmentation, policy enforcement and intelligent path selection. The objective is not merely to create a secure tunnel between two locations. It is to ensure that each flow travels through an authorised security boundary, uses an appropriate path and remains isolated from traffic that should never have access to it.
A secure SD-WAN flow is more than an encrypted packet. The design must establish who or what generated the traffic, which segment it belongs to, what policy applies, which path is appropriate and whether additional inspection is required.
From Connectivity to Secure Flow Control
In a traditional WAN, forwarding decisions may have been dominated by routing metrics and fixed topology. SD-WAN introduces an additional policy layer in which application and transport information can influence the forwarding decision.
For example, a voice application may require a low-latency path, a business-critical application may require predictable loss characteristics, and general Internet traffic may be permitted to use local broadband breakout. These decisions become security-relevant when different applications have different trust requirements.
This does not mean that every SD-WAN platform directly evaluates every one of these signals. Implementations differ. The engineering model is to understand that connectivity, security and context can increasingly be combined into a single policy decision.
Encryption Protects the Data Plane
Encryption is a fundamental component of SD-WAN security because traffic may cross shared or untrusted transport networks. A branch may use broadband or mobile connectivity to reach another branch, a data centre or a cloud service. The organisation cannot assume that the underlying transport provides the confidentiality or integrity required by the application.
Secure tunnels therefore provide a protected logical path across the physical transport. IPsec is widely used for this purpose, although the precise implementation, tunnel establishment process and control-plane mechanisms vary between SD-WAN platforms.
A useful architectural distinction is between the underlay and the overlay. The underlay consists of the physical or IP connectivity supplied by the transport networks. The overlay provides the logical SD-WAN connectivity and security relationships built across those transports.
Underlay
MPLS, broadband, fibre, LTE, 5G and other transport services that provide basic reachability between locations.
Overlay
Logical connectivity between SD-WAN endpoints, including secure tunnels, routing relationships and policy-controlled forwarding.
Encryption
Protects data in transit across transports that should not be treated as trusted application paths.
Policy
Determines which communications are allowed, restricted, inspected or isolated within the overlay.
The security value of encryption depends on correct key management, endpoint identity, tunnel configuration and lifecycle management. A tunnel that is technically encrypted but established with the wrong endpoint or inappropriate policy is not necessarily a secure communication channel.
Segmentation Creates Security Boundaries
Encryption protects traffic while it travels across a transport, but it does not determine which applications should be allowed to communicate. That responsibility belongs to policy and segmentation.
SD-WAN segmentation can be implemented using technologies such as VRFs, VPNs or platform-specific logical network constructs. These mechanisms allow different classes of traffic to maintain separate forwarding and policy contexts.
The security objective is to prevent unrelated trust domains from being treated as one large network.
| Traffic Domain | Typical Requirement | Security Objective |
|---|---|---|
| Corporate | Access to internal applications and services | Controlled access to trusted enterprise resources |
| Guest | Internet access only | Prevent access to corporate and management networks |
| IoT / OT | Restricted application communication | Reduce unnecessary lateral movement |
| Management | Administrative access | Strong isolation and privileged access control |
Segmentation should therefore be designed around business and security requirements rather than simply creating additional logical networks. Each segment should have an explicit definition of what it can reach, what can reach it and where controlled communication between segments is permitted.
Segmentation Is Not the Same as Microsegmentation
The terms segmentation and microsegmentation are sometimes used interchangeably, but they represent different levels of policy granularity. Traditional segmentation may separate broad traffic domains such as corporate, guest and management networks. Microsegmentation aims for much more granular control, potentially considering individual workloads, identities, applications or security groups.
An SD-WAN platform can contribute to segmentation, but the exact level of granularity depends on the platform and its integration with identity, endpoint and security systems. It is therefore better to describe SD-WAN as an enforcement point within a broader segmentation architecture rather than assuming that every SD-WAN deployment automatically provides full microsegmentation.
Application-Aware Path Selection
One of SD-WAN's defining capabilities is the ability to select paths according to application requirements and current network conditions. Instead of relying only on a static route, the system can consider metrics such as latency, packet loss, jitter, bandwidth availability and policy.
This creates a security opportunity. Different application classes can be assigned different forwarding policies, security requirements and acceptable paths.
For example, a real-time voice application may require a stable low-latency path, while a less sensitive backup workload may tolerate a higher-latency transport. A sensitive application might additionally require a particular security service or segmentation boundary before the flow is allowed to proceed.
Do not confuse “best path” with “permitted path.” A transport can be technically optimal from a performance perspective while still being unsuitable because of security policy, segmentation or inspection requirements.
Policy-Based Forwarding
Policy-based forwarding allows an organisation to define how selected traffic should be handled rather than allowing the routing table alone to determine the outcome.
A policy may identify traffic using application characteristics, source or destination networks, ports, users, segments or other available attributes. It can then determine whether the flow is allowed, which path should be preferred, whether it should be inspected, or whether it should be blocked.
The exact capabilities vary considerably between platforms, so the engineering design should start with the required security outcome rather than assuming a particular vendor feature exists everywhere.
A Useful Policy Model
A practical way to reason about secure SD-WAN forwarding is to separate the decision into stages:
- Identify the flow: determine source, destination, application and available context.
- Determine the segment: establish which security domain the traffic belongs to.
- Evaluate policy: determine whether the communication is permitted.
- Select the path: choose an appropriate transport or overlay path.
- Apply security controls: send the flow through required inspection or enforcement points.
- Monitor the result: record the decision and resulting traffic behaviour.
This model makes an important point: routing is only one part of the security decision.
Branch-to-Branch and Branch-to-Cloud Security
SD-WAN commonly connects branches not only to data centres but also to cloud services and other distributed resources. This changes the traditional assumption that all application traffic should first return to a central security perimeter.
A branch may need direct access to a SaaS platform, a cloud workload or another branch. Forcing every flow through a central data centre can introduce unnecessary latency and consume expensive transport capacity. SD-WAN allows more distributed forwarding models, but the security architecture must move with the traffic.
For branch-to-branch communication, this means defining which segments can communicate and whether the traffic should use direct encrypted connectivity or a controlled hub/service path. For branch-to-cloud traffic, it means deciding whether security inspection occurs locally, through a cloud security service or through another central enforcement point.
Containing Lateral Movement
One of the strongest reasons to combine SD-WAN with segmentation is to limit lateral movement after a device or workload has been compromised.
Consider a branch endpoint that becomes infected with malware. Encryption may keep its traffic protected in transit, but encryption does nothing to prevent the compromised endpoint from attempting to reach other internal systems.
Segmentation and least-privilege policy can reduce that risk by limiting the destinations available to the compromised system. Security controls can then identify suspicious traffic and apply additional restrictions.
The goal is not to guarantee that compromise never occurs. The goal is to make the compromised environment smaller, more observable and easier to contain.
Security Context and Identity
Network location alone is becoming a weaker indicator of trust. A device connected to a corporate branch may be managed and compliant, or it may be compromised. A user working from a branch may require access to one application but not another.
SD-WAN can participate in a broader identity-aware architecture by consuming or integrating with identity, endpoint and security context. This can allow policy decisions to become more granular than source IP address alone.
However, the architecture should remain explicit about where each decision is made. Identity systems determine identity and authentication context. Endpoint systems can provide device posture. SD-WAN can provide connectivity and policy enforcement. Security platforms can provide threat intelligence and inspection. Combining these signals can produce stronger decisions than relying on any single system.
Identity-aware SD-WAN does not mean that every SD-WAN router independently understands every user identity. In many designs, identity and endpoint context is supplied through integrations with other security and access systems. The important engineering question is how that context reaches the enforcement point and how reliably it can be used in policy.
Secure Traffic Engineering
A mature SD-WAN security design therefore treats traffic as a policy-controlled object rather than simply a packet travelling between two IP addresses.
The same branch may contain multiple traffic classes with completely different requirements. Corporate application traffic may require access to internal services. Guest traffic may require Internet-only connectivity. Operational technology may need to communicate with a small set of known systems. Voice may require a predictable low-latency path. Sensitive applications may require additional inspection.
The SD-WAN architecture should make these differences explicit rather than relying on one universal forwarding rule.
Protect
Use appropriate encryption and authenticated overlay connectivity to protect traffic across the underlying transport.
Separate
Use segmentation to prevent unrelated trust domains from communicating without explicit policy.
Decide
Apply policy to determine whether the flow is permitted and what security requirements apply.
Steer
Select an appropriate path according to application requirements, network conditions and security policy.
Vendor Architectures Are Different
The underlying engineering principles are broadly applicable, but SD-WAN products do not implement them identically. Terminology, control-plane architecture, tunnel establishment, segmentation models, application identification and security integrations differ between vendors.
For example, Cisco SD-WAN uses concepts such as OMP and TLOCs, while other SD-WAN platforms use different control and forwarding models. Some platforms integrate extensive security capabilities directly into the WAN edge; others rely more heavily on external security appliances or cloud-delivered services.
This is why a good SD-WAN security design should begin with requirements such as identity, segmentation, encryption, inspection, availability and policy enforcement, and only then map those requirements to vendor-specific features.
Secure Flow Design Checklist
For each important traffic class, the engineering team should be able to answer the following questions:
- Who or what is generating the traffic?
- Which application or service is being accessed?
- Which security segment does the traffic belong to?
- Is the source device trusted and appropriately managed?
- Is the destination authorised for that segment?
- Must the traffic be encrypted across the transport?
- Which transport or overlay path should be preferred?
- Can the path change without violating security policy?
- Does the traffic require firewall, IPS, DNS, URL or other inspection?
- What happens if the device, application or destination becomes risky?
SD-WAN security becomes meaningful when encrypted connectivity is combined with segmentation and policy-controlled forwarding. The objective is not simply to find the fastest route between two endpoints. It is to determine whether the communication is authorised, which security boundaries it must cross, which path is appropriate and whether additional controls must inspect the flow. The next question is what happens when that traffic leaves the private WAN and breaks directly out to the Internet.
SD-WAN Secure Flow Decision Lab
Change identity, application, segment and device context to see how a policy engine determines whether traffic should be allowed, inspected, blocked or isolated — and which secure path it can use.
Encryption, Segmentation & Secure Traffic
Secure DIA & Integrated Security Services
Direct Internet Access changes where enterprise traffic exits the WAN, but it does not remove the need for security inspection. Firewalling, IPS, DNS security, URL filtering, TLS inspection and cloud security services can be applied according to the application, destination and policy requirements of each flow.
The traditional WAN security model often assumed that Internet access would be concentrated behind a small number of central security boundaries. Modern SD-WAN makes local Internet breakout much more practical. A branch can send SaaS, web and cloud traffic directly to the Internet instead of backhauling every session through a central data centre.
This improves application performance and can reduce unnecessary WAN utilisation, but it also changes where security enforcement must occur. When the branch becomes an Internet access point, the security controls that previously protected traffic at a central perimeter must either move closer to the branch, move into the cloud, or be provided through a combination of both.
DIA is not inherently insecure. The security question is whether appropriate policy, inspection and monitoring follow the traffic when Internet access is distributed across many locations.
Why Direct Internet Access Changes Security
Direct Internet Access, commonly abbreviated as DIA, allows branch traffic to exit directly to the Internet rather than travelling through a central hub or data centre first.
This architecture is increasingly useful because many business applications are now delivered from cloud platforms. If a user in a branch is accessing a SaaS service, sending the traffic through a central data centre can create additional latency and consume WAN capacity without providing a security benefit that cannot be delivered elsewhere.
The challenge is that local breakout distributes the security perimeter. Instead of one or two Internet gateways, the organisation may now have dozens or hundreds of Internet exit points.
The engineering objective is therefore to create a distributed security perimeter without creating inconsistent security policy.
The Secure Internet Breakout Model
A secure DIA design typically places one or more enforcement layers between the branch user or device and the external destination. The exact architecture depends on the organisation's risk model, traffic types and available security services.
Some environments may place firewall and security inspection directly on the SD-WAN edge. Others may forward traffic to a regional security appliance or a cloud-delivered security service. Hybrid designs can combine local enforcement with cloud inspection depending on application and risk.
Local Edge Security
Firewall, application control and other security functions operate directly on or beside the SD-WAN edge.
Regional Security
Branch traffic is directed to a regional security enforcement point before reaching the Internet.
Cloud Security
Traffic is sent to cloud-delivered security services for inspection and policy enforcement.
Hybrid Enforcement
Different applications or risk classes can use different combinations of local, regional and cloud controls.
Firewall Enforcement at the WAN Edge
A firewall remains an important control for many SD-WAN deployments. The SD-WAN edge can use application, network, port, segment and other available attributes to determine whether traffic should be permitted.
The firewall policy should not simply reproduce a traditional perimeter rule set at every branch. A distributed environment requires central policy management, consistent object definitions, controlled exceptions and appropriate local enforcement.
The policy should also distinguish between traffic that is allowed to leave the branch and traffic that must never reach the Internet. Management services, internal infrastructure and sensitive systems may require significantly more restrictive rules than general user traffic.
| Traffic Type | Possible Policy | Reason |
|---|---|---|
| Business SaaS | Allow with appropriate inspection | Business requirement with controlled external access |
| General Web | Allow with web/DNS controls | Reduce exposure to malicious destinations |
| Management | Restrict or block direct Internet access | Reduce exposure of privileged infrastructure |
| Unknown / High Risk | Inspect, restrict or block | Prevent uncontrolled exposure to suspicious destinations |
IDS and IPS Protection
Firewall policy answers whether traffic is permitted according to defined rules, but permitted traffic can still contain malicious behaviour. Intrusion Detection and Intrusion Prevention Systems provide another layer of analysis.
An IDS identifies suspicious activity and generates an alert. An IPS can additionally take an enforcement action, depending on the implementation and policy.
These controls can be particularly valuable for Internet breakout because branch traffic is exposed directly to external destinations. They can also provide visibility into attacks that would otherwise appear to be legitimate permitted sessions.
Technologies such as Snort and Suricata are examples of IDS/IPS engines used in different network-security architectures. They should be viewed as examples rather than assuming that every SD-WAN platform uses the same inspection engine.
An alert tells the organisation that suspicious behaviour has been observed. Prevention requires the enforcement point to have the capability and policy authority to interrupt or restrict the traffic.
DNS Security
DNS is another important security enforcement point because many applications begin with a name-resolution request. Malicious infrastructure may use domains associated with phishing, malware delivery, command-and-control or other threats.
DNS security can therefore identify or block known malicious destinations before the connection is established. It can also provide useful telemetry about which devices are attempting to resolve suspicious domains.
However, DNS security should be treated as one layer rather than a complete security solution. Modern applications can use encrypted DNS, hard-coded destinations, content delivery networks and other techniques that make DNS alone insufficient for determining whether a connection is safe.
URL and Web Filtering
Web filtering provides another layer of policy by evaluating requested destinations or web categories. An organisation may allow business services while restricting categories that present unnecessary risk or violate corporate policy.
This becomes especially useful in distributed DIA environments because the policy can be applied consistently regardless of which branch provides the Internet connection.
The engineering challenge is balancing security with usability. Overly broad blocking can interfere with legitimate business activity, while overly permissive policy reduces the value of the control. Categories, reputation, user context and exception management should therefore be considered together.
TLS Inspection
Encryption protects users and applications, but it also reduces the visibility available to traditional security controls. A significant proportion of modern application traffic is encrypted using TLS, meaning that security devices may not be able to inspect the contents of the session without an appropriate inspection mechanism.
TLS inspection can provide deeper visibility by terminating and re-establishing encrypted sessions under controlled conditions. This can allow security systems to inspect otherwise opaque traffic.
However, TLS inspection introduces significant engineering considerations. Certificate deployment, device compatibility, performance, privacy, application breakage and legal or regulatory requirements must all be considered before enabling it broadly.
More inspection is not automatically better security. Inspection should be applied where it provides meaningful risk reduction and where the organisation can operate the associated certificate, privacy, performance and exception-management processes correctly.
Security Service Chaining
Some traffic requires multiple security controls. A high-risk Internet flow might need firewall enforcement, DNS protection, URL filtering, malware analysis and additional inspection before it is allowed to reach its destination.
The traffic path can therefore become a security service chain.
The important design principle is that not every application necessarily needs every security service. Applying the entire inspection chain to every packet can increase latency, consume resources and complicate troubleshooting.
Policy should determine which traffic requires which controls. Business-critical SaaS traffic may require one treatment, sensitive data another, and guest Internet traffic a simpler but still controlled path.
Security Policy Should Follow the Flow
Once Internet breakout is distributed, policy consistency becomes a major operational requirement. A user should not receive significantly different security treatment simply because they happen to be working from another branch.
Centralised policy management can help maintain consistency, but local conditions still matter. Branches may have different bandwidth, different security capabilities, different regulatory requirements or different application dependencies.
A strong design therefore combines central policy intent with controlled local enforcement.
Policy Intent
Define the security outcome centrally: who can access what, under which conditions and with which controls.
Enforcement Point
Determine where the required control should actually inspect or block the traffic.
Path Selection
Select a path that satisfies both application performance and security requirements.
Telemetry
Record enough information to determine whether the policy produced the expected result.
Relationship Between SD-WAN and SASE
SD-WAN and SASE are closely related but should not be treated as synonyms.
SD-WAN primarily provides software-controlled connectivity, transport abstraction, routing, segmentation and application-aware traffic steering. SASE is a broader architectural model that combines networking capabilities with distributed, often cloud-delivered security services.
An SD-WAN edge can therefore be an important networking component within a SASE architecture. Security services such as secure web access, Zero Trust access, cloud firewalling, DNS security and threat inspection may be delivered separately or integrated with the SD-WAN environment.
The important engineering question is not whether an organisation has “SD-WAN or SASE.” It is how connectivity and security services are combined to produce a consistent access and enforcement model.
Cisco provides multiple networking and cloud-security products that can participate in SASE-oriented architectures. Cisco Umbrella is a cloud security service within that broader ecosystem; it should not be described as simply “Cisco's version of SASE.”
Integrated Security at the Branch
Modern SD-WAN platforms increasingly integrate networking and security functions at the edge. This can simplify deployment because a single branch device may provide routing, segmentation, firewalling and application-aware controls.
Integration can also improve visibility because the same system understands the traffic path and security decision. However, consolidation introduces its own risks. A failure or compromise of the integrated edge may affect multiple functions simultaneously, and resource constraints can become important when advanced inspection is enabled.
Architecture should therefore consider capacity, resilience, software lifecycle, high availability and the ability to maintain security controls during transport or device failures.
Distributed Security Requires Distributed Operations
A centralised security architecture allows a small number of enforcement points to be monitored closely. Distributed DIA changes this operational model.
Security teams now need visibility into many Internet exit points, each potentially producing firewall events, DNS activity, web requests, IPS alerts and application telemetry.
This makes centralised logging and security analytics increasingly important. The objective is to make a distributed enforcement architecture appear as one coherent security system to the operations team.
DIA Security Design Checklist
For each branch with direct Internet access, the engineering team should be able to answer:
- Which traffic is allowed to use local Internet breakout?
- Which traffic must remain on the private WAN?
- Where is the firewall enforcement point?
- Where is DNS security applied?
- Is web or URL filtering required?
- Which traffic requires IDS/IPS inspection?
- Where, if anywhere, is TLS inspection performed?
- Which traffic is sent to cloud security services?
- How are exceptions approved and maintained?
- How are security events from all branches collected centrally?
- What happens when a local security service becomes unavailable?
- How does the SD-WAN policy respond when the preferred security path fails?
The Secure DIA Decision
A useful way to evaluate an Internet-bound flow is to stop thinking about DIA as simply “send the packet to the Internet.” Instead, treat the breakout as a security decision.
The SD-WAN edge should determine the traffic class, identify the appropriate security policy, select the required inspection services and then choose an available path that satisfies both performance and security requirements.
A managed corporate device requests a business SaaS application. The flow belongs to the corporate segment, is permitted by policy, passes DNS and web-security controls, uses an approved Internet breakout and is monitored. A guest device requesting an internal application receives a different outcome: the segment policy prevents the connection before it reaches the protected resource.
Direct Internet Access changes where security must be enforced, not whether security is required. A mature SD-WAN design combines local or cloud-based firewalling, DNS and web controls, threat inspection and appropriate encryption or TLS visibility with centralised policy and telemetry. Once security enforcement is distributed across the WAN, the final engineering challenge is operational: how do we know when a trusted device, flow or policy begins behaving suspiciously?
Secure DIA / Internet Breakout Explorer
Explore how Direct Internet Access changes the security path. Select a traffic scenario and determine which security services should inspect the flow before it reaches the Internet or SaaS.
DIA & Integrated Security Enforcement
Visibility, Threat Detection & Response
A secure SD-WAN must also be observable. Application flows, identity activity, device behaviour, DNS events, security alerts and path changes provide the telemetry required to detect abnormal behaviour, investigate incidents and respond before a local compromise becomes a wider WAN security problem.
A secure SD-WAN cannot be judged only by whether its tunnels are encrypted or whether its firewall rules appear correct. Modern WAN environments are dynamic: paths change, applications move to the cloud, devices change state, Internet breakout is distributed and policy is continually updated. Security therefore depends on being able to observe what the fabric is doing and recognise when normal behaviour becomes suspicious.
Visibility turns SD-WAN from a connectivity platform into an operational security system. Telemetry from the WAN edge, applications, users, security controls, DNS services and cloud platforms can be combined to establish what happened, where it happened and what response is appropriate.
You cannot reliably secure what you cannot observe. Security telemetry should connect the original policy decision to the resulting traffic behaviour so that engineers can investigate both successful and suspicious flows.
From Visibility to Security Evidence
SD-WAN generates a significant amount of operational information. Tunnel status, path quality, application performance, routing changes and device health are all useful, but security teams need more than raw counters.
Useful security telemetry should help answer questions such as:
- Which device generated the traffic?
- Which user or application was involved?
- Which segment carried the flow?
- Which path did the traffic use?
- Which security policy was applied?
- Was the traffic inspected or bypassed?
- What destination did the device contact?
- Did the device subsequently exhibit other suspicious behaviour?
The goal is to create an evidence chain rather than a collection of disconnected alerts.
WAN Telemetry and Application Visibility
The first layer of operational visibility comes from the WAN itself. SD-WAN platforms can typically expose information about transport health, tunnel state, packet loss, latency, jitter, bandwidth utilisation and application performance.
This information is valuable for both network operations and security investigation. A sudden change in traffic behaviour can be an operational problem, a security event or both.
For example, a branch may suddenly send substantially more traffic than normal to an unfamiliar destination. The initial symptom could appear as a bandwidth anomaly, but when correlated with DNS activity and endpoint telemetry it may become evidence of data exfiltration or malware activity.
Path Telemetry
Latency, loss, jitter, tunnel state and transport availability provide context for how traffic is moving through the WAN.
Application Telemetry
Application classification and traffic patterns help determine what services are actually using the network.
Security Telemetry
Firewall, DNS, web, IPS and other controls provide evidence about suspicious or prohibited behaviour.
Identity & Device Context
User and endpoint information can add the context required to distinguish normal business activity from risky behaviour.
Security Events Need Correlation
A single alert is rarely enough to determine what is happening. Security investigation becomes more effective when multiple events are correlated across time.
Consider a branch endpoint that has been operating normally. It suddenly begins resolving a newly observed domain, establishes an unusual outbound session and then generates an IPS alert. Shortly afterwards, it attempts to connect to systems in another internal segment.
Each event provides only part of the story. Together they create a much stronger indication that the endpoint may have been compromised.
This type of correlated timeline is much more useful to an engineer than five independent alerts arriving from five different systems.
Threat Detection in the SD-WAN Environment
Threat detection can operate at several layers. Signature-based IDS/IPS controls can identify known attack patterns. DNS and web-security services can identify malicious destinations. Behavioural analytics can identify unusual traffic patterns. Endpoint systems can provide evidence about process or device compromise.
No single mechanism should be expected to identify every threat. Modern attacks can change infrastructure, encrypt payloads, use legitimate cloud services and deliberately avoid obvious signatures.
The SD-WAN environment therefore benefits from combining network and security telemetry rather than treating the WAN as a separate operational silo.
Detecting Behavioural Anomalies
Behavioural analysis looks beyond individual signatures and asks whether activity is unusual for a device, application, user or location.
Examples include:
- A branch suddenly generating much more outbound traffic than normal.
- A device contacting destinations it has never previously accessed.
- A workstation communicating with a server segment that its policy normally prevents.
- An application suddenly using a different transport or destination profile.
- A privileged device attempting unusual Internet access.
- A large increase in DNS requests from a single endpoint.
An anomaly is not automatically an attack. A software update, business event or network migration can produce unusual behaviour. The value of behavioural analytics is therefore to provide investigative signals that can be combined with other evidence.
Anomaly detection should trigger investigation, not automatically become proof of compromise. Context and correlation determine whether unusual behaviour represents legitimate change, misconfiguration or an active security incident.
Threat Hunting Across the Fabric
Once telemetry is centralised, security teams can actively search for patterns rather than waiting for an alert.
Threat hunting might begin with a known malicious destination, an unusual DNS pattern, a suspicious application or an unexpected connection between two segments. Engineers can then work backwards and forwards through the available telemetry to identify affected devices and related activity.
The distributed nature of SD-WAN makes this especially valuable. A threat that appears at one branch may have related activity at another location, particularly when the same identity, application, policy or device type exists across the organisation.
SIEM and Centralised Security Analytics
A Security Information and Event Management platform can provide a central location for collecting and correlating events from SD-WAN infrastructure and associated security systems.
The SD-WAN platform may contribute tunnel events, application telemetry, configuration changes and policy decisions. Firewalls can contribute session and enforcement data. DNS systems can provide domain-resolution events. Endpoint platforms can provide device-level evidence. Identity systems can provide authentication and access information.
When these signals are combined, the security team can investigate an incident across the complete path rather than analysing each technology independently.
The SD-WAN platform does not need to become the organisation's entire security analytics platform. Its role is to expose useful telemetry and policy evidence that can be consumed by the wider security operations architecture.
Investigating a Compromised Endpoint
One of the most useful operational scenarios is investigating a device that was previously trusted but has begun behaving abnormally.
The investigation should not immediately focus on blocking a single destination. Instead, engineers should establish the sequence of events.
1. Establish Identity
Determine which device, user, segment and branch are involved and whether the device is normally trusted.
2. Reconstruct the Flow
Identify destinations, applications, paths and security decisions associated with the suspicious activity.
3. Correlate Evidence
Compare DNS, web, firewall, IPS, endpoint and identity events to determine whether the activity is connected.
4. Contain
Restrict access, isolate the device or revoke trust while preserving enough telemetry to continue the investigation.
Response Should Be Proportional to Risk
Not every suspicious event requires the same response. A mature architecture provides several levels of enforcement so that the security team can respond proportionally.
| Response | Use Case | Effect |
|---|---|---|
| Monitor | Low-confidence anomaly | Continue observation and collect evidence |
| Restrict | Elevated risk | Reduce available destinations or applications |
| Revoke | Loss of trust | Remove access previously granted to the device or identity |
| Isolate | Likely compromise | Contain the endpoint or segment to prevent further movement |
This approach is particularly useful when SD-WAN policy is integrated with identity and endpoint security. A device can move from a normal state to a restricted state without requiring the network team to redesign the entire topology.
Policy Changes Are Security Events Too
Security teams often focus on traffic alerts while overlooking configuration changes. In a software-defined WAN, however, policy changes can have a significant impact on the entire environment.
An unexpected firewall rule, segmentation change, routing policy modification or administrator login may explain why traffic behaviour changed. Configuration history should therefore be treated as part of the security evidence.
A useful investigation asks not only “What traffic occurred?” but also “What changed immediately before the traffic occurred?”
Operational Resilience and Security
Security controls themselves can fail. A firewall service may become unavailable, a cloud security path may be unreachable, a tunnel may fail or a branch device may lose connectivity to its controller.
The SD-WAN policy should define what happens in these conditions.
Some applications may tolerate a temporary loss of a security service and fail closed. Others may require an alternative inspection path. Certain non-sensitive traffic may continue through another controlled route.
The correct behaviour depends on the application's risk and availability requirements. The important point is that security failure behaviour should be designed rather than left to chance.
Continuous Security Improvement
SD-WAN security is not a configuration that is completed once and then left unchanged. New applications appear, users change behaviour, branches are added, transports evolve and threats change.
Telemetry should therefore feed back into policy design. Security teams can use observed traffic to identify unnecessary access, missing segmentation, ineffective inspection rules and new application requirements.
This creates a continuous engineering cycle:
The Complete SD-WAN Security Model
The four engineering stages in this guide are deliberately connected.
First, secure the fabric. Devices, management systems and control-plane relationships must be trusted before the network can be relied upon.
Second, protect the flow. Encryption, segmentation and policy-controlled forwarding determine how authorised traffic can move through the WAN.
Third, enforce security at the right point. DIA, firewalling, DNS security, web filtering, IPS and cloud security services provide inspection and enforcement where the traffic actually travels.
Finally, observe and respond. Telemetry connects the original decision to the resulting behaviour and allows the security team to identify anomalies, investigate incidents and change policy when risk changes.
SECURE FABRIC → PROTECT FLOW → ENFORCE POLICY → OBSERVE & RESPOND
Security becomes part of the WAN's operating model rather than a separate appliance positioned around the edge of it.
SD-WAN Security Operations Checklist
A mature SD-WAN security architecture should be able to answer the following questions continuously:
- Are all participating devices still trusted?
- Are management and control-plane relationships healthy and authorised?
- Are encrypted overlays operating as expected?
- Are segmentation boundaries preventing unintended communication?
- Are application flows using appropriate paths?
- Are Internet-bound flows receiving the required security controls?
- Are DNS, web, firewall and IPS events being collected?
- Can suspicious behaviour be correlated across branches?
- Can security teams reconstruct the sequence of an incident?
- Can a compromised device be restricted or isolated quickly?
- Are policy and configuration changes auditable?
- Does the architecture have defined behaviour when a security service fails?
A secure SD-WAN should not simply tell you that a connection exists. It should provide enough evidence to explain who or what communicated, where the traffic travelled, which policy allowed or denied it, what security controls inspected it, and what changed when the risk level changed.
Visibility completes the SD-WAN security model. Secure connectivity and enforcement establish the controls, but telemetry determines whether those controls are actually producing the intended outcome. By correlating identity, device state, application flows, DNS activity, security alerts, configuration changes and policy decisions, engineers can move from reactive troubleshooting to structured investigation and response. The result is a WAN that can not only connect and protect, but also explain, detect and adapt.
SD-WAN Security Incident Investigation
Investigate a previously trusted SD-WAN endpoint as its behaviour changes. Correlate identity, device, flow, DNS, web and IPS evidence before choosing the least disruptive response that contains the risk.
- BGP Solutions and Insights - October 8, 2026
- DMVPN - May 20, 2023
- Computer Networking: Building a Strong Foundation for Success - April 7, 2023