
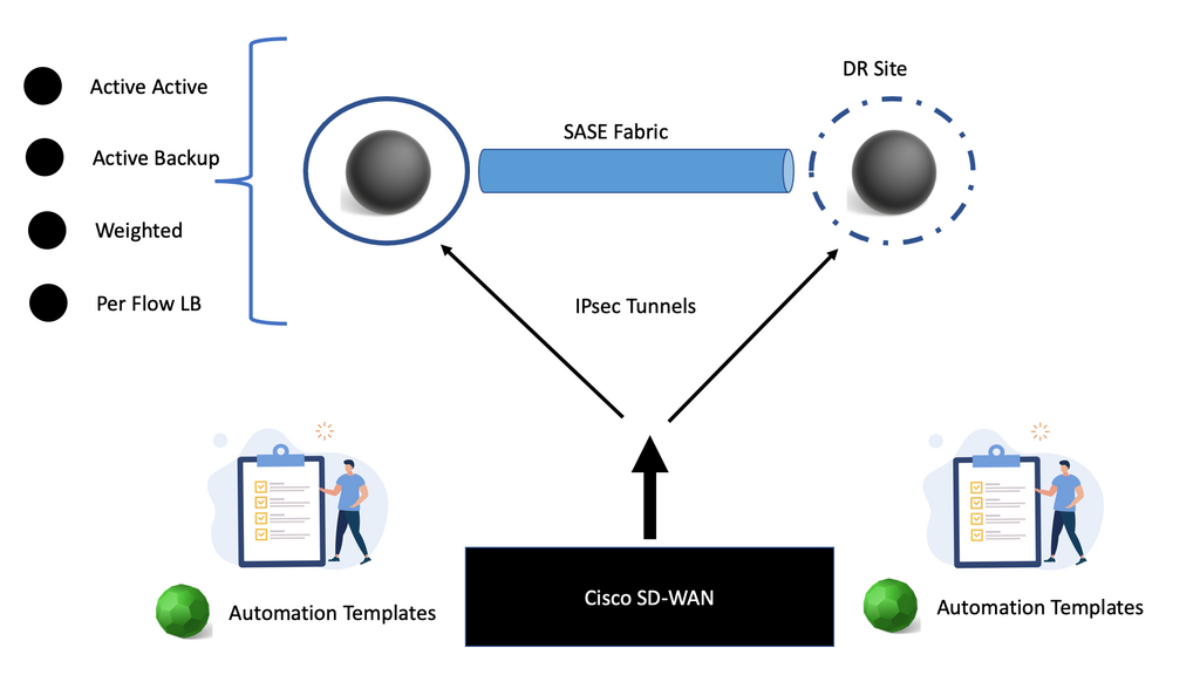
SD-WAN & SASE: From Intelligent Connectivity to Secure Access
SD-WAN and SASE address different parts of the modern connectivity problem. SD-WAN provides the software-controlled networking fabric that determines how traffic moves across available transports, while SASE extends security and access enforcement closer to users, devices, applications and Internet destinations.
What This Guide Examines
The relationship between SD-WAN and SASE is often reduced to a product comparison. The engineering problem is broader: traffic may originate from a branch, remote user, cloud workload or SaaS application, traverse multiple transports, and encounter security controls distributed across different enforcement points.
This guide follows that traffic and examines how connectivity, identity, application context, path quality, security policy and behavioural signals combine to determine what should happen to each flow.
The objective is not to treat SD-WAN and SASE as interchangeable technologies, but to understand where their responsibilities meet and how they can form a coherent architecture.
SASE provides a distributed security and access architecture that evaluates context and applies security controls closer to users and applications.
Together they enable a more dynamic model of connectivity + policy + security + continuous adaptation.
SD-WAN & SASE Architecture
SD-WAN & SASE
Follow the architecture from connectivity through policy decision, security enforcement and adaptive response.
Underlay and overlay, SD-WAN edge functions, application-aware routing, distributed SASE enforcement and the boundary between connectivity and security.
Section 01 — SD-WAN & SASE Architecture
The first step in understanding SD-WAN and SASE is to separate their responsibilities. They are complementary architectural capabilities, not two names for the same technology. SD-WAN focuses primarily on connectivity, routing, path selection and traffic steering, while SASE brings security and access controls closer to users, devices, applications and Internet destinations.
The SD-WAN Connectivity Fabric
SD-WAN creates a software-controlled abstraction over the available WAN transports. A branch may have broadband, private connectivity, 5G, LTE or other transport options, and the SD-WAN edge can use policy and real-time path information to determine how application traffic should be carried.
The important distinction is between the underlay and the overlay. The underlay provides the physical or provider connectivity. The overlay provides the logical networking relationships, routing information, tunnels and policy-controlled paths that operate across those transports.
This separation allows the network to make decisions based on application requirements rather than treating every available link as equivalent. A latency-sensitive application may require a different path from bulk data transfer, while a critical business service may be given a higher-quality path when conditions change.
Where SASE Enters the Architecture
SASE extends this model beyond connectivity. Instead of assuming that security enforcement must occur at a central enterprise data centre, security capabilities can be delivered through distributed cloud-based enforcement points, commonly referred to as SASE Points of Presence or security service edges.
Depending on the architecture and provider, these enforcement capabilities may include secure web access, firewall services, DNS security, intrusion prevention, URL filtering, cloud access controls, data protection and other security functions.
The architectural objective is to place security enforcement in a location that is appropriate for the traffic rather than automatically backhauling every Internet or SaaS request through a traditional central security stack.
SD-WAN and SASE Are Not the Same Decision
A useful engineering model is to treat connectivity and security as related but distinct decisions.
In practice these decisions interact. Application identity, user identity, device posture, path quality and security policy can all influence the resulting treatment of a flow. However, combining the technologies does not mean that routing and security become a single function.
From Branch Connectivity to Application Access
Consider a user at a branch accessing a cloud application. The request may begin at a local endpoint, cross the branch LAN, reach the SD-WAN edge and then use an available WAN transport. Rather than automatically sending the request through a central data centre, the architecture may steer it toward an appropriate cloud or SASE enforcement point.
At the security edge, the request can be evaluated using identity, device context, application classification, destination, policy and risk signals. The resulting decision may permit the request, require additional verification, restrict access or block the flow.
This creates a much more distributed architecture than the traditional model of branch → WAN → central data centre → Internet. The important change is not simply that security has moved into the cloud. It is that connectivity and security can now be coordinated around the location of the user, application and enforcement point.
The Architecture in Four Layers
Why the Architecture Matters
The value of combining SD-WAN and SASE is therefore not simply operational convenience. It is the ability to create a consistent policy model across increasingly distributed environments where users, applications and workloads are no longer concentrated inside one enterprise perimeter.
SD-WAN provides the connectivity intelligence required to move traffic efficiently across the available network. SASE provides security and access enforcement that can follow the traffic toward the user, application or destination.
The result is an architecture in which connectivity is dynamic, security is distributed, and access decisions can continuously adapt to context.
Modern Secure Connectivity Architecture
User / Branch
Traffic originates from a branch, remote user, device or workload. The request carries identity, application and device context that can influence the security decision.
SD-WAN Responsibilities
Connect: build the WAN fabric.
Measure: latency, loss and jitter.
Classify: identify applications.
Steer: select an appropriate path.
SASE Responsibilities
Evaluate: identity and context.
Inspect: apply security services.
Enforce: allow, restrict or block.
Protect: maintain policy at the cloud edge.
Identity, Context & Traffic Decision
Identity, device posture, application classification, link quality, risk signals and the difference between routing decisions and security decisions.
Section 02 — Identity, Context & Traffic Decision
Once SD-WAN provides a programmable connectivity fabric, the next engineering problem is deciding how an individual flow should be treated. Modern access decisions cannot rely only on an IP address or the network from which a request originated. User identity, device posture, application identity, destination, path conditions and security policy can all contribute to the final decision.
From Network Location to Context
Traditional network security often associated trust with location. A request arriving from an internal subnet or corporate WAN was generally treated differently from traffic arriving from the public Internet. Distributed applications and remote access have made that model increasingly difficult to maintain.
A modern architecture can instead evaluate the context surrounding the request. The same user accessing the same application may receive different treatment depending on the device being used, authentication strength, security posture, destination, current risk and other policy signals.
This does not mean that every architecture uses exactly the same signals. The engineering principle is that access decisions should be based on relevant context rather than network location alone.
The Context Used by a Traffic Decision
Routing Decision vs Security Decision
One of the most important distinctions in a combined SD-WAN and SASE architecture is that path selection and security enforcement are related but different decisions.
These decisions may influence one another without becoming the same decision. For example, an application may require a low-latency path while a security policy requires the traffic to pass through a particular inspection service. The resulting architecture must satisfy both requirements.
Application-Aware Connectivity
SD-WAN can classify traffic according to application characteristics and apply different forwarding policies. This allows the network to distinguish between business-critical collaboration, voice, SaaS, bulk data and less-sensitive traffic rather than treating every packet identically.
Path selection can then consider measured conditions across the available transports. If one path develops excessive loss or latency, traffic may be moved to another path when the policy permits that change.
This creates an important feedback loop: application requirements influence connectivity, while real-time network telemetry influences path selection.
Identity-Aware Access
SASE architectures extend the decision beyond the network path. A request can be evaluated against an identity-aware policy that considers who the user is, what device they are using and what application they are attempting to reach.
A successful authentication does not necessarily mean that every subsequent request should receive unrestricted access. Additional signals can change the decision. A managed device may receive normal access, while an unmanaged device may be restricted. A high-risk sign-in may trigger stronger authentication, while an explicitly prohibited destination may be blocked.
This is where Zero Trust principles become relevant: trust should not be treated as a permanent property of a user, device or network location. Access should be evaluated according to the policy and context applicable to the request.
Four Possible Policy Outcomes
A Policy Decision Is a Point-in-Time Evaluation
A major advantage of combining identity, network and security telemetry is that policy can respond to changing conditions. A flow that was acceptable several minutes ago may no longer satisfy policy if the user's risk changes, the device loses compliance, the destination becomes suspicious or the traffic pattern becomes anomalous.
This is why modern access architectures increasingly treat authorisation as a continuing control rather than a single event that occurs only at login.
The engineering model therefore becomes: IDENTITY + DEVICE + APPLICATION + DESTINATION + NETWORK + RISK → POLICY DECISION. The resulting decision can then determine both how the traffic is connected and which security controls are required.
SD-WAN → SASE Traffic Decision
Application Request
The flow arrives with source, destination, protocol, port and application information. The first task is to understand what traffic is being requested.
Possible Policy Outcomes
The final result depends on the combined evidence rather than a single signal.
Secure Internet Access & SASE Enforcement
Direct Internet Access, SASE PoPs, secure web access, firewall services, threat inspection, cloud controls, data protection and policy-driven service chaining.
Section 03 — Secure Internet Access & SASE Enforcement
Once a traffic flow has been classified and a connectivity decision has been made, the next question is where security enforcement should occur. Modern users and applications increasingly communicate directly with SaaS platforms, public cloud services and the Internet. Sending every request back through a central enterprise security stack can introduce unnecessary latency and complexity, particularly when users and branches are geographically distributed.
Secure Internet Access combines direct connectivity with distributed security controls. SD-WAN can provide the path toward the Internet or cloud destination, while SASE security services can inspect and enforce policy closer to the source or destination of the traffic.
Direct Internet Access Changes the Traffic Path
In a traditional branch architecture, Internet-bound traffic may be backhauled across the WAN to a central data centre where firewalls, proxies and other security controls are located. This can provide centralised control, but it also means that traffic may travel farther than necessary before reaching its destination.
Direct Internet Access, or DIA, allows a branch or user location to connect directly to Internet destinations. The important security requirement is that direct connectivity must not mean direct, uncontrolled access.
The advantage is not simply shorter routing. The architecture can select an appropriate security enforcement point while preserving policy visibility and control.
The SASE Enforcement Point
A SASE architecture can provide a distributed security edge through cloud-based enforcement points. Traffic is directed to an appropriate security location where multiple controls can be applied according to the policy associated with the request.
Security Service Chaining
Not every request needs every security service. An important part of SASE enforcement is determining which controls should inspect a particular flow.
For example, a request to a known business SaaS application may require identity-aware access control and policy enforcement, while general web traffic may require secure web filtering and DNS security. A suspicious destination may trigger deeper threat inspection or be blocked before the connection proceeds.
This creates a policy-driven security service path rather than a fixed sequence in which every packet is forced through every available inspection engine.
Common SASE Security Controls
TLS Inspection Requires Deliberate Design
Encrypted traffic can limit the visibility available to security controls. Where an organisation chooses to perform TLS inspection, the architecture must account for certificate deployment, application compatibility, privacy requirements, performance overhead and regulatory or organisational policy.
TLS inspection should therefore be treated as a deliberate security control rather than an assumption that every encrypted session should automatically be decrypted and inspected.
Choosing the Enforcement Path
The ideal path is therefore not necessarily the shortest network path. It is the path that satisfies the combined requirements of connectivity, security, application performance and organisational policy.
Resilience is equally important. Distributed security introduces dependencies on SASE enforcement locations, Internet connectivity and cloud security services. Organisations should therefore consider availability, alternate enforcement locations, failure behaviour and what traffic should happen when a preferred security path is unavailable.
The engineering model for this section can be summarised as: DIRECT CONNECTIVITY → SECURITY ENFORCEMENT → INSPECTION → POLICY DECISION → DESTINATION. The goal is secure, observable access without introducing unnecessary traffic detours.
SD-WAN Secure DIA / Internet Breakout Explorer
Branch / User
A branch or remote user generates traffic destined for an Internet or SaaS application. Identity, device and application information can accompany the request.
Choose the Traffic Type
Secure Internet Access & SASE Enforcement
Behavioural telemetry, anomaly detection, trust scoring, correlated signals, adaptive policy, isolation and the feedback loop between networking and security operations.
Section 04 — Behaviour, Analytics & Adaptive Security
A secure SD-WAN and SASE architecture cannot depend entirely on decisions made when a user first authenticates or when a device initially connects. Conditions change. Devices lose compliance, identities become compromised, applications behave differently and traffic patterns can move outside their expected baseline.
Behavioural analytics and continuous telemetry provide the feedback required to recognise those changes. Instead of treating trust as a permanent state, the architecture can continuously evaluate whether the current behaviour still satisfies policy and adjust enforcement when the risk changes.
From Static Trust to Continuous Evaluation
Authentication establishes an important identity signal, but it does not guarantee that every action performed by that identity is legitimate. A valid account can be compromised, a trusted endpoint can become infected, or a legitimate session can begin behaving in a way that is inconsistent with normal activity.
Continuous evaluation introduces additional signals into the security decision. These can include authentication events, device posture, application activity, destination changes, traffic volume, connection frequency, error rates and other behavioural indicators.
What Behavioural Analytics Looks For
Behavioural analysis does not necessarily mean that one unusual event is automatically treated as an attack. Useful detection normally comes from combining multiple signals and comparing activity against expected behaviour, policy thresholds or known threat indicators.
Correlation Is More Valuable Than a Single Alert
A single unusual event may have a legitimate explanation. A user accessing a new application, for example, is not automatically evidence of compromise. The risk becomes more meaningful when multiple independent signals occur together.
Risk Is a Signal, Not the Final Decision
A risk score or behavioural anomaly should not automatically become a block action. Security policy determines how the organisation responds to the assessed risk. A moderate anomaly may justify additional authentication or monitoring, while a combination of severe signals may justify restricting or isolating the session.
Adaptive Security Changes the Policy State
Adaptive security means that policy can change when the underlying conditions change. A session does not necessarily remain in the same enforcement state for its entire lifetime.
Telemetry Connects Networking and Security Operations
One of the strengths of a combined SD-WAN and SASE architecture is the amount of telemetry available across the environment. Network performance, application behaviour, identity events and security detections can be correlated rather than investigated as completely separate data sources.
For example, an application slowdown might initially appear to be a network problem. Telemetry could reveal that the traffic pattern changed at the same time as a new destination was contacted and an identity risk signal appeared. The incident then becomes a security investigation rather than simply a path-performance issue.
This correlation is particularly valuable to security operations because it provides a broader view of what happened before, during and after a policy change.
Closing the Feedback Loop
The architecture introduced throughout this guide is therefore not a one-way traffic pipeline. It is a feedback system. Connectivity produces telemetry. Security controls produce detections. Identity systems produce context. Behavioural analytics correlate those signals. Policy then determines whether the current treatment should remain unchanged or be modified.
The resulting model is CONNECT → DECIDE → ENFORCE → ADAPT. SD-WAN provides the intelligent connectivity foundation, SASE extends security enforcement toward users and applications, and continuous telemetry allows the architecture to respond when the assumptions behind an access decision change.
Behaviour, Analytics & Adaptive Security
Observe a trusted session as its behaviour changes. Correlate identity, device, traffic and destination signals, then determine when policy should adapt.
A session that was acceptable at authentication time may require stronger controls later when identity, device posture, behaviour, destination or other risk signals change.
- BGP Solutions and Insights - October 8, 2026
- DMVPN - May 20, 2023
- Computer Networking: Building a Strong Foundation for Success - April 7, 2023