kubernetes security best practice

Kubernetes Security Best Practice

Kubernetes Securtiy Best Practices

Kubernetes provides a powerful control plane for deploying and operating containerised workloads, but its flexibility also creates a broad security surface. A production cluster contains APIs, identities, workloads, container images, secrets, network paths, nodes, admission controls, and supporting infrastructure. Securing Kubernetes therefore requires controls across the entire application and platform lifecycle.

The objective is not simply to secure the Kubernetes API or restrict who can create pods. A mature Kubernetes security strategy should reduce unnecessary privileges, control what workloads can run, restrict communication, protect sensitive data, monitor activity, and provide mechanisms for detecting and responding to abnormal behaviour.

Identity and Least Privilege

The Kubernetes API is a critical security boundary. Access should be based on authenticated identities and carefully defined authorisation policies.

Role-Based Access Control (RBAC) should follow the principle of least privilege, giving users and service accounts only the permissions they require. Broad cluster-wide permissions should be avoided where namespace-level access is sufficient.

Service accounts also require careful management. Workloads should not automatically receive powerful credentials simply because they run inside the cluster.

Workload Security

Pods and containers should run with the minimum privileges required by the application. Security contexts can be used to control user and group IDs, privilege escalation, Linux capabilities, filesystem behaviour, and other runtime characteristics.

Privileged containers and unnecessary host access should be treated as high-risk configurations because they can significantly weaken workload isolation.

Where appropriate, organisations should use mechanisms such as Pod Security Standards and admission policies to prevent insecure workload configurations from being deployed in the first place.

Container Image and Supply Chain Security

Kubernetes security begins before a workload reaches the cluster.

Container images should originate from trusted registries and controlled build pipelines. Images should be scanned for known vulnerabilities, unnecessary packages should be removed, and image provenance should be established where possible.

Production deployments can use immutable image references or digests rather than relying solely on mutable tags. Image signing and verification can provide additional assurance that approved artifacts are being deployed.

Software supply-chain security should also consider dependencies, build systems, CI/CD credentials, source repositories, and the tools responsible for producing deployment artifacts.

Network Policies and Segmentation

Kubernetes networking can allow workloads to communicate broadly unless appropriate restrictions are implemented.

NetworkPolicy can be used to define which pods are permitted to communicate with other workloads and external destinations. A default-deny approach can provide a stronger starting point, with only required communication paths explicitly permitted.

Segmentation should be based on application architecture and trust relationships rather than simply treating the cluster as one trusted network.

Ingress and egress paths also require protection. Externally exposed services should use appropriate authentication, encryption, rate limiting, and application-layer security controls where required.

Secrets and Sensitive Data

Passwords, API keys, certificates, tokens, and other sensitive information should be handled carefully throughout the Kubernetes lifecycle.

Kubernetes Secrets provide a mechanism for distributing sensitive configuration, but they should not automatically be considered a complete secrets-management solution. Access permissions, encryption at rest, auditability, rotation, and integration with external secrets-management systems should be considered according to the sensitivity of the workload.

Credentials should also be prevented from appearing in container images, source repositories, configuration files, or application logs.

API and Control Plane Security

The Kubernetes API server is one of the most important security components in the platform. Authentication, authorisation, encryption, audit logging, network exposure, and secure configuration should all be carefully controlled.

The control plane should not be unnecessarily exposed to untrusted networks. Administrative access should use strong authentication and tightly controlled privileges.

Admission controls can provide another important enforcement layer by validating or rejecting workloads that violate organisational security policies before they are accepted by the cluster.

Node and Runtime Security

Kubernetes workloads ultimately execute on nodes, making node security an essential part of cluster security.

Nodes should be patched and hardened, unnecessary services should be removed, and access to the underlying operating system should be restricted. Container runtimes and supporting Kubernetes components should also be kept current.

A compromised node can potentially affect multiple workloads, so workload isolation, node segmentation, runtime protections, and rapid replacement mechanisms are important components of defence in depth.

Logging, Monitoring, and Auditing

Security controls need visibility to be effective.

Kubernetes audit logs can provide information about API activity, while application logs, container runtime events, node telemetry, network data, and security alerts can provide additional context.

Monitoring should look for behaviours such as unexpected privilege changes, unusual API activity, suspicious workload creation, abnormal network connections, failed authentication attempts, and unexpected changes to cluster configuration.

Centralised collection and correlation can help security teams distinguish isolated operational events from indicators of a broader compromise.

Patch and Vulnerability Management

Kubernetes environments contain multiple software layers, including the Kubernetes components themselves, operating systems, container runtimes, images, applications, libraries, and infrastructure integrations.

Security updates should therefore be treated as a continuous lifecycle process. Vulnerability management should identify affected components, prioritise risk, apply patches or rebuild images, and verify that remediation has been successful.

Security as a Continuous Process

Kubernetes security is not achieved through a single configuration setting. It is a layered operating model:

Secure Identity → Least Privilege → Trusted Images → Admission Controls → Isolated Networking → Protected Secrets → Hardened Nodes → Runtime Monitoring → Audit and Response

The strongest Kubernetes environments assume that credentials can be compromised, applications can contain vulnerabilities, and individual workloads can fail or become malicious.

The objective is therefore to limit what a compromised identity or workload can access, detect suspicious behaviour quickly, and provide reliable mechanisms for containment and recovery.

By treating Kubernetes security as a continuous combination of prevention, isolation, detection, and response, organisations can significantly reduce the potential impact of vulnerabilities while maintaining the flexibility that makes Kubernetes valuable for modern application platforms.

Interactive Kubernetes Security Lab

Kubernetes Security Posture Builder

Start with a weak Kubernetes security posture and progressively harden the cluster. Select controls across identity, workloads, network, supply chain and observability, then validate the resulting security posture.

Scenario

Harden a production Kubernetes cluster

The cluster is running workloads but several security controls are missing. Your objective is to reduce privilege, constrain workload behaviour, protect the supply chain and improve visibility.

12
Security Score / 100
CRITICAL POSTURE

Security controls

Select controls you would introduce as part of a layered Kubernetes security strategy.

Identity & Access
Workload & Runtime
Network Security
Supply Chain & Data
Observability

Posture analysis

The score is a teaching aid. Real Kubernetes risk depends on architecture, workload sensitivity, threat model and implementation.

Identity protection LOW
Workload isolation LOW
Network controls LOW
Supply chain LOW
Visibility LOW
# Hardened configuration summary
RBAC: not configured
networkPolicy: not configured
podSecurity: not configured
imageVerification: not configured
auditLogging: not configured
[READY] Kubernetes security posture assessment initialized
[INFO] Cluster contains multiple unprotected security boundaries
Engineering takeaway: Kubernetes security is layered. RBAC controls API permissions, Pod Security controls workload security requirements, NetworkPolicy controls permitted network communication, image controls address supply-chain risk, and audit logging provides visibility into activity. No single control provides complete protection.

Highlights: Kubernetes Securtiy Best Practices

The Move to the Cloud

– Cloud workloads are typically managed with Kubernetes as they move to the cloud. Kubernetes’ popularity can be attributed to its declarative nature: It abstracts infrastructure details and allows users to specify which workloads they want to run. App teams only need to set up configurations in Kubernetes to deploy their applications; they don’t need to worry about how workloads are deployed, where workloads run, or other details like networking.

– To achieve this abstraction, Kubernetes manages the creation, shutdown, and restart of workloads. As a typical implementation, workloads can be scheduled on any available network resource (physical host or virtual machine) based on their requirements. Kubernetes clusters consist of resources that run workloads.

– As needed, Kubernetes restarts unresponsive nodes based on the status of workloads (which are deployed as pods in Kubernetes). It also manages the network between pods and hosts and pod communication. Network plug-ins allow you to select the type of networking technology. Although the network plug-in has some configuration options, you cannot directly control networking behavior (either IP address assignment or scheduling).

An Orchestration Tool

Kubernetes has quickly become the de facto orchestration tool for deploying Kubernetes microservices and containers to the cloud. It offers a way of running groups of resources as a cluster and provides an entirely different abstraction level to single container deployments, allowing better management. From a developer’s perspective, it will enable the rolling out of new features that align with business demands while not worrying about the underlying infrastructure complexities.

Security Pitfalls: But there are pitfalls to consider when considering Kubernetes security best practices and Docker container security. Security teams must maintain the required visibility, compliance, and control, which is difficult because they do not control the underlying infrastructure. To help you on your security journey, you should introduce a chaos engineering project, specifically chaos engineering kubernetes.

This will help you find the breaking points and performance-related issues that may indirectly create security gaps in your Kubernetes cluster, making the cluster acceptable to Kubernetes attack vectors.

Kubernetes Security Best Practices

Kubernetes security is about protecting clusters, nodes, pods, containers, identities, and the control plane in a dynamic, distributed environment. Because Kubernetes is highly automated and highly scalable, misconfigurations can spread quickly — so security must be layered, enforced, and continuously verified.

Below is a clean, easy‑to‑copy, production‑grade breakdown you can drop directly into your notes, blog, or architecture docs.


1. Secure the Control Plane

  • API server hardening — restrict access, enforce RBAC, enable audit logs.

  • etcd encryption — encrypt secrets at rest.

  • TLS everywhere — secure all communication between components.

  • Network segmentation — isolate control plane from worker nodes.

The control plane is the brain — protect it first.


2. Identity & Access Security

  • RBAC — least‑privilege roles and role bindings.

  • Service Accounts — avoid using default service accounts.

  • OIDC integration — integrate with enterprise identity providers.

  • Pod Security Standards — enforce restricted policies.

Identity is the new perimeter.


3. Container & Runtime Security

  • Image scanning — scan images for CVEs before deployment.

  • Trusted registries — block untrusted sources.

  • Drop capabilities — remove unnecessary Linux capabilities.

  • Seccomp profiles — restrict dangerous syscalls.

  • AppArmor / SELinux — enforce mandatory access control.

  • Read‑only root filesystem — prevent tampering.

Containers must be locked down by default.


4. Network Security

  • NetworkPolicies — restrict pod‑to‑pod communication.

  • Service Mesh — mTLS, identity‑aware routing, policy enforcement.

  • Ingress security — TLS, WAF, rate limiting.

  • Egress control — restrict outbound traffic.

Kubernetes networking is open by default — close it.


5. Secrets & Config Security

  • Encrypt secrets at rest

  • Use external secret stores (Vault, AWS KMS, Azure Key Vault)

  • Avoid secrets in environment variables

  • Rotate secrets regularly

Secrets must never be treated as normal config.


6. Node & OS Security

  • Harden nodes — disable unused services, enforce firewall rules.

  • Use minimal OS images — reduce attack surface.

  • Keep nodes patched — automate updates.

  • Limit root access — protect kubelet and container runtime.

Nodes are the foundation — secure them aggressively.


7. Supply Chain Security

  • Image signing — verify trusted images (cosign, sigstore).

  • Admission controllers — block unsafe deployments.

  • Policy engines — enforce OPA Gatekeeper or Kyverno.

  • SBOMs — track dependencies and vulnerabilities.

Supply chain attacks are now the #1 cloud threat.


8. Observability & Runtime Monitoring

  • Audit logs — track API calls and changes.

  • Prometheus + Grafana — metrics and dashboards.

  • OpenTelemetry — traces and logs.

  • Falco — detect runtime anomalies.

  • Cluster health monitoring — detect drift and misconfigurations.

Visibility is mandatory for security.


Outcome

Kubernetes security best practices deliver:

  • hardened control plane

  • secure workloads and containers

  • strong identity enforcement

  • Zero Trust network segmentation

  • protected supply chain

  • continuous compliance

  • runtime threat detection

  • reliable, production‑grade cluster posture

Kubernetes becomes a secure, resilient, enterprise‑ready platform.

Before you proceed, you may find the following posts helpful:

  1. OpenShift SDN
  2. Hands On Kubernetes
  3. Kubernetes Network Namespace


Kubernetes Securtiy Best Practices

Incident Investigation

Kubernetes Attack Path Investigation Lab

A workload has been compromised. Investigate the evidence and reconstruct how an attacker could move from a compromised Pod toward Kubernetes API resources, secrets and other workloads.

Incident Scenario

Compromised workload detected

The application Pod is behaving suspiciously. Determine which security weaknesses contribute to the attack path. Select the evidence that should be investigated before drawing a conclusion.

Investigation evidence

Select the evidence you believe contributes to the attack path. Not every Kubernetes workload has every weakness.

Potential attack path

Your investigation should connect workload compromise with identity, authorization, API access and lateral movement.

Compromised Pod
↓
ServiceAccount Identity
↓
Kubernetes API Server
↓
Excessive RBAC Permissions
↓
Secrets / Workloads
↓
Lateral Movement
Workload UNDER INVESTIGATION
API Access UNKNOWN
Authorization UNKNOWN
Lateral Movement UNKNOWN
[READY] Incident investigation initialized
[INFO] Select evidence before running the investigation
Engineering takeaway: a Kubernetes ServiceAccount does not automatically have full API permissions. The security risk depends on the RBAC bindings assigned to that identity. Attackers often chain multiple weaknesses: workload compromise, excessive permissions, API access, secrets exposure and unrestricted network paths.

As workloads move to the cloud, Kubernetes is the most common orchestrator for managing them. Kubernetes’s popularity is due to its declarative nature: It abstracts infrastructure details and allows users to specify the workloads they want to run and the desired outcomes.

However, securing, observing, and troubleshooting containerized workloads on Kubernetes is challenging. It requires a range of considerations, from infrastructure choices and cluster configuration to deployment controls, runtime, and network security. Keep in mind that Kubernetes is not secure by default.

Kubernetes Architecture

Before we delve into some of Kubernetes’ security best practices and attack vectors, let’s recap Kubernetes Networking 101. Within Kubernetes, four common constructs will always be: pods, services, labels, and replication controllers. All constructs combine to create an entire application stack.

Pods

Pods are the smallest scheduling unit within a Kubernetes environment. They hold a set of closely related containers. Containers within a Pod share the same network namespace and must be installed on the same physical host. This enables processing locally without latency traversing from one physical host to another.

Labels

As I said, containers within a pod share the same network namespaces. As a result, the containers within a pod can reach each other’s ports on localhost. Therefore, we need to introduce a tagging mechanism known as labels. Labels offer another level of abstraction by tagging items as a group. They are essentially key-value pairs categorizing constructs. For example, labels distinguish containers as part of an application stack’s web or database tier.

Replication Controllers (RC)

Then, we have replication controllers. Their primary purpose is to manage the pods’ lifecycle and state by ensuring the desired state always matches the actual state. The replication controllers ensure the correct numbers are running by creating or removing pods at any time.

Services

Other standard Kubernetes components are services. Services represent groups of pods acting as one, allowing pods to access services in other pods without directing service-destined traffic to the pod IP. Pods are targeted by accessing a service that represents a group of pods. A service can be analogous to a load balancer in front of a pod accepting front-end service-destined traffic.

Kubernetes API server

Finally, the Kubernetes API server validates and configures data for the API objects, which include the constructs mentioned above—pods, services, and replication controllers, to name a few. Also, consider the practice of chaos engineering to understand your Kubernetes environment better and test for resilience and breaking points. Chaos engineering Kubernetes breaks your system to help you better understand it.

Listing Kubernetes Security Controls

  • Regularly Update Kubernetes:

Keeping your Kubernetes environment up to date is one of the fundamental aspects of maintaining a secure cluster. Regularly updating Kubernetes ensures you have the latest security patches and bug fixes, reducing the risk of potential vulnerabilities.

  • Enable RBAC (Role-Based Access Control):

Implementing Role-Based Access Control (RBAC) is crucial for controlling and restricting user access within your Kubernetes cluster. By assigning appropriate roles and permissions to users, you can ensure that only authorized personnel can perform specific operations, minimizing the chances of unauthorized access and potential security breaches.

  • Use Network Policies:

Kubernetes Network Policies allow you to define and enforce rules for network traffic within your cluster. Effectively utilizing network policies can isolate workloads, control ingress and egress traffic, and prevent unauthorized communication between pods. This helps reduce the attack surface and enhance the overall security posture of your Kubernetes environment.

  • Employ Pod Security Policies:

Pod Security Policies (PSPs) enable you to define security configurations and restrictions for pods running in your Kubernetes cluster. By defining PSPs, you can enforce policies like running pods with non-root users, disallowing privileged containers, and restricting host namespace sharing. These policies help prevent malicious activities and reduce the impact of potential security breaches.

  • Implement Image Security:

Ensuring the security of container images is crucial to protect your Kubernetes environment. Employing image scanning tools and registries that provide vulnerability assessments allows you to identify and address potential security issues within your images. Additionally, only using trusted and verified images from reputable sources reduces the risk of running compromised or malicious containers.

  • Monitor and Audit Cluster Activity:

Implementing robust monitoring and auditing mechanisms is essential for promptly detecting and responding to security incidents. By leveraging Kubernetes-native monitoring solutions, you can gain visibility into cluster activity, detect anomalies, and generate alerts for suspicious behavior. Furthermore, regularly reviewing audit logs helps identify potential security breaches and provides valuable insights for enhancing the security posture of your Kubernetes environment.

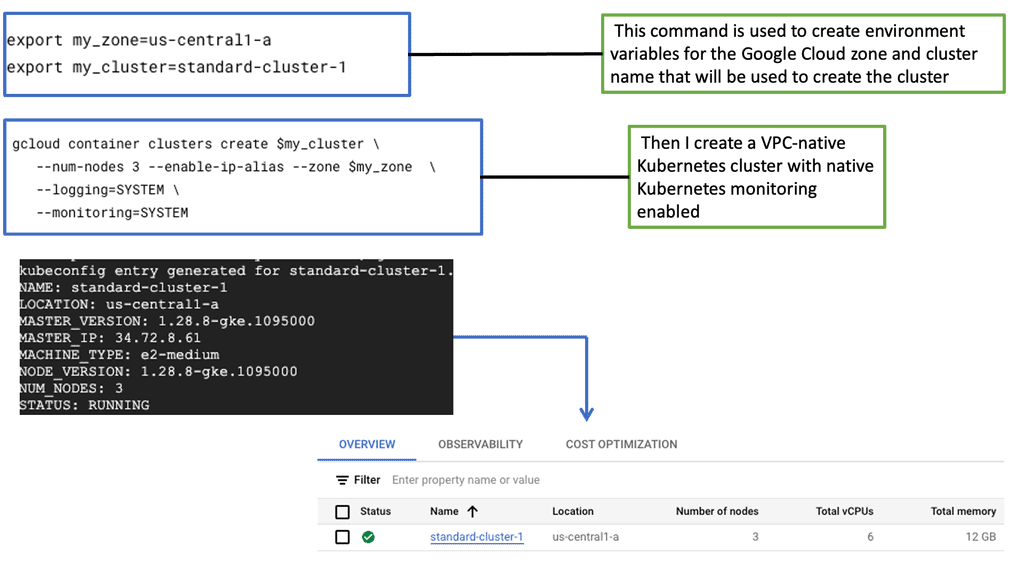
**Understanding GKE-Native Monitoring**

GKE-native monitoring provides a seamless and integrated way to collect, analyze, and visualize metrics and logs from your GKE clusters. By leveraging Google Cloud’s robust monitoring services like Stackdriver, GKE offers a comprehensive solution for monitoring the health and performance of your applications. With GKE-native monitoring, you gain valuable insights into resource utilization, latency, error rates, and more, enabling you to make data-driven decisions and ensure optimal performance.

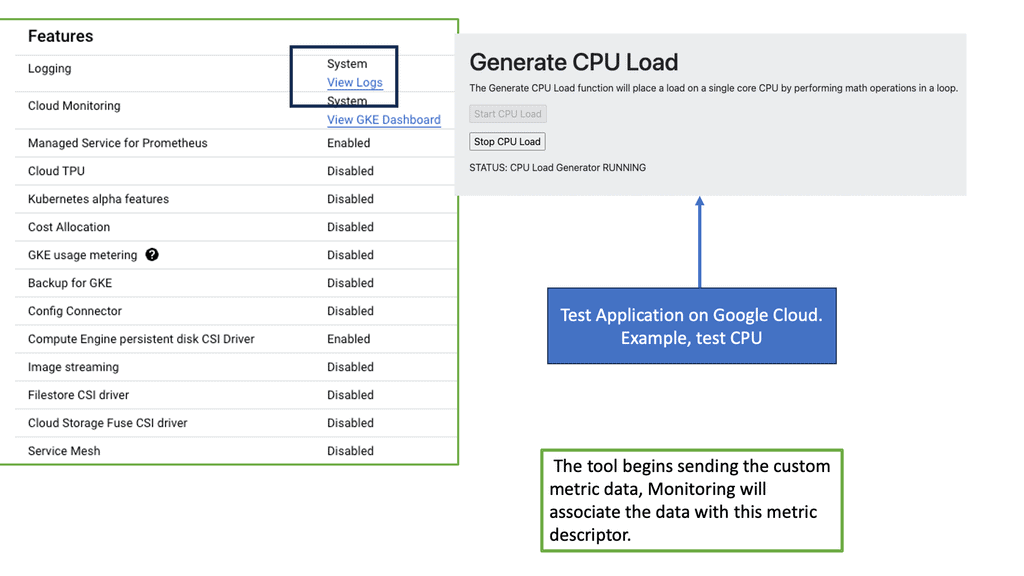
Logging plays a crucial role in understanding your applications’ behavior and diagnosing issues. GKE-native logging allows you to capture and analyze logs from your GKE clusters effortlessly. With Stackdriver Logging, you can collect logs from various sources, including application logs, system logs, and even logs from managed services running on GKE. This unified logging platform provides powerful filtering, searching, and alerting capabilities, making troubleshooting issues easier and gaining deeper insights into your system.
Kubernetes Attack Vectors

The hot topic for security teams is improving Kubernetes security, implementing Kubernetes security best practices within the cluster, and making container networking deployments more secure. Kubernetes is a framework that provides infrastructure and features. However, thinking outside the box regarding Kubernetes’ best security practices would be best.

We are not saying that Kubernetes doesn’t have built-in security features to protect your application architecture! These include logging and monitoring, debugging and introspection, identity, and authorization. But ask yourself: Do these defaults cover all aspects of your security requirements? Remember that much of the complexity with Kubernetes can be abstract with OpenShift networking.

Traditional Security Constructs  

A: -) Traditional security constructs don’t work with containers, as we have seen with the introduction of Zero Trust Networking. Containers have a different security model as they are short-lived and immutable. For example, securing containers differs from securing a virtual machine (VM).

B: -) For one, the attack surface is smaller, as containers usually only live for about a week, as opposed to a VM that may stay online forever. As a result, we need to manage vulnerabilities and compliance throughout the container scheduler lifecycle—from build tools to image registries to production.

C: -) How do you measure security within a Kubernetes environment? No one can ever be 100% secure, but one should follow certain best practices to harden the gates against bad actors. You can have different levels of security within other parts of the Kubernetes domain. However, a general Kubernetes security best practice would be introducing as many layers of protection as possible between your Kubernetes environment and the bad actors to secure valuable company assets.

Hacker sophistication

Hackers are growing in sophistication. We started with script kiddies in the 1980s and are now entering a world of artificial intelligence ( AI ) and machine learning (ML) in the hands of bad actors. They have the tools to throw everything and anything at your Kubernetes environment, dynamically changing attack vectors on the fly. If you haven’t adequately secured the domain, once a bad actor gains access to your environment, they can move laterally throughout the application stack, silently accessing valuable assets.

Kubernetes Security Best Practice: Security 101

Now that you understand the most commonly used Kubernetes constructs let’s explore some of the best practices for central Kubernetes security and attack vectors.

**Kubernetes API**

Firstly, a bad actor can attack the Kubernetes API server to attack the cluster further. By design, each pod has a service account associated with it. The service account has full permissions and sufficient privileges to access the Kubernetes API server. A bad actor can get the token mounted in the pod and then use that token to gain access to the API server.

Unfortunately, once they can access the Kubernetes API server, they can get information, such as secrets, to compromise the cluster further. For example, a bad actor could access the database server where sensitive and regulatory data is held.

**Kubernetes API – Mitigate**

Another way to mitigate a Kubernetes API attack is to introduce role-based access control (RBAC). Essentially, RBAC gives rules to service accounts that can be assigned to the entire cluster. RBAC allows you to set permission on individual constructs such as pods and containers and then define rules based on personal use cases.

Another Kubernetes best practice would be to introduce an API server firewall. This firewall would work similarly to a standard firewall, where you can allow and block ranges of addresses. Essentially, this narrows the attack surface, hardening Kubernetes security.

**Secure pods with network policy**

Introducing ingress and egress network policies would allow you to block network access to certain pods. Only then can certain pods communicate with each other. For example, network policies can be set up to restrict the web front end from communicating directly to the database tier.

There is also a risk of a user implementing unsecured pods. In this case, you can have network policies in place so that if an unsecured pod does appear in the Kubernetes environment, the Kubernetes API will reject it.

Remember, left to its defaults, intra-cluster pod-to-pod communication is open. You may think a bad actor could sniff this traffic, but that’s harder to do than in everyday environments. A better strategy to harden Kubernetes security would be to use a network policy that only allows certain pods to communicate with each other.

**Container escape**

In the past, an unpatched kernel or a bug in the web front-end allowed a bad actor to exit a container and gain access to other containers or even to the Kubelet process itself. Once the bad actor gets access to the Kubelet client, it can access the API server, gaining a further foothold in the Kubernetes environment.

**Sandboxed Pods**

One way to mitigate a container escape would be to introduce sandboxed pods inside a lightweight VM. A sandboxed pod provides additional barriers to security as it lies above the kernel itself. Providing layers of protection above the kernel brings many Kubernetes security advantages. As the sandboxed pod runs inside a VM, an additional bug is required to break out of the container if there is a kernel exploit.

**Scanning containers**

For adequate Kubernetes security, you should know if your container image is vulnerable. Running containers with vulnerabilities exposes the entire system to attacks. Scanning all container images to discover and remove known vulnerabilities would be best. The scanning function should integrate runtime enforcement and remediation capabilities, enabling a secure and compliant SDLC (Software Development Life Cycle).

**Restrict access to Kubectl**

Kubectl is a powerful command-line interface for running commands against Kubernetes clusters. It allows you to create and update resources in a Kubernetes environment. Due to its potential, one should restrict access to this tool with firewall rules.

Disabling the Kubernetes dashboard is a must, as it has been part of some high-profile compromises. Previously, bad actors accessed a publicly unrestricted Kubernetes dashboard and privileged account credentials to access resources and mine cryptocurrency.

As Kubernetes adoption continues to grow, ensuring the security of your cluster becomes increasingly essential. By following these Kubernetes security best practices, you can establish a robust security foundation for your infrastructure and applications.

Regularly updating Kubernetes, enabling RBAC, utilizing network policies, employing pod security policies, implementing image security measures, and monitoring cluster activity will significantly enhance your security posture. Embracing these best practices will protect your organization’s sensitive data and provide peace of mind in today’s ever-evolving threat landscape.

Containment & Segmentation

Kubernetes Network & Runtime Segmentation Lab

A frontend Pod has been compromised. Build a least-privilege security boundary around the application so that the compromised workload cannot freely reach the API or database.

Application topology

Protect the application dependency chain

The intended application flow is Internet → Ingress → Frontend → API → Database. The objective is to permit required traffic while preventing unnecessary lateral movement.

Internet external
→
Ingress entry point
→
Frontend workload
→
API service
→
Database data tier

Required traffic policy

These are the intended application dependencies. Everything else should be treated as unnecessary unless explicitly required.

Internet → Ingress Public application entry
ALLOW
Ingress → Frontend Application frontend
ALLOW
Frontend → API Required application call
ALLOW
API → Database Required data access
ALLOW
Frontend → Database Bypass of API tier
DENY
Database → Internet Unnecessary egress
DENY
API → Internet Restrict unless required
DENY

Containment controls

Apply multiple layers. Network segmentation alone does not replace workload or identity security.

⚠ COMPROMISED FRONTEND

The attacker attempts to bypass the API tier and connect directly to the Database.

[READY] Segmentation lab initialized
[INFO] Frontend compromise is simulated
[INFO] Apply controls before running the attack test
Engineering takeaway: Kubernetes NetworkPolicy can restrict which Pods may communicate, but effective enforcement depends on the cluster's network plugin and policy configuration. Combine network controls with least-privilege RBAC, workload security, runtime restrictions and controlled egress to reduce lateral movement and blast radius.