Cloud Native Meaning

In today’s technology landscape, the term cloud native is used extensively across software engineering, infrastructure, DevOps, and platform engineering. But cloud native is more than simply running an application in the cloud.

Cloud native is an architectural and operational approach to building and running applications so they can take advantage of the elasticity, automation, distributed infrastructure, and on-demand capabilities of modern cloud platforms.

A cloud-native application is designed with change, scale, failure, and automation in mind. Rather than treating the cloud as simply another place to host servers, cloud-native architectures use cloud capabilities as part of the application’s operating model.

Several technologies and practices commonly support this approach:

Microservices and modular architectures break applications into smaller, independently deployable components. This can allow teams to develop, release, scale, and update individual services without having to redeploy an entire application. Not every cloud-native system requires microservices, but independently deployable components are a common design pattern.

Containers package applications and their dependencies into portable execution environments. This improves consistency between development, testing, and production environments and provides a common foundation for automated deployment.

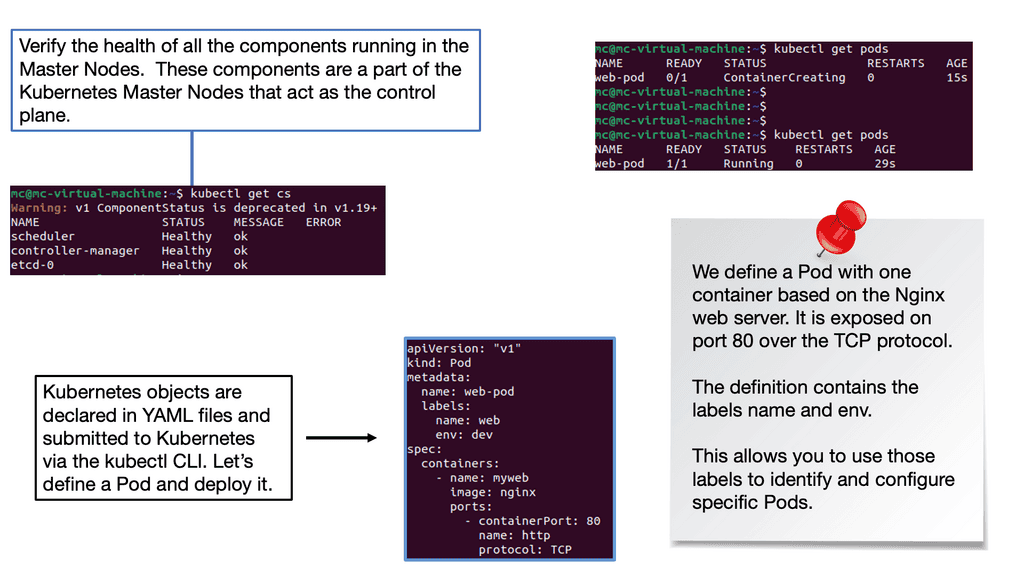
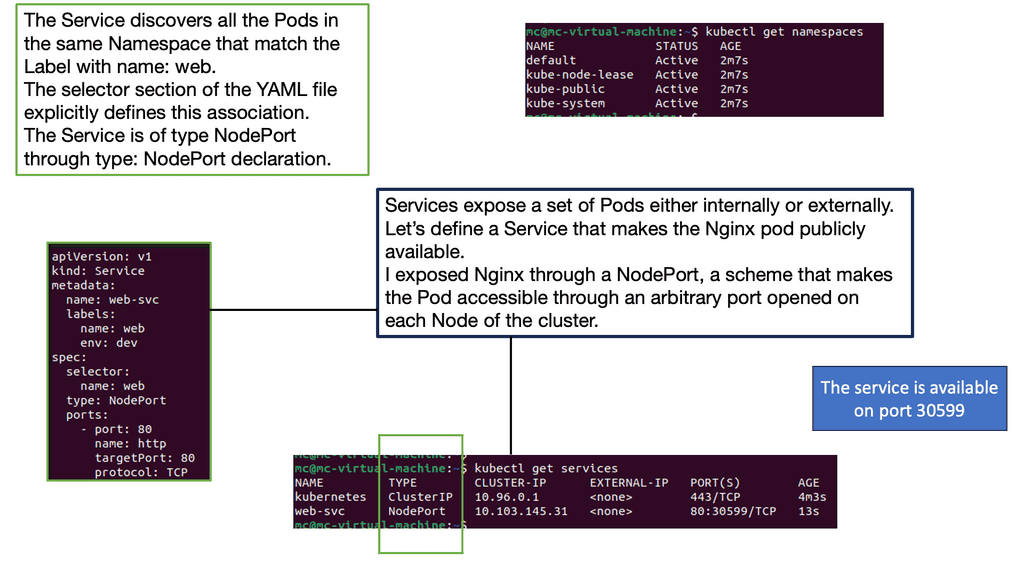
Orchestration and platform automation allow infrastructure and workloads to be managed programmatically. Platforms such as Kubernetes can automate scheduling, service discovery, scaling, rolling deployments, and workload recovery across distributed environments.

APIs and loosely coupled services allow application components and external systems to communicate through well-defined interfaces. This makes it easier to evolve individual components without creating tight dependencies throughout the entire platform.

Automation and Infrastructure as Code move infrastructure and operational configuration into repeatable, version-controlled processes. Tools such as Terraform, Ansible, and cloud-provider automation services can help reduce manual configuration and improve consistency.

Observability is also fundamental to modern cloud-native environments. Metrics, logs, traces, health information, and events provide visibility into distributed applications and help engineering teams identify performance problems and failures.

The result is an architecture designed around several important characteristics:

Scalability and elasticity: workloads can respond to changing demand by adding or removing resources automatically or through controlled automation.

Resilience and fault tolerance: applications are designed to continue operating when individual services, instances, containers, or infrastructure components fail.

Continuous delivery: automated build, test, deployment, and rollback processes allow changes to move through environments more frequently and consistently.

Operational automation: repetitive infrastructure and application-management tasks can be handled by software rather than manual intervention.

Independent change: well-designed components can evolve and be deployed without requiring the entire application to change at the same time.

Cloud native therefore should not be viewed as a single technology or product. Kubernetes is not synonymous with cloud native, containers are not synonymous with cloud native, and moving an existing application into a public cloud does not automatically make it cloud native.

Instead, cloud native represents a way of designing, delivering, and operating applications for a highly automated, distributed environment.

Understanding this distinction is important because the real value of cloud native architecture comes from combining architecture, automation, platform engineering, observability, security, and operational practices rather than adopting a particular technology in isolation.

Cloud-native meaning

Highlights: Cloud-native meaning

Cloud-Native Architecture Builder

Assemble the capabilities that turn a traditional application into a cloud-native architecture.

Learning Objective

Understand how microservices, containers, orchestration, automation, scalability, resilience, and observability combine to create a cloud-native application platform.

Architecture Components

Select the capabilities you would expect in a complete cloud-native platform.

Entry Layer User / API Request
↓
Application Layer Microservice Layer
↓
Runtime Layer Container Runtime
↓
Platform Layer Kubernetes / Orchestration

Architecture Assessment

The platform is evaluated against seven cloud-native engineering capabilities.

0/7
Architecture incomplete Select capabilities and build the architecture to run the assessment.
Microservices architecture Missing
Containerization Missing
Dynamic orchestration Missing
Automation and CI/CD Missing
Scalability and elasticity Missing
Resilience and fault tolerance Missing
Observability Missing
Architecture Console
READY


Select architecture capabilities.
Build the architecture to evaluate the design.

Engineering Takeaway

Cloud-native is more than running an application in the cloud. The architecture combines independently deployable services, containerized workloads, automated delivery, dynamic orchestration, elastic scaling, resilience, and observability so the platform can continuously adapt to changing application demand.

**The Core Principles of Cloud-Native**

Cloud-native applications are designed with several key principles in mind. Firstly, they are built to be resilient. By using microservices architecture, applications can be designed as a suite of independently deployable services, which enhances fault tolerance.

Secondly, they are scalable. Cloud-native applications leverage the elasticity of the cloud environment, allowing resources to be scaled up or down based on demand.

Thirdly, automation is at the heart of cloud-native practices. From deployment to management, automation tools and practices (like CI/CD pipelines) ensure that updates and scaling can happen seamlessly, reducing human error and speeding up the development process.

**Benefits of Adopting Cloud-Native Practices**

The benefits of adopting cloud-native practices are manifold. Organizations can achieve greater agility since they are no longer constrained by traditional IT infrastructure. This agility allows businesses to innovate faster, bringing new features and products to market more rapidly.

Additionally, the cost-effectiveness of the cloud-native model can’t be overstated. By optimizing resource use and only paying for what they actually use, companies can significantly reduce operational costs. Furthermore, with enhanced resilience and quicker recovery times, cloud-native applications can ensure better uptime and reliability for end-users.

**Overcoming Challenges in Cloud-Native Transition**

While the advantages are clear, transitioning to a cloud-native architecture is not without its challenges. One of the primary hurdles is the cultural shift required within organizations. Developers and IT teams must embrace new tools, methodologies, and ways of thinking. Security is another concern, as the distributed nature of cloud-native applications can introduce new vulnerabilities. Lastly, there’s the complexity of managing microservices. With potentially hundreds of services interacting with each other, maintaining smooth communication and operation requires robust orchestration and monitoring tools.

Understanding Cloud-Native

At its core, cloud-native refers to an approach that leverages cloud computing and embraces the full potential of the cloud environment. It involves designing, developing, and deploying applications specifically for the cloud rather than simply migrating existing applications to the cloud infrastructure. Certain principles are essential to embody the cloud-native philosophy truly. They include:

1. Microservices Architecture: Cloud-native applications are built as a collection of small, independent services that work together to provide complete functionality. This modular approach allows for scalability, flexibility, and easier maintenance.

2. Containerization: Containers like Docker play a crucial role in cloud-native development. They encapsulate an application and its dependencies, providing consistency across different environments and enabling portability.

3. DevOps Culture: Cloud-native development embraces a collaborative culture between development and operations teams. Automation, continuous integration, and continuous deployment are key pillars of this culture, ensuring faster and more efficient software delivery.

Cloud-native Applications

Cloud-native applications exhibit distinctive characteristics that set them apart from traditional software. They are typically containerized, leveraging technologies like Docker or Kubernetes for efficient deployment, scaling, and management. Moreover, these applications are built using microservices architecture, allowing for modular development and enabling teams to work independently on different components. This decoupled nature brings flexibility and promotes rapid innovation.

One of the most significant advantages of going cloud-native lies in its ability to foster innovation and agility. By embracing cloud-native principles, development teams can expedite the release of new features and updates, enabling faster time-to-market. The modular nature of microservices architecture facilitates continuous integration and deployment (CI/CD), empowering developers to iterate rapidly, respond to user feedback, and deliver value to customers more efficiently.
Adopting cloud-native practices brings numerous advantages to businesses and developers alike. Some of the key benefits include:

1. Scalability and Elasticity: Cloud-native applications can effortlessly scale up or down to meet demand, thanks to the flexible nature of the cloud environment. This allows businesses to optimize resource usage and deliver optimal user experiences.

2. Faster Time-to-Market: Leveraging cloud-native principles speeds up the software development lifecycle. Microservices architecture enables parallel development, while containerization and automation streamline deployment, resulting in faster time-to-market for new features and updates.

3. Resilience and Fault Tolerance: Cloud-native applications are designed to resist failures. Cloud-native applications can recover quickly from failures and ensure high availability by utilizing distributed systems, redundant components, and automated monitoring.

—-

A-)  A Cloud Native architecture consists of developing software applications as a collection of loosely coupled, independent, business capability-oriented services (microservices) that are automated, scalable, resilient, manageable, and observable across dynamic environments (public, private, hybrid, and multi-cloud).

B-) Cloud-based applications are increasingly common due to their agility, reliability, affordability, and scalability. Application deployment and operations are primarily the focus of current cloud-native architectures. However, applying conventional application development patterns and techniques is impossible. When developing cloud-native applications

—-

Google Cloud Data Centers

### The Power of Kubernetes

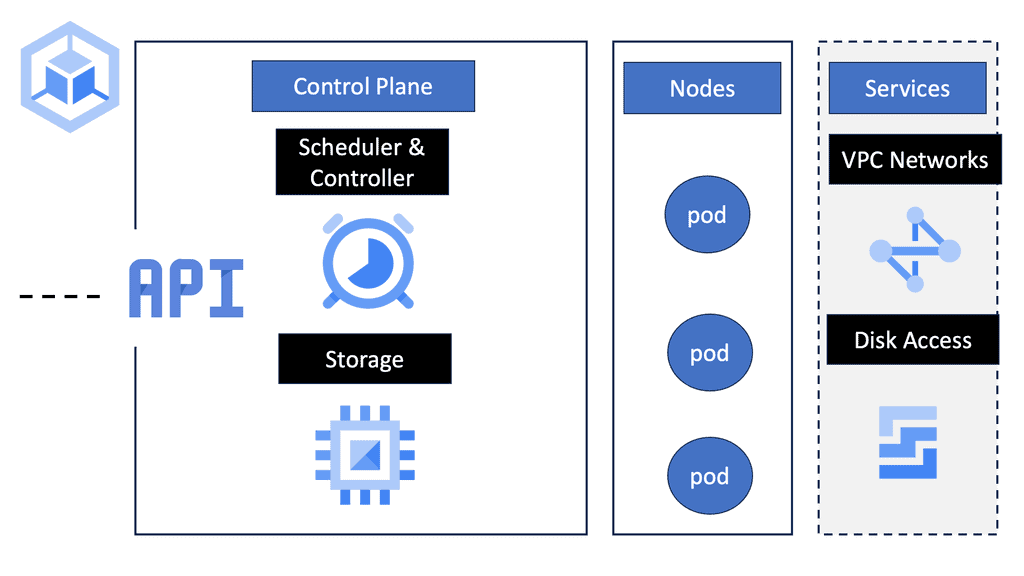
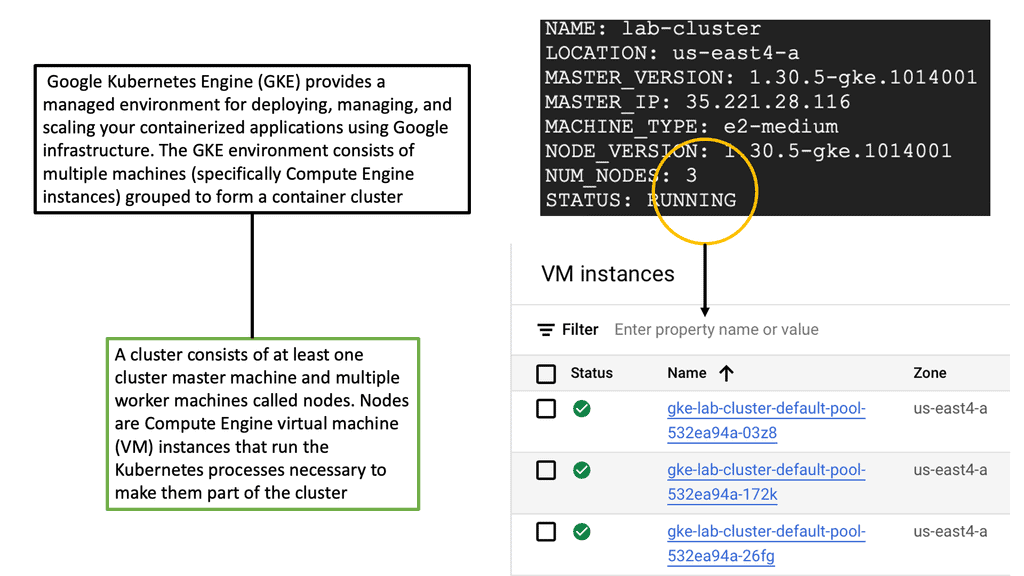
Kubernetes has revolutionized the way we think about deploying applications. Originally developed by Google, Kubernetes is an open-source platform designed to automate the deployment, scaling, and operation of application containers. As a managed service, GKE extends these capabilities, allowing users to harness the full power of Kubernetes without the complexity of managing the infrastructure. This means you can focus more on developing your applications and less on the underlying systems.
### Key Features of Google Kubernetes Engine

GKE offers a plethora of features tailored for efficiency and performance. One of the standout features is its auto-scaling capability, which ensures that your applications have the right amount of resources at any given time. This flexibility is crucial for handling varying workloads and traffic spikes. Moreover, GKE’s integration with other Google Cloud services provides a seamless ecosystem for developers, enhancing capabilities such as monitoring, logging, and security.

### Embracing Cloud-Native with GKE

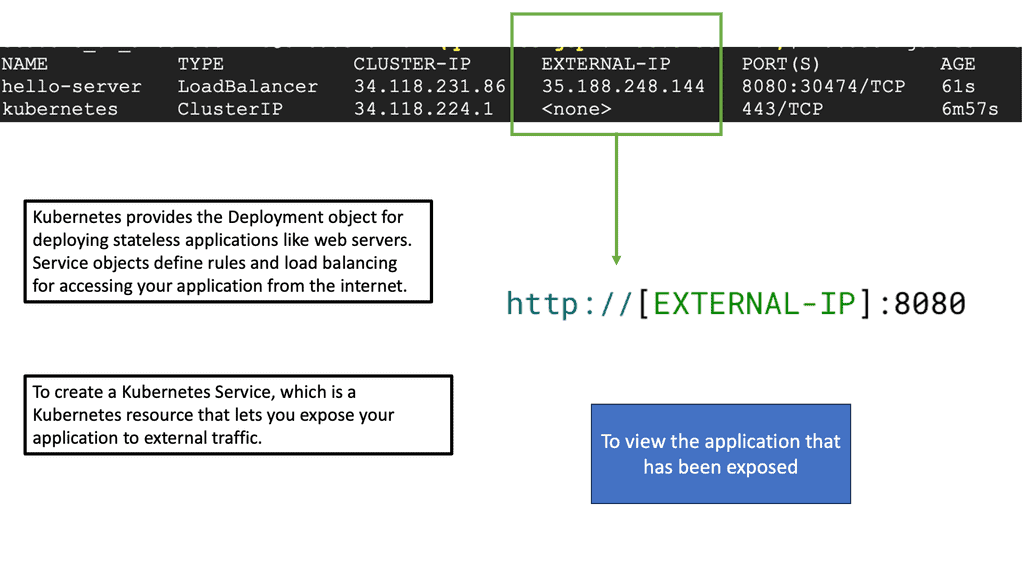
Adopting a cloud-native approach means building applications that fully leverage the cloud’s advantages. GKE supports this by providing a platform that is both resilient and scalable. By using microservices architecture, developers can create applications that are more modular and easier to manage. This not only improves development cycles but also enhances the overall reliability of applications. Additionally, GKE’s continuous integration and continuous delivery (CI/CD) support streamline the path from development to production.
Google Kubernetes Engine**The Journey To Cloud Native**

We must find ways to efficiently secure cloud-native microservice environments and embrace a Zero Trust Network Design. To assert who we say we are, we need to provide every type of running process in an internal I.T. infrastructure with an intrinsic identity. So, in our journey for cloud-native meaning, how do you prove who you are flexibly, regardless of what platform?

**Everything is an API Call**

First, you need to give someone enough confidence to trust your words. I.P. addresses are like home addresses, creating a physical identity for the house but not telling you who the occupants are. The more you know about the people living in the house, the richer the identity you can give them. The richer the identity, the more secure the connection.

Larger companies have evolved their authentication and network security components to support internal service-to-service, server-to-server, and server-to-service communications. Everything is an API call. There may only be a few public-facing API calls, but there will be many internal API calls, such as user and route lookups.

In this situation, CASB tools will help your security posture. However, this will result in a scale we have not seen before. Companies like Google and Netflix have realized there is a need to move beyond what most organizations do today.

Example – Service Networking API

**Understanding the Basics**

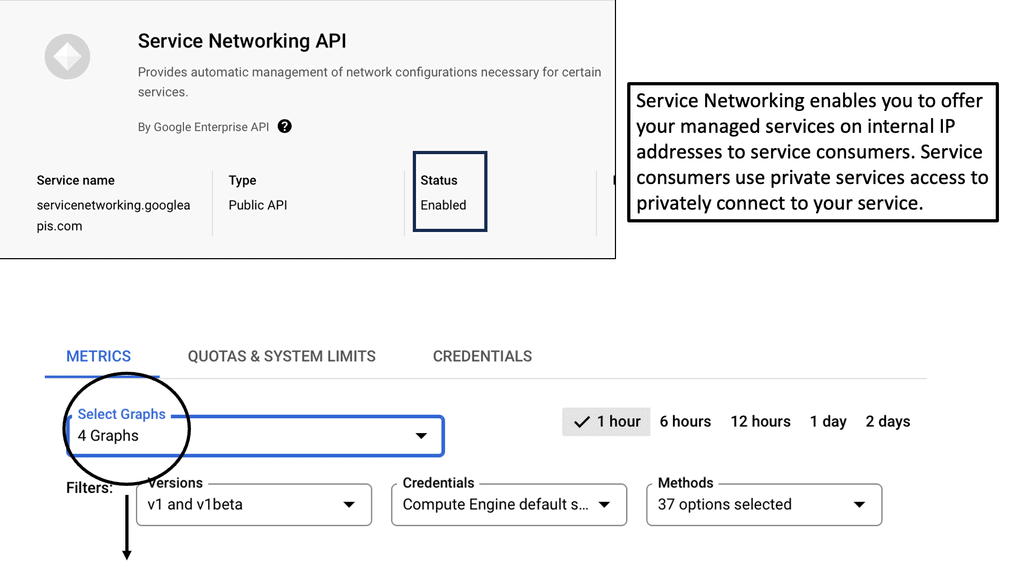
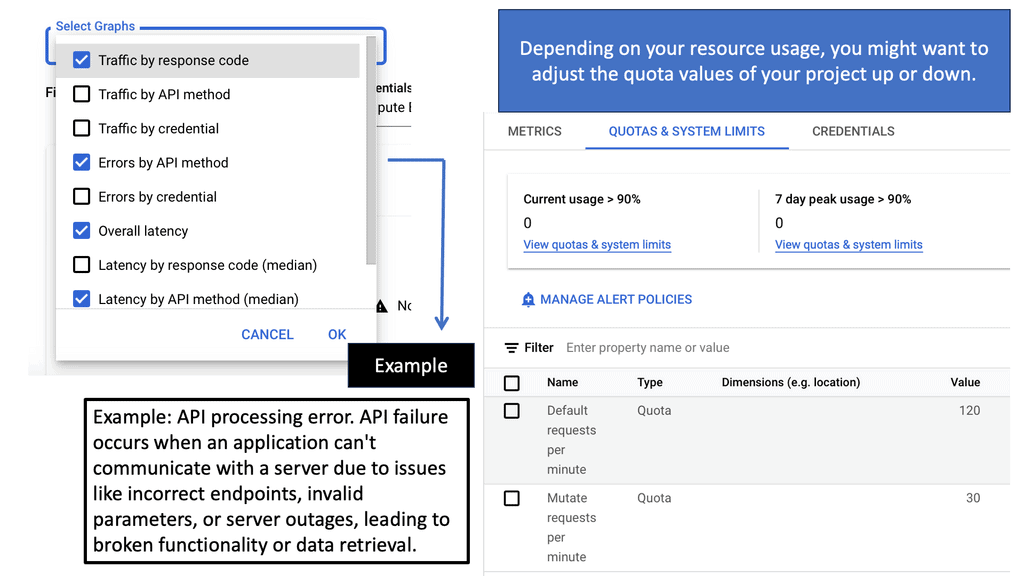
The Service Networking API is designed to simplify the process of establishing private connections between your Virtual Private Cloud (VPC) networks and Google Cloud services. By using this API, you can create private connections, known as VPC Network Peering, which enable secure communication without exposing your data to the public internet. This ensures that your data remains protected while also reducing latency and improving the overall performance of your applications.

**Key Features and Benefits**

One of the primary advantages of using the Service Networking API is its ability to provide a seamless integration between your on-premises infrastructure and Google Cloud services. This includes not only the basic connection setup but also automated IP address management and routing configuration. Additionally, the API supports a range of Google Cloud services, including Cloud SQL, Memorystore, and AI Platform, giving you the flexibility to connect and manage different services according to your specific needs.

Moreover, the API is designed to be highly scalable, accommodating the growing demands of your business without compromising on security or performance. With its robust security features, the Service Networking API ensures that your data remains safe from unauthorized access, while also providing detailed monitoring and logging capabilities to help you keep track of network activity.

**Getting Started with Service Networking API**

To get started with the Service Networking API, you need to enable the API in your Google Cloud project and configure your network settings. This involves setting up VPC Network Peering, allocating IP address ranges, and establishing the necessary firewall rules. Google Cloud provides comprehensive documentation and tutorials to guide you through the setup process, making it easy for even beginners to leverage the powerful capabilities of the Service Networking API.

Once your network is configured, you can start connecting your Google Cloud services to your private network, allowing you to build a more secure and efficient cloud environment. Whether you’re looking to optimize your existing infrastructure or expand into new areas, the Service Networking API can help you achieve your goals with ease and confidence.
Service Networking API


Cloud-Native Investigation Lab

Microservice Network Segmentation

Trace application traffic across a cloud-native service network and identify where segmentation should prevent unrestricted lateral movement.

Learning Objective
Trace traffic from the public edge to internal services, identify the trust boundaries, and determine whether a suspicious service-to-service connection should be allowed.
Service Network Topology Select a node
Public Edge
Application Services
Protected Data
Policy Boundary
◉
Internet
External user
◇
API Gateway
Edge control
□
Web
Frontend service
△
API
Application service
▣
Database
Protected data
◆
Worker
Internal workload
Click a service to inspect its trust boundary. Then select a traffic path from the investigation panel.
Traffic Investigation 0 / 3
Request Paths
Internet → Gateway → Web
Expected public application entry path.
Web → API → Database
Expected internal application path to protected data.
Worker → Database
Investigate whether this direct connection should be permitted.
Investigation Actions
[system] Segmentation investigation ready.
[system] Select a traffic path to begin.
Engineering Takeaway
Cloud-native segmentation should follow application identity and service relationships rather than assuming that everything inside the network is trusted.
A secure service network creates explicit boundaries between workloads. A compromised service should not automatically gain unrestricted access to neighbouring services or protected data.

Cloud-native meaning

Understanding the Fundamentals

To comprehend the concept of Cloud Native, we must first grasp its underlying principles. At its core, Cloud Native refers to the design and development of applications specifically built to thrive in cloud environments. It emphasizes containerization, microservices, and orchestration tools like Kubernetes. This approach enables applications to be highly scalable, resilient, and portable, paving the way for efficient utilization of cloud resources.

1. Achieving Agility and Flexibility: One of the critical advantages of adopting a Cloud Native approach is the ability to achieve unparalleled agility and flexibility. Organizations can iterate, deploy, and scale each component separately without disrupting the system by decoupling applications into smaller, independent microservices. This empowers development teams to rapidly respond to changing business needs, roll out new features, and experiment with innovative ideas, fostering a culture of continuous innovation.

2. Scalability and Resilience at its Core: Cloud Native architecture embraces scalability and resilience. By leveraging containerization, applications can seamlessly scale up or down, depending on demand, enabling organizations to handle spikes in traffic or sudden surges in workload efficiently. Moreover, the system can automatically recover from failures using automated orchestration tools like Kubernetes, ensuring high availability and minimizing downtime.

3. Embracing DevOps and Collaboration: The Cloud Native philosophy aligns perfectly with the principles of DevOps, fostering collaboration and improving the overall efficiency of software development and operations. By breaking down monolithic applications into microservices, development and operations teams can work independently on different components, accelerating the release cycle and enabling faster iterations. This collaborative approach enhances communication, reduces bottlenecks, and delivers high-quality, reliable software.

4. Security and Governance Considerations: While the benefits of Cloud Native are substantial, it is crucial to address security and governance aspects. With components distributed across various containers and services, organizations must adopt robust security practices and implement proper access controls. Additionally, monitoring and observability tools become essential to gain insights into the system’s behavior and ensure compliance with industry regulations.

The Role of Cloud Computing

Cloud computing is feasible only because of the technologies that enable resource virtualization. Multiple virtual endpoints share a physical network. Still, different virtual endpoints belong to various customers, and the communication between these endpoints also needs to be isolated. In other words, the network is a resource, too, and network virtualization is the technology that enables sharing a standard physical network infrastructure.

Cloud Native Meaning: Network Segmentation

Firstly, they rely on traditional network constructs such as firewalls and routers to enforce authentication. If traffic wants to get from one I.P. segment to another I.P. segment, it passes through a layer 4 to layer 7 rule set filter; then, those endpoints should be allowed to talk to each other.

However, network segmentation is a bit too coarse-grained compared to what is happening at the application layer. The application layer is going through significant transformational changes. The changes to network security represent the application less than the application should be described.

API gateways, web application firewalls (WAFs), and next-gen firewalls are all secondary to protecting microservices. They are just the first layer of defense. Every API call is HTTP/HTTPS, so what good is a firewall anyway?

Traditional Security Mechanism

We have new technologies that are being protected by traditional means. The conventional security mechanism based on I.P. and 5-tuple can’t work in a cloud-native microservice architecture, especially when there are lateral movements. Layer 4 is coupled with the network topology and lacks the flexibility to support agile applications.

These traditional devices must follow the microservice workload, source/destination IP address, and source/destination port number around the cloud, or else things will be practical. This is a design phase that will not happen. You need to bring security to the microservice, not vice versa.

Traditional security mechanisms are evaporating. The perimeter has changed and is now at the API layer. Every API presents a new attack surface, which results in a gap. A gap must be filled, and only a few companies do this. There are too few, and we need more. 

Outdated: Tokens and Keys

The other thing is the continued use of Tokens and Keys. They are hard-coded strings that serve as a proxy for who you are. The problem is that the management of these items is complex. For example, rotating and revoking them is challenging. This is compounded by the fact that we must presume that the I.T. organization infrastructure will become more horizontally scaled and dynamic.

We can all agree that we will arbitrarily see these things spin up and down with the introduction of technologies such as containers and serverless because it’s more cost-effective than building and supporting tightly coupled monolithic applications. So, the design pattern of enterprise I.T. is moving forward, making the authentication problem more difficult. So we need to bring life a new initiative. We need a core and identity construct that supports the design pattern when building for the future. 

Cloud-native meaning with a new identity-based mechanism

We need companies to recognize that a new identity-based mechanism is required. We have had the identity for human-centric authentication for decades. There are hundreds of companies built to do this. However, the scale of identity management of internal infrastructure is an order of magnitude more significant than it was with humans.

That means existing technology constructs and technologies such as Active Directory need to be more scalable and built for this scale. This is where the opportunity arises – building architectures that match this scale.

Another thing that comes to mind when you look at these authentication frameworks when you think about identity and cryptography is that it’s a bit of a black box, especially for the newer organizations that don’t have the capacity and DNA to think about infrastructure at that layer.

The organization is interested in a product that allows them to translate internal policies that are no longer in the internal data center but in the cloud. We need a way to carry out the mappings to the middleware public cloud using identity as the core service. When everything has an atomic identity, it can also be used for other purposes. For example, you can use it to chain identities together and better debug and trace, to name a few.

Closing Points – Cloud Native Meaning

At the heart of cloud-native are several core principles that guide its implementation. These include microservices architecture, containers, and continuous integration/continuous deployment (CI/CD) pipelines. Microservices allow developers to break down applications into smaller, independent services that can be developed, deployed, and scaled independently. Containers, such as those orchestrated by Kubernetes, provide a portable and efficient environment for these microservices. Meanwhile, CI/CD pipelines automate the process of building, testing, and deploying code, ensuring that updates can be delivered quickly and reliably.

Adopting a cloud-native strategy offers numerous benefits to organizations. Firstly, it enhances scalability, allowing businesses to handle increased loads by simply deploying additional instances of microservices as needed. This flexibility is particularly beneficial during peak usage times. Secondly, it improves resilience; with applications spread across multiple cloud environments, the failure of one component doesn’t necessarily lead to a complete system shutdown. Lastly, the cloud-native approach fosters innovation by enabling developers to experiment and iterate rapidly, without being bogged down by monolithic codebases.

Despite its advantages, transitioning to cloud-native is not without challenges. Organizations must consider the complexity of managing numerous microservices and ensuring they communicate effectively. Additionally, security becomes a top priority, as the distributed nature of cloud-native applications can increase the risk of vulnerabilities. Companies must also be prepared to invest in training and upskilling their teams to effectively leverage cloud-native technologies.

Cloud-Native Security Investigation

Identity, API Calls & Trust

Investigate a cloud-native API request by following its identity, token, behaviour and policy decision. Determine when a trusted workload should lose access.

Learning Objective
Use identity and application context to investigate an API request, recognise a change in trust, and apply an appropriate security response.
API Security Event Stream Monitoring
Current Request
service-web → /api/customer → service-api
10:42:01
API request received
service-web requests customer data from service-api.
Normal
10:42:02
Workload identity verified
Workload identity matches the registered service identity.
Valid
10:42:03
Token inspected
Token is valid but the request context has changed.
Review
10:42:04
Behaviour anomaly detected
Request volume and data access pattern differ from the normal service profile.
Risk
10:42:05
Policy decision required
Identity remains valid, but contextual trust has decreased.
Action
Identity & Trust Analysis Trusted
Request Context
Identity
service-web
API
/api/customer
Token
Valid
Behaviour
Expected
Adaptive Trust 76%
[system] Identity security investigation ready.
[system] Monitor the event stream and investigate the trust change.
Engineering Takeaway
A valid identity does not automatically make every request trustworthy. Cloud-native security can continuously evaluate identity, API context and workload behaviour.
In dynamic infrastructure, trust should be continuously evaluated. Tokens and credentials identify workloads, but policy can still change when behaviour, context or risk changes.
Matt Conran
Latest posts by Matt Conran (see all)

Comments are closed.