Removing State from Network Functions

Removing State From Network Functions

In recent years, the networking industry has witnessed a significant shift towards stateless network functions. This revolutionary approach has transformed the way networks are designed, managed, and operated. In this blog post, we will explore the concept of removing state from network functions and delve into the benefits it brings to the table.

State in network functions refers to the information that needs to be stored and maintained for each connection or flow passing through the network. Traditionally, network functions such as firewalls, load balancers, and intrusion detection systems heavily relied on maintaining state. This stateful approach introduced complexities and limitations in terms of scalability, performance, and fault tolerance.

Stateless network functions, on the other hand, operate without the need for maintaining connection-specific information. Instead, they process packets or flows independently, solely based on the information present in each packet. This paradigm shift eliminates the burden of state management, enabling networks to scale more efficiently, achieve higher performance, and exhibit enhanced resiliency.

Enhanced Scalability: By removing state from network functions, networks become inherently more scalable. Stateless functions allow for easier distribution and parallel processing, empowering networks to handle increasing traffic demands without being limited by state management overhead.

Improved Performance: Stateless network functions offer improved performance compared to their stateful counterparts. Without the need to constantly maintain state information, these functions can process packets or flows more quickly, resulting in reduced latency and improved overall network performance.

Enhanced Fault Tolerance: Stateless network functions facilitate fault tolerance by enabling easy redundancy and failover mechanisms. Since there is no state to be replicated or synchronized, redundant instances can seamlessly take over in case of failures, ensuring uninterrupted network services.

The removal of state from network functions has revolutionized the networking landscape. Stateless network functions bring enhanced scalability, improved performance, and enhanced fault tolerance to networks, enabling them to meet the ever-increasing demands of modern applications and services. Embracing this paradigm shift paves the way for more agile, efficient, and resilient networks that can keep up with the rapid pace of digital transformation.

NETWORK FUNCTIONS • STATE MANAGEMENT

Stateful vs Stateless Network Function Lab

See how connection state changes the way a network function processes traffic, scales across instances and handles subsequent packets in the same flow.

Scenario: A client sends a TCP connection through a network function. Compare what happens when the function maintains per-flow state locally versus when processing is designed so that instances do not depend on locally stored connection state.
Traffic Scenario
Processing Architecture
Local State
REQUIRED
Instance Dependency
HIGH
CLIENT Packet / Flow
→
NF INSTANCE Local processing
→
SERVER Application
State Model
State Element Stateful Function Stateless Processing Model
Flow Context Stored with processing instance Not required locally
Packet Decision May depend on connection state Based on packet/flow attributes and available policy
Instance Failure State may need recovery or synchronisation Another instance can process traffic if required state is externally available
Scale Out May require state distribution or affinity Processing instances can be more independently replicated
Packet Processing Console
[LAB] Stateful processing selected.
[FLOW] Waiting for packet processing test.
[STATE] Connection-specific state is associated with the processing instance.
Engineering Takeaway

Stateless does not mean that the overall system contains no state. It means the processing instance does not need to own the connection-specific state required to handle every packet. State can instead be externalised or represented in other system components, allowing processing instances to be replaced or replicated more independently.

Highlights: Removing State From Network Functions

**Understanding State in Network Functions**

To grasp the significance of stateless network functions, it’s essential to first understand what “state” means in this context. State refers to the stored information that a network function requires to operate effectively. This includes data about past interactions, user sessions, and configuration settings. While stateful functions can offer certain advantages, such as maintaining session continuity, they also introduce complexity and potential bottlenecks.

**The Benefits of Stateless Network Functions**

1. **Scalability**: Stateless network functions can easily scale horizontally. Without the need to store and manage state information, these functions can be replicated across multiple instances, distributing the load and improving performance.

2. **Resilience**: Stateless functions are inherently more resilient to failures. In a stateless architecture, if one instance fails, another can seamlessly take over without the risk of data loss or service interruption.

3. **Simplicity**: By removing the need to manage state, developers can focus on building simpler, more maintainable code. This reduction in complexity often leads to faster development cycles and easier debugging processes.

**Implementing Statelessness in Network Functions**

Transitioning to stateless network functions involves rethinking how data is handled. One approach is to offload state management to external storage systems or databases. By doing so, network functions can remain lightweight and focused solely on processing data. Additionally, modern technologies such as microservices and containerization can support the implementation of stateless architectures, allowing for more efficient resource utilization.

**Real-World Applications and Case Studies**

Many leading tech companies have successfully adopted stateless network functions to enhance their operations. For instance, cloud service providers have embraced stateless architectures to offer scalable and reliable services to their customers. These real-world applications demonstrate the practicality and effectiveness of removing state from network functions, providing valuable insights for organizations considering a similar transition.

Understanding Stateful Network Functions

Stateful network functions have been the backbone of traditional networking architectures. These functions, such as firewalls, load balancers, and NAT (Network Address Translation), maintain complex state information about the connections passing through them. While they have served us well, stateful network functions have inherent limitations. They introduce latency, create single points of failure, and hinder scalability, especially in modern distributed systems.

Enter stateless network functions, a paradigm shift that aims to address the shortcomings of their stateful counterparts. Stateless network functions operate without maintaining connection-specific states, treating each packet independently. By decoupling the state from the functions, networks become more agile, scalable, and fault-tolerant. This approach aligns perfectly with the demands of cloud-native architectures, microservices, and modern software-defined networking (SDN) frameworks.

Considerations: Stateless Network Functions

Enhanced Scalability: One key benefit of removing the state from network functions is its improved scalability. By eliminating the need for state management and storage, network systems can handle significantly more concurrent connections. This enables seamless scaling to accommodate growing demands without compromising performance or stability.

Improved Flexibility and Interoperability: When the state is removed from network functions, it allows for greater flexibility and interoperability among different systems and platforms. Stateless network functions can be easily deployed across various environments, making integrating new technologies and adapting to evolving requirements easier. This promotes innovation and paves the way for developing advanced network solutions.

Enhanced Security: Stateless network functions also offer enhanced security benefits. With no state to maintain, the risk of data breaches and unauthorized access is significantly reduced. Stateless systems can operate in a zero-trust environment, where each transaction is treated independently and authentically. This approach minimizes the potential impact of security breaches and strengthens overall network resilience.

Simplified Management and Maintenance: Removing the state from network functions significantly reduces the complexity of managing and maintaining these systems. Stateless architectures require less administrative overhead, as there is no need to track and manage state information across different network nodes. This simplification leads to cost savings and allows network administrators to focus on other critical tasks.

The Role of Non-Proprietary Hardware

We have seen a significant technological evolution, where network functions can run in software on non-proprietary commodity hardware, whether in a grey box or white box deployment model. However, taking network functions from a physical appliance and putting them into a virtual appliance is only half the battle.

The move to software provides network security components’ on-demand elasticity and scale and quick recovery from failures. However, one major factor still hinders us—the state that each network function needs to process.

The Tights Coupling of State

We still face challenges created by the tight coupling of the state and processing for each network function, be it virtual firewalls, load balancer scaling, intrusion protection system (IPS), or even distributed firewalls closer to the workloads for dynamic workload scaling use cases. The state is tightly coupled with the network functions, limiting the network functions’ agility, scalability, and failure recovery.

Compounded by this, we have seen an increase in network complexity. The rise of the public cloud and the emergence of hybrid and multi-cloud has made data center connectivity more complicated and critical than ever.


NETWORK FUNCTIONS • INCIDENT INVESTIGATION

State Scaling & Failure Investigation Lab

Investigate what happens when a stateful network function fails, scales out, or receives return traffic through a different instance. Your task is to identify the state dependency behind the failure.

Scenario: A client has an active connection through a network function. Traffic is now affected by an instance failure, asymmetric routing, or a scale-out event.
Inject Investigation Event
CLIENT Existing TCP flow
→
NF A Flow state: ACTIVE
→
NF B Flow state: UNKNOWN
Investigation Status
Current Event
NF INSTANCE FAILURE
Primary Dependency
LOCAL CONNECTION STATE
Likely Impact
STATE LOOKUP FAILURE
Select the Evidence
Incident Console
[LAB] Investigation initialized.
[FLOW] Existing connection detected.
[STATE] NF A owns the active connection context.
[ACTION] Select an event and inspect the evidence.
Engineering Takeaway

Stateful processing can make failure recovery and horizontal scaling harder because connection-specific state may remain tied to one instance. Active-active designs can synchronise state, but synchronisation itself introduces complexity, consistency and availability considerations.

Removing State From Network Functions

Virtualization

Virtualization (which generally indicates server virtualization when used as a standalone phrase) refers to the abstraction of the application and operating system from the hardware. Similarly, network virtualization is the abstraction of the network endpoints from the physical arrangement of the network. In other words, network virtualization permits you to group or arrange endpoints on a network independent from their physical location.

Network Virtualization refers to forming logical groupings of endpoints on a network. In this case, the endpoints are abstracted from their physical locations so that VMs (and other assets) can look, behave, and be managed as if they are all on the same physical segment of the network.

Importance of Network Functions:

Network functions are the backbone of modern communication systems, making them essential for businesses, organizations, and individuals. They provide the necessary infrastructure to connect devices, transmit data, and facilitate the exchange of information reliably and securely. Without network functions, our digital interactions, such as accessing websites, making online payments, or conducting video conferences, would be nearly impossible.

Types of Network Functions:

1. Routing: Routing functions enable forwarding data packets between different networks, ensuring that information reaches its intended destination. This process involves selecting the most efficient path for data transmission based on network congestion, bandwidth availability, and network topology.

2. Switching: Switching functions allow data packets to be forwarded within a local network, connecting devices within the same network segment. Switches efficiently direct packets to their intended destination, minimizing latency and optimizing network performance.

3. Firewalls: Firewalls act as barriers between internal and external networks, protecting against unauthorized access and potential security threats. They monitor incoming and outgoing traffic, filtering and blocking suspicious or malicious data packets.

4. Load Balancing: Load balancing distributes network traffic across multiple servers to prevent overloading and ensure optimal resource utilization. Load balancing enhances network performance, scalability, and reliability by evenly distributing workloads.

5. Network Address Translation (NAT): NAT allows multiple devices within a private network to share a single public IP address. It translates private IP addresses into public ones, enabling communication with external networks while maintaining the security and privacy of internal devices.

6. Intrusion Detection Systems (IDS): IDS monitors network traffic for any signs of intrusion or malicious activity. They analyze data packets, identify potential threats, and generate alerts or take preventive actions to safeguard the network from unauthorized access or attacks.
**What is State**

Before we delve into potential solutions to this problem, mainly by introducing stateless network functions, let us first describe the different types of states. We have two: dynamic and static. The network function processes continuously update the dynamic state, which could be anything from a firewall’s connection information to the load balancer’s server mappings.

On the other hand, the static state could include something like pre-configured firewall rules or the IPS signature database. The dynamic state must persist across instance failures and be available to the network functions when scaling in or out. On the other hand, the static state is accessible and can be replicated to a network instance upon boot time.

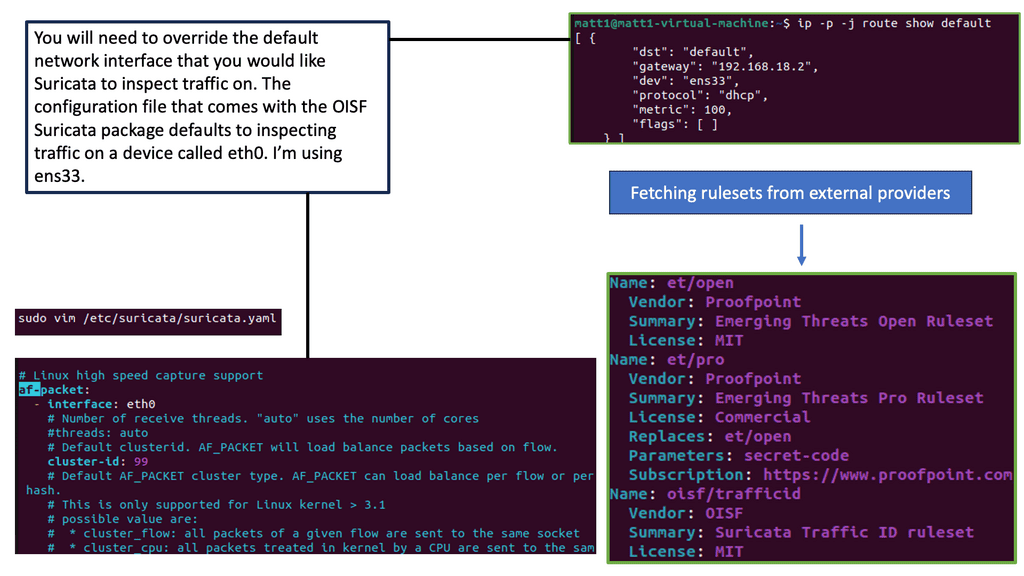
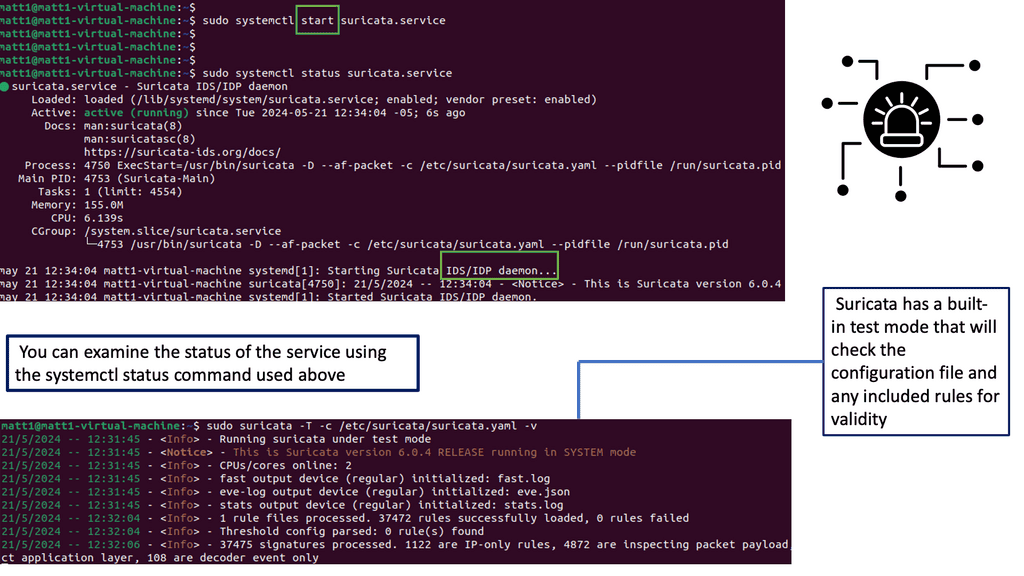
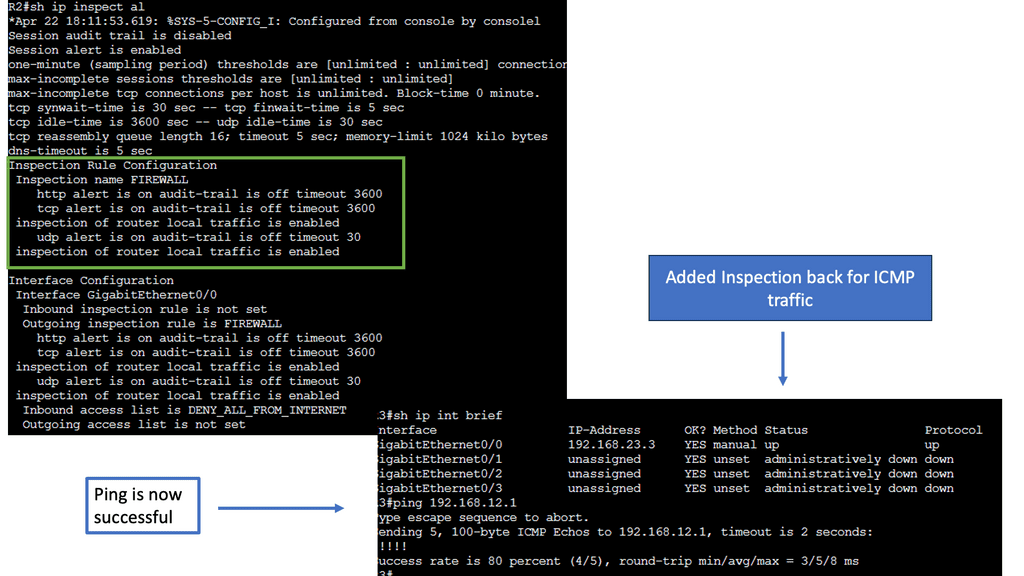
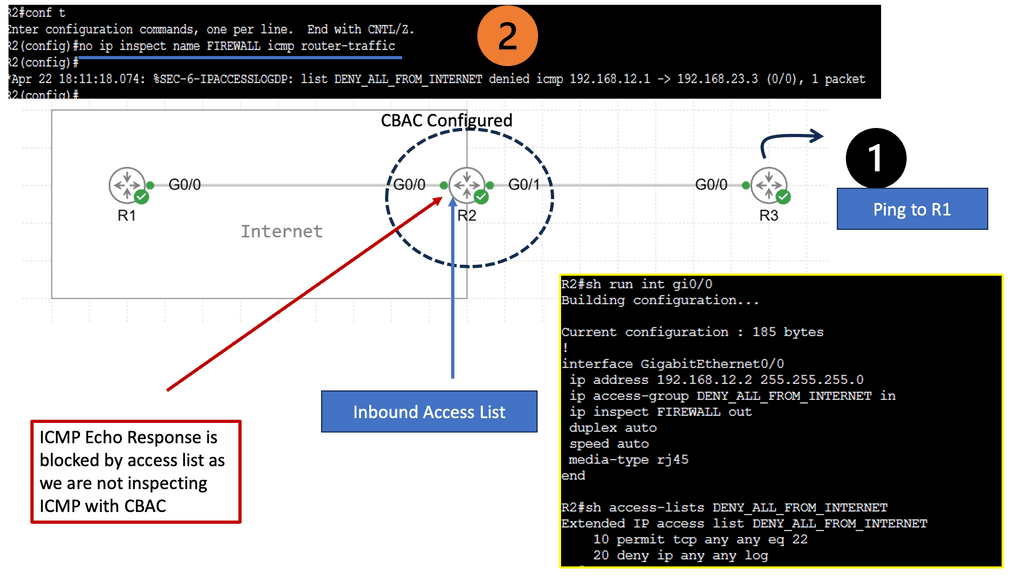
Example Stateful Technology: Cisco CBAC Stateful Firewall

**How CBAC Works: Stateful Inspection Explained**

At its core, CBAC functions as a stateful firewall, which means it monitors the state of active connections and makes decisions based on the context of the traffic. Unlike stateless firewalls that merely assess packet headers, CBAC inspects the entire traffic stream, understanding and remembering the state of connections. This enables it to effectively block unauthorized access while allowing legitimate traffic to flow smoothly. By maintaining a state table, CBAC can dynamically filter packets based on the context of the communication session, providing a more nuanced and effective security measure.
CBAC Firewall CBAC Firewall

**Stateless Network Functions**

Stateless Network Functions are a new and disruptive technology that decouples the design of network functions into a stateless process component and a data store layer. An orchestration layer that can monitor the network function instances for load and failure and adjust the number of cases accordingly is also needed.

Taking or decoupling the state from a network function enables a more elastic and resilient infrastructure. So how does this work? From a 20,000 bird’s eye view, the network functions become stateless. The statefulness of the application, such as a stateful firewall, is maintained by storing the state in a separate data store. The data store provides the resilience of the state. No state is stored on the individual networking functions themselves.

Datastore Example:

The data store can be, for example, RAMCloud. RAMCloud is a distributed key-value storage system with high-speed storage for large-scale applications. It is designed for many servers needing low-latency access to a durable data store. RAMCloud is suitable for low-latency access as it’s based primarily on DRAM.  RAMCloud keeps all data in DRAM. As a result, the network functions can read RAMCloud objects remotely over the network in as little as 5μs.

**Stateless network functions advantages**

Stateless network functions may not be helpful for all, but they are valid for standard network functions that can be redesigned statelessly. Stateful network functions are helpful for a stateful firewall, intrusion prevention system, network address translator, and load balancer. Removing the state and placing it in a database brings many advantages to network management.

As the state is accessed via a data store, a new instance can be launched, and traffic is immediately directed to it, offering elasticity. Secondly, resilience, a new instance, can be spawned instantaneously upon failure.  Finally, as any instance can handle an individual packet, packets traversing different paths do not have asymmetric and multi-path routing issues.

Problems with having state: Failure

The majority of network designs have redundancy built-in. It sounds easy when one data center fails to let the secondary take over. When the data center interconnect (DCI) is configured correctly, everything should work upon failover, correct?

Let’s not forget about one little thing called state with a firewall in each data center design. The network address translation (NAT) in the primary data center stores the mapping for two flows, let’s call them F1 and F2. Upon failure, the second firewall in the other data center takes over, and traffic is directed to the new firewall. However, any packets from flows F1 and F2 will not enter the second firewall.

This will result in a failed lookup; existing connections will timeout, causing application failure.  Asymmetric routing causes problems. If a firewall has an established state for a client-to-server connection (SYN packet), if the return SYN-ACK passes through a different firewall, the packet will result in a failed lookup and get dropped.

Some have tried to design distributed active-active firewalls to solve layer three issues and asymmetrical traffic flow over the stateful firewalls. The solution looks perfect. Configure both wide area network (WAN) routers to advertise the same IP prefix to the outside world.

This will attract inbound traffic and pass it through the nearest firewall—nice and easy. The active-active firewalls would exchange flow information, solving the asymmetrical flow problems. Distributed active-active firewall state across each data center is better in PowerPoint than in real life.

Problems with having the state: Scaling

The tight coupling of the state can also cause problems with the scaling of network functions. Scaling out NAT functions will have the same effect as NAT box failure. Packets from flow originating from a different firewall directed to a new instance will result in a failed lookup.

Network functions form the foundation of modern communication systems, enabling us to connect, share, and collaborate in a digitized world. Network functions ensure smooth and secure data flow across networks by performing vital tasks such as routing, switching, firewalls, load balancing, NAT, and IDS. Understanding the significance of these functions is crucial for businesses and individuals to harness the full potential of the interconnected world we live in today.

Example Technology: Browser Caching

Understanding Browser Caching

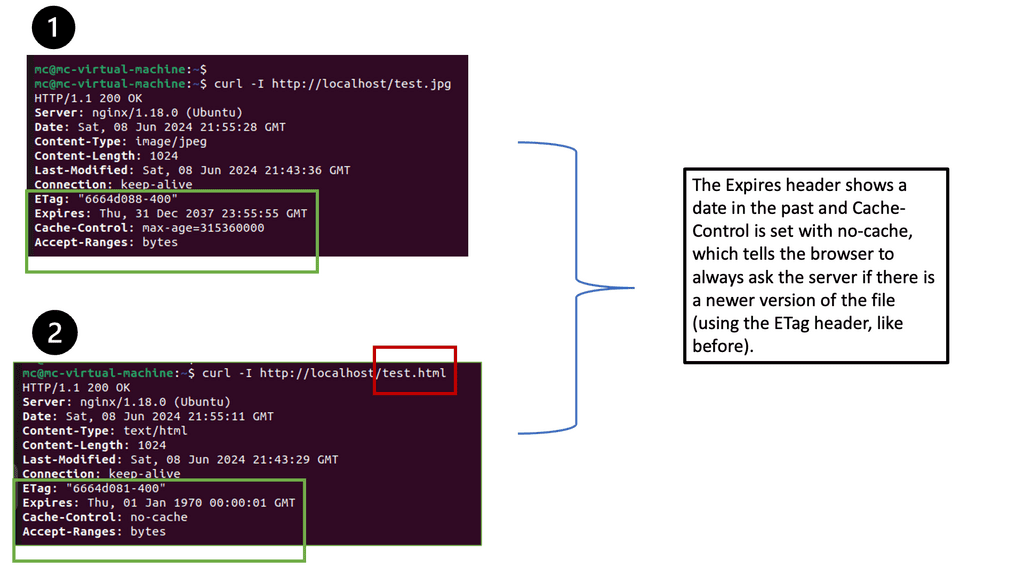
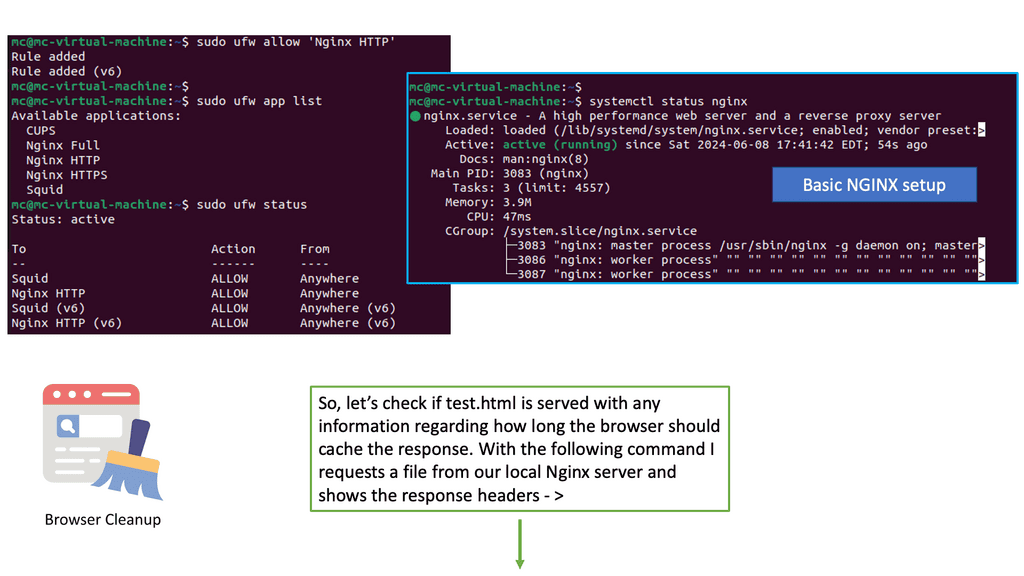
Browser caching is a mechanism that allows web browsers to store static resources, such as images, CSS files, and JavaScript, locally on a user’s device. When a user revisits a website, the browser can retrieve these cached resources instead of downloading them again from the server. This results in faster page load times and reduced server load.

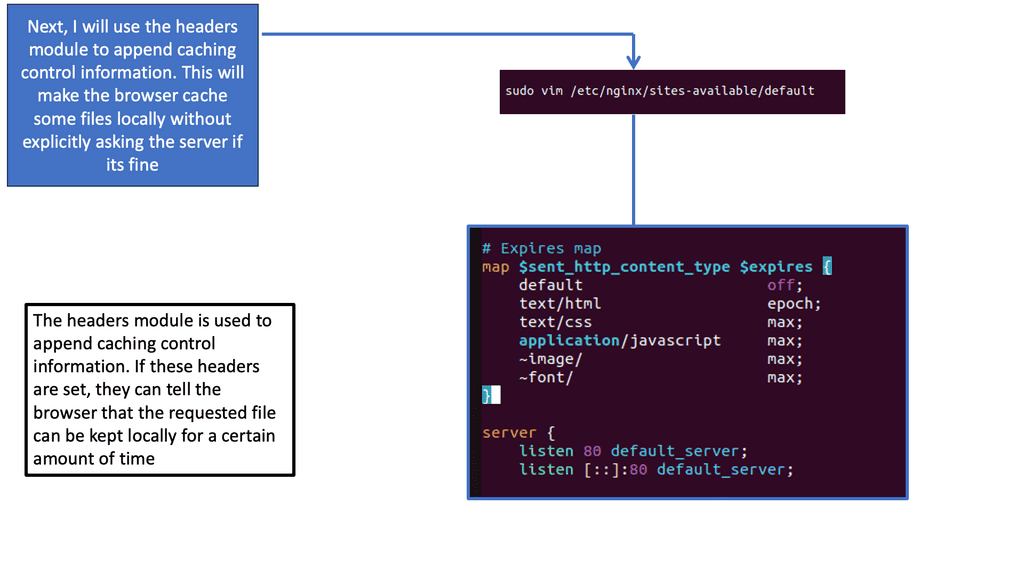
Nginx, a popular open-source web server, provides a powerful module called ‘header’ that enables fine-grained control over HTTP response headers. With this module, you can easily configure browser caching directives to instruct clients on how long to cache specific resources. By leveraging the ‘expires’ and ‘Cache-Control’ headers, you can set expiration times for different file types, ensuring optimal caching behavior.
NETWORK FUNCTIONS • CLOUD-NATIVE ARCHITECTURE

Stateless Network Function Architecture Lab

Move connection-specific state away from individual processing instances and observe how the architecture can scale and recover more independently.

Scenario: Build a processing tier where multiple network function instances can handle traffic while shared dynamic state is maintained outside the individual processing instances.
Decoupled Processing Architecture
TRAFFIC Packets / flows
→
NF INSTANCES 4 processing instances
→
STATE STORE Shared dynamic state
→
ORCHESTRATOR Scale / recover / place
NF-01 ACTIVE
NF-02 ACTIVE
NF-03 ACTIVE
NF-04 ACTIVE
Processing Dependency
LOW
State Availability
SHARED
Recovery Model
REPLACE INSTANCE
Architecture Console
[LAB] Stateless architecture initialized.
[STATE] Dynamic state is external to the processing instances.
[SCALE] Processing tier can be replicated independently.
[READY] Select an event and run the architecture test.
Engineering Takeaway

The goal is not to eliminate state from the system. The goal is to decouple packet or flow processing from state that would otherwise be tightly bound to one network function instance. Externalising state can improve elasticity and recovery, but it also introduces datastore latency, availability, consistency and failure considerations.

network server room with computers for digital tv ip communications and internet

Stateless Network Functions

Stateless Network Functions

In the ever-evolving world of networking, the concept of stateless network functions has emerged as a game-changer. This revolutionary approach to network architecture is transforming the way we design, deploy, and manage networks. In this blog post, we will delve into the intricacies of stateless network functions and explore their profound impact on the networking landscape.

Stateless network functions (SNFs) are a paradigm shift from traditional network architectures. Unlike their stateful counterparts, SNFs do not store session-specific information, making them highly scalable and agile. These functions process packets independently, without relying on the state of previous packets, enabling faster processing and reduced latency.

Enhanced Scalability: By eliminating the need to maintain session state, SNFs can handle a significantly larger number of concurrent sessions. This scalability is crucial in modern network environments where the number of connected devices and data traffic is growing exponentially.

Flexibility and Modularity: Stateless network functions promote flexibility and modularity in network design. Each function can be developed, deployed, and updated independently, allowing network operators to adapt to changing requirements quickly. This modular approach also fosters innovation and encourages the development of specialized network functions.

Improved Fault Tolerance: With SNFs, network failures and disruptions can be contained more effectively. Since stateless functions do not rely on session-specific information, failures in one function do not impact the entire network. This fault-tolerant characteristic ensures more resilient and reliable network operations.

Software-Defined Networking (SDN): Stateless network functions play a pivotal role in SDN deployments. By decoupling control and data planes, SDN architectures can leverage the agility and scalability of SNFs. This enables efficient traffic management, dynamic resource allocation, and rapid network provisioning.

Network Function Virtualization (NFV): In the realm of NFV, stateless network functions are instrumental in achieving network virtualization and service chaining. By encapsulating network functions in virtualized environments, SNFs enable on-demand scaling, improved resource utilization, and simplified network management.

Stateless network functions are revolutionizing network architecture by offering enhanced scalability, flexibility, and fault tolerance. With their applicability in SDN, NFV, and beyond, SNFs are driving the transformation of the networking landscape. As we embrace this paradigm shift, we can expect more agile, scalable, and efficient networks that can meet the demands of the digital age.

NETWORK FUNCTIONS • ARCHITECTURE DECISION

Stateless Network Function Decision Lab

Determine whether a network function is a good candidate for stateless processing. The objective is not to remove all state, but to identify which state is required for packet processing and where that state can safely live.

Scenario: You are designing a cloud-scale network service. Select a network function, inspect its state requirements, and decide whether its processing can be separated from connection-specific state.
Network Function Under Review
Architecture Assessment
Stateless Fit
HIGH
State Dependency
LOW
PACKET Input traffic
→
PROCESSING Independent evaluation
→
DECISION Policy / attributes
Where Does the State Live?
DYNAMIC STATE Connection/session information
STATIC STATE / POLICY Configuration, rules or signatures
Architecture Decision Console
[LAB] Network function assessment ready.
[MODEL] Select a network function and traffic model.
[OBJECTIVE] Determine whether packet processing can be decoupled from session-specific state.
Engineering Takeaway

A stateless network function does not mean that the overall architecture contains no state. The design objective is to separate packet processing from tightly coupled dynamic state wherever practical. Functions such as routing or some forms of inspection may be good candidates, while NAT and stateful firewalling normally require connection-specific information somewhere in the system.

Highlights: Stateless Network Functions

**The Basics: What Does Stateless Mean?**

To grasp the significance of stateless network functions, it’s essential to understand what “stateless” entails. In a stateless system, each request from a client is treated independently, without relying on stored information from previous interactions. This approach contrasts with stateful systems, where previous interactions influence current actions. Statelessness enhances network efficiency by reducing dependencies, allowing for seamless scaling and improved fault tolerance.

**Benefits of Stateless Network Functions**

One of the primary advantages of stateless network functions is their scalability. Since each request is independent, adding more resources to handle increased load is straightforward. This flexibility is vital for networks experiencing unpredictable traffic patterns. Additionally, statelessness enhances fault tolerance. In the event of a failure, the system can easily reroute requests without worrying about lost state information, ensuring consistent service availability.

**Challenges in Implementing Stateless Network Functions**

While the benefits are clear, transitioning to stateless network functions presents challenges. One significant hurdle is the need for efficient data storage solutions to handle the information typically maintained by stateful systems. Developers must also address security concerns, as stateless systems can be more vulnerable to malicious attacks if not properly secured. Despite these challenges, the potential for improved performance makes the effort worthwhile.

Understanding Stateless Network Functions

Stateless network functions, also known as SNFs, represent a paradigm shift in network architecture. Unlike their traditional counterparts, which rely on maintaining and managing session states, SNFs operate independently, without knowledge of prior interactions. This statelessness increases scalability, flexibility, and simplicity in network design.

The adoption of stateless network functions brings forth an array of advantages. Firstly, SNFs reduce complexity and enhance overall system performance by eliminating the need for session state management. Additionally, the statelessness enables horizontal scalability, empowering networks to handle an ever-increasing number of requests without compromising efficiency. Moreover, SNFs facilitate faster network deployment, as their independence from the session state eliminates the need for complex configurations.

Use Cases and Applications:

A- Stateless network functions find applications across various domains. In cloud computing, SNFs enable efficient load balancing and dynamic resource allocation. They also prove invaluable in network security, as their statelessness mitigates the risk of session-based attacks. Furthermore, SNFs are leveraged in content delivery networks (CDNs) to optimize content routing and improve user experience.

B- While stateless network functions offer immense potential, specific challenges must be addressed. One such concern is the loss of session-related information, which might be crucial in particular scenarios. Additionally, transitioning from traditional architectures to stateless paradigms requires careful planning and potential modifications to existing infrastructure.

Benefits of Stateless Network Functions:

1. Enhanced Scalability: SNFs offer improved scalability by eliminating the need to store session state information. Network devices can handle more packets and perform better, making them ideal for large-scale deployments and high-traffic scenarios.

2. Simplified Network Management: Stateless network functions simplify network management by reducing the complexity associated with session state maintenance. This streamlined approach allows for more straightforward configuration, troubleshooting, and monitoring, improving operational efficiency.

3. Increased Flexibility: SNFs enable more flexible network architectures that can be easily deployed and scaled without session state limitations. This flexibility allows organizations to rapidly adapt their networks to changing demands and deploy new services.

4. Enhanced Security: Stateless processing enhances network security by reducing potential attack vectors. Since SNFs do not rely on session state information, they minimize the risk of session hijacking or data leakage, leading to more robust and secure networks.

Applications of Stateless Network Functions:

1. Load Balancing: Stateless network functions are well-suited for load-balancing applications. They enable efficient network traffic distribution across multiple servers or resources, ensuring optimal resource utilization and improved application performance.

2. Deep Packet Inspection: SNFs can be used for deep packet inspection (DPI), a technique that analyzes the content of network packets for security or application identification purposes. The stateless nature of SNFs allows for faster and more efficient DPI, enabling real-time threat detection and network optimization.

3. Network Function Virtualization (NFV): Stateless network functions are foundational to network function virtualization (NFV) architectures. By decoupling network functions from dedicated hardware, NFV leverages SNFs to achieve greater flexibility, scalability, and cost-effectiveness in network deployments.

**Tight State and Processing**

New technology is needed, and it’s time to break the tight state and processing. This involves decoupling the existing network function design into a stateless processing component ( stateless network functions) and a data store layer. Doing this and breaking the tight coupling enables a more elastic and resilient network functions infrastructure.


NETWORK FUNCTIONS • STATE DECOUPLING

State Decoupling & Performance Investigation Lab

A stateless processing tier can improve elasticity and failure isolation, but moving state outside the network function introduces its own engineering trade-offs. Investigate latency, consistency, availability and recovery before choosing an architecture.

Incident: A network service is being scaled across multiple processing instances. Engineers have externalised connection state, but packet processing is now dependent on a shared state service. Determine whether the architecture remains viable.
State Location
Event
Consistency
Processing Architecture
TRAFFIC Packets / flows
→
STATELESS PROCESSING Any healthy instance can process traffic
→
STATE Shared state service
Scale-Out
HIGH
Failure Recovery
HIGH
State Dependency
EXTERNAL
Main Risk
LATENCY
Evidence
Processing Instance NF-01 can process the packet without owning the session state.
State Availability Required state is available from the shared state layer.
Scaling Impact A new processing instance can join without inheriting local session state.
Architecture Risk The external state service becomes a dependency.
Investigation Console
[LAB] State-decoupling investigation ready.
[MODEL] External distributed state selected.
[OBJECTIVE] Determine whether the architecture improves scale and recovery without introducing unacceptable dependencies.
Engineering Takeaway

Externalising state can make processing instances easier to scale, replace and recover. It does not make the architecture dependency-free. The state service introduces latency, availability, consistency and failure-domain considerations that must be engineered explicitly.

Stateless Network Functions

The Role of Networks

Let’s face it. Networks need to be both scalable and sophisticated. To be successful, you need to completely redesign the network functions, such as routing and firewall functions, along with the underlying platforms that manage and orchestrate these functions. However, to accomplish this, you need to create an entirely new architecture and adapt the existing technology to this new architecture.

If you look at technologies used for cloud storage, no one has ever used them for networks. Why is this? The reason is mainly down to performance requirements, such as throughput and latency in distributed systems.

One can understand that the industry will be very pushy with this type of disruptive technology, saying that it is just impossible. But we need to give the world something new. It deserves the ability to customize networks on-demand. It would help to have a logical place to start with a new architecture.

Stateless Network Functions: Changing the environment

Decentralized workloads, the decline of on-premise, and the increase in multi-cloud deployments have created one of the most extensive connectivity challenges for data centers. A key finding is that colocation providers, traditionally serving as space, power, and physical network connectivity resources, should not become the hub for all traffic as workloads decentralize.

The problem is these colocation providers have not focused on connectivity that requires multi-tenancy and routing, and they usually have physical cloud connects; this has introduced growing management and operational challenges, which will only increase in large-scale deployments.

Cloud Connect is where you need to connect multiple enterprises, where these enterprises need to connect to various cloud providers. All of these tenants need BGP routing, firewall functions, and NAT, but to do this on a larger scale with a solution that couples the state cannot scale and be reliable.

New technologies come in waves – some appear, and others disappear.

The market needs a new type of technology, a software-defined interconnect like the Internet exchange. This came to light in 2016 when Laurent Vanbever proposed a software-defined internet exchange based on OpenFlow ( what is OpenFlow ) known as SDX; software-defined internet exchange is an SDN solution originating from the combined efforts of Princeton and UC Berkeley. It aims to address IXP pain points by deploying additional SDN controllers and OpenFlow-enabled switches. It doesn’t try to replace the entire classical IXP architecture with something new; rather, it augments existing designs with a controller.

Software-defined interconnect (SDIX)

However, a software-defined interconnect (SDIX) is a new category of offering that allows colocation providers to manage their cloud connects via software and extend their connectivity control. It should cover the cloud connection and multiple data center interconnects. In the past, the colocation providers focused on space and power. However, in today’s world, they have new responsibilities. The responsibilities now extend to new types of connectivity for customers. Customers now have new requirements.

They must move their data from one colocation facility to another to avoid latency or backup purposes. For these cases, colocation providers need a new type of platform to direct all of their different tenant’s tasks and requirements to a software-based platform.

The Tight Coupling

Why is this different? The underlying technology concerns network functions such as firewalls, routers, and load balancers; regardless of the application architecture and requirements, these network functions are physical boxes. The challenge is that traffic that flows through these boxes is tightly coupled with the box.

The physical box, virtual machine, or container performing a network function is coupled with the state. What happens with the state when you launch a new network function or redirect the traffic to a backup device? This will affect the application. This might be acceptable for a single application but not for a large-scale deployment when you have millions of connections and applications running on top of network functions.

Network Function Virtualizaton

Network function virtualization (NFV) and NFV use cases didn’t help here. All it did was change the physical boxes to virtual ones. It’s like changing a physical appliance in Dublin to a cloud-based provider. Is this the future? NFV inherits the same design and features as the physical box. But what needs to be done is realizing that the problem is the state. You need to decouple the dynamic state from each network function and put them in a high-performance data store within a cluster of commodity hardware and switches—a hardware-agnostic solution with code that is not open source.

Network function stateless

Then, you can make the network function stateless, so it’s physically just a thread. It doesn’t affect application performance if it fails, as the state is collected from the data store. This is needed as an underlying design, but does it seem possible? There will be overheads from decoupling the state.

The state can be put into a cluster of servers. Some servers maintain some of the state, and some of the other servers can be the network functions. The state is not physically in another data center or location. Every type of dynamic state, such as counters, timers, and handshaking that you see in the TCP flow, all of which is state, is a challenge to decouple without breaking application performance. However, this can be done by adapting technology-distributed systems—a database to store the state needed that is designed for high-performance computing. A read for a state should be around 5 microseconds.  

An algorithm is needed to read and write the state in a way that reads multiple packets simultaneously. This enables you to overcome any latency issues and achieve better performance than traditional appliances that have the state coupled.

Stateless network functions are revolutionizing networking infrastructure by offering enhanced scalability, simplified management, increased flexibility, and improved security. SNFs are paving the way for more agile and efficient networks with their wide range of applications. As organizations embrace digital transformation, understanding and harnessing the potential of stateless network functions will be vital to building resilient and future-proof network architectures.

NETWORK FUNCTIONS • SDIX • CLOUD CONNECTIVITY

Software-Defined Interconnect Architecture Lab

Bring stateless network functions, multi-tenant connectivity, orchestration and cloud interconnection together. Design a service that can steer traffic across locations while keeping processing components independently scalable.

Scenario: A tenant needs connectivity between two data centres and a cloud environment. The service must dynamically steer traffic through network functions such as firewalling, NAT or inspection while allowing processing capacity to scale independently.
Deployment Model
Service Chain
Traffic Event
Software-Defined Interconnect
TENANT / SITE A Enterprise workload
→
SERVICE CHAIN Firewall → Router
→
CLOUD / SITE B Application workload
Connectivity
READY
Processing
ELASTIC
Orchestration
ACTIVE
Main Dependency
POLICY
Connectivity Layer
UNDERLAY / INTERCONNECT Provides reachability between sites, clouds and service insertion points.
CONNECTIVITY
TRAFFIC STEERING Selects the appropriate service path for the tenant.
STEERING
Service Layer
NETWORK FUNCTIONS Processing functions can be deployed as independently scalable components.
PROCESSING
ORCHESTRATION Applies tenant intent, service policy and placement decisions.
CONTROL
Investigation Evidence
Tenant Connectivity Tenant traffic has an available service path.
Service Processing Processing instances can be added without redesigning the interconnect.
Orchestration Policy determines where traffic is steered.
Failure Domain A processing instance can fail without necessarily removing the underlying connectivity.
Architecture Event Console
[LAB] Software-defined interconnect ready.
[MODEL] Multi-data-centre + cloud selected.
[SERVICE] Firewall → Router
[CONTROL] Orchestration is active.
[READY] Run an architecture event and investigate the resulting traffic path.
Engineering Takeaway

A software-defined interconnect can coordinate connectivity, traffic steering and service insertion across data centres and cloud environments. Stateless processing can make individual network-function tiers easier to scale, but the complete system still depends on routing, policy, orchestration, service-state requirements and the availability of the underlying connectivity.