OpenDaylight Integration: OpenStack SDN Controller
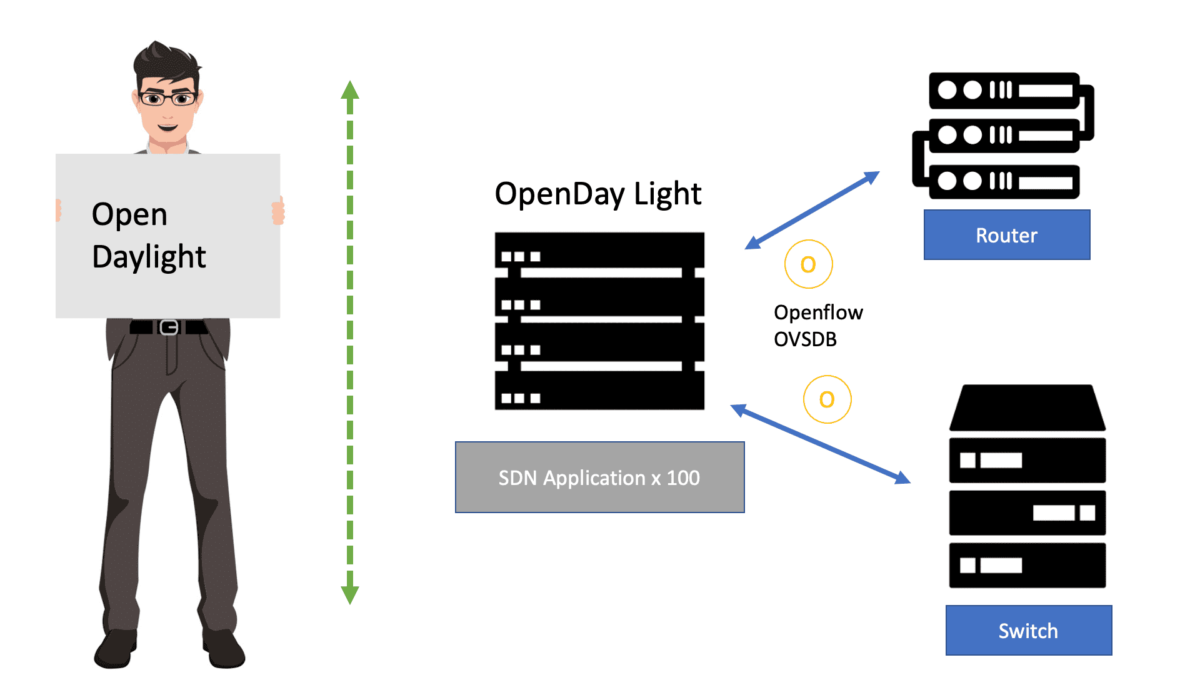
The single API is used to configure heterogeneous hardware. OpenDaylight integrates tightly with the OpenStack SDN controller, providing the central controller element for many open-source clouds. It was born shortly after Neutron, and the two projects married as soon as the ML2 plugin was available in Neutron. OpenDaylight is not intended to replace the Neutron Networks but adds and provides better functionality and network management. OpenDaylight Beryllium offers a Base, Virtualized, and Service Provider edition.
OpenDaylight (ODL) understands the network at a high level, running multiple applications on top of managing network objects. It consists of a Northbound interface, Middle tier, and Southbound interface. The northbound interface offers the network’s abstraction. It exposes interfaces to those writing applications to the controller, and it’s here that you make requests with high-level instructions.
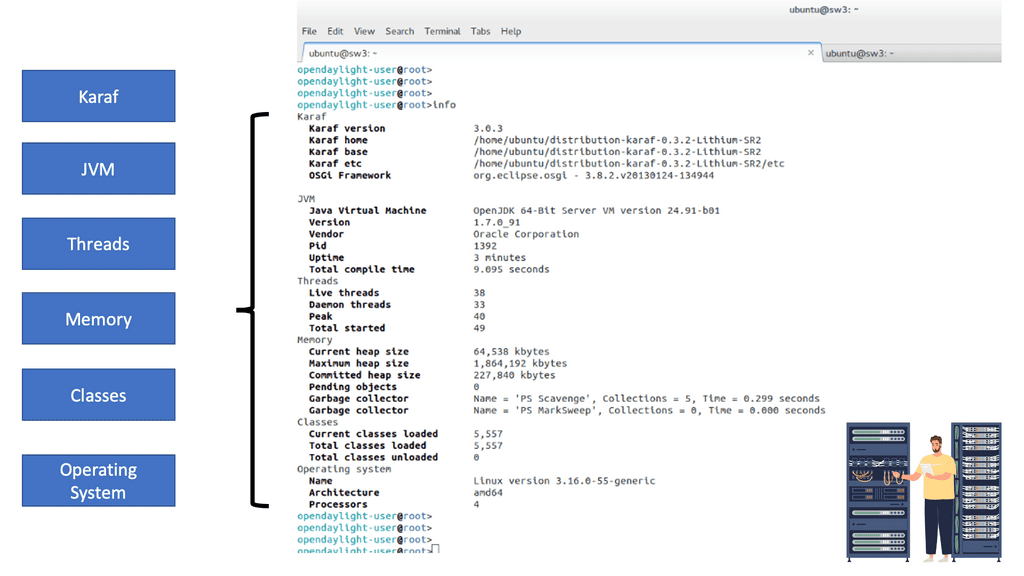
The middle tier interprets and compiles the request, enabling the southbound interface to action the network. The type of southbound protocol is irrelevant to the northbound API. It’s wholly abstracted and could be OpenFlow, OVSDB, or BGP-LS. The following screen displays generic information for the OpenDaylight Lithium release.
**Key Features and Capabilities**
1. OpenDaylight Controller: At the core of OpenDaylight is its controller, which acts as the brain of the network. The controller provides a centralized network view, enabling administrators to manage resources, define network policies, and dynamically adapt to changing network conditions.
2. Northbound and Southbound Interfaces: OpenDaylight offers northbound and southbound interfaces that facilitate communication between the controller and network devices. The northbound interface enables applications and services to interact with the controller, while the southbound interface allows the controller to communicate with network devices, such as switches and routers.
3. Modular Architecture: OpenDaylight’s modular architecture provides flexibility and extensibility. It allows developers to add or remove modules based on specific network requirements, ensuring the platform remains lightweight and adaptable to various network environments.
4. Comprehensive Set of Protocols: OpenDaylight supports various industry-standard protocols, including OpenFlow, NETCONF, and BGP. This compatibility ensures seamless integration with existing network infrastructure, making adopting OpenDaylight in diverse network environments easier.
**Benefits of OpenDaylight**
1. Network Automation: OpenDaylight simplifies network management by automating repetitive tasks like provisioning and configuration. This automation significantly reduces the time and effort required to manage complex networks, allowing network engineers to focus on more strategic initiatives.
2. Enhanced Network Visibility: With its centralized control and management capabilities, OpenDaylight provides real-time visibility into network performance and traffic patterns. This visibility allows administrators to promptly identify and troubleshoot network issues, improving reliability and performance.
3. Scalability and Flexibility: OpenDaylight’s modular architecture and support for industry-standard protocols enable seamless scalability and flexibility. Network administrators can quickly scale their networks to accommodate growing demands and integrate new technologies without disrupting existing infrastructure.
4. Innovation and Collaboration: Being an open-source platform, OpenDaylight encourages collaboration and innovation within the networking community. Developers can contribute to the project, share ideas, and leverage their collective expertise to build cutting-edge solutions that address evolving network challenges.
Complications with Neutron Network
Initially, OpenStack networking was built into Nova ( nova-network ) and offered little network flexibility. It was rigid and significant if you only wanted a flat Layer 2 network. Flat networks are fine for small designs with single application environments, but anything at scale will reach CAM table limits. VLANs also have theoretical hard stops.
Nova networking was represented as a second-class citizen in the compute stack. Even OpenStack Neutron Security Groups were dragged to another device and not implemented at a hypervisor level. This was later resolved by putting IPtables in the hypervisor, but we still needed to be on the same layer 2 domain.
Limitation of Nova networking
Nova networking represented limited network functionality and did not allow tenants to have advanced control over network topologies. There was no load balancing, firewalling, or support for multi-tenancy with VXLAN. These were some pretty big blocking points.
Suppose you had application-specific requirements, such as a vendor-specific firewall or load balancer, and you wanted OpenStack to be the cloud management platform. In that case, you couldn’t do this with Nova. OpenStack Neutron solves all these challenges with its decoupled Layer 3 model.
A key point: Networking with Neutron
Networking with Neutron offers better network functionality. It provides an API allowing the interaction of network constructs ( router, ports, and networks ), enabling advanced network functionality with features such as DVR, VLXAN, Lbass, and FWass.
It is pluggable, enabling integration with proprietary and open-source vendors. Neutron offers more power and choices for OpenStack networking, but it’s just a tenant-facing cloud API. It does not provide a complete network management experience or SDN controller capability.
The Neutron networking model
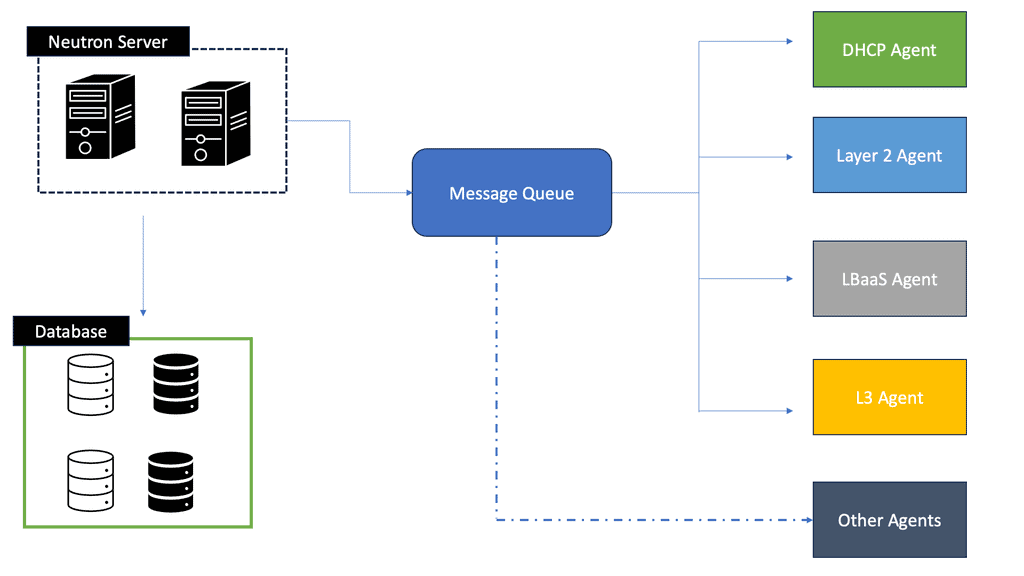
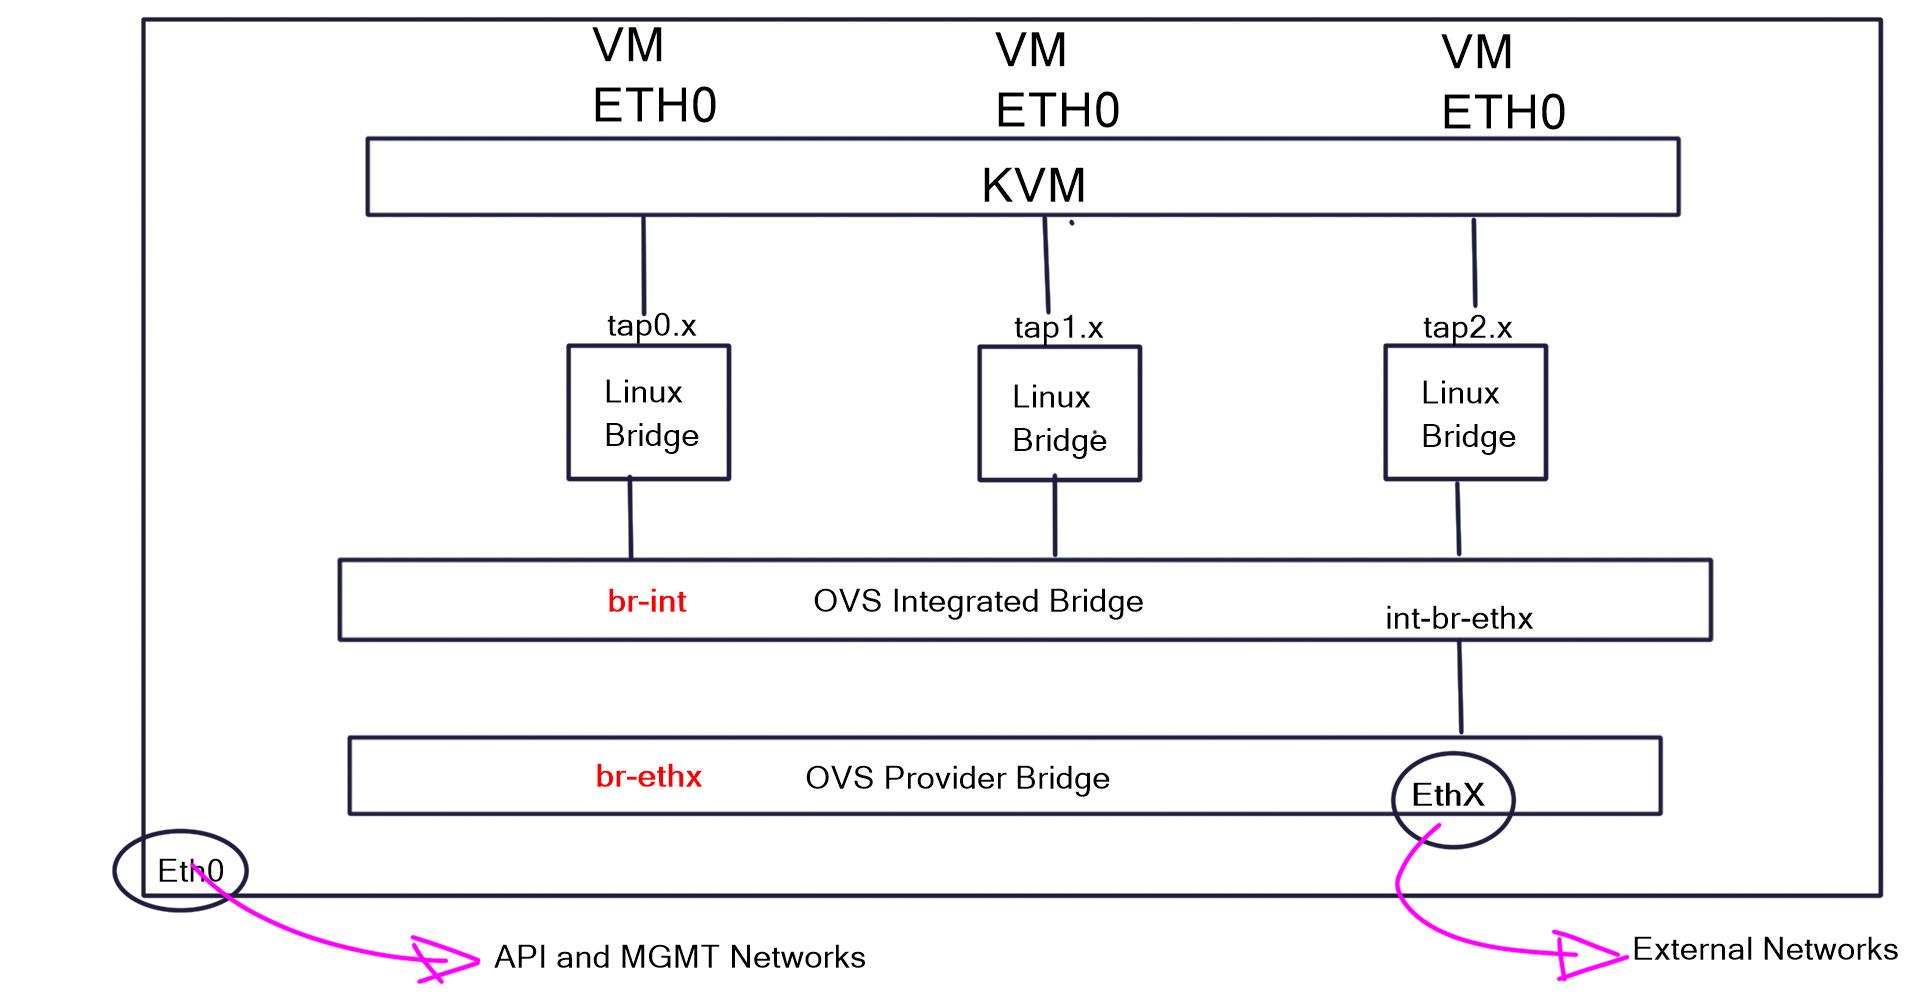
The Neutron networking model consists of several agents and databases. The neutron server receives API calls and sends the message to the Message Queue to reach one of the agents. Agents on each compute node are local, actioning, and managing the flow table. They are the ones that carry out the orders.
The Neutron server receives a response from the agents and records the new network state in the database. Everything connects to the integration bridge ( br-int ), where traffic is tagged with VLAN ID and handed off to the other bridges, such as br-tun, for tunneling traffic.
Each network/router uses a Linux namespace for isolation and overlapping IP addresses. The complex architecture comprises many agents on all compute, network, and controller nodes. It has scaling and robustness issues you will only notice when your system goes down.
Neutron is not an API for managing your network. If something is not working, you need to check many components individually. There is no specific way to look at the network in its entirety. This would be the job of an OpenDaylight SDN controller or an OpenStack SDN controller.
OpenDaylight Project Components
OpenDaylight is used in conjunction with Neutron. It represents the controller that sits on top and offers abstraction to the user. It bridges the gap between the user’s instructions and the actions on the compute nodes, providing the layer that handles all the complexities. The Neutron doesn’t go away and works together with the controller.
Neutron gets an ODL driver installed that communicates with a Northbound interface that sits on the controller. The MD-SAL (inventory YANG model) in the controller acts as the heart and communicates to both the controller OpenFlow and OVSDB components.
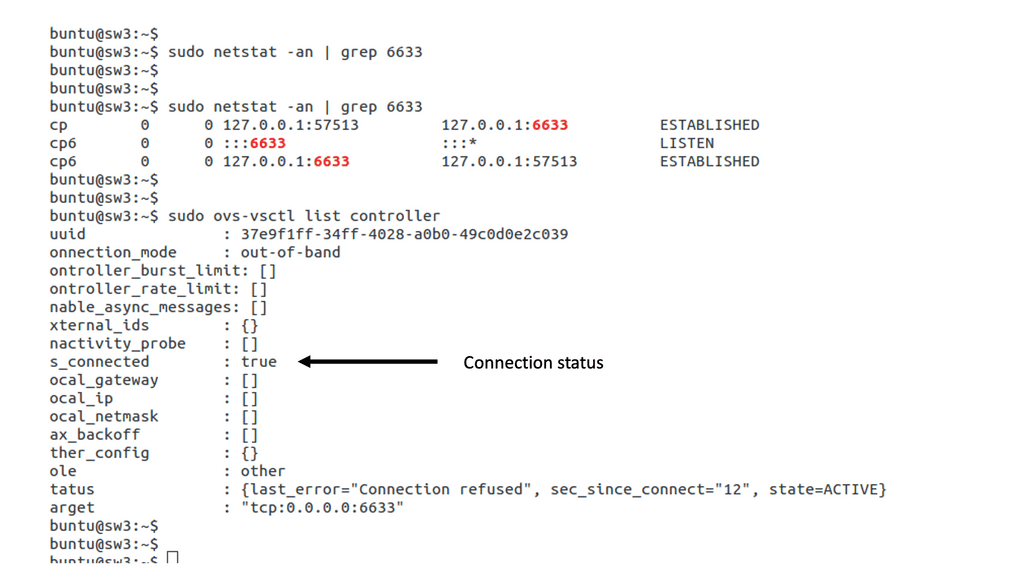
OpenFlow and OVSDB are the southbound protocols that configure and program local compute nodes. The OpenDaylight OVSDB project is the network virtualization project for OpenStack. The following displays OpenvSwtich connection to OpenDaylight. Notice the connection status is “true.” For this setup, the controller and switch are on the same node.
The role of OpenvSwitch
OpenvSwitch is viewed as the workhorse forOpenDaylight. It is programmable and offers advanced features such as NetFlow, sFlow, IPFIX, and mirroring. It has extensive flow matching capabilities – Layer 1 ( QoS priority, Tunnel ID), Layer 2 ( MAC, VLAN ID, Ethernet type), Layer 3 (IPv4/v6 fields, ARP), Layer 4 ( TCP/UDP, ICMP, ND) with many chains of action such as output to port, discard and packet modification. The two main userspace components are the ovsdb-server and the ovs-vswitchd.
The ODL OVSDB manager interacts with the ovsdb-server, and the ODL OpenFlow controller interacts with the ovs-vswitchd process. The OVSDB southbound plugin plugs into the ovsdb-server. All the configuration of OpenvSwitch is done with OVSDB, and all the flow adding/removing is done with OpenFlow.
OpenDaylight OpenFlow forwarding
OpenStack traditional Layer 2 and Layer 3 agents use Linux namespaces. The entire separation functionality is based on namespaces. OpenDaylight doesn’t use namespaces; you only have a namespace for the DHCP agent. It also does not have a router or operate with a network stack—the following displays flow entries for br0. OpenFlow ver1.3 is in use.
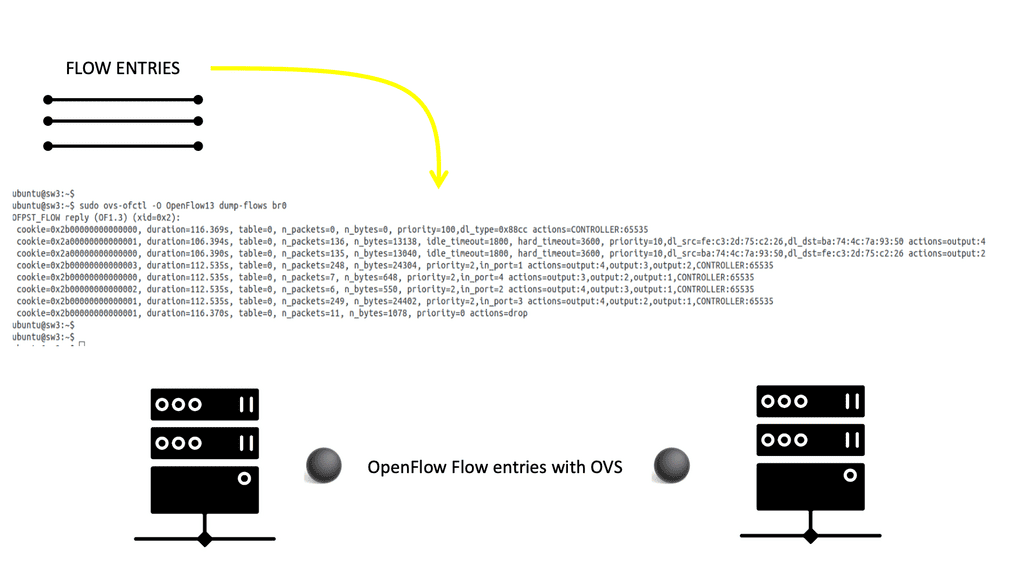
OpenFlow rules are implemented to do the same job as a router. For example, MAC is changing or TTL decrementation. ODL can be used to manipulate packets, and the Service Function Chain (SFC) feature is available for advanced forwarding. Then, you can use service function chaining with service classifier and service path for path manipulation.
OpenDaylight service chaining has several components. The job of the Service Function Forwarder (SFF) is to get the flow to the service appliance; this can be accomplished with a Network Service Header (NSH) or using some tunnel with GRE or VXLAN.
Closing Points on OpenDaylight
OpenDaylight is a collaborative open-source project hosted by the Linux Foundation. Its primary goal is to facilitate progress and innovation in SDN and NFV, making networks more adaptable and scalable. As a software platform, it provides a controller that allows for centralized management of network resources, which is essential for handling the complexities of modern networks.
One of the standout features of OpenDaylight is its modular architecture. This flexibility allows developers to tailor the platform to their specific needs, integrating various modules to expand its capabilities. Additionally, OpenDaylight supports a wide range of networking protocols, making it a versatile choice for diverse network environments.
The benefits of using OpenDaylight are numerous. It offers enhanced network automation, which reduces the need for manual configuration and minimizes human error. Furthermore, its open-source nature means continuous development and community support, ensuring the platform remains on the cutting edge of network technology.
OpenDaylight is being adopted across industries for its ability to simplify network management and optimize performance. Telecommunications companies, for instance, utilize OpenDaylight to manage large-scale networks efficiently. Enterprises benefit from its automation capabilities, which streamline operations and reduce costs. Additionally, OpenDaylight’s adaptability makes it ideal for research institutions exploring new networking paradigms.
For those interested in exploring OpenDaylight, the journey begins with understanding its architecture and components. The OpenDaylight project provides extensive documentation and community support to help newcomers navigate the platform. Setting up a test environment is an excellent way to experiment with its features and understand its potential impact on your network management strategy.