
Data Center Security — Engineering Guide
Modern data centers are no longer simple collections of physical servers connected to a small number of network segments.
They host business-critical applications, databases, APIs, virtual machines, containers, distributed platforms, cloud-connected services, and increasingly dynamic workloads.
As application architectures have become more distributed, the security model has had to evolve with them.
Traditional security architectures often relied heavily on perimeter firewalls, VLANs, IP addressing, and manually maintained access-control lists. These mechanisms remain important, but they are no longer sufficient by themselves.
Modern applications generate large amounts of east-west traffic between workloads inside the data center.
A web application may communicate with application services.
Application services may communicate with databases.
Microservices may communicate with dozens of other services.
Containers may appear and disappear dynamically.
Cloud workloads may communicate with on-premises infrastructure.
Management, monitoring, backup, identity, and security systems create additional communication relationships.
The result is a highly interconnected environment in which the traditional concept of a single security perimeter becomes increasingly difficult to apply.
From Network Security to Workload Security
Modern data center security therefore needs to answer a different question.
Instead of asking:
Which network is this server connected to?
we increasingly need to ask:
Which workload is this, what does it need to communicate with, and why?
This is the foundation of application-centric security.
Security policy can be associated with applications, workloads, identities, relationships, and risk rather than being permanently tied to physical network locations.
Cisco Application Centric Infrastructure (ACI) provides one example of this approach.
ACI allows application requirements to become part of the network policy model. Endpoint groups, contracts, filters, micro-segmentation, and Layer 4–Layer 7 service integration can be used to express and enforce communication relationships across the fabric.
Security as a Layered Architecture
Modern data center security should not be treated as a single technology.
It is better understood as a series of complementary layers:
Security architecture
↓
Segmentation
↓
Policy
↓
Enforcement
↓
Deep inspection
↓
Telemetry
↓
Detection
↓
Response
Each layer addresses a different problem.
Physical and infrastructure controls protect the underlying environment.
Segmentation reduces the size of security boundaries.
Policy defines authorised relationships.
Distributed enforcement prevents unauthorised communication.
Firewalls and other Layer 4–Layer 7 services provide deeper inspection.
Telemetry provides visibility into what is actually happening.
Analytics identify abnormal behaviour.
Response mechanisms allow compromised workloads to be contained.
The Data Center Security Engineering Model
This guide develops that model across four sections.
Section 1 — Security Architecture
Examines the different security layers that protect modern data centers, including physical, network, compute, storage, application, cloud, identity, observability, and resilience controls.
Section 2 — Segmentation and Policy
Explores how security requirements become enforceable communication relationships using concepts such as EPGs, ESGs, contracts, filters, and micro-segmentation.
Section 3 — Enforcement and L4–L7 Services
Examines how authorised and unauthorised traffic is enforced within the fabric and how deeper inspection can be integrated through firewalls, IPS, load balancers, service graphs, and policy-based redirect.
Section 4 — Visibility, Detection and Adaptive Defence
Moves beyond preventative controls into telemetry, behavioural analysis, security analytics, incident investigation, risk-based enforcement, containment, and adaptive security.
The Core Principle
The objective is not simply to prevent every possible connection.
The objective is to create an environment where:
Required communication is explicitly permitted, unnecessary communication is restricted, abnormal behaviour is visible, and compromised workloads can be contained before they become a larger incident.
That is the foundation of a modern, policy-driven data center security architecture.
Engineering Guide Structure
1. Security Architecture
Understand the layers that protect the modern data center.
2. Segmentation and Policy
Define which workloads should communicate and under what conditions.
3. Enforcement and L4–L7 Services
Enforce those relationships and introduce deeper inspection where required.
4. Visibility, Detection and Adaptive Defence
Observe the environment, identify abnormal behaviour, investigate incidents, and respond to changing risk.
The Complete Security Loop
Understand → Segment → Enforce → Inspect → Observe → Detect → Respond
Data Center Security Architecture
From Segmentation to Adaptive Defense
Use the four engineering sections below to move from security foundations and policy design through distributed enforcement, visibility, incident response and adaptive defense.
Data Center Security Techniques covering physical, network, compute, storage, application, cloud, identity and Zero Trust security controls.
EPGs, contracts, filters, micro-segmentation, cloud security boundaries and workload relationships used to define permitted communication.
ACI EPGs, contracts, micro-segmentation, service graphs and L4–L7 security inspection used to enforce and inspect application traffic.
Visibility, telemetry, behavioural detection, incident response, containment, recovery and continuous security validation.
Data center security is not a single firewall, ACL or security product. It is a layered engineering model spanning physical infrastructure, network segmentation, workloads, applications, identity, telemetry and incident response.
How modern data center security combines segmentation, least privilege, identity, workload protection, observability and resilience rather than relying on a single perimeter control.
The objective is to make every communication path intentional, observable and enforceable — from physical infrastructure through application workloads.
1. Data Center Security Architecture
Data center security is not a single control or appliance.
A modern data center requires multiple security layers working together to protect physical infrastructure, networks, workloads, applications, data, identities, and operational processes.
The objective is to prevent unauthorised access, reduce the attack surface, detect abnormal behaviour, limit lateral movement, and maintain resilience when security controls fail or an incident occurs.
A useful way to approach data center security is to consider the environment as a series of interconnected security domains.
1.1 The Security Layers
A modern data center can include:
Physical security
Network security
Segmentation
Compute security
Storage security
Application security
Cloud and hybrid security
Identity and access control
Observability
Threat detection
Incident response
Resilience and recovery
These layers should not operate independently.
A compromised workload may generate network traffic.
Network telemetry may identify the behaviour.
Identity telemetry may identify the associated user or service.
Endpoint security may provide additional evidence.
Security analytics can correlate the events.
A response system can then contain the workload.
This is the basis of layered defence.
1.2 Physical Security
The physical environment remains the first security boundary.
Controls can include:
Controlled facility access
Badge authentication
Biometrics
Surveillance
Security personnel
Restricted data center areas
Rack security
Tamper detection
Secure cabling
Environmental monitoring
Physical security is particularly important because compromise of the physical infrastructure can undermine otherwise strong logical controls.
An attacker who gains direct access to infrastructure may be able to bypass network-based assumptions.
1.3 Network Security
The network provides the communication foundation for the data center.
Traditional controls include:
VLAN segmentation
VRF isolation
ACLs
Firewalls
Routing policy
Network security zones
IDS/IPS
VPNs
Encryption
Network telemetry
However, modern applications increasingly require security controls that understand workloads and application relationships rather than only addresses and interfaces.
1.4 East-West Security
Traditional perimeter security focuses heavily on north-south traffic.
Modern data centers also require strong east-west security.
For example:
WEB → APP
APP → DB
APP → CACHE
SERVICE → SERVICE
MONITORING → WORKLOAD
If an attacker compromises one workload, east-west controls determine how easily that attacker can move to other systems.
This makes internal segmentation a fundamental security requirement.
1.5 Compute Security
The compute layer introduces additional security boundaries.
Virtualisation platforms such as:
VMware ESXi
Microsoft Hyper-V
KVM
can provide workload isolation, but the hypervisor itself must also be protected.
Important controls include:
Secure boot
Host hardening
Patch management
Hypervisor security
VM isolation
Privileged-access controls
Host monitoring
Containerised environments introduce additional controls.
These can include:
Container image security
Runtime protection
Namespace isolation
Kubernetes network policy
Workload identity
Runtime behaviour monitoring
The objective is to ensure that compromise of one workload does not automatically provide unrestricted access to others.
1.6 Storage Security
Storage frequently contains the most valuable information in the environment.
Security controls can include:
Encryption at rest
Encryption in transit
Access control
Storage segmentation
Immutable backups
Protected snapshots
Replication
Backup isolation
Recovery testing
Ransomware resilience is particularly important.
A backup that is accessible through the same credentials and security boundaries as production systems may be vulnerable to the same compromise.
Security therefore needs to extend into the recovery architecture.
1.7 Application Security
Applications introduce another security layer.
Controls can include:
Web Application Firewalls
API gateways
Application authentication
Secret management
Secure CI/CD
Dependency scanning
Code security testing
Runtime protection
Application logging
Application security and network security should complement one another.
A secure network cannot compensate for an insecure application, and an application security control cannot replace appropriate network segmentation.
1.8 Cloud and Hybrid Security
Modern data centers increasingly operate across:
On-premises infrastructure
Private cloud
Public cloud
Kubernetes
SaaS
Security policy therefore has to extend beyond the physical data center.
Cloud environments introduce controls such as:
VPC/VNet segmentation
Security groups
Cloud firewalls
IAM
Workload identity
Private connectivity
Cloud logging
Cloud security posture management
Service-to-service policy
The important principle is consistency.
A workload should not become significantly less protected simply because it has moved from an on-premises environment into a cloud environment.
1.9 Zero Trust
Zero Trust changes the assumption that internal network location automatically implies trust.
Instead of:
Internal network = trusted
the model becomes:
Access must be explicitly authorised.
Important principles include:
Least privilege
Explicit authentication
Continuous verification
Identity-aware policy
Device posture
Workload identity
Encryption
Deny-by-default principles
Zero Trust therefore complements segmentation.
Segmentation limits communication.
Identity determines who or what is requesting access.
Risk determines whether the communication should remain trusted.
1.10 Identity-Driven Security
Identity provides context that IP addresses cannot.
A network address tells us where traffic is coming from.
Identity can tell us:
Which user is involved
Which workload is involved
Which service account is involved
Which device is involved
Which application is involved
What privileges are associated with the request
This enables more contextual security decisions.
For example:
User identity
Device posture
Application
Network location
Risk
can produce a much stronger security decision than IP address alone.
1.11 Observability
Security requires visibility.
Important telemetry sources include:
NetFlow
IPFIX
Packet capture
Firewall logs
DNS logs
Authentication logs
Endpoint telemetry
Application logs
Cloud logs
Kubernetes telemetry
Distributed tracing
Tools and platforms can include:
SIEM
SOAR
EDR/XDR
Prometheus
Grafana
OpenTelemetry
The objective is not to collect every possible event.
The objective is to collect enough meaningful evidence to understand:
What happened?
Who or what was involved?
What changed?
What was affected?
What should happen next?
1.12 Incident Response and Resilience
Prevention will never be perfect.
A mature security architecture therefore assumes that incidents will occur and prepares for them.
Important capabilities include:
Incident response plans
Security runbooks
Automated containment
Backup and recovery
Disaster recovery
Tabletop exercises
Recovery testing
Crisis communication
Forensic evidence collection
The architecture should allow security teams to move from:
Detection
to
Investigation
to
Containment
to
Recovery
without requiring the network to be redesigned during the incident.
1.13 Security Analytics
Modern environments generate too many events for manual analysis alone.
Analytics can identify:
Unexpected communication
Lateral movement
Privilege escalation
Abnormal traffic
Unusual authentication
Misconfiguration
Excessive permissions
Unused policy
Shadow workloads
Unexpected exposure
The value comes from correlation.
A single unusual connection may be harmless.
The same connection combined with:
unusual authentication
abnormal process activity
unexpected DNS queries
increased traffic
may become a high-value security signal.
1.14 Adaptive Security
Modern security architectures increasingly need to respond to changing conditions.
For example:
Normal workload
→ normal policy
Suspicious workload
→ increased monitoring
High-risk workload
→ restricted communication
Compromised workload
→ quarantine
This introduces a feedback loop between security telemetry and enforcement.
1.15 Engineering Model
A useful architecture is:
Physical security
↓
Network security
↓
Segmentation
↓
Workload security
↓
Application security
↓
Identity
↓
Observability
↓
Detection
↓
Response
↓
Recovery
No individual layer is sufficient.
The strength of the architecture comes from how these controls work together.
1.16 Section 1 Engineering Principle
The modern data center should therefore be treated as a distributed security system, not simply a collection of network devices.
The architecture must understand:
Where workloads are located
What those workloads represent
Who or what can access them
Which services they require
How they communicate
What normal behaviour looks like
How abnormal behaviour will be detected
How compromised workloads will be contained
This provides the foundation for the next stage:
How do we turn these security requirements into enforceable communication policy?
The workload is the starting point for the security decision. Modern data-center security begins by understanding what is communicating, rather than relying only on its IP address or VLAN.
WEB-01 is making an expected HTTPS request to APP-01. The security architecture evaluates the communication progressively.
Segmentation and Security Policy
Modern data center security increasingly moves beyond the question of which subnet or VLAN a workload occupies. The engineering problem is to define which workloads should communicate, under which conditions, and what happens when that relationship is not permitted.
How EPGs, contracts, filters, security groups, micro-segmentation and cloud security boundaries translate application requirements into enforceable policy.
Good segmentation is not about creating as many zones as possible. It is about creating clear security boundaries with explicit communication relationships that can be understood, tested and maintained.
2. Segmentation and Security Policy
Once the security architecture has been established, the next engineering question is:
Which workloads should be allowed to communicate, and why?
Traditional data center security often relied on VLANs, IP subnets, interfaces and ACLs.
These mechanisms remain useful, but modern applications require a more expressive model.
An application may contain multiple workload types, and those workloads may move across the infrastructure.
Security policy therefore needs to follow the application relationship, rather than simply the physical location of a server.
2.1 From Network Segmentation to Policy Segmentation
Traditional segmentation might look like:
VLAN 10 → Web
VLAN 20 → Application
VLAN 30 → Database
This creates useful boundaries, but it does not automatically define which communication is permitted.
A more complete model is:
WEB
↓
Application policy
↓
APP
↓
Application policy
↓
DB
The important question becomes:
What relationship exists between these workloads?
2.2 Designing Segmentation Around Application Relationships
Consider a three-tier application:
Web
↓
Application
↓
Database
The security policy may require:
Web can communicate with application services
Application can communicate with databases
Web cannot directly access databases
Management systems can access approved administrative interfaces
Monitoring systems can collect telemetry
Backup systems can access protected storage
This is much more precise than simply defining three VLANs.
The security architecture is now based on relationships.
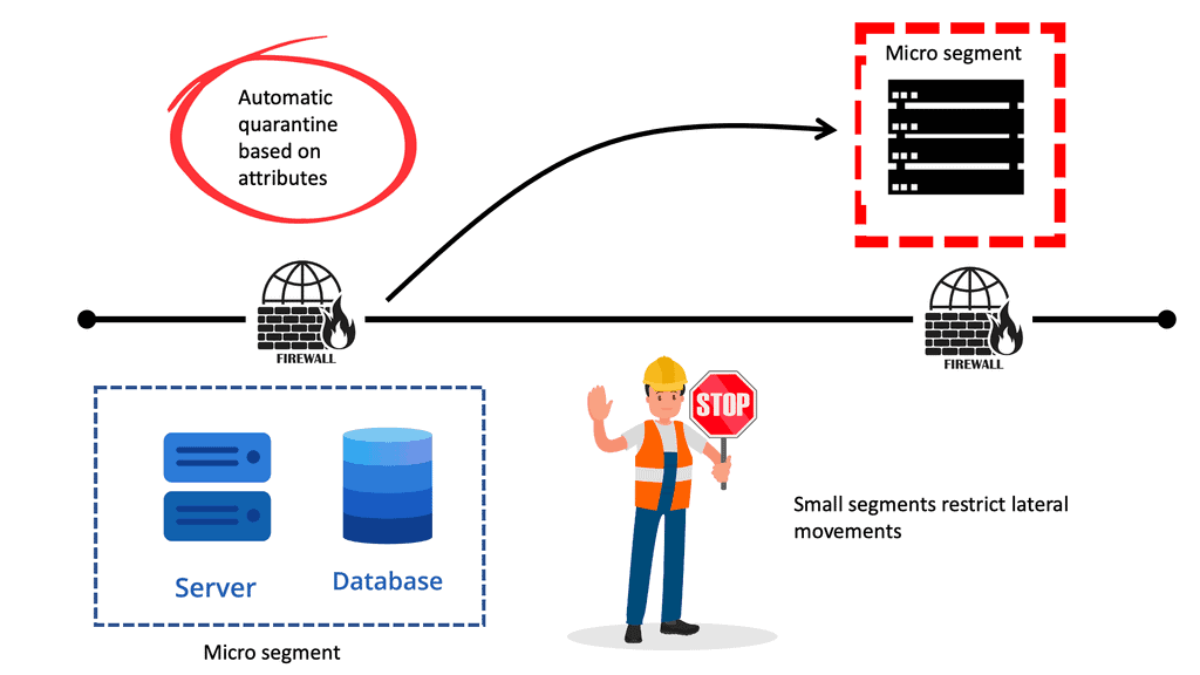
2.3 Micro-Segmentation
Large security zones can create excessive trust.
If hundreds of workloads share the same security boundary, compromise of one workload may provide an attacker with many possible lateral-movement paths.
Micro-segmentation reduces these trust relationships.
Instead of:
Production → Production
we can define:
WEB → APP
APP → DB
MONITORING → WORKLOAD
BACKUP → STORAGE
Each relationship can be independently controlled.
2.4 Policy as the Security Contract
A useful way to think about security policy is as a contract between workloads.
The policy states:
This workload is allowed to communicate with that workload using these services.
For example:
APP → DB
Allowed:
TCP/5432
Not automatically allowed:
SSH
RDP
SMB
Other unnecessary services
This produces a least-privilege communication model.
2.5 Cisco ACI and Policy-Based Segmentation
Cisco ACI provides an application-centric policy framework.
Rather than configuring every security rule independently on physical interfaces, administrators can define groups of endpoints and relationships between those groups.
Important constructs include:
Endpoint Groups
Contracts
Filters
Endpoint Security Groups
Micro-segmentation
L3Out policy
Layer 4–Layer 7 service integration
These constructs allow policy to be represented in terms of applications and workloads.
2.6 Endpoint Groups
An Endpoint Group, or EPG, provides a mechanism for grouping endpoints that share common policy requirements.
An EPG can represent a logical application tier such as:
WEB-EPG
APP-EPG
DB-EPG
Security policy can then be applied to the relationships between these groups.
This provides a more scalable model than individually managing every endpoint.
2.7 Contracts
Contracts define communication relationships between EPGs.
For example:
WEB-EPG
↓
WEB-TO-APP contract
↓
APP-EPG
The contract can reference filters describing the traffic that is permitted.
This allows the policy to express both:
Who may communicate
What traffic is allowed
2.8 Filters and Least Privilege
A filter defines traffic characteristics such as protocol and ports.
For example:
TCP/443
or:
TCP/5432
The security model can therefore become:
Group
→ Contract
→ Filter
→ Permitted traffic
This is more meaningful than simply allowing an entire subnet to communicate.
2.9 EPGs, Contracts and the Security Boundary
The relationship between the endpoint group and contract becomes the security boundary.
For example:
WEB-EPG
can communicate with:
APP-EPG
because a contract exists.
However:
WEB-EPG
cannot directly communicate with:
DB-EPG
unless an appropriate policy relationship exists.
This creates an explicit application communication model.
2.10 Endpoint Security Groups
Endpoint Security Groups, or ESGs, provide an additional security-oriented abstraction within ACI.
They allow security classification to be separated from some of the forwarding relationships that historically constrained EPG-based designs.
This can provide greater flexibility when applying security policy across workloads.
The important concept is:
Security classification does not always have to map directly to a traditional network segment.
This becomes increasingly valuable in environments containing dynamic workloads.
2.11 Micro-Segmentation Across Distributed Workloads
Micro-segmentation becomes particularly useful when workloads that appear similar from a network perspective require different security treatment.
For example:
Production APP
and
Development APP
may share infrastructure but should not necessarily share identical security policy.
Similarly:
Windows workloads
and
Linux workloads
may require different treatment during a security incident.
Micro-segmentation provides additional classification mechanisms that can support these requirements.
2.12 L4–L7 Security Service Integration
Segmentation determines whether communication should occur.
Sometimes that is not enough.
A security architecture may also require:
Firewall inspection
IPS
Load balancing
Application security
Other L4–L7 services
This introduces a second question:
If the traffic is permitted, does it also require deeper inspection?
That distinction becomes the focus of Section 3.
2.13 Cloud Security Perimeters
Segmentation is not limited to the physical data center.
Cloud environments require similar principles.
For example, Google Cloud VPC Service Controls can establish security perimeters around supported cloud resources to help reduce the risk of unauthorised data movement.
The important principle is that cloud security boundaries should complement:
IAM
Network controls
Workload identity
Logging
Application security
No single cloud perimeter replaces identity or application-level authorisation.
2.14 Cloud Edge Protection
Cloud environments may also require edge protection.
Cloud security services can provide capabilities such as:
DDoS protection
WAF
Security policy
Threat detection
Edge traffic controls
These controls protect applications before traffic reaches the workload environment.
2.15 Hybrid Security
Hybrid architectures may contain:
Data center
↓
Cloud connectivity
↓
Cloud VPC
↓
Managed services
↓
Internet-facing applications
The security model therefore has to remain consistent across these boundaries.
Security policy should identify:
Which workloads communicate
Which services are exposed
Which identities are trusted
Which traffic is permitted
Where deeper inspection is required
2.16 Private Service Connectivity
Private connectivity mechanisms such as Private Service Connect can provide private access to supported services without requiring workloads to use public IP paths for that service relationship.
However, private connectivity should not be confused with authorisation.
A private connection answers:
How does the traffic reach the service?
Security policy still needs to answer:
Is this workload authorised to use the service?
Connectivity and authorisation are separate security concerns.
2.17 Traditional ACL-Based Security
Traditional ACLs remain useful.
They are particularly appropriate for:
Infrastructure filtering
Management-plane protection
Simple protocol restrictions
Layer 2 controls
Specific interface requirements
The problem occurs when ACLs become the only mechanism used to represent complex application security.
At that point, the configuration can become difficult to understand and maintain.
2.18 MAC ACLs
MAC-based filtering can be useful for Layer 2 security requirements.
It can control traffic based on source or destination MAC information.
This is a more granular mechanism than simply trusting an entire VLAN, but it remains a relatively low-level security control.
2.19 VLAN ACLs
VLAN-based access controls can provide filtering for traffic associated with particular VLANs.
They remain useful for specific infrastructure requirements, but they do not provide the same application-centric abstraction as workload groups and contracts.
2.20 Policy as a Layered Enforcement Model
A mature security architecture can therefore combine:
Traditional ACLs
EPGs
ESGs
Contracts
Filters
Micro-segmentation
L4–L7 services
The controls are complementary.
The objective is not to eliminate traditional networking controls.
The objective is to place each control at the appropriate architectural layer.
2.21 Engineering Design Principles
A modern segmentation architecture should follow several principles.
Start with communication requirements
Determine which workloads actually need to communicate.
Apply least privilege
Permit only the protocols and services required.
Minimise security zones
Avoid unnecessarily large trust boundaries.
Make policy application-centric
Express policy in terms of workloads and application relationships where possible.
Separate segmentation from deep inspection
A communication relationship being permitted does not mean that the traffic requires no further inspection.
Design for mobility
Policy should remain meaningful as workloads move.
Build quarantine capability
Compromised workloads should be capable of being isolated.
2.22 The Result: Policy-Driven Segmentation
The traditional security model can be represented as:
Interface → ACL → IP address → Rule
The application-centric model becomes:
Workload → Group → Contract → Filter → Enforcement
This allows the security architecture to follow the workload rather than simply following the physical topology.
The key engineering question becomes:
Who should communicate, what should they communicate with, and which traffic is actually required?
Once that policy has been established, the next challenge is enforcing it and introducing deeper inspection where necessary.
Role: Front-End
Role: Application Tier
The communication is evaluated against identity, segmentation, application relationship and risk before the final action is applied.
Micro-segmentation is not simply creating more VLANs. The objective is to express which workloads may communicate, under which conditions, and with which security controls.
Data Center Security with Cisco ACI
Once security relationships have been defined, the next engineering challenge is enforcement. Cisco ACI provides a policy-driven fabric model for segmentation and communication control, while dedicated security services can provide deeper inspection where required.
How EPGs, contracts, filters, micro-segmentation, uSeg/µEPG concepts and service graphs can be combined to enforce application-aware security policy.
ACI segmentation should not be treated as a replacement for every security appliance. Use the fabric for segmentation and policy enforcement, and dedicated security services when deeper inspection is required.
3. Data Center Security with Cisco ACI
Cisco ACI provides a policy-driven framework for implementing segmentation and security enforcement across the data center fabric.
Sections 1 and 2 established the architecture and policy model.
This section moves to the next question:
How is that policy actually enforced, and when do we need deeper security inspection?
ACI can enforce communication relationships between groups of endpoints through constructs such as EPGs, ESGs, contracts, and filters.
However, segmentation and policy enforcement should not be confused with complete deep-packet or application security inspection.
A modern architecture can therefore combine:
Workload identity → Segmentation → Contract → Filter → Traffic steering → Security service → Application
3.1 Application-Centric Security
Traditional security often begins with the physical or logical location of a device.
Application-centric security begins with the workload.
Instead of asking:
Which VLAN is this server connected to?
we ask:
What workload is this, what application does it belong to, and what should it communicate with?
ACI allows these application relationships to become part of the infrastructure policy model.
3.2 The ACI Allowlist Model
ACI uses an allowlist-oriented policy model.
Communication between endpoint groups requires appropriate policy.
For example:
WEB → APP
Allowed:
TCP/443
The existence of a policy relationship does not mean that all traffic between the workloads should be permitted.
Filters can restrict the relationship to the services actually required.
This supports least-privilege communication.
3.3 Segmentation Is Not a Next-Generation Firewall
This distinction is important.
ACI provides distributed policy enforcement inside the fabric.
It can determine:
Which endpoint groups are communicating
Whether a policy relationship exists
Which traffic is permitted
Which protocols and ports are allowed
However, deeper security functions may require dedicated services.
These can include:
Next-generation firewalls
IPS
Application security
Load balancers
Other L4–L7 services
Therefore:
ACI segmentation ≠ complete security inspection
Instead:
ACI segmentation + security services = layered enforcement
3.4 Contracts as Enforcement Policy
A contract establishes the policy relationship between endpoint groups.
For example:
APP-EPG
↓
APP-TO-DB
↓
DB-EPG
The contract can reference filters that define the permitted traffic.
This separates:
Relationship
from
Traffic definition
The policy therefore becomes easier to understand and reuse.
3.5 The Challenge with Static ACLs
Traditional ACLs can become increasingly complex as applications grow.
Rules may contain:
Source addresses
Destination addresses
Protocols
Ports
Interfaces
Exceptions
Temporary rules
As the environment changes, administrators may add additional rules without removing old ones.
This creates policy accumulation.
Over time, the ACL may still function but become difficult to understand.
A security policy that cannot be easily understood is difficult to audit and maintain.
3.6 Topology-Independent Policy
One of the important advantages of an application-centric policy model is that security relationships are not permanently tied to individual interfaces.
The conceptual model becomes:
Endpoint → Group → Policy → Contract → Filter
rather than:
Interface → ACL → Address → Rule
This allows policy to remain meaningful as workloads move within the fabric.
3.7 Micro-Segmentation
Large security zones can create excessive trust.
If hundreds of workloads share the same broad security boundary, compromise of one workload can provide an attacker with opportunities for lateral movement.
Micro-segmentation reduces these trust relationships.
Instead of:
Production → Production
we can define:
WEB → APP
APP → DB
MONITORING → WORKLOAD
BACKUP → STORAGE
3.8 EPGs and ESGs
EPGs provide a fundamental mechanism for grouping endpoints and applying common policy.
ESGs provide an additional security-oriented abstraction that can offer greater flexibility when classifying workloads for security policy.
The important engineering principle is that security classification does not always need to map directly onto a single traditional network segment.
3.9 Micro-Segmentation with Additional Endpoint Attributes
ACI micro-segmentation capabilities can provide more granular classification of endpoints.
This can be useful when workloads inside the same broader application environment require different security treatment.
For example:
Production APP
and
Development APP
may require different security policies.
Similarly:
Windows workloads
and
Linux workloads
may require different treatment during an incident.
3.10 Example: Workload Quarantine
Imagine an application environment containing both Windows and Linux workloads.
A security team identifies a vulnerability affecting the Windows workload population.
Instead of manually modifying policies for every individual host, the affected workloads can be classified into a more restrictive security policy where the architecture supports the required classification.
The resulting model is:
Normal workload
↓
Normal application policy
After compromise:
Affected workload
↓
Restricted communication
↓
Security / remediation services
This demonstrates an important security principle:
Containment should reduce the blast radius without requiring the entire application architecture to be redesigned.
3.11 L4–L7 Security Services
Segmentation determines whether communication should occur.
Deep inspection determines whether permitted traffic is safe or appropriate according to additional security criteria.
Potential security services include:
Firewalls
IPS
Load balancers
Application security platforms
Other L4–L7 services
This introduces the next layer of the architecture.
3.12 Cisco Secure Firewall Integration
Cisco security platforms can be integrated into ACI-based architectures where deeper inspection is required.
A dedicated firewall can provide capabilities beyond distributed fabric policy, depending on the platform and deployment.
These may include:
Stateful firewalling
Intrusion prevention
Threat inspection
Application-aware security
VPN services
Security logging
The architectural principle is:
ACI determines which traffic requires additional policy enforcement.
The security service performs the deeper inspection.
3.13 Policy-Based Redirect
Policy-based redirect provides a mechanism for steering selected traffic towards a service node.
Conceptually:
WEB → APP
Normal flow:
WEB → APP
Traffic requiring inspection:
WEB → Firewall → APP
This means that not every communication flow necessarily has to traverse the same security appliance.
Inspection can be applied according to application and security policy.
3.14 ACI L4–L7 Services
ACI can integrate Layer 4–Layer 7 services into the application policy model.
Potential services include:
Firewalls
IPS
Load balancers
Application delivery services
Other supported security appliances
This allows security functions to become part of the traffic-processing architecture.
3.15 Service Graphs
A service graph represents a logical processing path through integrated services.
For example:
Consumer
↓
Firewall
↓
IPS
↓
Load Balancer
↓
Provider
Each service can perform a different function.
The graph therefore describes the intended service chain rather than simply representing a physical sequence of network devices.
3.16 Selective Traffic Inspection
Not every flow necessarily requires the same level of inspection.
For example:
| Traffic | Security approach |
|---|---|
| WEB → APP | Application-aware inspection |
| APP → DB | Restricted database traffic |
| Monitoring → Workload | Permit required telemetry |
| Backup → Storage | Permit approved backup services |
| Unknown → Production | Deny |
| Quarantined → Application | Restrict |
Inspection should therefore be based on:
Application requirements
Security risk
Performance
Capacity
Compliance
Operational requirements
3.17 Distributed Enforcement and Centralised Policy
ACI combines:
Centralised policy definition
with:
Distributed enforcement
This allows policy to be centrally managed while enforcement occurs within the fabric.
Dedicated L4–L7 services can then provide deeper inspection where required.
The architecture becomes:
APIC
↓
Policy
↓
ACI Fabric
↓
Distributed enforcement
↓
L4–L7 Security Services
↓
Inspection
This separation makes the overall security architecture easier to reason about.
3.18 Security Enforcement as a Layered Model
A complete enforcement architecture can therefore be represented as:
Endpoint classification
↓
Segmentation
↓
Contract
↓
Filter
↓
Traffic steering
↓
Deep inspection
↓
Telemetry
Each layer answers a different question.
| Layer | Question |
|---|---|
| Endpoint | What is communicating? |
| Group | What security class does it belong to? |
| Contract | Are these groups allowed to communicate? |
| Filter | Which traffic is permitted? |
| Redirect | Does the flow require a service? |
| Inspection | Does deeper security analysis occur? |
| Telemetry | What actually happened? |
3.19 Example: Web Application Security
Consider:
WEB → APP → DB
The security policy may be:
WEB → APP
TCP/443 permitted.
APP → DB
Only required database traffic permitted.
WEB → DB
No direct communication.
Management → Workloads
Restricted to approved management systems.
Unknown → Production
Denied.
Selected application traffic can then be steered through appropriate security services.
3.20 Security Enforcement and Lateral Movement
Suppose an attacker compromises a web server.
Without effective segmentation:
WEB
↓
APP
↓
DB
↓
Management
↓
Backup
The attacker may have multiple paths to additional systems.
With application-centric segmentation:
WEB
↓
APP
↓
Policy boundary
↓
DB
Each relationship becomes another security decision.
If the workload is later identified as compromised, its policy can be restricted further.
3.21 Enforcement as Part of a Feedback Loop
Security enforcement should not operate independently of visibility.
A policy may state:
WEB can communicate with APP using TCP/443.
Telemetry may later show:
WEB has started communicating with unexpected destinations.
That behaviour becomes a security signal.
The architecture can then move towards:
Observe → Analyse → Restrict → Investigate
This connects directly with Section 4.
3.22 Engineering Design Principles
A modern enforcement architecture should:
Start with application relationships
Use least privilege
Separate segmentation from deep inspection
Use micro-segmentation where required
Steer appropriate traffic through security services
Avoid unnecessary inspection paths
Design for workload mobility
Provide quarantine capability
Collect telemetry from enforcement points
3.23 The Result: Policy-Driven Enforcement
The traditional model is:
Interface → ACL → Address → Rule
The application-centric model becomes:
Workload → Group → Contract → Filter → Service → Inspection
The network fabric enforces the communication relationship.
Dedicated security services provide deeper inspection.
Telemetry validates what actually occurred.
The result is a layered security architecture in which each technology performs a specific role.
ACI provides policy-driven traffic classification and can steer selected flows toward integrated L4–L7 services. The fabric's segmentation policy and dedicated inspection functions solve different security problems.
Visibility, Detection and Adaptive Defence
Segmentation and enforcement reduce the available attack surface, but security does not end when a policy is deployed. Modern data centers also need continuous visibility, correlated evidence, incident investigation and a controlled path from detection to containment and recovery.
How flow telemetry, packet visibility, SIEM/SOAR, EDR/XDR, identity context and behavioural analysis can be combined to investigate east-west security events.
The objective is not simply to generate more alerts. It is to build a measurable control loop where evidence leads to a decision, the decision drives enforcement, and the result is verified.
4. Visibility, Detection and Adaptive Defence
Sections 1–3 established the security architecture:
Security architecture → segmentation → policy → enforcement → inspection
However, preventative controls alone are not enough.
A policy can define what should happen.
Telemetry tells us what actually happened.
A firewall may permit a connection.
A workload may still behave abnormally.
A correctly segmented server may still become compromised.
Modern data center security therefore requires a continuous feedback loop:
Observe → Analyse → Detect → Investigate → Respond → Validate
4.1 From Security Policy to Security Observability
Consider a simple policy:
WEB → APP
Allowed:
TCP/443
From a policy perspective, the relationship is correct.
But telemetry might reveal:
A sudden increase in connections
Unexpected traffic volumes
Repeated failed connections
Communication with previously unused endpoints
Unusual connection timing
Unexpected external destinations
A workload communicating outside its normal application relationship
The policy has not necessarily changed.
The behaviour has changed.
This is why security architecture requires both policy enforcement and continuous observation.
4.2 The Security Telemetry Pipeline
A modern environment can generate telemetry from many layers:
Workload
↓
Network flow
↓
Packet / protocol
↓
Identity
↓
Application
↓
Infrastructure
↓
Security platform
↓
Analytics
No single telemetry source provides the complete picture.
4.3 Network Flow Visibility
Flow telemetry such as NetFlow and IPFIX can provide information about communication patterns including:
Source
Destination
Protocol
Ports
Volume
Packet counts
Timing
Direction
For example:
APP-01 → DB-01
TCP/5432
Normal
versus:
APP-01 → DB-17
TCP/5432
Unexpected
The second event may become a security investigation even if the network technically permits the traffic.
4.4 Packet-Level Visibility
Flow telemetry tells us that communication occurred.
Packet-level analysis can provide additional information about the communication itself.
Depending on the deployment, packet analysis can help identify:
Protocol behaviour
Application exchanges
Suspicious traffic patterns
Malformed packets
Unexpected protocols
Attack indicators
Session behaviour
Packet capture is particularly useful during incident investigation.
4.5 Identity-Aware Security
Network addresses are not sufficient security identities.
An IP address can represent one workload today and another tomorrow.
Modern environments therefore associate network activity with additional context.
Useful information can include:
User identity
Workload identity
Device identity
Application identity
Namespace
Kubernetes service
VM identity
Cloud resource identity
Security group
Endpoint classification
This allows security teams to move from:
10.10.20.15 connected to 10.10.30.20
towards:
Production application APP-01 attempted to access database service DB-01.
The second statement provides substantially more useful security context.
4.6 Security Analytics
Telemetry becomes more valuable when it is correlated.
Consider:
Event 1
Authentication succeeded.
Event 2
The user accessed a server.
Event 3
The server established a new outbound connection.
Event 4
The workload contacted an unusual destination.
Event 5
Traffic volume increased dramatically.
Each event might be harmless in isolation.
Together they may describe a potential compromise.
Security analytics attempts to identify these relationships.
The objective is to move from:
Thousands of independent events
to:
A smaller number of meaningful security stories.
4.7 Behavioural Baselines
Security systems need to understand normal behaviour.
An application server may normally:
Communicate with three application services
Use HTTPS
Connect to a known database
Generate predictable traffic
Operate continuously
Use known DNS services
This creates a behavioural baseline.
If the same workload suddenly:
Scans hundreds of hosts
Attempts SSH connections
Contacts an unfamiliar external service
Generates significantly more traffic
Attempts unexpected database access
the behaviour becomes anomalous.
An anomaly does not automatically mean compromise.
It means:
The workload’s behaviour requires investigation.
4.8 Detecting Lateral Movement
Lateral movement occurs when an attacker attempts to move from an initial compromised workload to additional systems.
A simplified attack path is:
Initial compromise
↓
Credential acquisition
↓
Discovery
↓
Service enumeration
↓
Additional connections
↓
Second workload
Segmentation can reduce these paths.
Telemetry can reveal them.
Analytics can correlate them.
Response mechanisms can attempt to contain them.
The resulting model is:
Prevent → Detect → Contain
4.9 East-West Traffic Analytics
Modern applications generate significant east-west traffic.
Examples include:
WEB → APP
APP → DB
APP → CACHE
SERVICE → SERVICE
MONITORING → WORKLOAD
Security analytics can model these relationships.
Normal:
APP-01 → DB-01
Abnormal:
APP-01 → DB-01
APP-01 → DB-02
APP-01 → DB-03
APP-01 → hundreds of hosts
The final pattern could indicate:
Scanning
Discovery
Malware propagation
Misconfiguration
Legitimate operational activity
Context determines the conclusion.
4.10 Security Graphs
A useful way to understand modern security is as a graph.
Nodes represent:
Users
Workloads
Applications
Databases
Services
Devices
Security systems
Edges represent:
Network communication
Authentication
Application dependencies
Policy relationships
Administrative access
This model can answer questions such as:
Which systems can this compromised workload reach?
or:
Which applications depend on this database?
or:
Which systems would be affected if this workload were quarantined?
Security therefore becomes a relationship-analysis problem rather than simply a log-analysis problem.
4.11 SIEM Integration
A SIEM can aggregate security events from multiple systems.
Potential sources include:
Firewalls
IDS/IPS
Network infrastructure
Servers
Identity platforms
Cloud platforms
Kubernetes
Endpoint security
Applications
The SIEM can provide:
Search
Correlation
Alerting
Investigation
Historical analysis
Reporting
The SIEM does not replace the underlying security controls.
It provides a central analytical layer.
4.12 SOAR and Automated Response
Detection becomes more valuable when it can trigger an appropriate response.
A response workflow might be:
High-risk alert
↓
Verify evidence
↓
Identify workload
↓
Check identity
↓
Review communications
↓
Apply containment
↓
Notify security team
↓
Record incident
Possible actions include:
Isolating a workload
Restricting communication
Disabling an identity
Blocking a destination
Increasing inspection
Opening an incident
Collecting forensic evidence
Automation must be carefully controlled.
A false positive that automatically isolates a critical production system can itself create an operational incident.
4.13 Dynamic Segmentation
Security state can change over time.
A workload that is healthy at 09:00 may become suspicious at 09:15.
The security architecture should therefore be capable of changing its posture.
4.14 Risk-Based Enforcement
A useful model is:
| Risk | Example | Response |
|---|---|---|
| Low | Normal behaviour | Allow |
| Medium | Unusual destination | Monitor |
| High | Repeated scanning | Restrict |
| Critical | Confirmed compromise indicators | Quarantine |
This introduces a more flexible model than simply:
Allow / Deny
Security becomes increasingly risk-aware.
4.15 Identity, Device and Workload Context
Risk decisions become more useful when multiple dimensions are considered.
A security system can evaluate:
Identity
Who is requesting access?
Device
Is the device trusted and compliant?
Workload
Which application is generating the traffic?
Network
Where is the communication occurring?
Behaviour
Is the activity normal?
Threat intelligence
Is the destination or behaviour associated with known threats?
This creates contextual security decisions.
4.16 Continuous Verification
Authentication should not be treated as permanent trust.
An entity may initially be trusted and later become risky.
Security can therefore continuously evaluate:
Identity
Context
Policy
Behaviour
Device posture
Risk
This creates a feedback loop rather than a one-time access decision.
4.17 Threat Intelligence
Threat intelligence can add external context to security analysis.
Examples include intelligence relating to:
Malware infrastructure
Command-and-control systems
Phishing
Suspicious domains
Known malicious addresses
Threat intelligence becomes more valuable when combined with internal evidence.
For example:
Threat intelligence
DNS activity
Network flow
Endpoint telemetry
Identity context
can create a much stronger security signal.
4.18 Cloud Security Visibility
Cloud environments introduce additional security telemetry.
Security platforms can provide visibility into:
Resources
Identities
Configuration
Network exposure
Policy violations
Threat findings
Vulnerabilities
Hybrid environments are particularly challenging because a workload may communicate across:
Data Center
↓
Cloud VPC
↓
Managed service
↓
Internet-facing API
Network telemetry alone may not provide sufficient context.
Cloud security telemetry therefore needs to become part of the broader security architecture.
4.19 Kubernetes and Container Security
Containerised environments introduce additional security dimensions:
Namespace
Pod
Service
Service account
Network policy
Container image
Runtime behaviour
Cluster identity
A workload may therefore be represented as:
User
↓
Kubernetes workload
↓
Service
↓
Pod
↓
Container
↓
Network destination
Traditional IP-based monitoring alone can lose important application context because containers are often short-lived and addresses can change.
4.20 Runtime Security
Network controls cannot explain everything happening inside a workload.
Runtime security can provide visibility into:
Unexpected processes
File access
Privilege changes
Suspicious system calls
Unexpected network connections
Container escape indicators
Abnormal process behaviour
This complements network telemetry.
The resulting evidence becomes:
Network behaviour
Identity
Application behaviour
Runtime behaviour
4.21 Detection Engineering
Security detection should be engineered rather than simply enabled.
A detection might begin with:
Can we detect a production workload scanning a large number of internal hosts?
The engineering process becomes:
Define expected behaviour
↓
Identify telemetry
↓
Create detection logic
↓
Test against normal traffic
↓
Test against simulated abnormal behaviour
↓
Measure false positives
↓
Tune
↓
Deploy
↓
Monitor
This turns security analytics into an engineering discipline.
4.22 Measuring Security Effectiveness
Security should be measurable.
Useful questions include:
Coverage
Can we see the important workloads?
Policy coverage
Are critical workloads protected by appropriate segmentation?
Detection coverage
Can important attack behaviours be detected?
Response time
How quickly can a security event be investigated?
Containment time
How quickly can a compromised workload be isolated?
False positives
How many alerts require no action?
Recovery
How quickly can the affected service return to normal?
4.23 Incident Investigation Workflow
A repeatable investigation process can be:
1. Identify
Which workload, identity, or device generated the event?
2. Establish baseline
What normally happens?
3. Identify deviation
What changed?
4. Determine scope
What else communicated with the affected workload?
5. Determine impact
What systems or data may be affected?
6. Contain
Can the workload be isolated?
7. Investigate
What evidence explains the event?
8. Remediate
Remove the underlying cause.
9. Validate
Confirm that the environment has returned to an expected state.
10. Improve
Update policy, detection, architecture, or operational processes.
4.24 Example: Compromised Application Server
Consider the application architecture developed throughout this guide:
WEB → APP → DB
APP-01 normally communicates with:
WEB services
DB services
Monitoring
Approved infrastructure services
Security analytics detects that APP-01 has started scanning internal hosts.
The investigation identifies:
APP-01 → DB-01
Normal
APP-01 → Monitoring
Normal
APP-01 → Hundreds of internal addresses
Abnormal
The security team correlates:
Network flow
Endpoint telemetry
Authentication activity
DNS activity
Firewall events
The combined evidence increases the risk score.
The response becomes:
APP-01
↓
High-risk state
↓
Restricted policy
↓
Security investigation
If compromise is confirmed:
APP-01
↓
Quarantine
↓
Remediation
The complete lifecycle is now:
Prevent → Observe → Detect → Investigate → Contain → Recover
4.25 Adaptive Security
The final evolution is adaptive security.
Instead of treating policy as permanently static, the architecture can respond to changing conditions.
Normal
Risk = Low
Standard application policy.
Suspicious
Risk = Medium
Additional monitoring and inspection.
High Risk
Risk = High
Restrict communication.
Compromised
Risk = Critical
Quarantine workload.
This does not mean every decision should be automated.
It means the architecture has mechanisms capable of changing security posture when evidence justifies it.
4.26 The Complete Data Center Security Architecture
The four sections can now be combined.
Layer 1 — Security Architecture
Physical, network, compute, storage, application, cloud and identity controls.
↓
Layer 2 — Segmentation and Policy
EPGs, ESGs, contracts, filters and micro-segmentation.
↓
Layer 3 — Enforcement and Inspection
Distributed enforcement, policy-based redirect, service graphs, firewalls, IPS and other L4–L7 services.
↓
Layer 4 — Visibility and Adaptive Defence
Flow telemetry, packet visibility, identity, analytics, SIEM, detection, response and dynamic containment.
The complete architecture becomes:
Workload
↓
Identity / Classification
↓
Segmentation
↓
Policy
↓
Enforcement
↓
Inspection
↓
Telemetry
↓
Analytics
↓
Risk
↓
Response
↓
Policy adjustment
This is the modern data center security feedback loop.
4.27 Engineering Principles
A mature security architecture should:
Know the workload
Minimise trust
Enforce least privilege
Inspect according to risk
Observe continuously
Correlate context
Detect behaviour
Prepare containment
Automate carefully
Measure effectiveness
4.28 Final Engineering Perspective
Modern data center security is no longer a single firewall positioned at the network perimeter.
Applications are distributed.
Workloads move.
Users and services are increasingly identity-driven.
Cloud and on-premises infrastructure coexist.
East-west communication can be as important as north-south traffic.
Security must therefore become an architectural capability rather than a single appliance.
The model developed throughout this guide is:
Understand the workload
↓
Define its security relationships
↓
Segment the environment
↓
Enforce least privilege
↓
Inspect higher-risk traffic
↓
Observe actual behaviour
↓
Detect deviations
↓
Respond to changing risk
↓
Continuously improve policy
The objective is not simply to prevent every possible connection.
It is to create an environment where:
Required communication is explicitly permitted, unnecessary communication is restricted, abnormal behaviour is visible, and compromised workloads can be contained before they become a larger incident.
That is the foundation of a modern, policy-driven data center security architecture.
Expected Role
Expected Target
Restricted Target
Begin with the baseline. WEB-01 has an expected role and is communicating with APP-01 over HTTPS.