Cyber security threat. Computer screen with programming code. Internet and network security. Stealing private information. Using technology to steal password and private data. Cyber attack crime

Software defined perimeter (SDP) A disruptive technology

Software-Defined Perimeter

Software Defined Perimeter (SDP) is a security architecture designed to control access to applications and network resources based on identity, device context, policy, and trust rather than simply relying on network location. The model became particularly influential as organizations moved beyond traditional data-centre perimeters toward cloud services, remote work, mobile users, and distributed applications.

The underlying principle is closely aligned with Zero Trust: a user or device should not receive implicit trust simply because it is connected to a corporate network. Access should be explicitly authenticated, authorised, continuously evaluated where appropriate, and limited to the resources required for the task.

SDP is therefore less about creating another physical network perimeter and more about creating a logical access boundary around applications and services.

How Software Defined Perimeter Works

A typical SDP architecture combines identity, policy enforcement, device information, application visibility, and encrypted connectivity. The exact implementation varies between vendors and platforms, but the overall workflow is generally based on several core capabilities.

Identity-Based Authentication

Users and devices are authenticated before access is granted. Modern implementations commonly integrate with enterprise identity providers, single sign-on, multi-factor authentication, certificates, and other strong authentication mechanisms.

Authentication establishes who or what is requesting access, but authentication alone does not determine whether access should be permitted.

Context-Aware Access Control

Access decisions can incorporate additional context such as device posture, operating-system state, user role, location, authentication strength, application sensitivity, and security policy.

For example, an authenticated user may be permitted to access a development application from a managed corporate device but denied access from an unmanaged or compromised endpoint.

This creates a more granular security decision than simply allowing or denying access based on an IP address or network segment.

Application-Level Access

Rather than exposing an entire internal network to an authenticated user, SDP aims to provide access only to the applications and services that the user is authorised to use.

This reduces unnecessary network visibility and limits the potential attack surface. A user accessing one internal application does not automatically need visibility of unrelated servers, databases, or management interfaces.

Micro-Segmentation and Lateral Movement Control

SDP architectures can support fine-grained segmentation by separating applications, workloads, users, and services according to policy.

If an endpoint or account is compromised, limiting access to specific resources can make lateral movement considerably more difficult. Segmentation therefore becomes an important containment mechanism alongside identity and endpoint security.

Encrypted Connectivity

After policy evaluation, authorised users are typically provided with an authenticated and encrypted connection to the required application or service.

This is particularly important for remote and hybrid environments where users may connect from networks that the organization does not control.

SDP and Zero Trust

SDP is closely associated with Zero Trust architecture, but the two terms are not interchangeable.

Zero Trust is the broader security model based on principles such as explicit verification, least-privilege access, continuous evaluation, and assuming that network location alone does not establish trust.

SDP describes an architectural approach for implementing some of those principles, particularly secure and controlled access to applications and services.

In modern enterprise environments, many capabilities originally associated with SDP are delivered through Zero Trust Network Access (ZTNA) platforms.

Benefits of SDP

Reduced Attack Surface

Applications and services do not necessarily need to be broadly exposed to users or external networks. Access can be restricted to authenticated and authorised identities.

Reduced Lateral Movement

Fine-grained access policies can prevent a compromised account or endpoint from automatically reaching large portions of the environment.

Identity-Centric Security

Security decisions can be based on user and device identity rather than relying primarily on source IP addresses, VLANs, or physical network location.

Support for Remote and Hybrid Access

SDP is well suited to environments where employees, contractors, applications, and services operate across corporate networks, cloud platforms, and remote locations.

Policy-Based Access

Centralised policy can define who can access particular applications, under which conditions, and from which types of devices.

Improved Visibility and Control

By combining identity, device, application, and access information, security teams can gain greater context around who is accessing which resources and why.

SDP in a Modern Security Architecture

SDP should not be viewed as a replacement for endpoint protection, identity security, secure web gateways, network segmentation, vulnerability management, or security monitoring.

Instead, it forms one layer of a broader security architecture.

A modern access model may therefore combine:

Identity and MFA → Device Posture → Policy Evaluation → ZTNA/SDP Access → Application Segmentation → Encryption → Monitoring and Audit

This layered approach allows organizations to enforce security controls before, during, and after access is granted.

The Evolution from SDP to ZTNA

The terminology around SDP has evolved considerably as Zero Trust has become a mainstream security architecture.

Many modern platforms now use the term Zero Trust Network Access rather than Software Defined Perimeter. The underlying objective remains similar: authenticate the user and device, evaluate context, apply policy, and provide narrowly scoped access to authorised applications.

The important architectural shift is away from asking whether a device is “inside” or “outside” the network and toward asking whether a specific access request should be allowed at that moment.

The Core Principle

Software Defined Perimeter represents an important step in the evolution from traditional perimeter security toward identity-centric access control.

Its most important contribution is the idea that network access should not automatically expose an entire environment. Instead, users and devices should receive explicit, policy-controlled access to the applications and resources they actually require.

Combined with Zero Trust, strong identity, device security, segmentation, encryption, and continuous monitoring, SDP provides a practical foundation for reducing attack surface and controlling access across modern hybrid and cloud environments.

Interactive Zero-Trust Lab

SDP Access Decision Lab

Software-Defined Perimeter changes the access model from “connect first, authenticate later” to “verify first, connect later.” Evaluate identity and context before allowing access to a protected application.

Scenario

Should this user be allowed to reach the Finance application?

A remote user requests access to a protected application. The SDP decision engine evaluates identity strength, device posture, application posture and network origin before deciding whether the application should be exposed.

Request Application requested
→
Authenticate Verify identity
→
Evaluate Check context
→
Authorize Apply policy
→
Connect Expose application

Access request

Change the request attributes and observe how the SDP decision changes.

SDP decision engine

The score is a teaching model showing how contextual signals can influence an access decision. Real implementations use their own policies.

0
Context Trust Score
Decision
NOT EVALUATED
Run the access evaluation to calculate the decision.
Identity PENDING
Authentication PENDING
Device posture PENDING
Application posture PENDING
Network context PENDING
[READY] SDP access decision engine initialized
[INFO] Protected application is not directly exposed
[INFO] Authenticate and evaluate context before connection
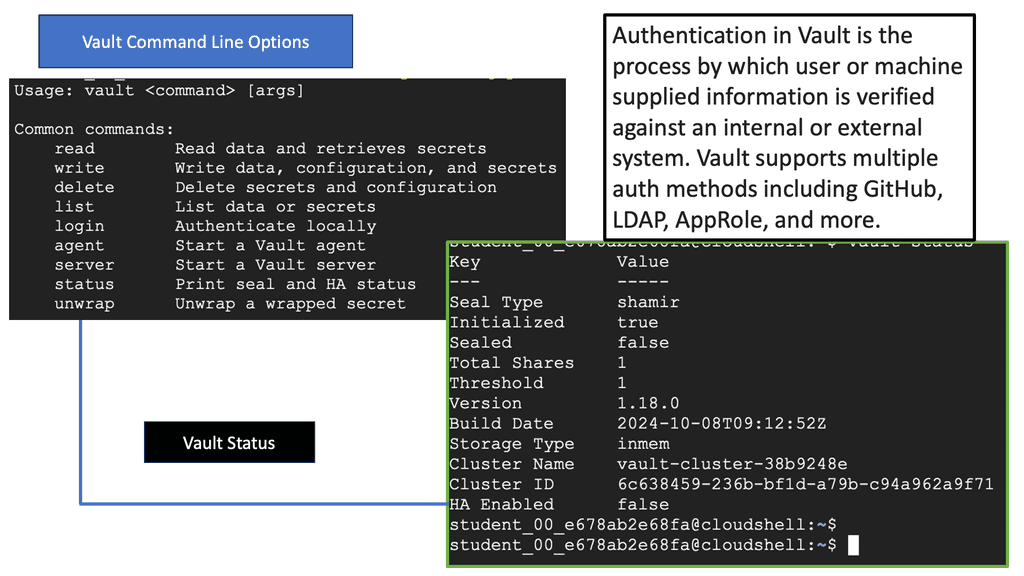
Engineering takeaway: SDP is based on identity-centric, policy-driven access rather than trusting network location alone. Authentication establishes who or what is requesting access; authorization determines what that identity and context are allowed to reach. A successful decision can then be followed by a controlled connection to the specific application.

Highlights: Software-Defined Perimeter

Understanding Software-Defined Perimeter

1- ) The software-defined perimeter, also known as Zero-Trust Network Access (ZTNA), is a security framework that adopts a dynamic, identity-centric approach to protecting critical resources. Unlike traditional perimeter-based security measures, SDP focuses on authenticating and authorizing users and devices before granting access to specific resources. By providing granular control and visibility, SDP ensures that only trusted entities can establish a secure connection, significantly reducing the attack surface.

2- )  its core, a Software-Defined Perimeter leverages a zero-trust security model, meaning that trust is never assumed simply based on network location. Instead, SDP dynamically creates secure, encrypted connections to applications or data, only after users and devices are authenticated. This approach significantly reduces the attack surface by ensuring that unauthorized entities cannot even see the network resources, let alone access them.

3- ) an SDP can transform the way organizations approach security. One major advantage is the enhanced security posture, as SDPs effectively cloak network resources from potential attackers. Moreover, SDPs are highly scalable, allowing organizations to quickly adapt to changing demands without compromising security. This flexibility is particularly beneficial for businesses with remote workforces, as it facilitates secure access to resources from any location.

Key SDP Components:

To implement an effective SDP, several key components work in tandem to create a robust security architecture. These components include:

1. Identity-Based Authentication: SDP leverages strong identity verification techniques such as multi-factor authentication (MFA) and certificate-based authentication to ensure that only authorized users gain access.

2. Dynamic Provisioning: SDP enables dynamic policy-based provisioning, allowing organizations to adapt access controls based on real-time context and user attributes.

3. Micro-Segmentation: With SDP, organizations can establish micro-segments within their network, isolating critical resources from potential threats and limiting lateral movement.

Software‑Defined Perimeter Through Continuous Trust Evaluation

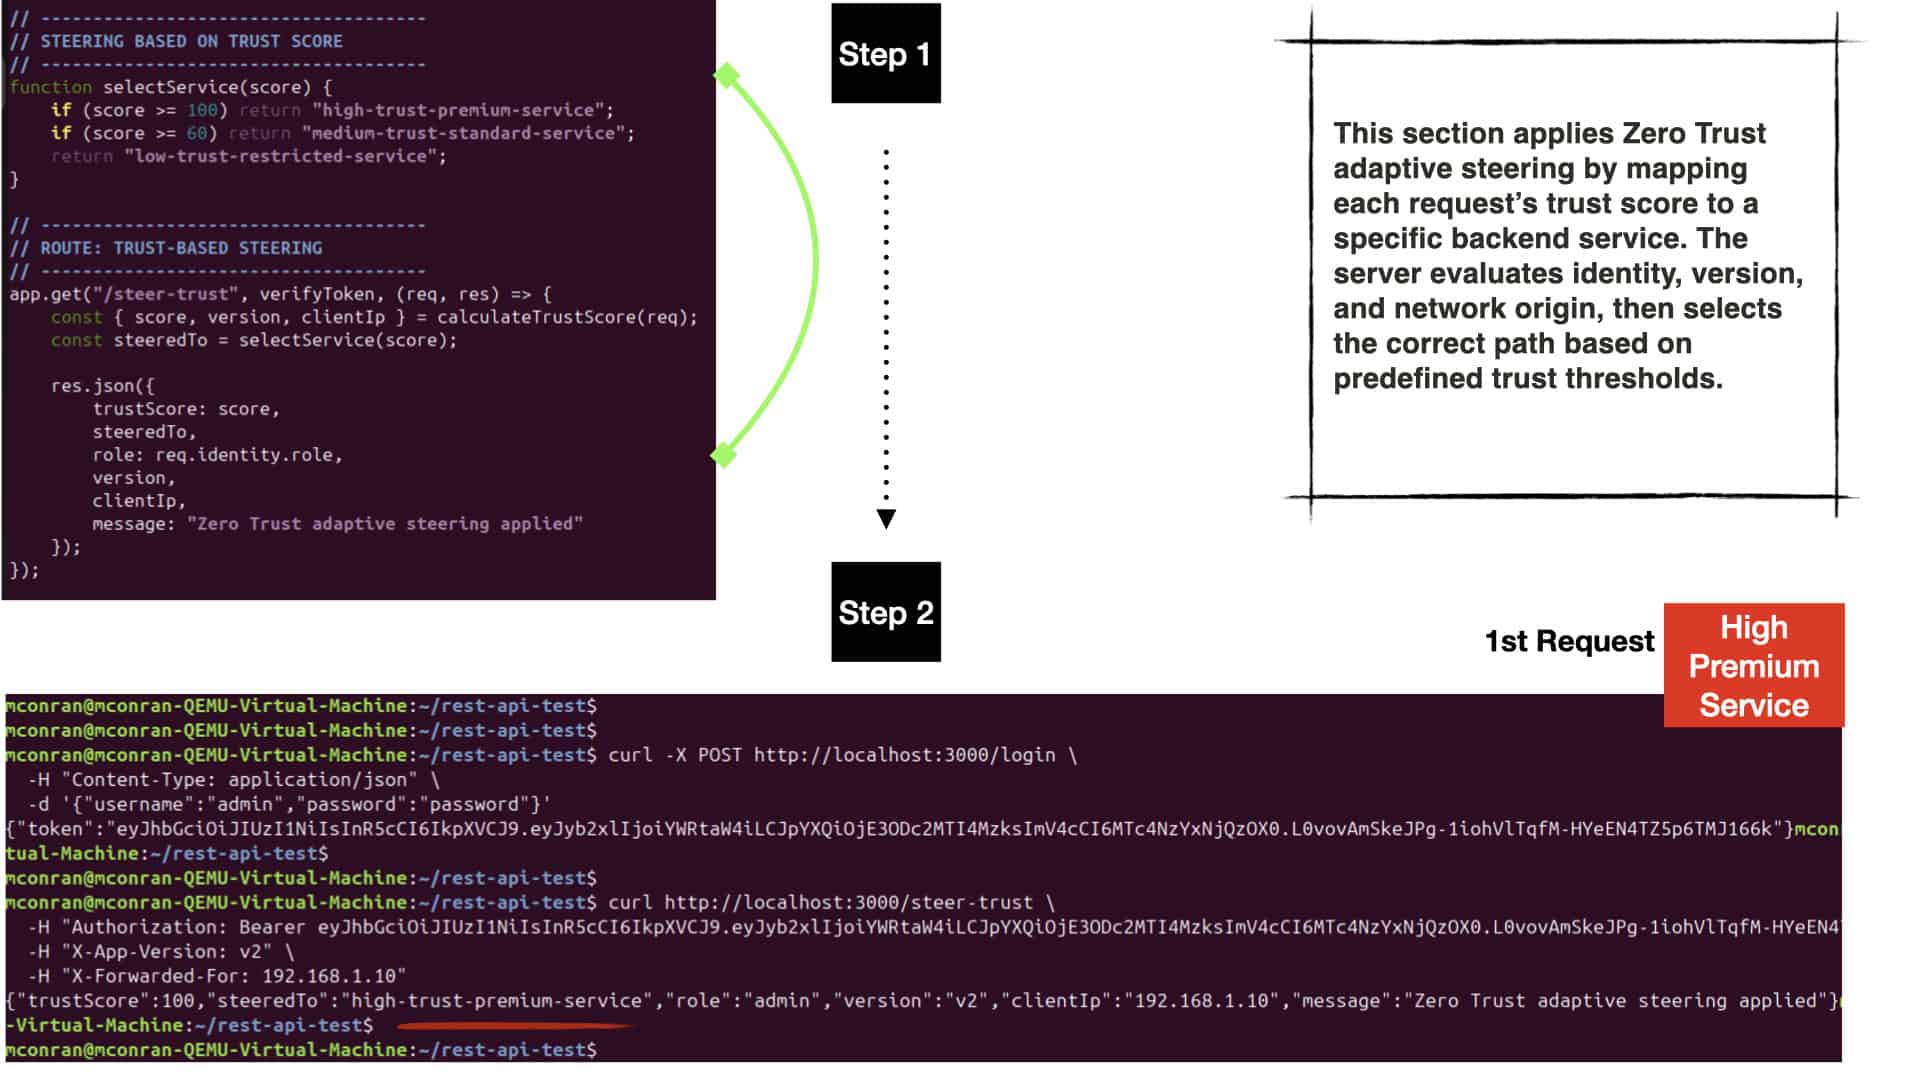
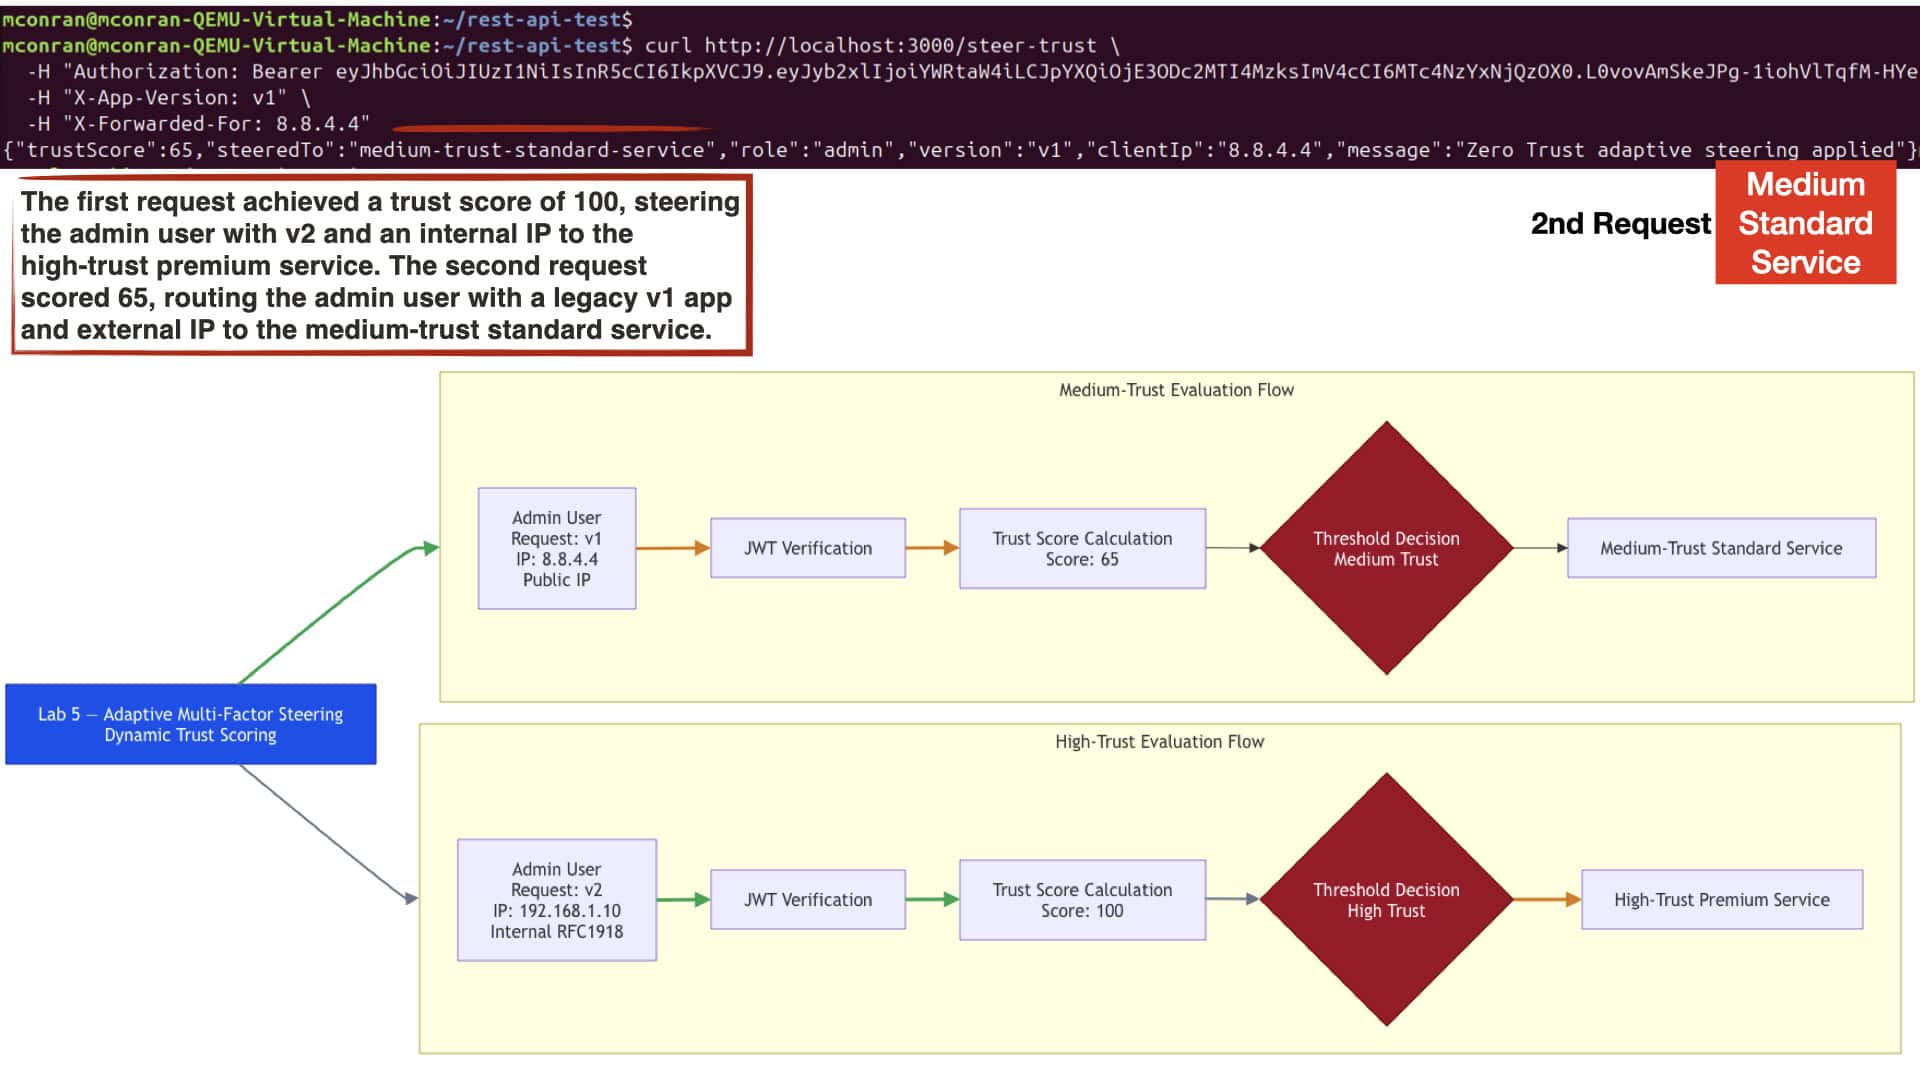
This lab demonstrates how a Software‑Defined Perimeter enforces continuous verification by evaluating every request against dynamic trust conditions. Instead of relying on static authentication, the trust engine calculates a score based on identity strength, application version, and network origin. This reflects SDP principles where access is granted only after identity is validated at every stage, creating a secure, identity‑centric perimeter around applications.
Trust Evaluation

The trust engine combines multiple contextual signals—user role, application posture, and IP source—to generate a weighted trust score. This aligns with Software‑Defined Perimeter architecture, where access decisions depend on layered identity and device attributes rather than network location. By classifying requests into high‑trust, medium‑trust, or low‑trust categories, the system enforces SDP’s identity‑driven access model and ensures that only validated entities reach protected services.

Once the trust score is computed, the steering engine selects the correct backend service based on identity‑driven trust thresholds. High‑trust identities are routed to premium services, medium‑trust identities to standard services, and low‑trust identities to restricted paths. This adaptive routing mirrors the Software‑Defined Perimeter model, ensuring that every request is segmented and steered according to verified identity posture, effectively hiding services behind a dynamic, identity‑controlled perimeter.
Trust Management

Example Micro-segmentation Technology:

Network Endpoint Groups (NEGs)

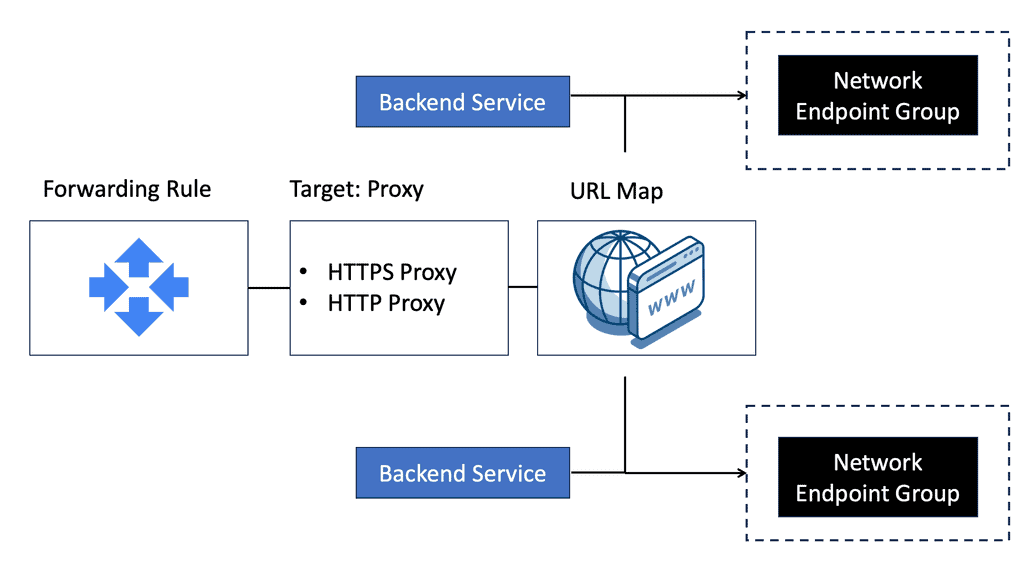
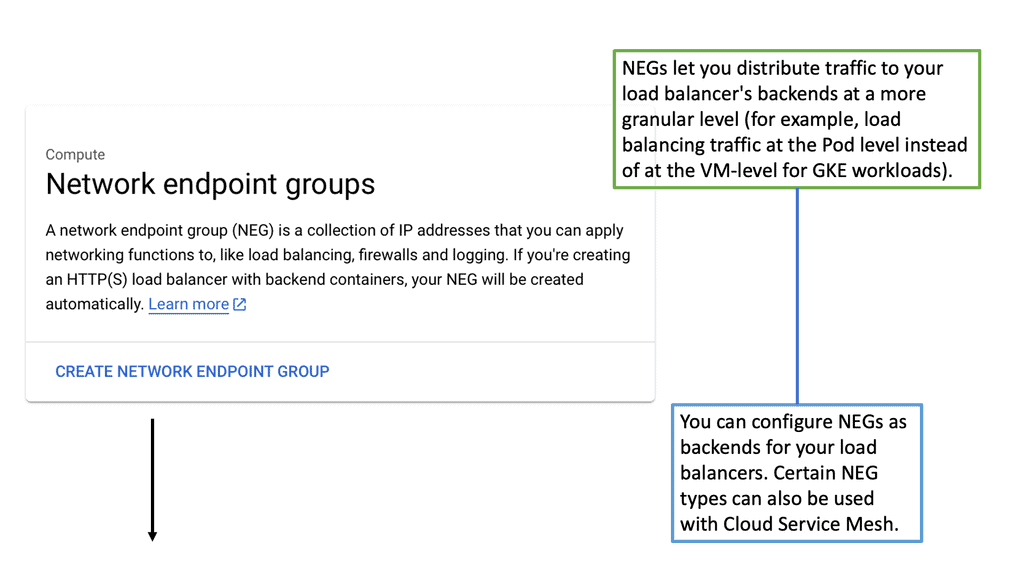
Network Endpoint Groups, or NEGs, are collections of IP address-port pairs that enable you to define how traffic is distributed across your applications. This flexibility makes NEGs a versatile tool, particularly in scenarios involving microsegmentation. Microsegmentation involves dividing a network into smaller, isolated segments to improve security and traffic management. NEGs support both zonal and serverless applications, allowing you to efficiently manage your infrastructure’s traffic flow.

The Role of NEGs in Microsegmentation

One of the standout features of NEGs is their ability to support microsegmentation within Google Cloud. By using NEGs, you can create precise policies that govern the flow of data between different segments of your network. This granular control is vital for security, as it allows you to isolate sensitive data and applications, minimizing the risk of unauthorized access. With NEGs, you can ensure that each microservice in your architecture communicates only with the necessary components, further enhancing your network’s security posture.
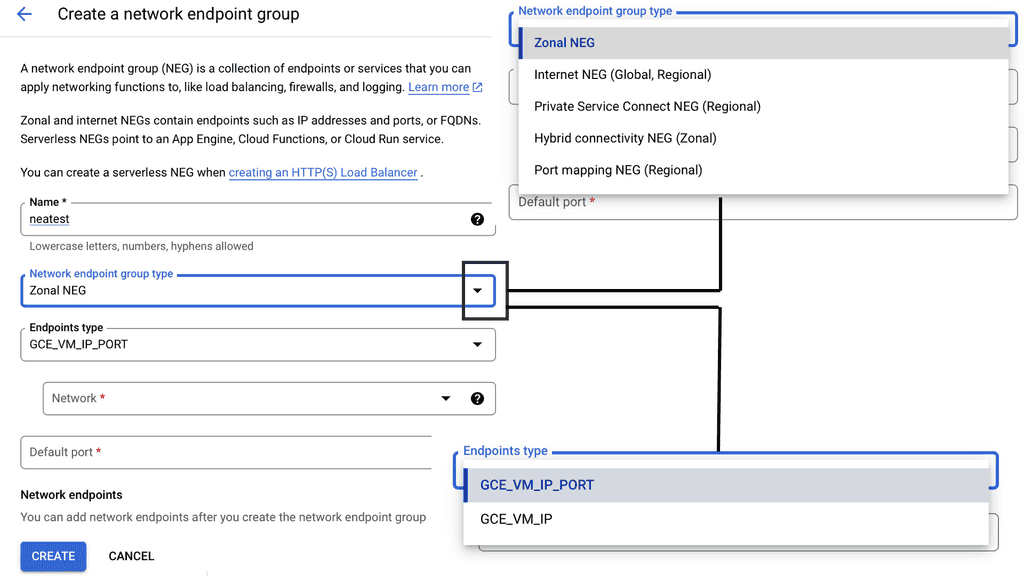
 

network endpoint groups

**A Disruptive Technology**

Over the last few years, there has been tremendous growth in the adoption of software-defined perimeter solutions and zero-trust network design. This has resulted in SDP VPN becoming a disruptive technology, especially when replacing or working with the existing virtual private network. Why? because the steps that software-defined perimeter proposes are needed.

Challenge With today’s Security

Today’s network security architectures, tools, and platforms are lacking in many ways when trying to combat current security threats. From a bird’ s-eye view, the zero-trust software-defined perimeter (SDP) stages are relatively simple. SDP requires that endpoints, both internal and external to an organization, authenticate and then be authorized before being granted network access. Once these steps occur, two-way encrypted connections between the requesting entity and the intended protected resource are created.

Example SDP Technology: VPC Service Controls

**What Are VPC Service Controls?**

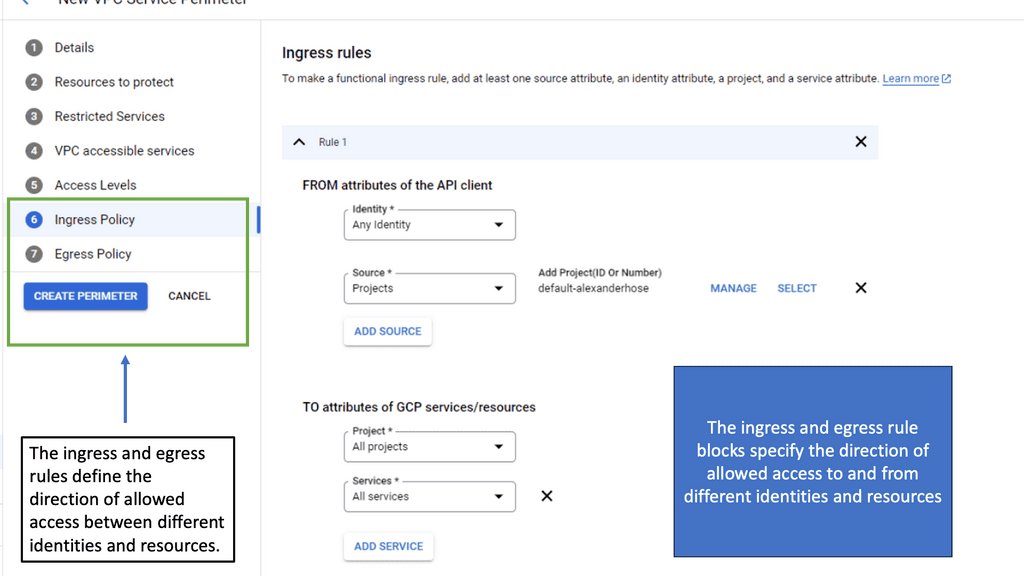
VPC Service Controls are a security feature in Google Cloud that help define a secure perimeter around Google Cloud resources. By creating service perimeters, organizations can restrict data exfiltration and mitigate risks associated with unauthorized access to sensitive resources. This feature is particularly useful for businesses that need to comply with strict regulatory requirements, as it provides a framework for managing and protecting data more effectively.

**Key Features and Benefits**

One of the standout features of VPC Service Controls is the ability to set up service perimeters, which act as virtual borders around cloud services. These perimeters help prevent data from being accessed by unauthorized users, both inside and outside the organization. Additionally, VPC Service Controls offer context-aware access, allowing organizations to define access policies based on factors such as user location, device security status, and time of access. This granular control ensures that only authorized users can interact with sensitive data.
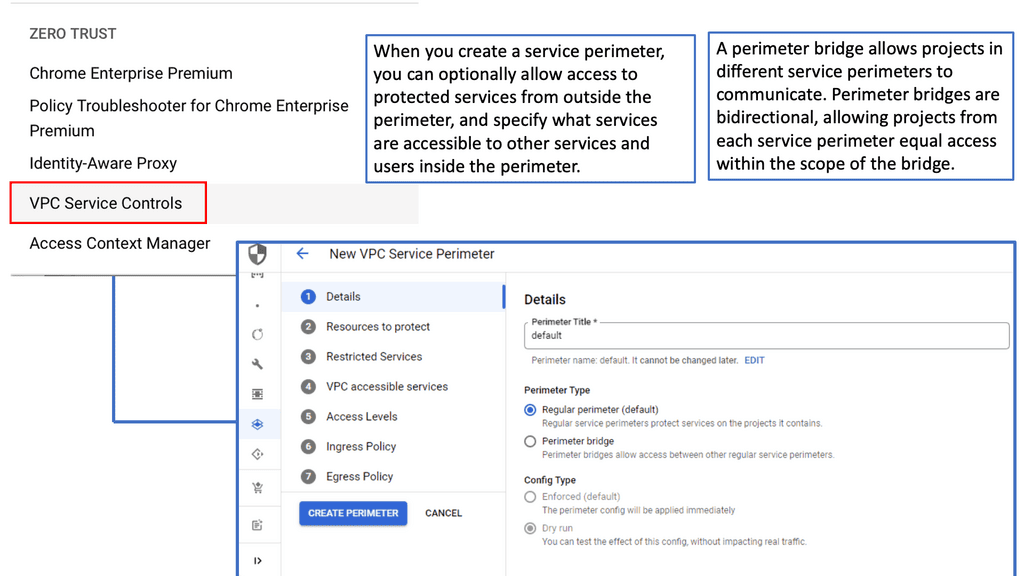
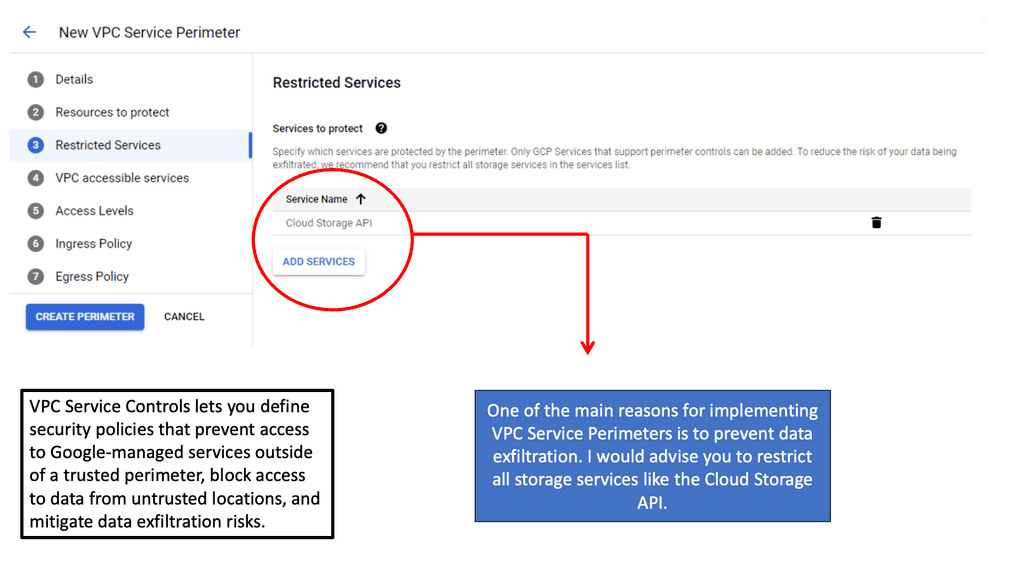
VPC Security Controls VPC Service Controls

**Implementing VPC Service Controls in Your Organization**

To effectively implement VPC Service Controls, organizations should begin by identifying the resources that require protection. This involves assessing which data and services are most critical to the business and determining the appropriate level of security needed. Once these resources are identified, service perimeters can be configured using the Google Cloud Console. It’s important to regularly review and adjust these configurations to adapt to changing security requirements and business needs.

**Best Practices for Maximizing Security**

To maximize the security benefits of VPC Service Controls, organizations should follow several best practices. First, regularly audit and monitor access logs to detect any unauthorized attempts to access protected resources. Second, integrate VPC Service Controls with other Google Cloud security features, such as Identity and Access Management (IAM) and Cloud Audit Logs, to create a comprehensive security strategy. Finally, ensure that all employees are trained on security protocols and understand the importance of maintaining data integrity.

Benefits of Software-Defined Perimeter:

1. Enhanced Security: SDP employs a zero-trust approach, ensuring that only authorized users and devices can access the network. This eliminates the risk of unauthorized access and reduces the attack surface.

2. Scalability: SDP allows organizations to scale their networks without compromising security. It seamlessly accommodates new users, devices, and applications, making it ideal for expanding businesses.

3. Simplified Management: With SDP, managing access controls becomes more straightforward. IT administrators can easily assign and revoke permissions, reducing the administrative burden.

4. Improved Performance: By eliminating the need for backhauling traffic through a central gateway, SDP reduces latency and improves network performance, enhancing the overall user experience.

Implementing Software-Defined Perimeter:

**Deploying SDP in Your Organization**

– Implementing SDP requires a strategic approach to ensure a seamless transition. Begin by identifying the critical assets that need protection and mapping out access requirements for different user groups.

– Next, choose an SDP solution that aligns with your organization’s needs and integrate it with existing infrastructure. It’s crucial to provide training for your IT team to effectively manage and maintain the system.

– Additionally, regularly monitor and update the SDP framework to adapt to evolving security threats and organizational changes.

Implementing SDP requires a systematic approach and careful consideration of various factors. Here are the critical steps involved in deploying SDP:

1. Identify Critical Assets: Determine the applications and resources that require enhanced security measures. This could include sensitive data, intellectual property, or customer information.

2. Define Access Policies: Establish granular access policies based on user roles, device types, and locations. This ensures that only authorized individuals can access specific resources.

3. Implement Authentication Mechanisms: To verify user identities, incorporate strong authentication measures such as multi-factor authentication (MFA) or biometric authentication.

4. Implement Encryption: Encrypt all data in transit to prevent eavesdropping or unauthorized interception.

5. Continuous Monitoring: Regularly monitor network activity and analyze logs to identify suspicious behavior or anomalies.


Interactive Investigation Lab

SDP Attack Surface Investigation

Investigate how identity-aware access, hidden application exposure, micro-segmentation and default-deny policies can reduce unnecessary network reachability and limit lateral movement.

Incident scenario

A compromised endpoint is probing the corporate environment

Your task is to identify which SDP controls prevent an attacker from discovering and reaching protected applications. Select the evidence that belongs in the investigation.

Internet / Attacker Scanning and probing
→
SDP Gateway Policy-controlled access
→
Protected Applications Finance · HR · Admin

Investigation evidence

Select the observations that explain why the protected environment has a reduced attack surface.

Investigation result

Build the evidence set, then validate your conclusion.

Attack Surface Assessment
INVESTIGATION PENDING
Select the evidence that correctly describes the SDP protection model.
Required findings: 5
Incorrect assumptions: 0
[READY] Investigation environment initialized
[INFO] Protected application surface is intentionally restricted
[INFO] Select evidence and validate the attack-path hypothesis
Engineering takeaway: SDP does not make systems invisible or magically secure. Its value is reducing unnecessary exposure and enforcing application-level access. Identity, authorization, segmentation and monitoring still matter after the initial access decision.

Software-Defined Perimeter

A software-defined perimeter constructs a virtual boundary around company assets. This separates it from access-based controls, restricting user privileges but allowing broad network access. The three fundamental pillars on which a software-defined perimeter is built are Zero Trust:

It leverages micro-segmentation to apply the principle of least privilege to the network, ultimately reducing the attack surface. Identity-centric: It’s designed around the user identity and additional contextual parameters, not the IP address.
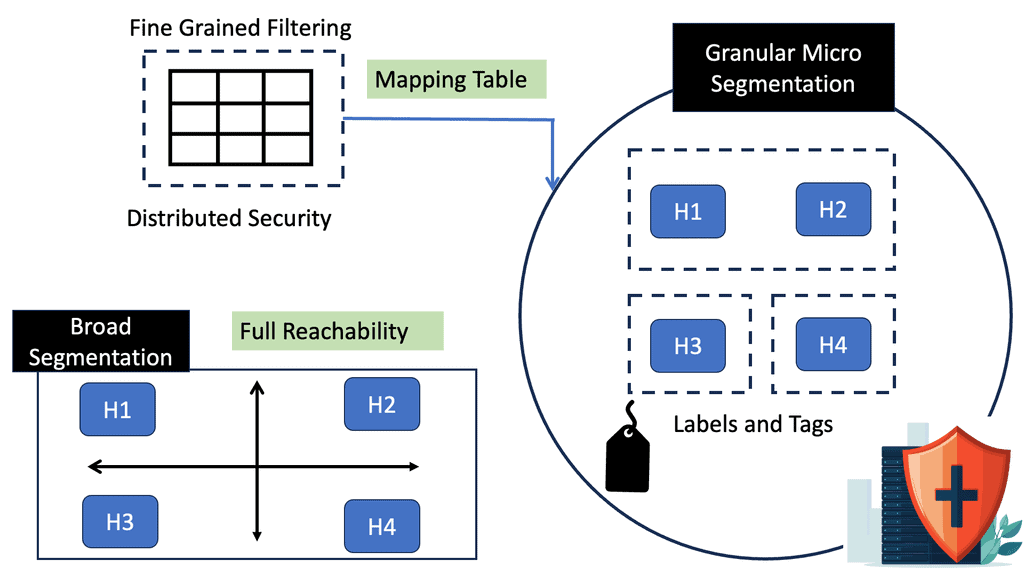
The Software-Defined Perimeter Proposition

Security policy flexibility is offered with fine-grained access control that dynamically creates and removes inbound and outbound access rules. Therefore, a software-defined perimeter minimizes the attack surface for bad actors to play with—a small attack surface results in a small blast radius. So less damage can occur.

A VLAN has a relatively large attack surface, mainly because the VLAN contains different services. SDP eliminates the broad network access that VLANs exhibit. SDP has a separate data and control plane.

A control plane sets up the controls necessary for data to pass from one endpoint to another. Separating the control from the data plane renders protected assets “black,” thereby blocking network-based attacks. You cannot attack what you cannot see.

Example: VLAN-based Segmentation

**Challenges and Considerations**

While VLAN-based segmentation offers many advantages, it also presents challenges that need addressing:

1. **Complexity in Management**: With increased segmentation, the complexity of managing and troubleshooting the network can rise. Proper training and tools are essential.

2. **Compatibility Issues**: Ensure that all network devices support VLANs and are configured correctly to avoid communication breakdowns.

3. **Security Oversight**: While VLANs enhance security, they are not foolproof. Regular audits and updates are necessary to maintain a robust security posture.
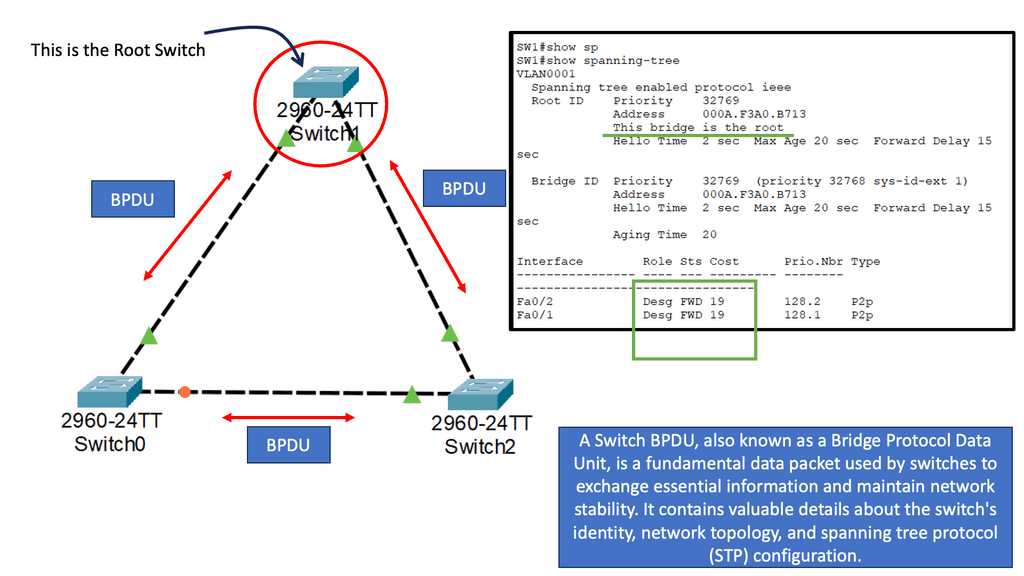
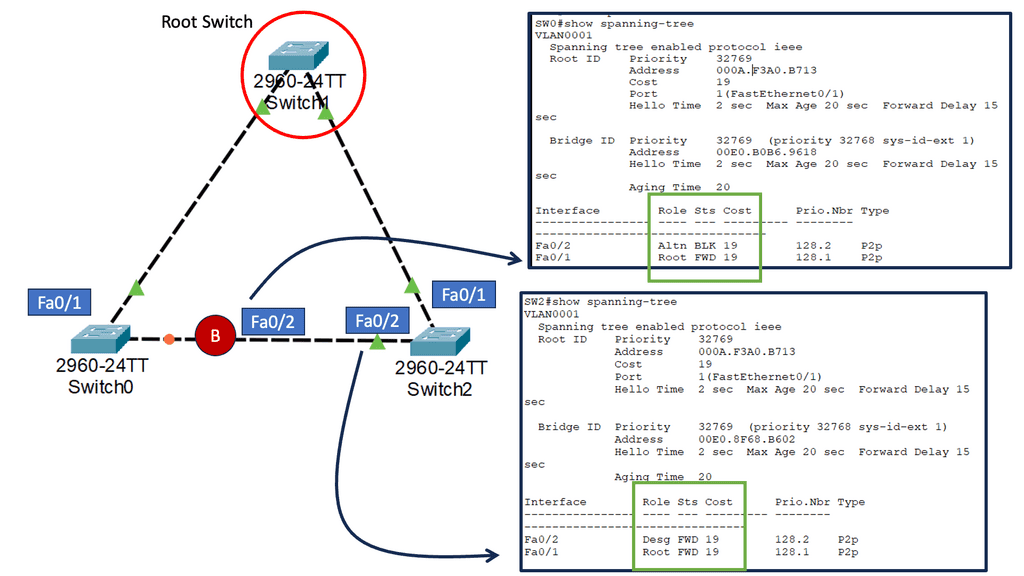
Spanning Tree Root Switch stp port states


The IP Address Is Not a Valid Hook

We should know that IP addresses are lost in today’s hybrid environment. SDP provides a connection-based security architecture instead of an IP-based one. This allows for many things. For one, security policies follow the user regardless of location. Let’s say you are doing forensics on an event 12 months ago for a specific IP.

However, that IP address is a component in a test DevOps environment. Do you care? Anything tied to IP is ridiculous, as we don’t have the right hook to hang things on for security policy enforcement.

Example – Firewalling based on Tags & Labels
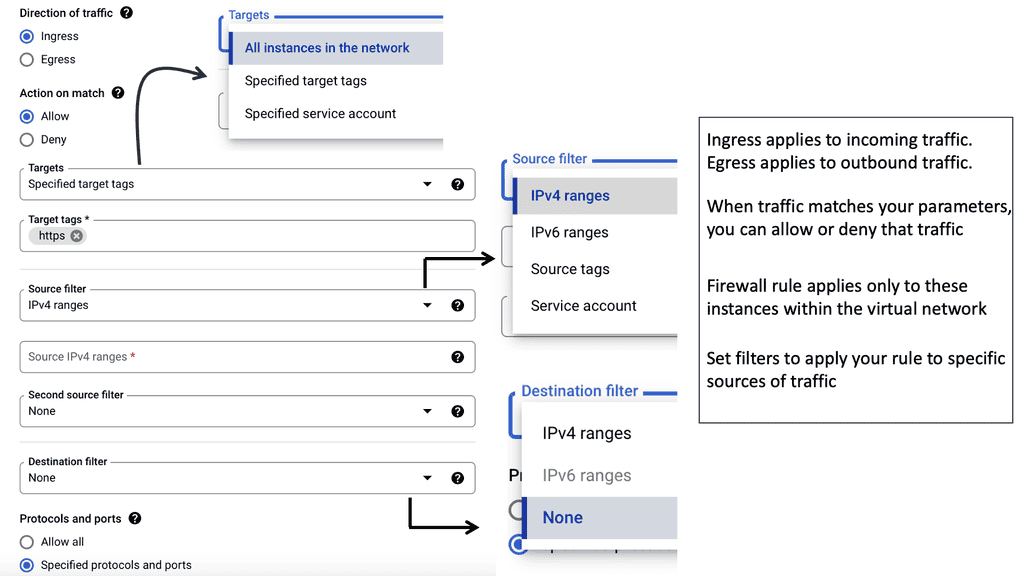
Firewall tags

Software-defined perimeter; Identity-driven access

Identity-driven network access control is more precise in measuring the actual security posture of the endpoint. Access policies tied to IP addresses cannot offer identity-focused security. SDP enables the control of all connections based on pre-vetting who can connect and to what services.

If you do not meet this level of trust, you can’t, for example, access the database server, but you can access public-facing documents. Users are granted access only to authorized assets, preventing lateral movements that will probably go unnoticed when traditional security mechanisms are in place.

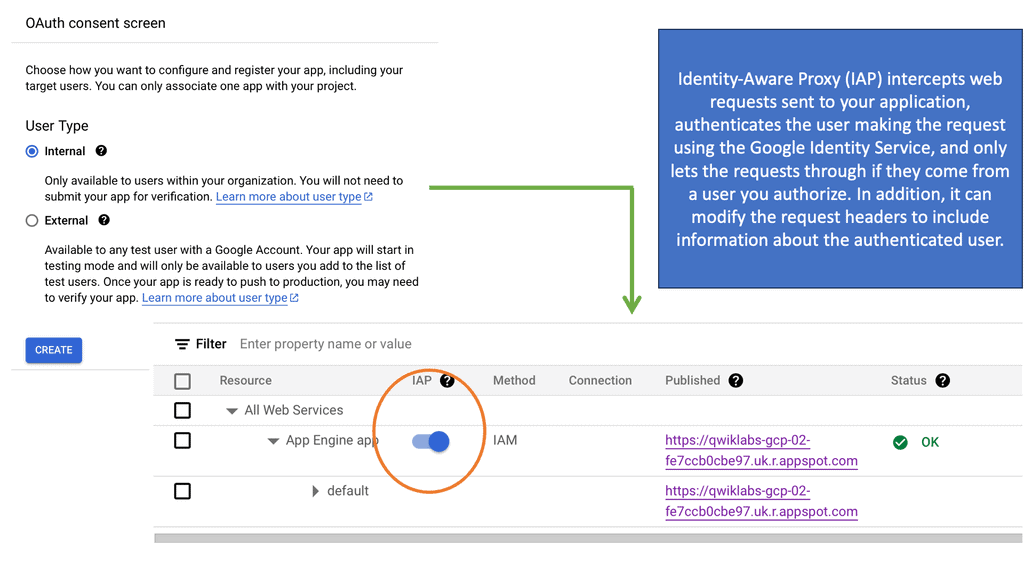
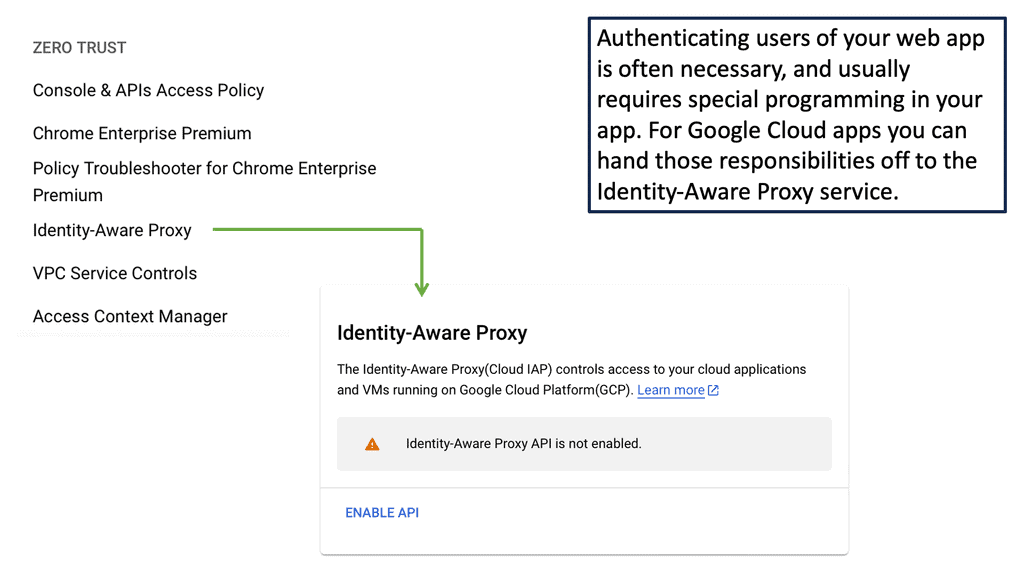
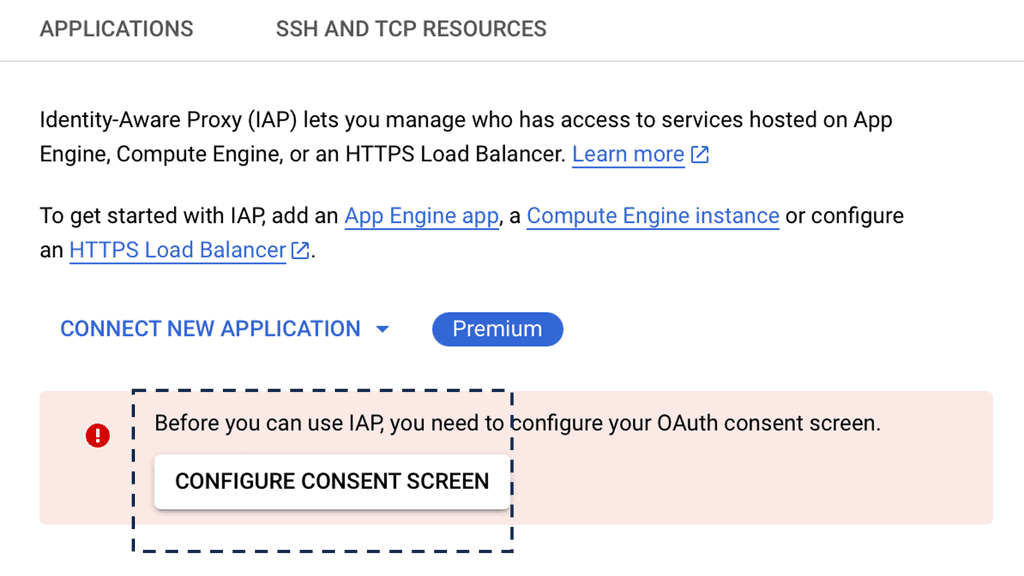
Example Technology: IAP in Google Cloud

### How IAP Works

IAP functions by intercepting user requests before they reach the application. It verifies the user’s identity and context, allowing access only if the user’s credentials match the predefined security policies. This process involves authentication through Google Identity Platform, which leverages OAuth 2.0, OpenID Connect, and other standards to confirm user identity efficiently. Once authenticated, IAP evaluates the context, such as the user’s location or device, to further refine access permissions.
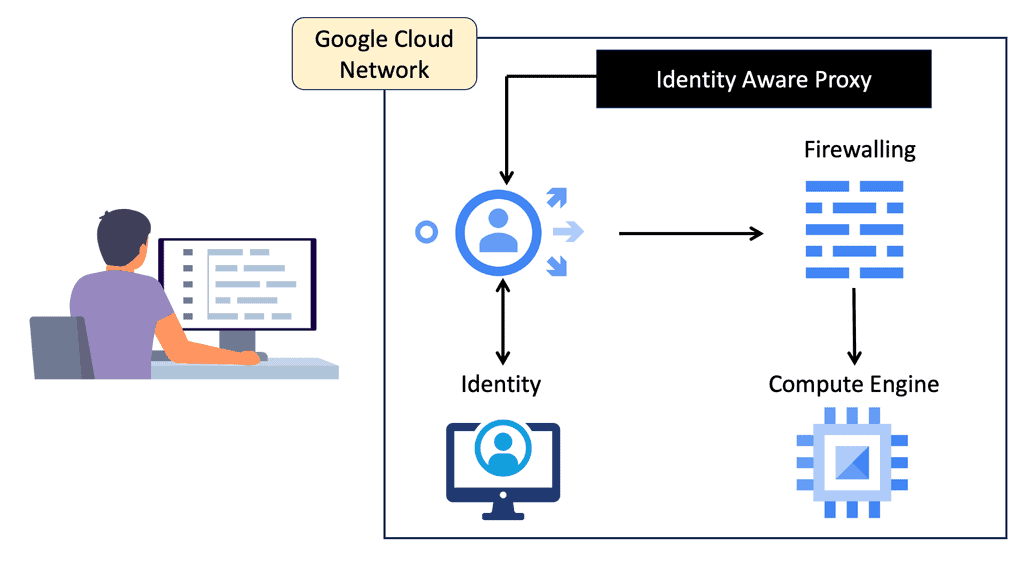
### Benefits of Using IAP on Google Cloud

Implementing IAP on Google Cloud offers several compelling benefits. First, it enhances security by centralizing access control, reducing the risk of unauthorized entry. Additionally, IAP simplifies the user experience by eliminating the need for multiple login credentials across different applications. It also supports granular access control, allowing organizations to tailor permissions based on user roles and contexts, thereby improving operational efficiency.

### Setting Up IAP on Google Cloud

Setting up IAP on Google Cloud is a straightforward process. Administrators begin by enabling IAP in the Google Cloud Console. Once activated, they can configure access policies, determining who can access which resources and under what conditions. The system’s flexibility allows administrators to integrate IAP with various identity providers, ensuring compatibility with existing authentication frameworks. Comprehensive documentation and support from Google Cloud further streamline the setup process.
Identity aware proxy

Information & Infrastructure Hiding 

SDP does a great job of hiding information and infrastructure. The SDP architectural components ( the SDP controller and gateways ) are “dark, ” providing resilience against high- and low-volume DDoS attacks. A low-bandwidth DDoS attack may often bypass traditional DDoS security controls. However, the SDP components do not respond to connections until the requesting clients are authenticated and authorized, allowing only good packets through.

A suitable security protocol for this is single packet authorization (SPA). Single Packet Authorization, or Authentication, gives the SDP components a default “deny-all” security posture.

The “default deny” can be achieved because if an accepting host receives any packet other than a valid SPA packet, it assumes it is malicious. The packet will get dropped, and a notification will not get sent back to the requesting host. This stops the survey at the door, silently detecting and dropping bad packets.

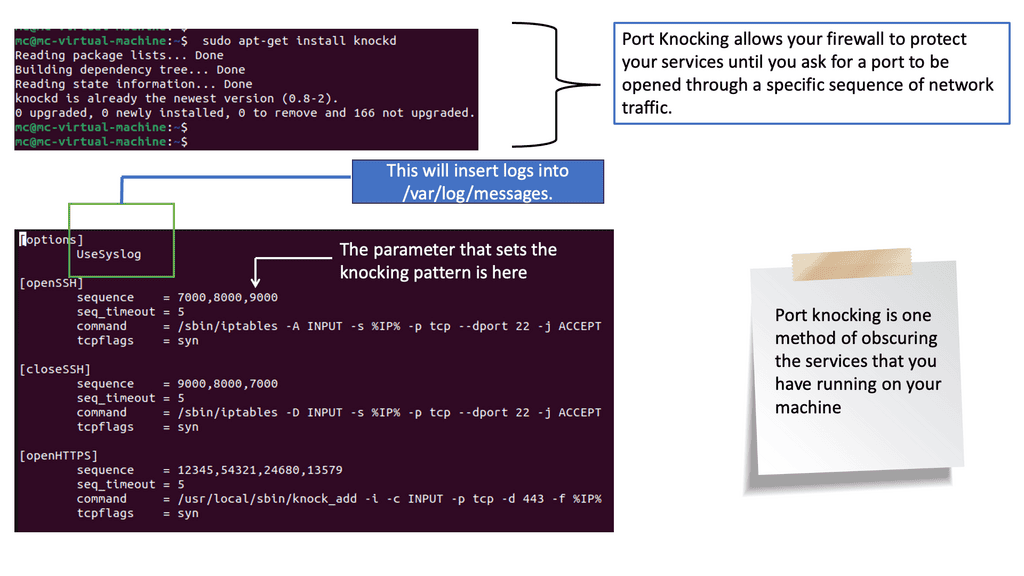
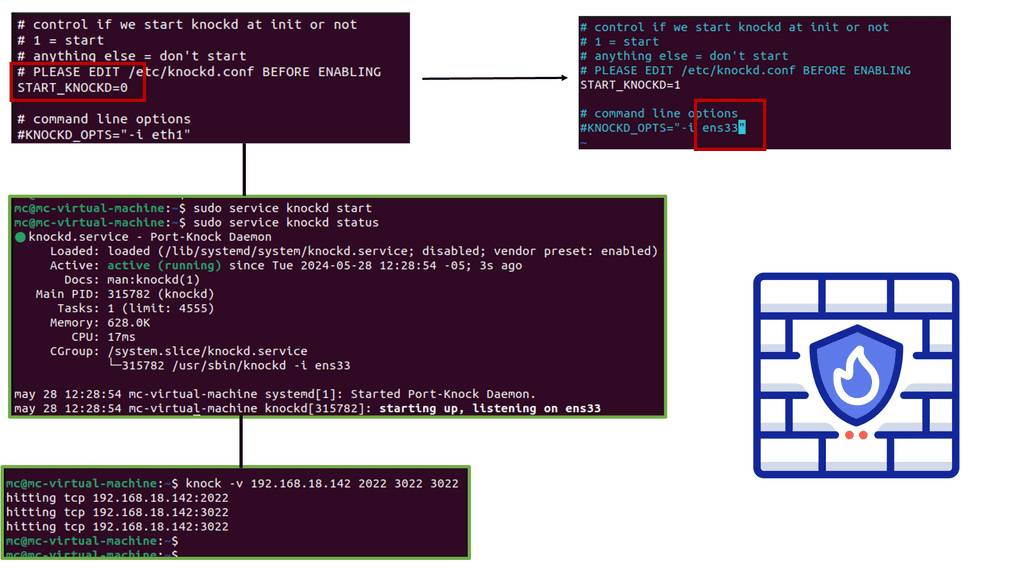
What is Port Knocking?

– Port knocking is a security technique that involves sequentially probing a predefined sequence of closed ports on a network to establish a connection with a desired service. It acts as a virtual secret handshake, allowing users to access specific services or ports that would otherwise remain hidden or blocked from unauthorized access.

– Port knocking typically involves sending connection attempts to a series of ports in a specific order, which serves as a secret code. Once a listening daemon or firewall detects the correct sequence, it dynamically opens the desired port and allows the connection. This stealthy approach helps to prevent unauthorized access and adds an extra layer of security to network services.
Sniffing a SPA packet

However, SPA can be subject to Man-In-The-Middle (MITM) attacks. If a bad actor can sniff an SPA packet, they can establish the TCP connection to the controller or AH client. However, there is another level of defense: the bad actor cannot complete the mutually encrypted connection (mTLS) without the client’s certificate.

SDP brings in the concept of mutually encrypted connections, also known as two-way encryption. The usual configuration for TLS is that the client authenticates the server, but TLS ensures that both parties are authenticated. Only validated devices and users can become authorized members of the SDP architecture.

We should also remember that the SPA is not a security feature that can be implemented to protect all. It has its benefits but does not take over from existing security technologies. SPA should work alongside them. The main reason for its introduction to the SDP world is to overcome the problems with TCP. TCP connects and then authenticates. With SPA, you authenticate first and then connect only then.
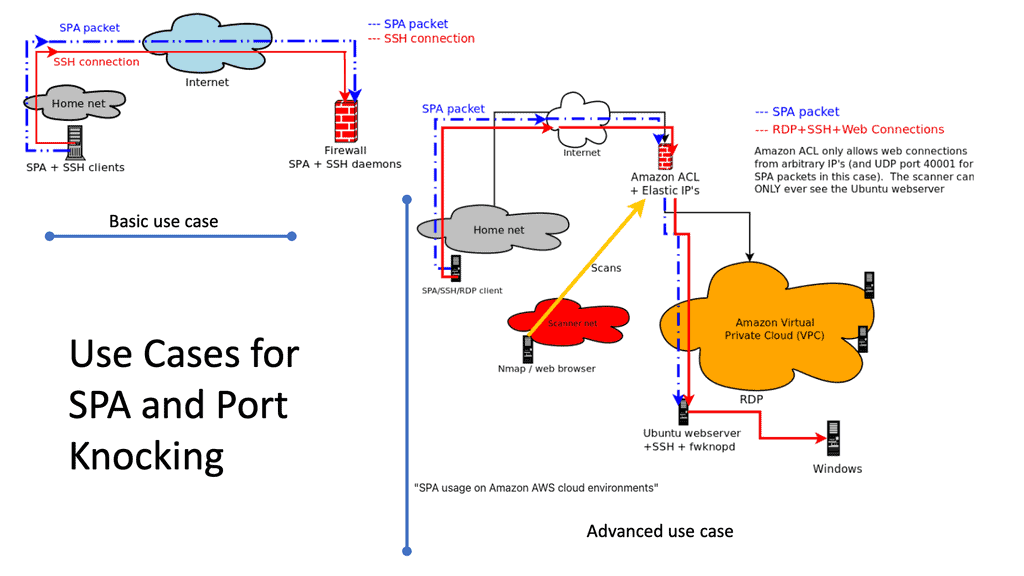
 

SPA Use Case
Diagram: SPA Use Case. Source mrash Github.

**The World of TCP & SDP**

When clients want to access an application with TCP, they must first set up a connection. There needs to be direct connectivity between the client and the application. So, this requires the application to be reachable and is carried out with IP addresses on each end. Then, once the connect stage is done, there is an authentication phase.

Once the authentication stage is completed, we can pass data. Therefore, we must connect, authenticate, and pass data through a stage. SDP reverses this.

The center of the software-defined perimeter is trust.

In Software-Defined Perimeter, we must establish trust between the client and the application before the client can set up the connection. The trust is bi-directional between the client and the SDP service and the application to the SDP service. Once trust has been established, we move into the next stage, authentication.

Once this has been established, we can connect the user to the application. This flips the entire security model and makes it more robust. The user has no idea of where the applications are located. The protected assets are hidden behind the SDP service, which in most cases is the SDP gateway, or some call this a connector.

Cloud Security Alliance (CSA) SDP

    • With the Cloud Security Alliance SDP architecture, we have several components:

Firstly, the IH & AH are the clients initiating hosts (IH) and the service accepting hosts (AH). The IH devices can be any endpoint device that can run the SDP software, including user-facing laptops and smartphones. Many SDP vendors have remote browser isolation-based solutions without SDP client software. The IH, as you might expect, initiates the connections.

With an SDP browser-based solution, the user accesses the applications using a web browser and only works with applications that can speak across a browser. So, it doesn’t give you the full range of TCP and UDP ports, but you can do many things that speak natively across HTML5.

Most browser-based solutions don’t require additional security posture checks to assess the end-user device rather than an endpoint with the client installed.

Software-Defined Perimeter: Browser-based solution

The AHs accept connections from the IHS and provide a set of services protected securely by the SDP service. They are under the administrative control of the enterprise domain. They do not acknowledge communication from any other host and will not respond to non-provisioned requests. This architecture enables the control plane to remain separate from the data plane, achieving a scalable security system.

The IH and AH devices connect to an SDP controller that secures access to isolated assets by ensuring that the users and their devices are authenticated and authorized before granting network access. After authenticating an IH, the SDP controller determines the list of AHs to which the IH is authorized to communicate. The AHs are then sent a list of IHs that should accept connections.

Aside from the hosts and the controller, we have the SDP gateway component, which provides authorized users and devices access to protected processes and services. The protected assets are located behind the gateway and can be architecturally positioned in multiple locations, such as the cloud or on-premise. The gateways can exist in various locations simultaneously.

**Highlighting Dynamic Tunnelling**

A user with multiple tunnels to multiple gateways is expected in the real world. It’s not a static path or a one-to-one relationship but a user-to-application relationship. The applications can exist everywhere, and the tunnel is dynamic and ephemeral.

For a client to connect to the gateway, latency or SYN SYN/ACK RTT testing should be performed to determine the Internet links’ performance. This ensures that the application access path always uses the best gateway, improving application performance.

Remember that the gateway only connects outbound on TCP port 443 (mTLS), and as it acts on behalf of the internal applications, it needs access to the internal apps. As a result, depending on where you position the gateway, either internal to the LAN, private virtual private cloud (VPC), or in the DMZ protected by local firewalls, ports may need to be opened on the existing firewall.

**Future of Software-Defined Perimeter**

As the digital landscape evolves, secure network access becomes even more crucial. The future of SDP looks promising, with advancements in technologies like Artificial Intelligence and Machine Learning enabling more intelligent threat detection and mitigation.

In an era where data breaches are a constant threat, organizations must stay ahead of cybercriminals by adopting advanced security measures. Software Defined Perimeter offers a robust, scalable, and dynamic security framework that ensures secure access to critical resources.

By embracing SDP, organizations can significantly reduce their attack surface, enhance network performance, and protect sensitive data from unauthorized access. The time to leverage the power of Software Defined Perimeter is now.

Closing Points on SDP

At its core, a Software Defined Perimeter is a security framework designed to protect networked applications by concealing them from external users. Unlike traditional security measures that rely on a perimeter-based approach, SDP focuses on identity-based access controls. This means that users must be authenticated and authorized before they can even see the resources they’re trying to access. By effectively creating a “black cloud,” SDP ensures that only legitimate users can interact with the network, significantly reducing the risk of unauthorized access.

The operation of an SDP is based on a simple yet powerful principle: “Verify first, connect later.” It employs a multi-step process that involves:

1. **User Authentication**: Before any connection is established, SDP verifies the identity of the user or device attempting to connect.

2. **Access Validation**: Once authenticated, the system checks the user’s permissions and determines whether access should be granted.

3. **Dynamic Environment**: SDP dynamically provisions network connections, ensuring that only the necessary resources are exposed to the user.

This approach not only minimizes the attack surface but also adapts to the changing needs of the network, providing a flexible and scalable security solution.

The implementation of a Software Defined Perimeter offers numerous benefits:

– **Enhanced Security**: By hiding network resources and requiring stringent authentication, SDP provides a robust defense against cyber threats.

– **Reduced Attack Surface**: SDP ensures that only authorized individuals have access to specific resources, significantly reducing potential vulnerabilities.

– **Scalability and Flexibility**: As organizations grow, SDP can easily scale to meet their expanding security needs without requiring substantial changes to the existing infrastructure.

– **Improved User Experience**: With its streamlined access process, SDP can improve the overall user experience by reducing the friction often associated with security measures.
Interactive Connection Lab

SDP Connection & Dynamic Tunnel Lab

Explore the SDP sequence: verify identity and context first, authorize the requested application, select an appropriate gateway, then establish a protected connection.

Verify First Request received
→
Authenticate Identity verified
→
Authorize Policy evaluated
→
Connect Later Gateway selected
→
mTLS Tunnel Protected channel
→
Application Authorized access

Connection request

Configure the request and test whether a controlled tunnel can be established.

Dynamic gateway selection

Lower measured RTT can make a gateway more attractive, provided policy authorization succeeds. This is an illustrative model, not a production gateway-selection algorithm.

Gateway A London · 24 ms
Gateway B Dublin · 11 ms
Gateway C Frankfurt · 31 ms
— Selected RTT
— Authentication
— Tunnel
Connection result
NOT CONNECTED
Verify the request before establishing the tunnel.
[READY] SDP connection engine initialized
[INFO] No application connection established
[INFO] Verify identity and policy before selecting a gateway
Engineering takeaway: “Verify first, connect later” separates the access decision from the network connection. A user can be authenticated without automatically receiving broad network access. After authorization, the implementation can establish a protected connection to the specific application or service that policy permits.
Cyber security threat. Young woman using computer and coding. Internet and network security. Stealing private information. Person using technology to steal password and private data. Cyber attack crime

SDP Network

SDP Network

The world of networking has undergone a significant transformation with the advent of Software-Defined Perimeter (SDP) networks. These innovative networks have revolutionized connectivity by providing enhanced security, flexibility, and scalability. In this blog post, we will explore the key features and benefits of SDP networks, their impact on traditional networking models, and the future potential they hold.

SDP networks, also known as "Black Clouds," are a paradigm shift in how we approach network security. Unlike traditional networks that rely on perimeter-based security, SDP networks adopt a "Zero Trust" model. This means that every user and device is treated as untrusted until verified, reducing the attack surface and enhancing security.
<br one="" of="" the="" standout="" features="" sdp="" networks="" is="" their="" ability="" to="" provide="" granular="" access="" control.="" by="" authenticating="" users="" and="" devices="" before="" granting="" access,="" organizations="" can="" ensure="" that="" only="" authorized="" entities="" connect="" network.="" this="" eliminates="" risk="" unauthorized="" minimizes="" potential="" for="" data="" breaches.

Another benefit of SDP networks is their flexibility. These networks are not tied to physical locations, allowing users to securely connect from anywhere in the world. This is especially beneficial for remote workers, as it enables them to access critical resources without compromising security.

SDP networks challenge the traditional hub-and-spoke networking model by introducing a decentralized approach. Instead of relying on a central point of entry, SDP networks establish direct connections between users and resources. This reduces latency, improves performance, and enhances the overall user experience.

As technology continues to evolve, the future of SDP networks looks promising. The rise of Internet of Things (IoT) devices and the increasing reliance on cloud-based services necessitate a more secure and scalable networking solution. SDP networks offer precisely that, with their ability to adapt to changing network demands and provide robust security measures.
SDP networks have emerged as a game-changer in the world of connectivity. By focusing on security, flexibility, and scalability, they address the limitations of traditional networking models. As organizations strive to protect their valuable data and adapt to evolving technological landscapes, SDP networks offer a reliable and future-proof solution.

SDP NETWORK • IDENTITY-CENTRIC ACCESS

SDP Identity-Centric Access Lab

Explore how a Software-Defined Perimeter can evaluate identity, device posture, application context and risk before establishing access to a protected resource.

Scenario: A remote employee requests access to a protected Finance application. The application should not be treated as reachable simply because the user knows its address. The SDP access layer evaluates the request first.
Access Request POLICY INPUT
SDP Decision Engine DYNAMIC POLICY
TRUST / ACCESS SCORE
Illustrative learning model
—
Final Decision
AWAITING EVALUATION
Configure the request and run the SDP policy evaluation.
SDP Access Flow
REQUEST
IDENTITY
DEVICE + RISK
POLICY
APPLICATION
Decision Trace
[SDP] Waiting for access request...
[SDP] Protected application is not treated as broadly reachable.
[SDP] Identity and context will be evaluated before access is established.
Engineering Takeaway

SDP shifts the access decision away from simple network location or IP address and toward identity, device posture, application context and policy. Authentication establishes who or what is requesting access; authorization determines what that identity is permitted to reach. A successful identity check therefore does not automatically provide broad network access.

Highlights: SDP Network

**The Core Principles of SDP Networks**

At the heart of an SDP network are three core principles: identity-based access, dynamic provisioning, and the principle of least privilege. Identity-based access ensures that only authenticated users can access the network, a significant shift from traditional models that rely on IP addresses. Dynamic provisioning allows the network to adapt in real-time, creating secure connections only when necessary, thus reducing the attack surface. Lastly, the principle of least privilege ensures that users receive only the access necessary to perform their tasks, minimizing potential security risks.

**How SDP Networks Work**

SDP networks function by utilizing a multi-stage process to verify user identity and device health before granting access. The process begins with an initial trust assessment where users are authenticated through a secure channel. Once authenticated, the user’s device undergoes a health check to ensure it meets security requirements. Following this, access is granted on a need-to-know basis, with micro-segmentation techniques used to isolate resources and prevent lateral movement within the network. This layered approach significantly enhances network security by ensuring that only verified users gain access to the resources they need.

Black Clouds – SDP

SDP networks, also known as ” Black Clouds,” represent a paradigm shift in network security. Unlike traditional perimeter-based security models, SDP networks focus on dynamically creating individualized perimeters around each user, device, or application. By adopting a Zero-Trust approach, SDP networks ensure that only authorized entities can access resources, reducing the attack surface and enhancing overall security.

SDP networks are a paradigm shift in network security. Unlike traditional perimeter-based approaches, SDP networks adopt a zero-trust model, where every user and device must be authenticated and authorized before accessing resources. This eliminates the vulnerabilities of a static perimeter and ensures secure access from anywhere.

SDP Network and Identity‑Centric Access Control

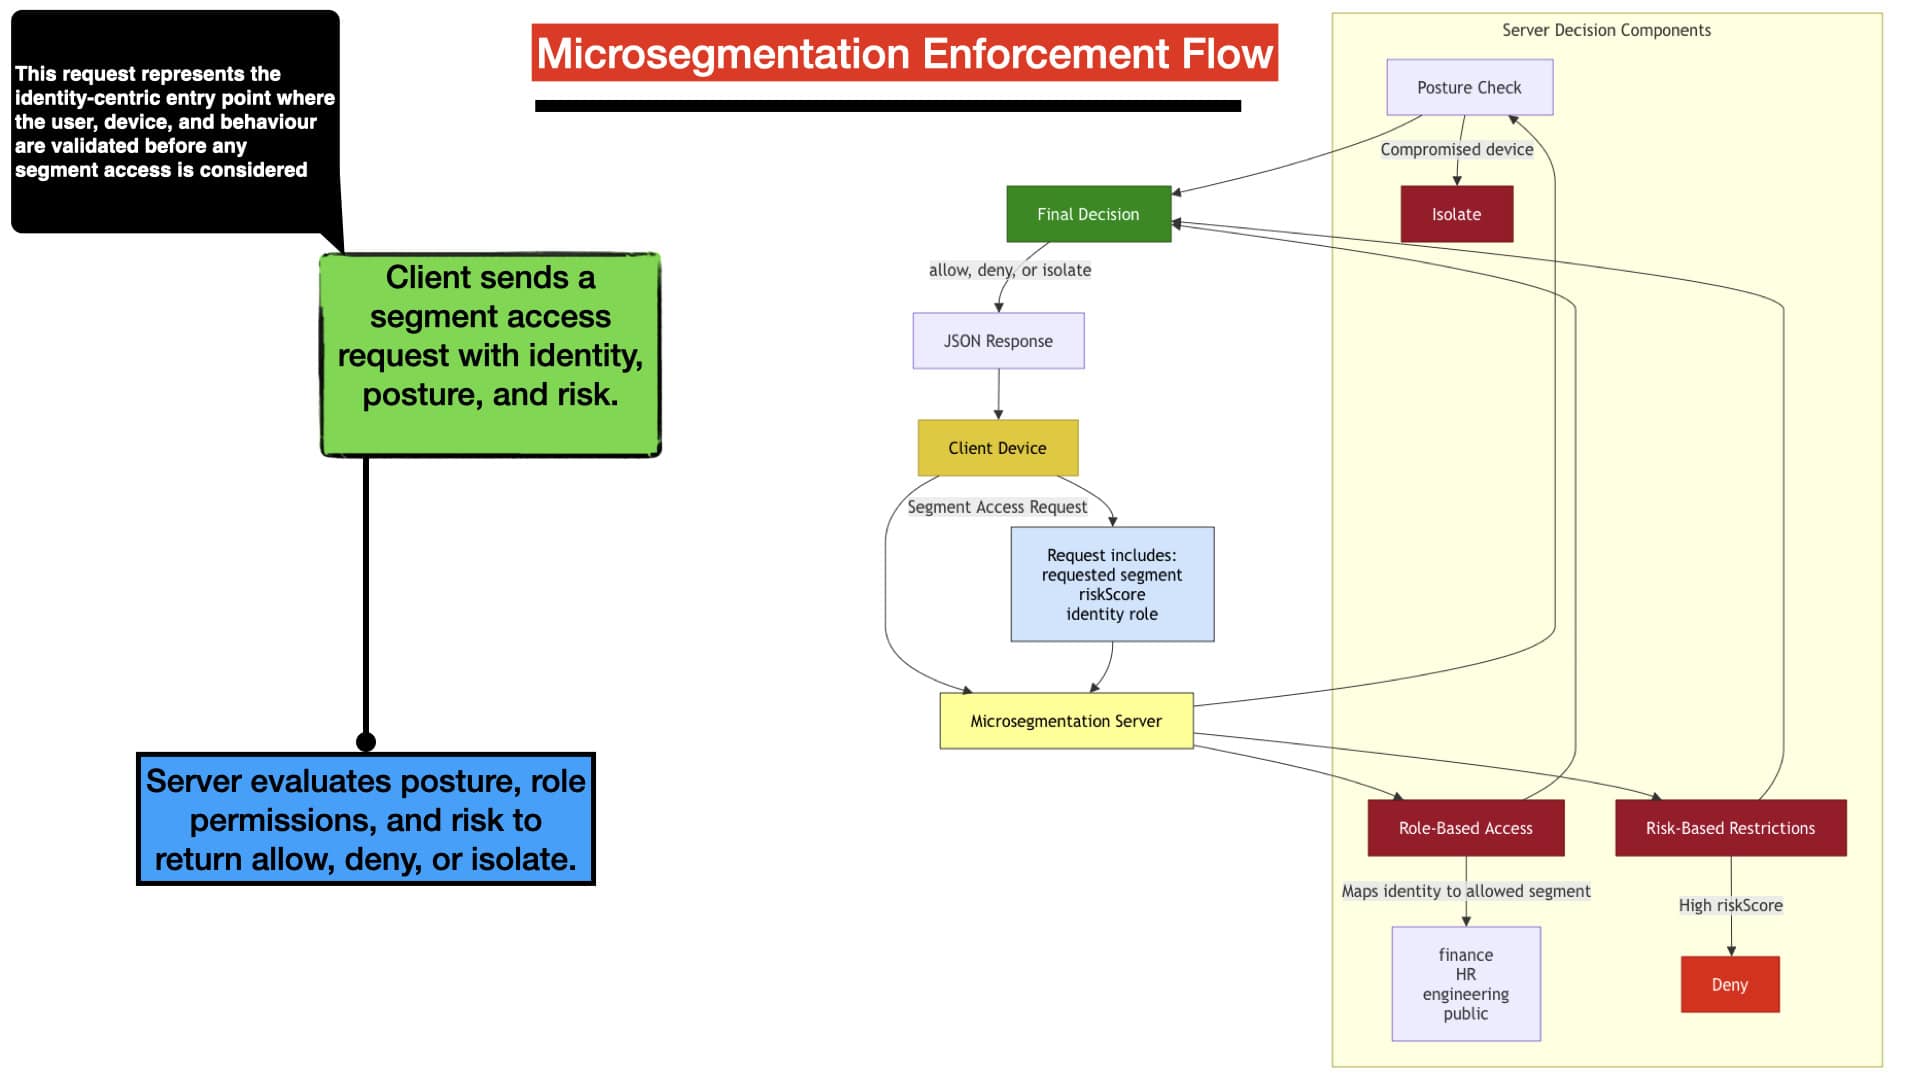
This lab demonstrates how an SDP Network enforces identity‑centric access by validating every request before any connection is established. Instead of exposing applications directly, the SDP Network model evaluates identity role, device posture, and behavioural risk to determine whether a session should be permitted. By applying these checks at the access layer, learners see how an SDP Network hides services behind a Zero Trust fabric and only reveals them once identity and posture have been fully verified.

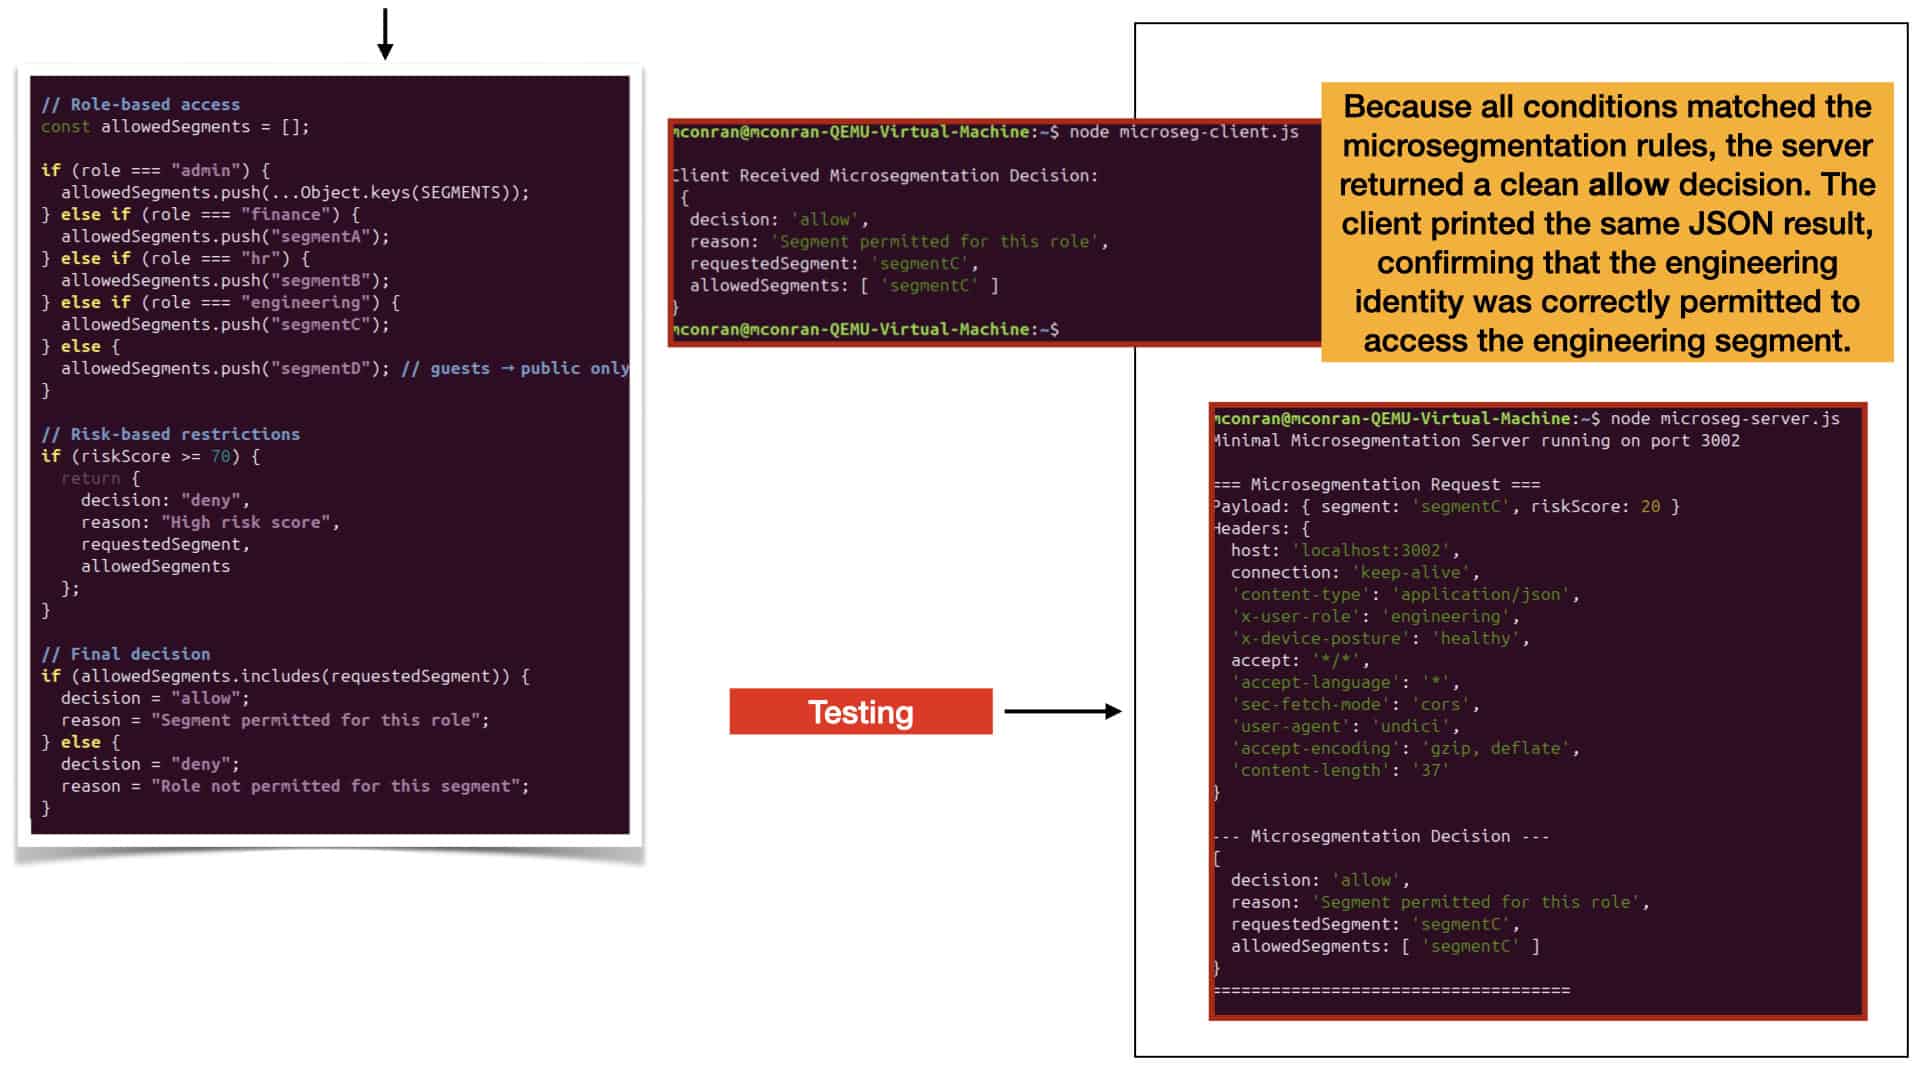
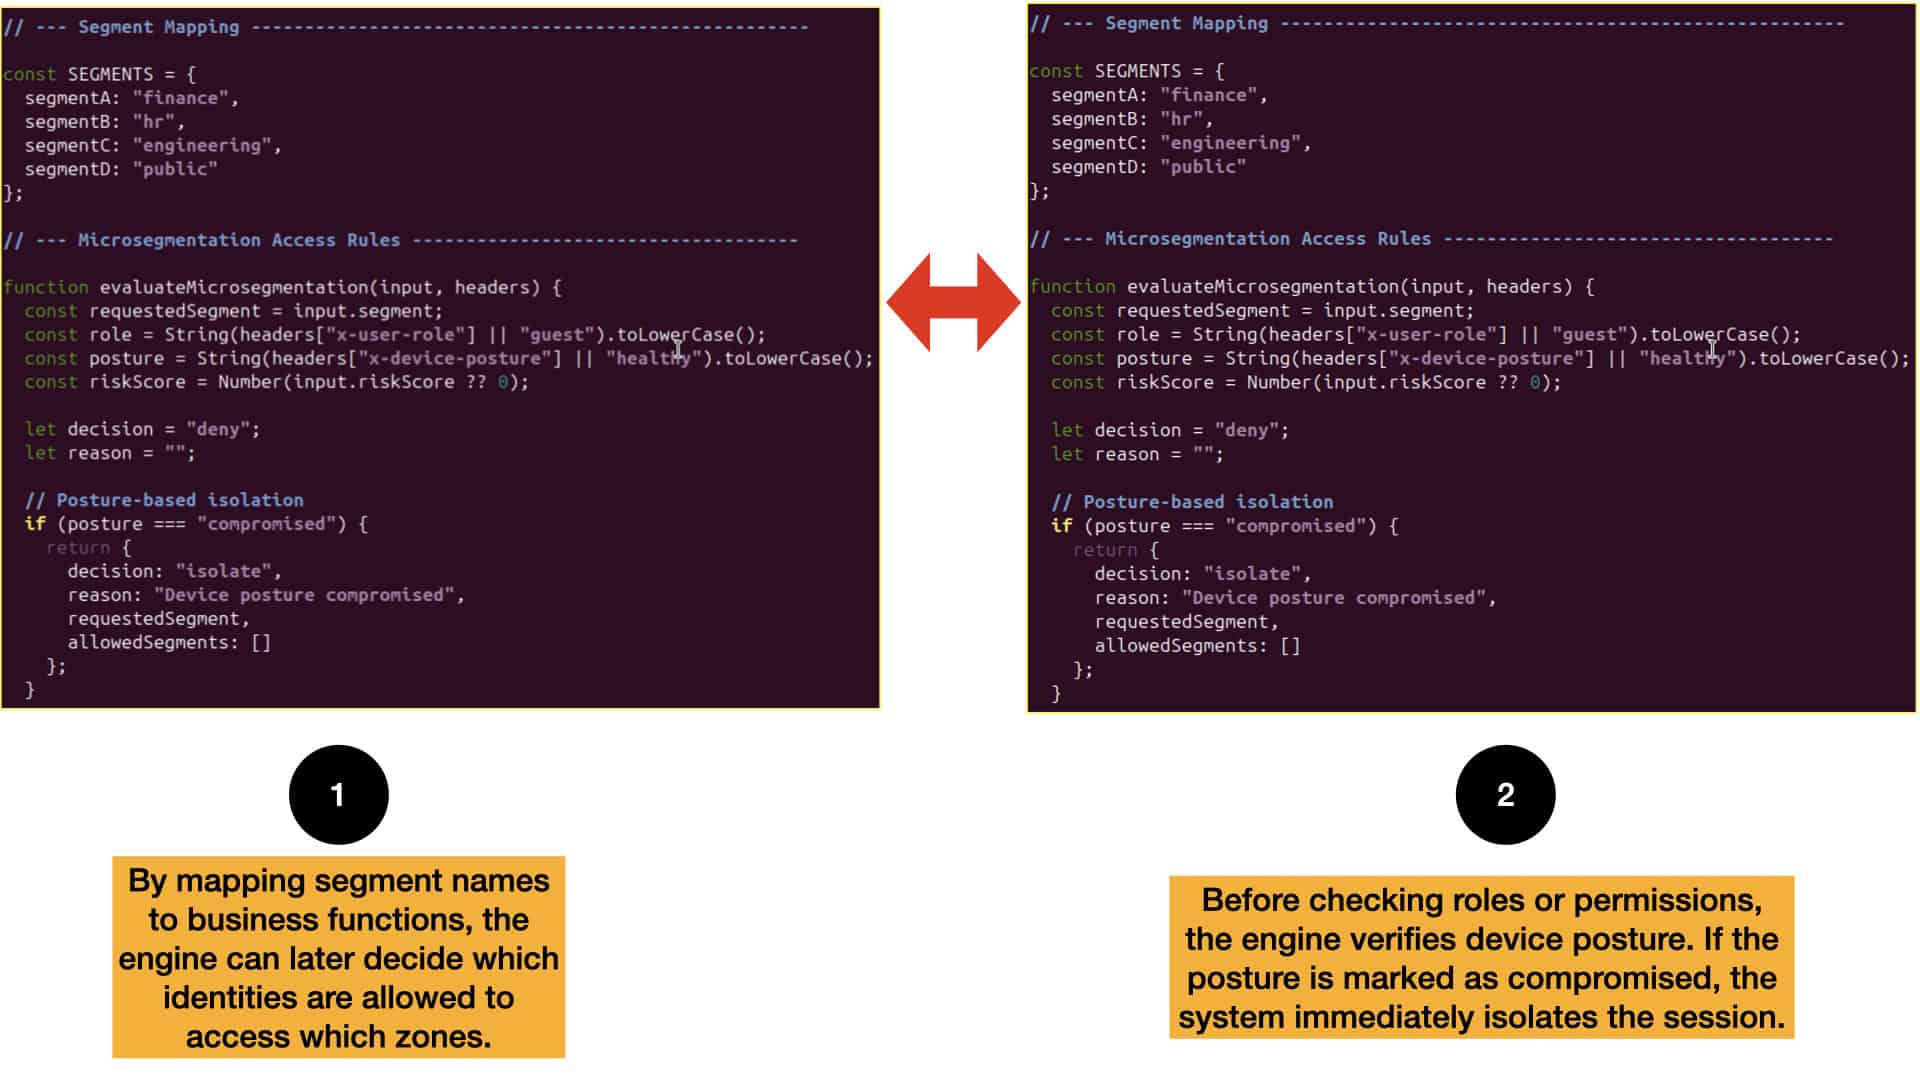
micro segmentation

When the server receives a segment access request, it applies SDP Network rules that combine identity permissions, posture validation, and risk scoring. Each identity role is mapped to specific hidden segments, while compromised posture or high risk immediately restricts access. Because the test payload represents a healthy device, low risk, and a role aligned with the requested segment, the SDP Network engine returns an allow decision. This shows how SDP Network architectures use dynamic, identity‑driven enforcement to prevent lateral movement and unauthorized access.

The lab provides full visibility into how an SDP Network evaluates and enforces access. The server logs the payload, identity headers, posture signals, risk score, and final decision, while the client displays the JSON response returned by the engine. This end‑to‑end flow illustrates how an SDP Network merges identity validation, posture assessment, and behavioural analytics into a unified Zero Trust access path. With this foundation, learners can expand into advanced SDP topics such as service cloaking, dynamic trust evaluation, and identity‑aware microsegmentation.


Benefits of Software-Defined Perimeter:

1. Enhanced Security: SDP provides an additional layer of security by ensuring that only authenticated and authorized users can access the network. By implementing granular access controls, SDP reduces the attack surface and minimizes the risk of unauthorized access, making it significantly harder for cybercriminals to breach the system.

2. Improved Flexibility: Traditional network architectures often struggle to accommodate the increasing number of devices and the demand for remote access. SDP enables businesses to scale their network infrastructure effortlessly, allowing seamless connectivity for employees, partners, and customers, regardless of location. This flexibility is precious in today’s remote work environment.

3. Simplified Network Management: SDP simplifies network management by centralizing access control policies. This centralized approach reduces complexity and streamlines granting and revoking access privileges. Additionally, SDP eliminates the need for VPNs and complex firewall rules, making network management more efficient and cost-effective.

4. Mitigated DDoS Attacks: Distributed Denial of Service (DDoS) attacks can cripple an organization’s network infrastructure, leading to significant downtime and financial losses. SDP mitigates the impact of DDoS attacks by dynamically rerouting traffic and preventing the attack from overwhelming the network. This proactive defense mechanism ensures that network resources remain available and accessible to legitimate users.

5. Compliance and Regulatory Requirements: Many industries are bound by strict regulatory requirements, such as healthcare (HIPAA) or finance (PCI-DSS). SDP helps organizations meet these requirements by providing a secure framework that ensures data privacy and protection. Implementing SDP can significantly simplify the compliance process and reduce the risk of non-compliance penalties.

SDP Network and Identity‑Centric Access

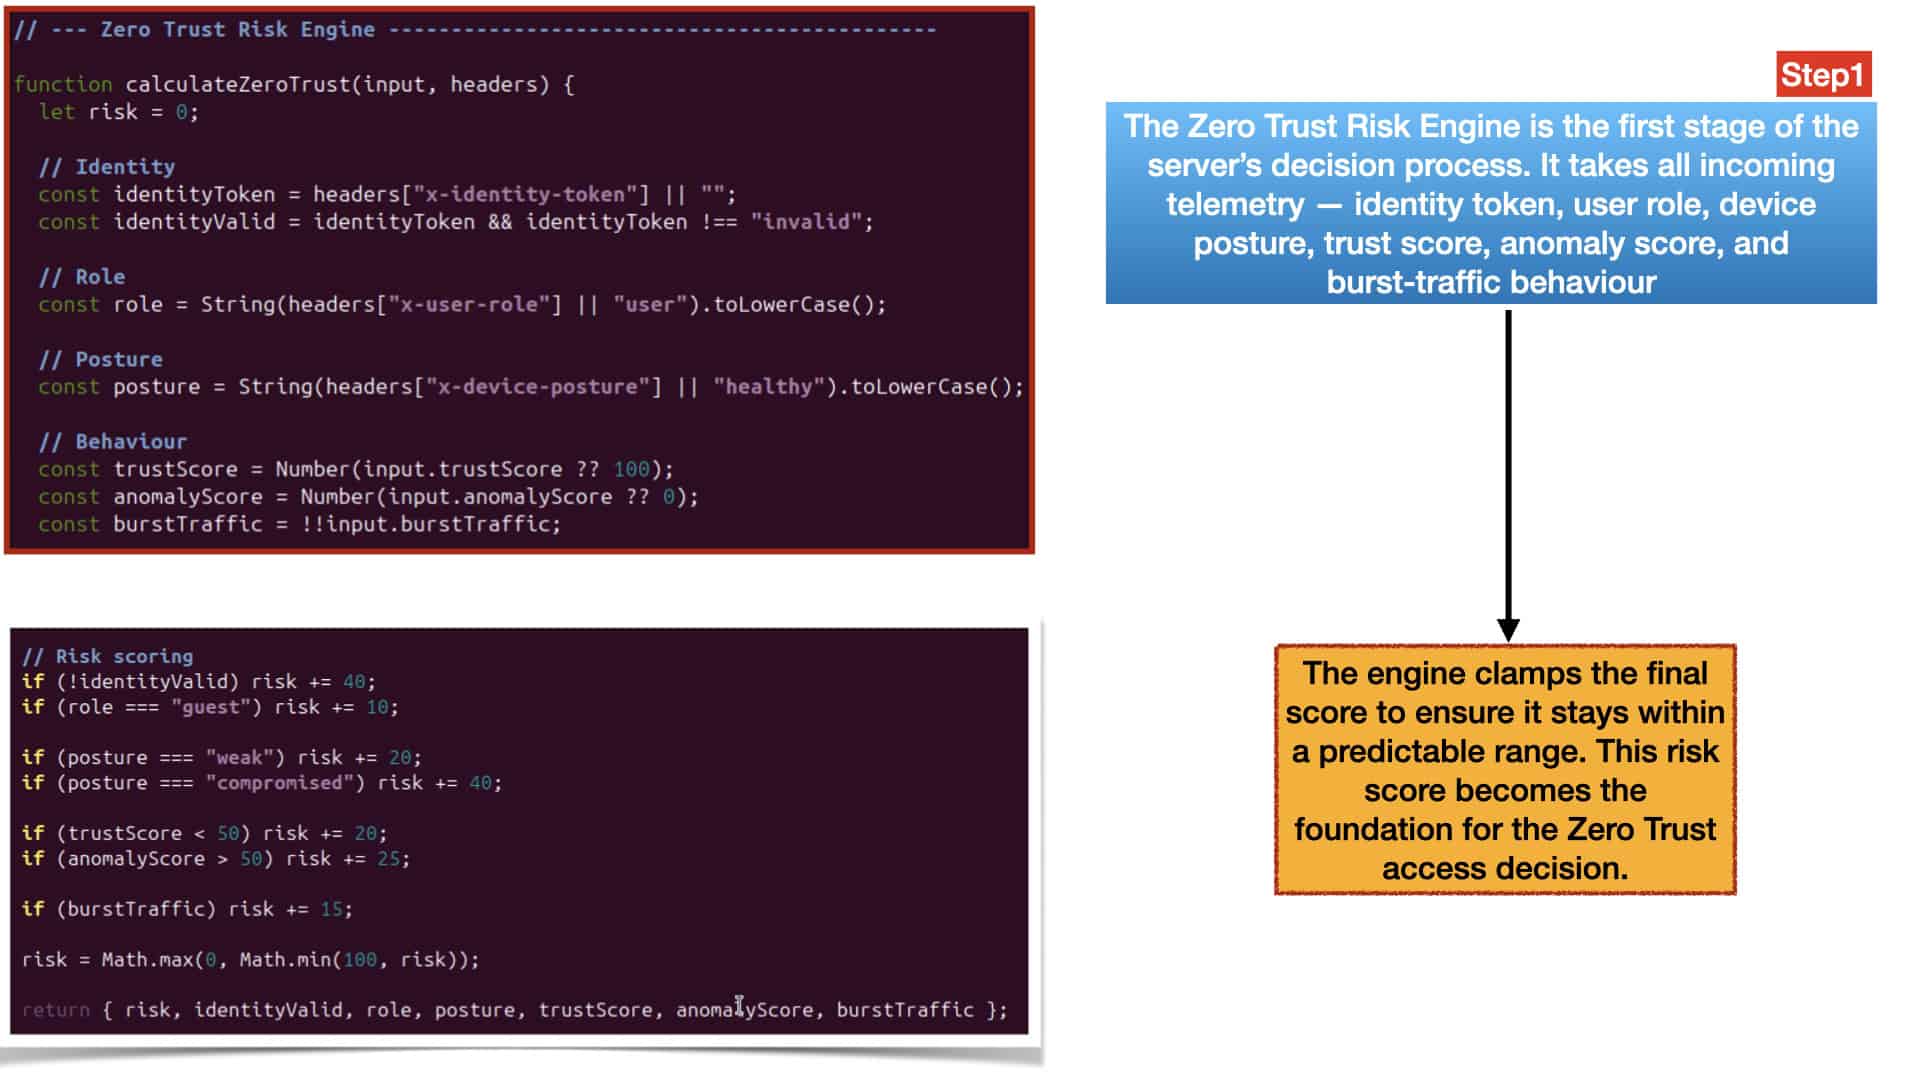
This lab demonstrates how an SDP Network enforces identity‑centric access by validating every request before allowing any connection to form. Instead of exposing services directly, the SDP Network model evaluates trustScore, anomalyScore, burst‑traffic behaviour, device posture, and identity tokens to determine whether a session should be permitted. This lightweight approach shows learners how an SDP Network hides applications behind a Zero Trust fabric, granting access only after identity and posture have been fully verified.

Unified Access and Steering

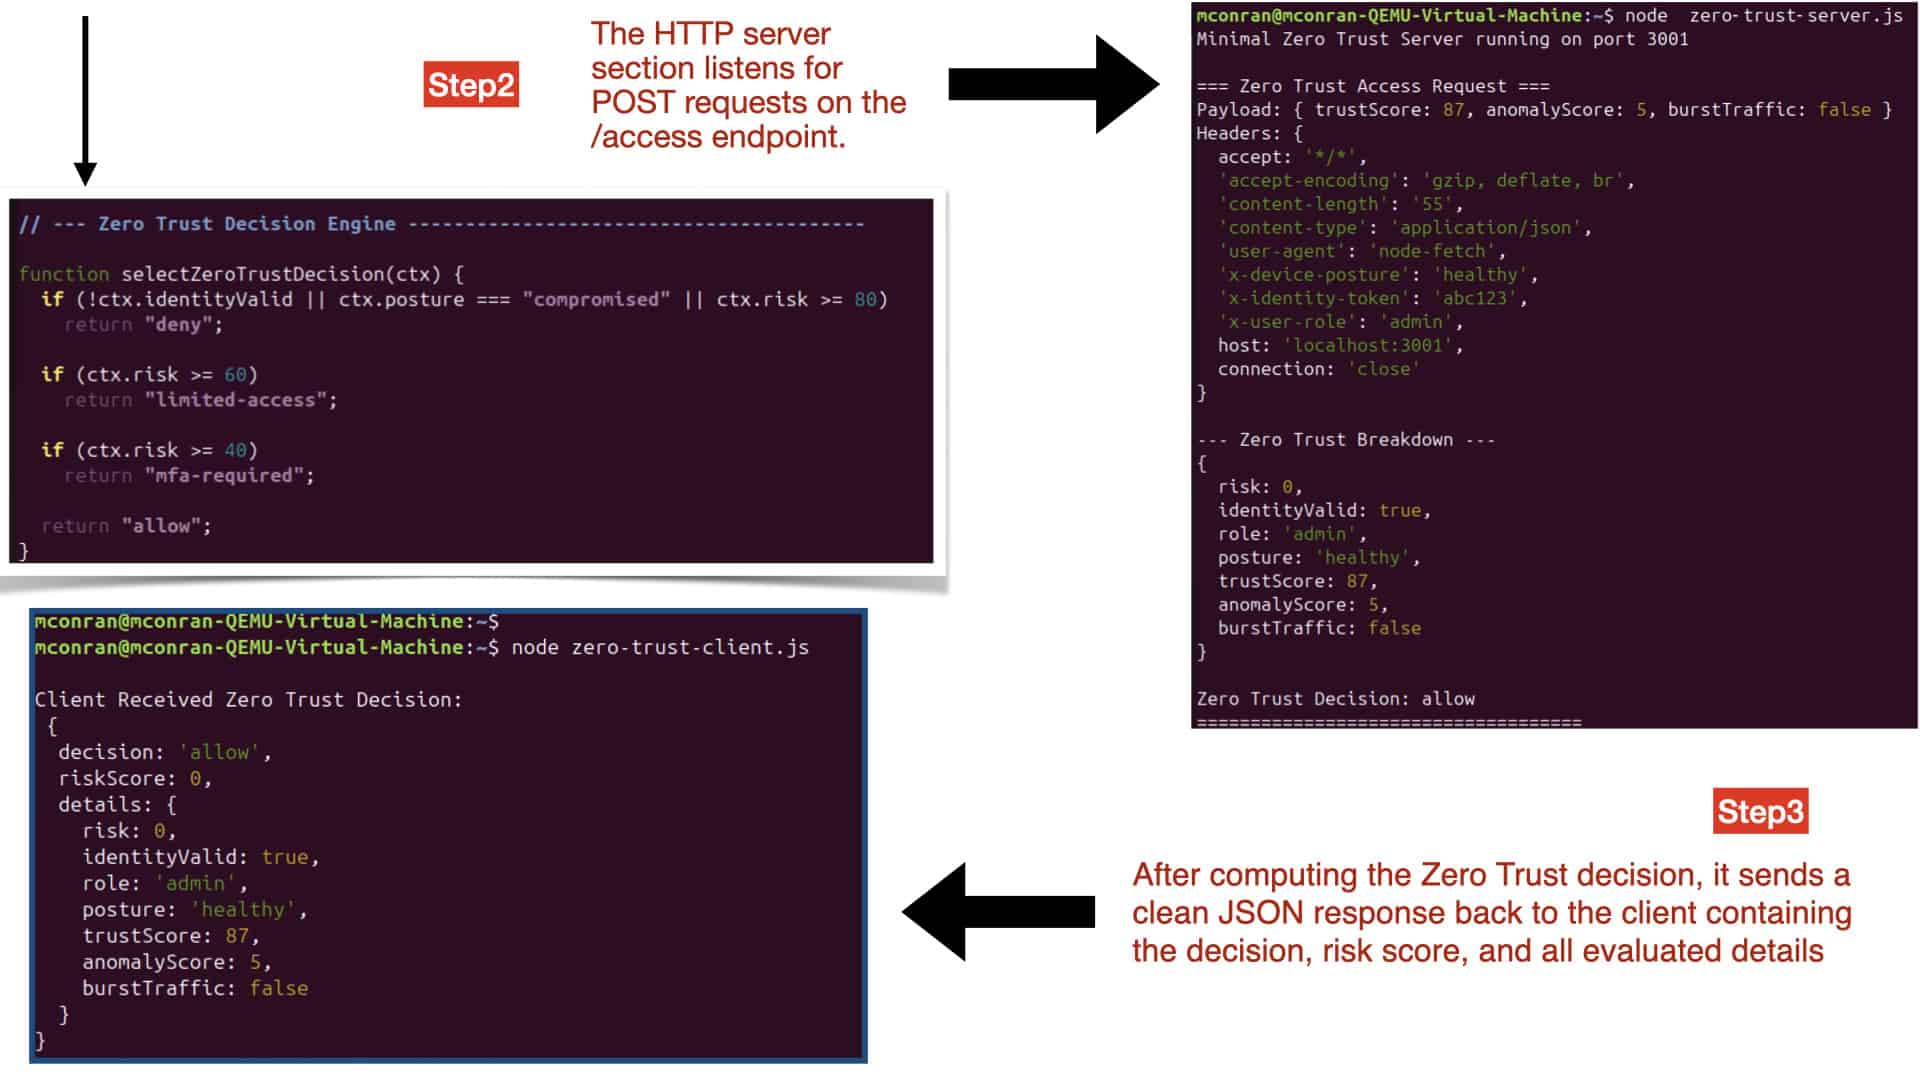
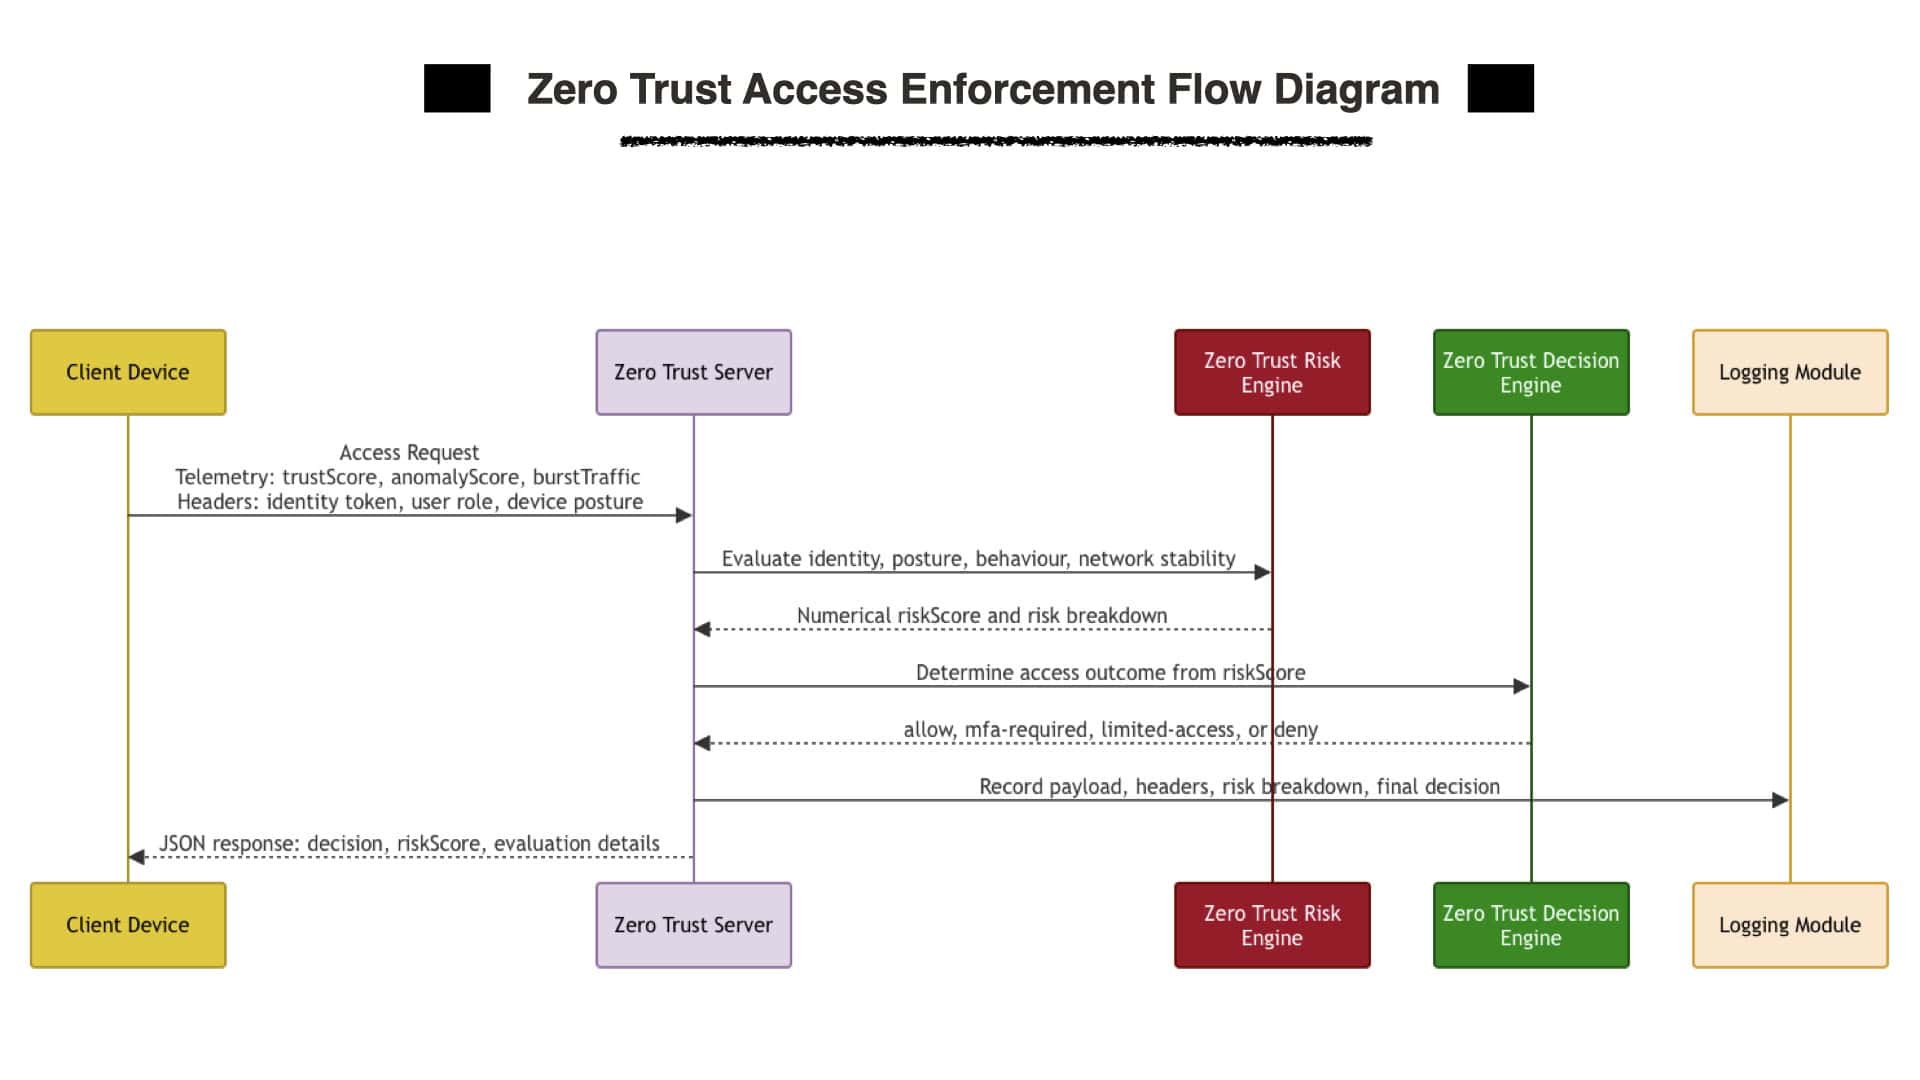
When the server receives a request, it applies SDP Network principles by calculating a risk score that reflects identity strength, posture health, and behavioural stability. This risk score drives the enforcement outcome, shifting the session between allow, MFA‑required, limited‑access, or deny. Because the test payload represents a trusted and stable session, the SDP Network engine returns an allow decision. This makes it easy for learners to see how SDP Network architectures use risk‑based access control to prevent lateral movement and unauthorized access.Zero Trust Engine

The lab provides full visibility into how an SDP Network evaluates and enforces access. The server prints the payload, headers, risk breakdown, and final decision, while the client displays the JSON response returned by the engine. This end‑to‑end flow illustrates how SDP Network design merges identity validation, posture assessment, and behavioural analytics into a unified access pipeline. With this foundation in place, learners can expand into microsegmentation, continuous authentication, and dynamic session re‑evaluation within an SDP Network environment.
Zero Trust Enforcement Engine


SDP Network Through Behaviour‑Driven Trust

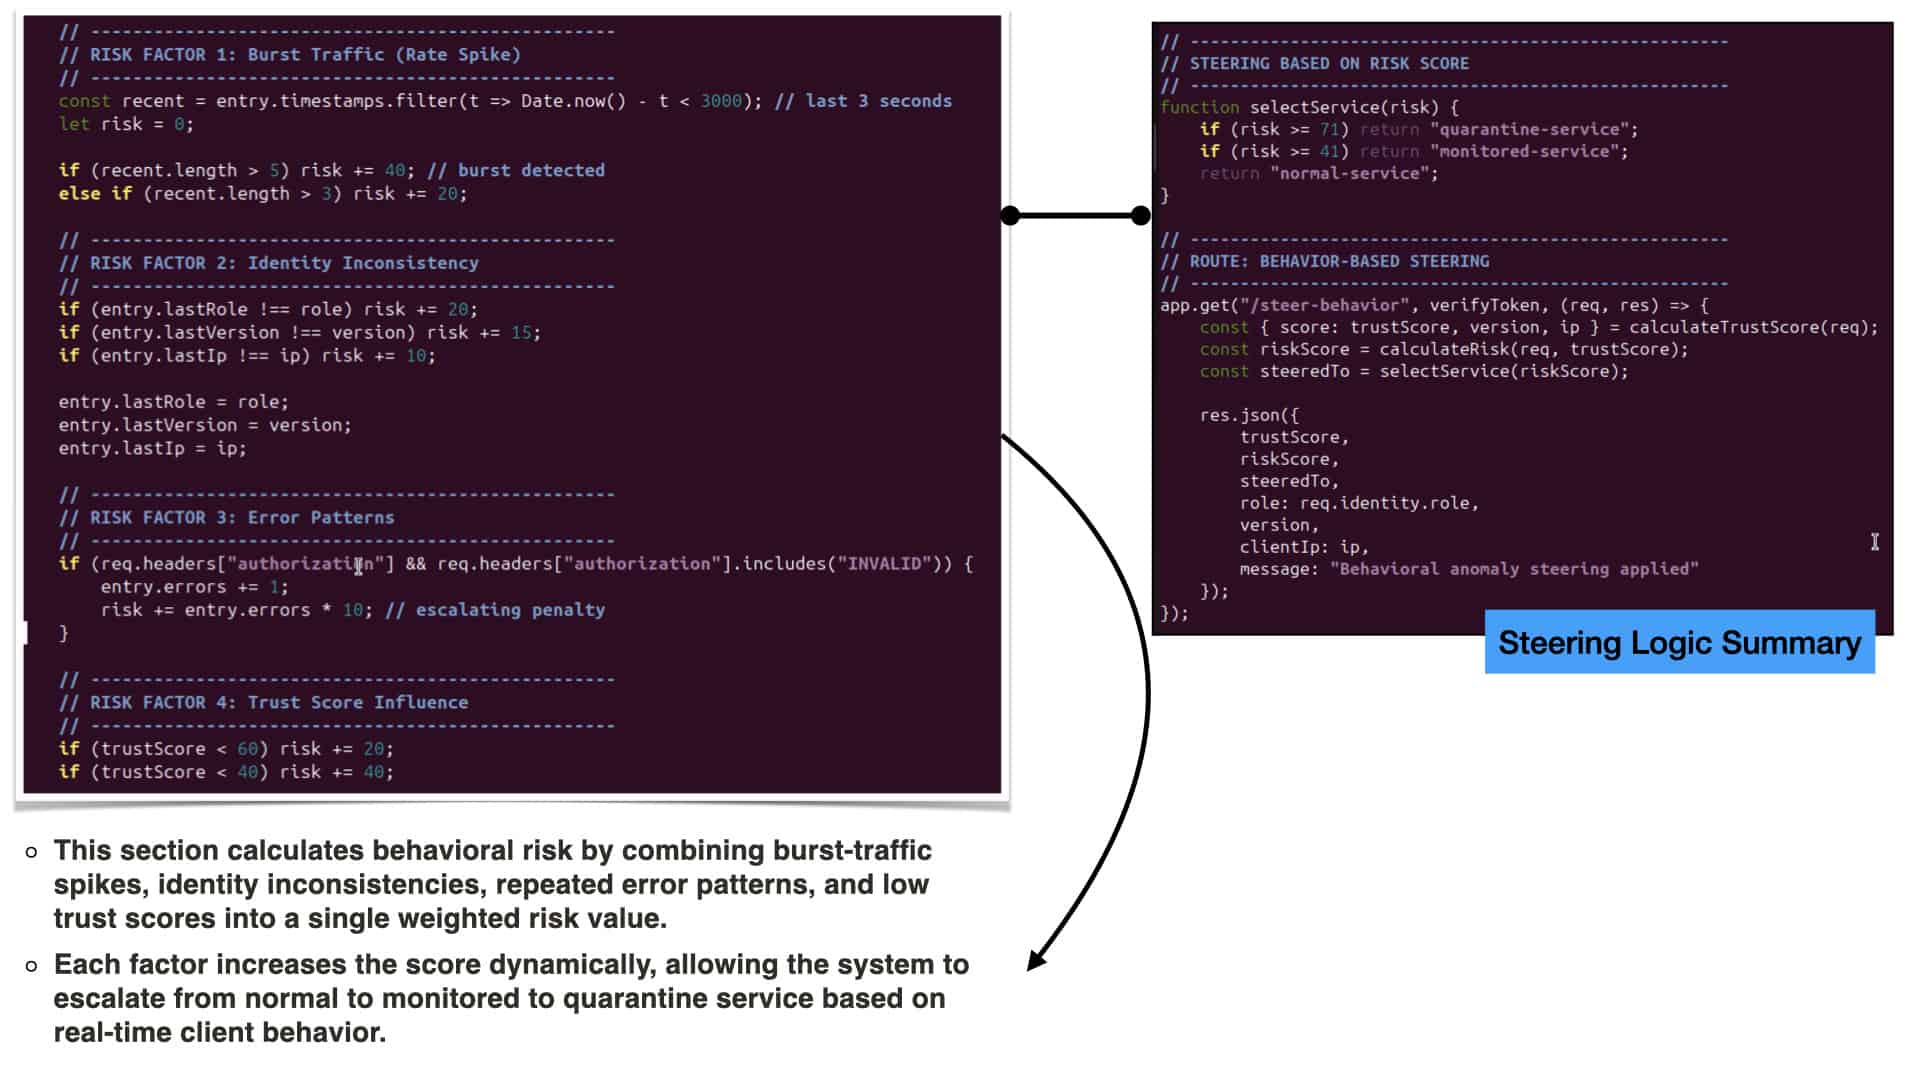
This lab demonstrates how an SDP network strengthens access control by evaluating every client request using behavioural signals rather than relying solely on identity or tokens. By analysing request frequency, metadata consistency, and error patterns, the system builds a dynamic trust profile for each client. This ensures that SDP network policies continuously validate every action, preventing risky behaviour from reaching protected applications.

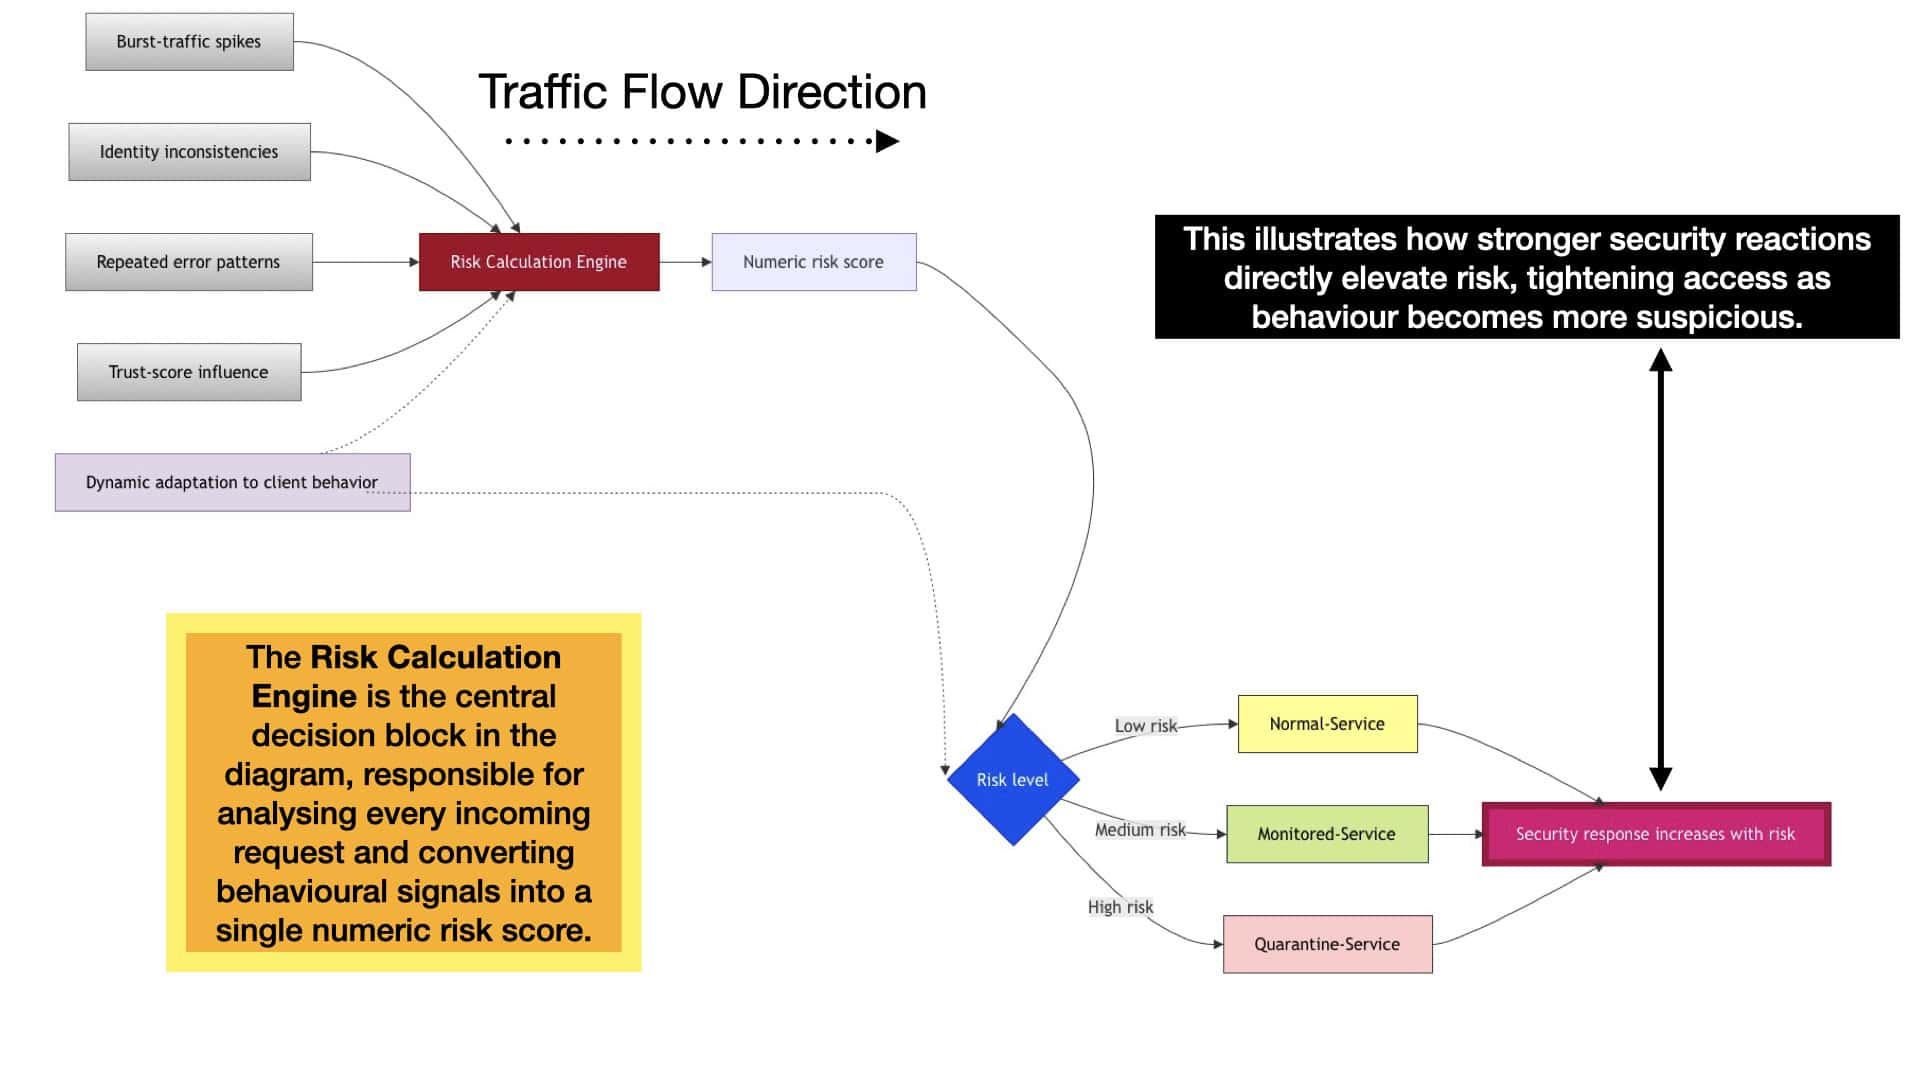
The risk engine applies weighted rules to burst‑traffic spikes, identity mismatches, repeated failures, and trust‑score influence to generate a single risk value. This multi‑factor scoring model reflects how an SDP network depends on combining diverse indicators to detect anomalies before granting application access. As risk increases, the system escalates its security posture, shifting from normal to monitored to quarantine service to protect hidden services.

Once the risk score is computed, the steering engine selects the appropriate response path. Low‑risk behaviour is routed normally, medium‑risk behaviour is monitored, and high‑risk behaviour is quarantined. This adaptive routing illustrates how an SDP network enforces dynamic segmentation, ensuring that suspicious behaviour triggers stronger controls while legitimate application flows continue securely.

Example: Understanding Port Knocking

Port knocking is a technique in which a sequence of connection attempts is made to specific ports on a remote system. In a predetermined order, these attempts serve as a secret “knock” that triggers the opening of a closed port. Port knocking acts as a virtual doorbell, allowing authorized users to access a system that would otherwise remain invisible and protected from potential threats.

The Process: Port Knocking

To delve deeper, let’s explore how port knocking works. When a connection attempt is made to a closed port, the firewall silently drops it, leaving no trace of the effort. However, when the correct sequence of connection attempts is made, the firewall recognizes the pattern and dynamically opens the desired port, granting access to the authorized user. This sequence can consist of connections to multiple ports, further enhancing the system’s security.

**Understand your flows**

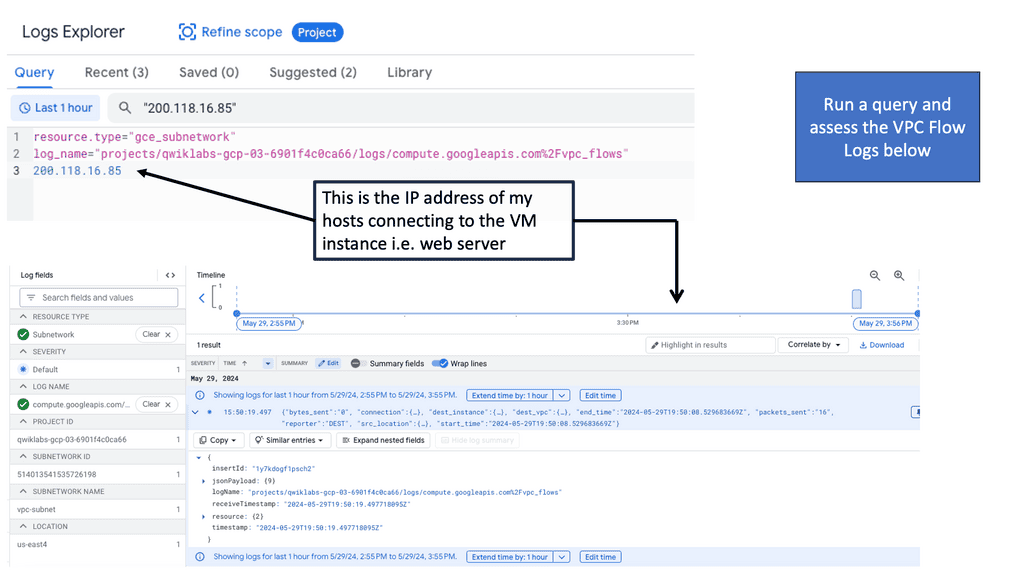
Network flows are time-bound communications between two systems. A single flow can be directly mapped to an entire conversation using a bidirectional transport protocol, such as TCP. However, a single flow for unidirectional transport protocols (e.g., UDP) might capture only half of a network conversation. Without a deep understanding of the application data, an observer on the network may not associate two UDP flows logically.

A system must capture all flow activity in an existing production network to move to a zero-trust model. The new security model should consider logging flows in a network over a long period to discover what network connections exist. Moving to a zero-trust model without this up-front information gathering will lead to frequent network communication issues, making the project appear invasive and disruptive.

Example: VPC Flow Logs

### What are VPC Flow Logs?

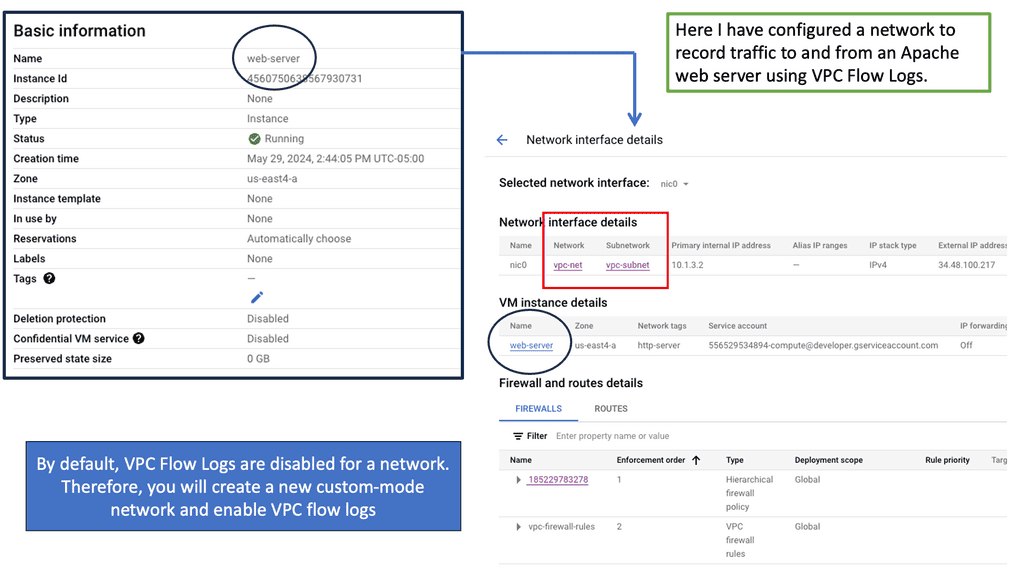
VPC Flow Logs are a feature in Google Cloud that captures information about the IP traffic going to and from network interfaces in your VPC. These logs offer detailed insights into network activity, helping you to identify potential security risks, troubleshoot network issues, and analyze the impact of network traffic on your applications.

### How VPC Flow Logs Work

When you enable VPC Flow Logs, Google Cloud begins collecting data about each network flow, including source and destination IP addresses, protocols, ports, and byte counts. This data is then stored in Google Cloud Storage, BigQuery, or Pub/Sub, depending on your configuration. You can use this data for real-time monitoring or historical analysis, providing a comprehensive view of your network’s behavior.

### Benefits of Using VPC Flow Logs

1. **Enhanced Security**: By monitoring network traffic, VPC Flow Logs help you detect suspicious activity and potential security threats, enabling you to take proactive measures to protect your infrastructure.

2. **Troubleshooting and Performance Optimization**: With detailed traffic data, you can easily identify bottlenecks or misconfigurations in your network, allowing you to optimize performance and ensure seamless operations.

3. **Cost Management**: Understanding your network traffic patterns can help you manage and predict costs associated with data transfer, ensuring you stay within budget.

4. **Compliance and Auditing**: VPC Flow Logs provide a valuable record of network activity, assisting in compliance with industry regulations and internal auditing requirements.

### Getting Started with VPC Flow Logs on Google Cloud

To start using VPC Flow Logs, you’ll need to enable them in your Google Cloud project. This process involves configuring the logging settings for your VPC, selecting the desired storage destination for the logs, and setting any filters to narrow down the data collected. Google Cloud provides detailed documentation to guide you through each step, ensuring a smooth setup process.

**Creating a software-defined perimeter**

With a software-defined perimeter (SDP) architecture, networks are logically air-gapped, dynamically provisioned, on-demand, and isolated from unprotected networks. An SDP system enhances security by requiring authentication and authorization before users or devices can access assets concealed by the SDP system. Additionally, by mandating connection pre-vetting, SDP will restrict all connections into the trusted zone based on who may connect, from those devices to what services, infrastructure, and other factors.

Zero Trust – Google Cloud Data Centers

**The Essence of Zero Trust Network Design**

Before delving into VPC Service Controls, it’s essential to grasp the concept of zero trust network design. Unlike traditional security models that rely heavily on perimeter defenses, zero trust operates on the principle that threats can exist both outside and inside your network. This model requires strict verification for every device, user, and application attempting to access resources. By adopting a zero trust approach, organizations can minimize the risk of security breaches and ensure that sensitive data remains protected.

**How VPC Service Controls Enhance Security**

VPC Service Controls are a critical component of Google Cloud’s security offerings, designed to bolster the protection of your cloud resources. They enable enterprises to define a security perimeter around their services, preventing data exfiltration and unauthorized access. With VPC Service Controls, you can:

– Create service perimeters to restrict access to specific Google Cloud services.

– Define access levels based on IP addresses and device attributes.

– Implement policies that prevent data from being transferred to unauthorized networks.

These controls provide an additional layer of security, ensuring that your cloud infrastructure adheres to the zero trust principles.

VPC Security Controls


Creating a Zero Trust Environment

Software-defined perimeter is a security framework that shifts the focus from traditional perimeter-based network security to a more dynamic and user-centric approach. Instead of relying on a fixed network boundary, SDP creates a “Zero Trust” environment, where users and devices are authenticated and authorized individually before accessing network resources. This approach ensures that only trusted entities gain access to sensitive data, regardless of their location or network connection.

Implementing SDP Networks:

Implementing SDP networks requires careful planning and execution. The first step is to assess the existing network infrastructure and identify critical assets and access requirements. Next, organizations must select a suitable SDP solution and integrate it into their network architecture. This involves deploying SDP controllers, gateways, and agents and configuring policies to enforce access control. It is crucial to involve all stakeholders and conduct thorough testing to ensure a seamless deployment.

Zero trust framework:

The zero-trust framework for networking and security is here for a good reason. There are various bad actors, ranging from opportunistic and targeted to state-level, and all are well prepared to find ways to penetrate a hybrid network. As a result, there is now a compelling reason to implement the zero-trust model for networking and security.

SDP network brings SDP security, also known as software defined perimeter, which is heavily promoted as a replacement for the virtual private network (VPN) and, in some cases, firewalls for ease of use and end-user experience.

Dynamic tunnel of 1:

It also provides a solid SDP security framework utilizing a dynamic tunnel of 1 per app per user. This offers security at the segmentation of a micro level, providing a secure enclave for entities requesting network resources. These are micro-perimeters and zero-trust networks that can be hardened with technology such as SSL security and single packet authorization.


SDP NETWORK • BEHAVIOUR INVESTIGATION

SDP Behaviour & Microsegmentation Investigation Lab

Investigate how behavioural signals can change access decisions and how microsegmentation limits the blast radius when a trusted identity begins behaving unexpectedly.

Scenario: A previously trusted user is accessing an internal application. The identity remains valid, but the request pattern has changed. Your task is to identify the signals that should influence the access decision.
Investigation Evidence
Behaviour Risk Engine
Trust Score
78
Anomaly Score
12
Current Enforcement
NORMAL ACCESS
No significant behavioural anomaly has been selected.
Microsegmentation Path
USER / DEVICE Identity + Behaviour
→
SDP POLICY Risk + Context
→
PROTECTED SEGMENT Application Scope
Investigation Console
[SDP] Monitoring behavioural signals...
[FLOW] Normal application traffic observed.
[POLICY] User currently remains within authorised application scope.
Engineering Takeaway

Behavioural analytics can provide additional context to an access decision, but a risk score should not replace identity, authorization or segmentation controls. Microsegmentation limits which applications or segments an identity can reach, reducing lateral movement when behaviour becomes suspicious.

SDP Network

A software-defined perimeter is a security approach that controls resource access and forms a virtual boundary around networked resources. Think of an SDP network as a 1-to-1 mapping, unlike a VLAN, which can have many hosts within, all of which could be of different security levels.

Also, with an SDP network, we create a security perimeter via software versus hardware; an SDP can hide an organization’s infrastructure from outsiders, regardless of location. Now, we have a security architecture that is location-agnostic. As a result, employing SDP architectures will decrease the attack surface and mitigate internal and external network bad actors. The SDP framework is based on the U.S. Department of Defense’s Defense Information Systems Agency’s (DISA) need-to-know model from 2007.

Feature 1: Dynamic Access Control

One of the primary features of SDP is its ability to dynamically control access to network resources. Unlike traditional perimeter-based security models, which grant access based on static rules or IP addresses, SDP employs a more granular approach. It leverages context-awareness and user identity to dynamically allocate access rights, ensuring only authorized users can access specific resources. This feature eliminates the risk of unauthorized access, making SDP an ideal solution for securing sensitive data and critical infrastructure.

Feature 2: Zero Trust Architecture

SDP embraces zero-trust, a security paradigm that assumes no user or device can be trusted by default, regardless of their location within the network. With SDP, every request to access network resources is subject to authentication and authorization, regardless of whether the user is inside or outside the corporate network. By adopting a zero-trust architecture, SDP eliminates the concept of a network perimeter and provides a more robust defense against internal and external threats.

Feature 3: Application Layer Protection

Traditional security solutions often focus on securing the network perimeter, leaving application layers vulnerable to targeted attacks. SDP addresses this limitation by incorporating application layer protection as a core feature. By creating micro-segmented access controls at the application level, SDP ensures that only authenticated and authorized users can interact with specific applications or services. This approach significantly reduces the attack surface and enhances the overall security posture.

SDN Network Principles Applied at the Application Layer

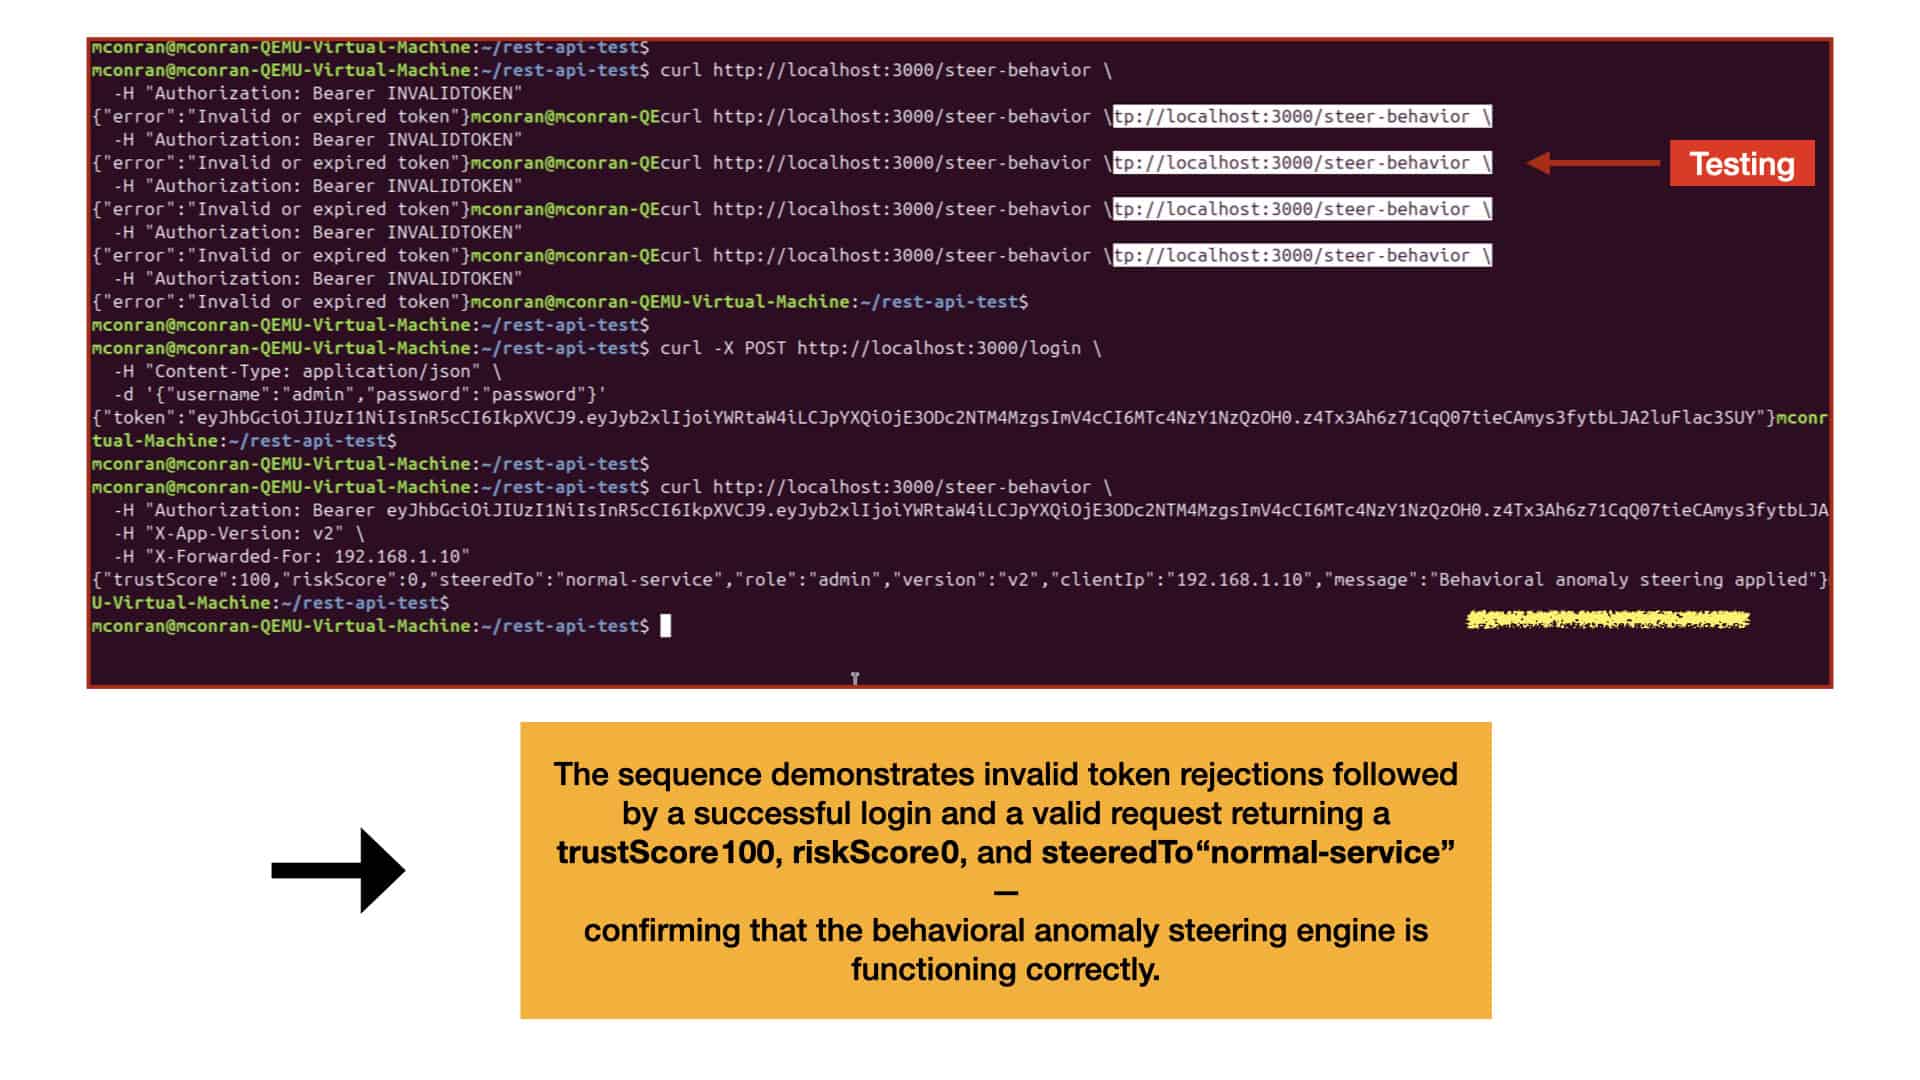
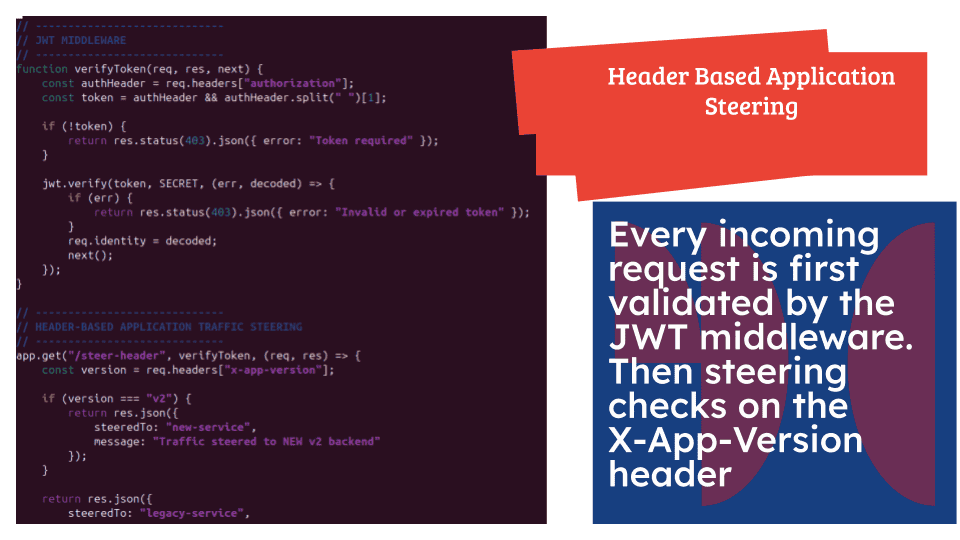
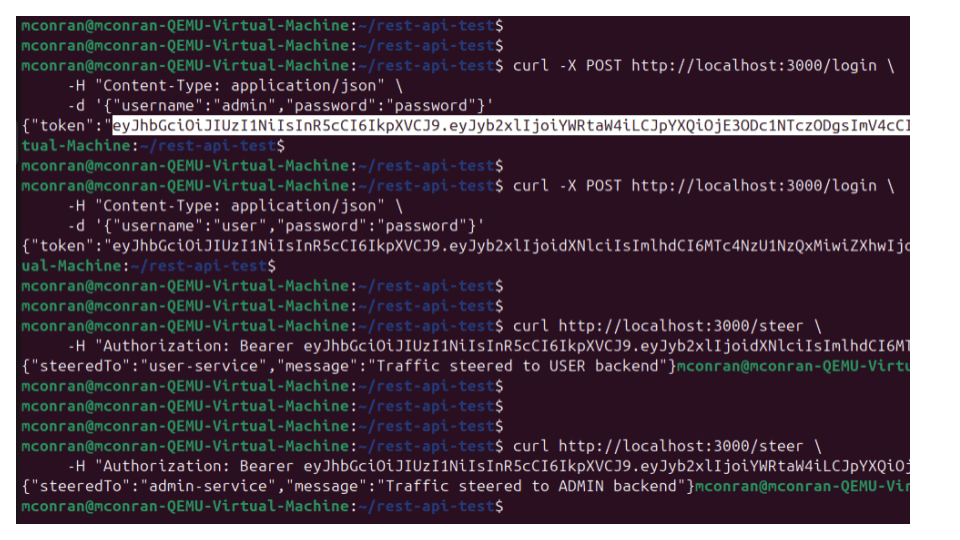
This server file reflects how SDN Network concepts can be implemented directly within an application by separating control logic from the underlying connectivity. The login endpoint issues JWT tokens that act as identity credentials, allowing the application to treat user identity as a programmable control signal. Just as SDN controllers validate and authorize flows before installing forwarding rules, the JWT middleware ensures that only authenticated traffic is permitted to move deeper into the system. This creates an SDN‑like control plane inside the application, where identity validation becomes the first step in determining how traffic should be handled.

Header based network connectivity

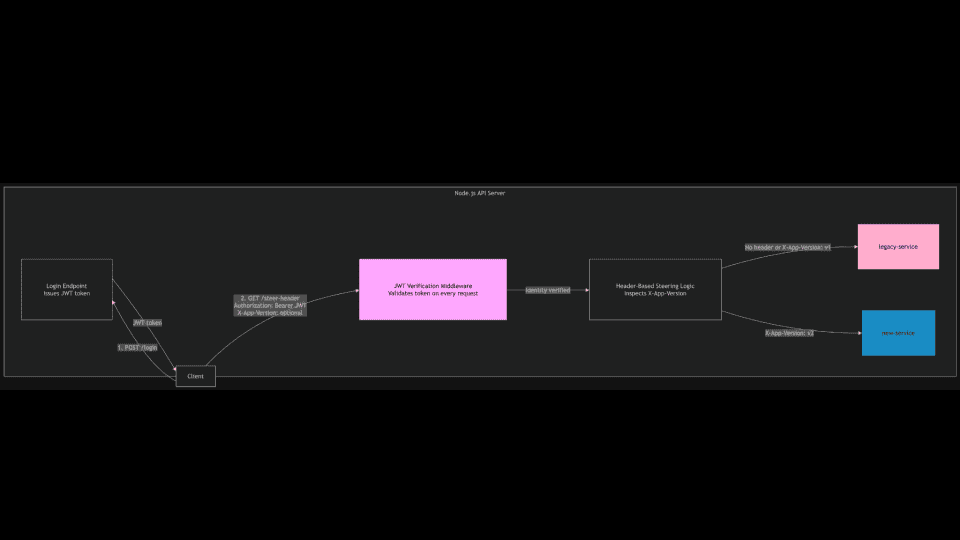
After identity is verified, the application applies SDN‑style steering logic by inspecting the X-App-Version header to decide how traffic should be routed. In an SDN Network, forwarding decisions are based on programmable policies rather than static network constructs, and this file mirrors that behavior. The steering block acts like a simplified SDN controller: it reads metadata from the request, evaluates policy, and dynamically selects the correct backend path. Requests marked with version v2 are routed to the new-service, while all other flows are directed to the legacy-service. This demonstrates how SDN principles—policy‑driven forwarding and dynamic flow selection—can be implemented at the application layer.

Header control

The overall flow of this file showcases how SDN Network ideas can be used to segment and control traffic paths within an application. Once a request passes identity validation, the steering logic determines which backend service the flow should reach, effectively creating dynamic segmentation similar to SDN flow rules. Instead of relying on static routing or fixed network paths, the application makes real‑time decisions based on identity and metadata, steering traffic to different services as needed. This mirrors how SDN Networks dynamically adjust forwarding behavior to enforce policy, optimize connectivity, and isolate flows across distributed systems.

Diagram network connectivity

Example Technology: Web Security Scanner

**How Web Security Scanners Work**

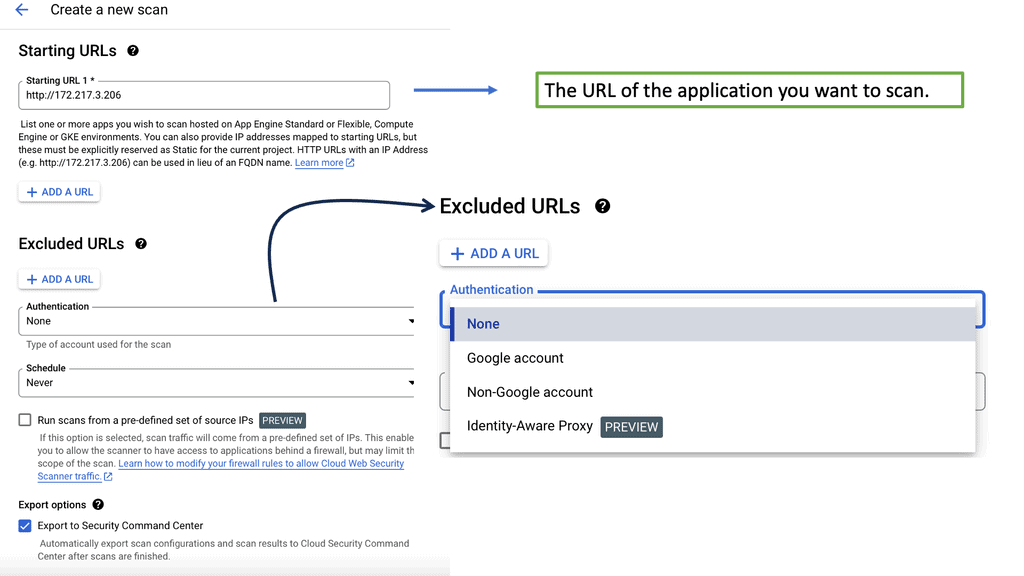
Web security scanners function by crawling through web applications and testing for known vulnerabilities. They analyze various components, such as forms, cookies, and headers, to identify potential security flaws. By simulating attacks, these scanners provide insights into how a malicious actor might exploit your web application. This information is crucial for developers to patch vulnerabilities before they can be exploited, thus fortifying your web defenses.

security web scanner

Feature 4: Scalability and Flexibility

SDP offers scalability and flexibility to accommodate the dynamic nature of modern business environments. Whether an organization needs to provide secure access to a handful of users or thousands of employees, SDP can scale accordingly. Additionally, SDP seamlessly integrates with existing infrastructure, allowing businesses to leverage their current investments without needing a complete overhaul. This adaptability makes SDP a cost-effective solution with a low barrier to entry.

**SDP Security**

Authentication and Authorization

So, how can one authenticate and authorize themselves when creating an SDP network and SDP security?

First, trust is the main element within an SDP network. Therefore, mechanisms that can associate themselves with authentication and authorization to trust at a device, user, or application level are necessary for zero-trust environments.

When something presents itself to a zero-trust network, it must go through several SDP security stages before access is granted. The entire network is dark, meaning that resources drop all incoming traffic by default, providing an extremely secure posture. Based on this simple premise, a more secure, robust, and dynamic network of geographically dispersed services and clients can be created.

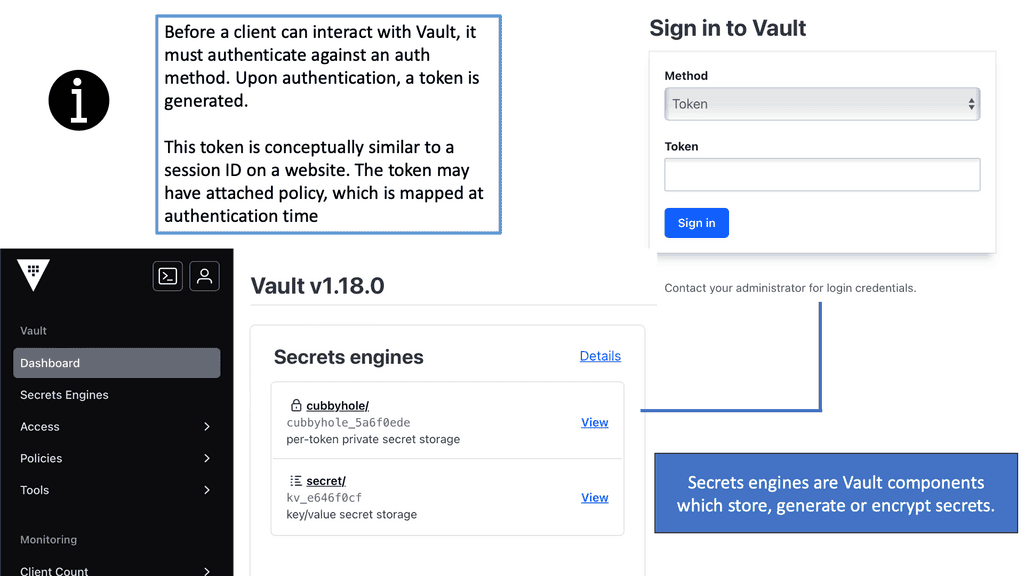
Example: Authentication with Vault

### Understanding Authentication Methods

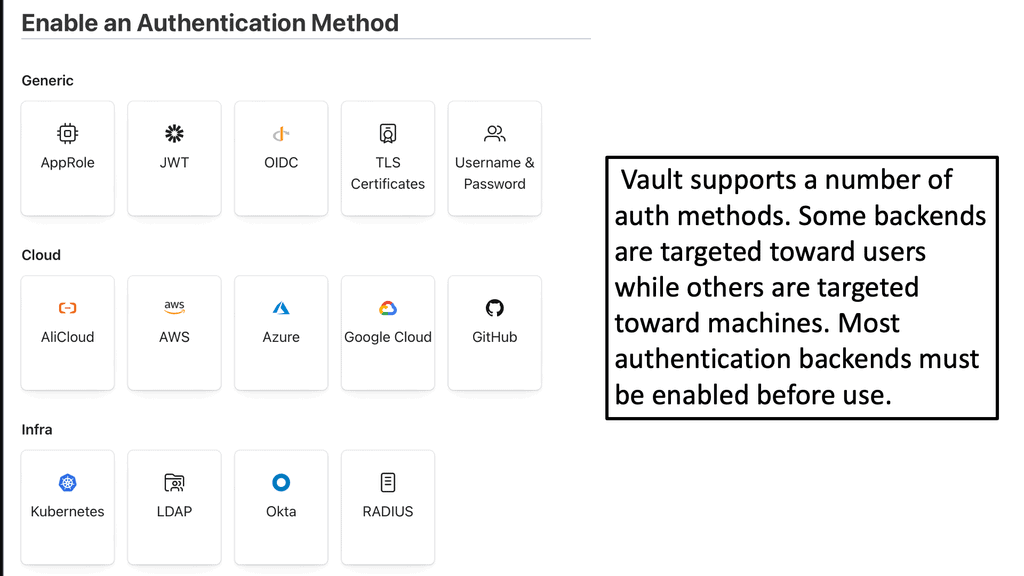
Vault offers a variety of authentication methods, allowing it to integrate seamlessly into diverse environments. These methods determine how users and applications prove their identity to Vault before gaining access to secrets. Some of the most common methods include:

– **Token Authentication**: The simplest form of authentication, where tokens are used as a bearer of identity. Tokens can be created with specific policies that define what actions can be performed.

– **AppRole Authentication**: This method is designed for applications and automated processes. It uses a role-based approach to issue secrets, providing enhanced security through role IDs and secret IDs.

– **LDAP Authentication**: Ideal for organizations already using LDAP directories, this method allows users to authenticate using their existing LDAP credentials, streamlining the authentication process.

– **OIDC and OAuth2**: These methods support single sign-on (SSO) capabilities, integrating with identity providers to authenticate users based on their existing identities.

Understanding these methods is crucial for configuring Vault in a way that best suits your organization’s security needs.

### Implementing Secure Access Control

Once you’ve chosen the appropriate authentication method, the next step is to implement secure access control. Vault uses policies to define what authenticated users and applications can do. These policies are written in a domain-specific language (DSL) and can be as fine-grained as required. For instance, you might create a policy that allows a specific application to read certain secrets but not modify them.

By leveraging Vault’s policy framework, organizations can ensure that only authorized entities have access to sensitive data, significantly reducing the risk of unauthorized access.

### Automating Secrets Management

One of Vault’s standout features is its ability to automate secrets management. Traditional secrets management involves manually rotating keys and credentials, a process that’s not only labor-intensive but also prone to human error. Vault automates this process, dynamically generating and rotating secrets as needed. This automation not only enhances security but also frees up valuable time for IT teams to focus on other critical tasks.

For example, Vault can dynamically generate database credentials for applications, ensuring that they always have access to valid and secure credentials without manual intervention.

Vault

  • A key point: The difference between Authentication and Authorization.

Before we go any further, it’s essential to understand the difference between authentication and authorization. In the zero-trust world, upon examining an end host, a device, and a user from an agent. Device and user authentication are carried out first before agent formation. The user will authenticate the device first and then against the agent. Authentication confirms your identity, while authorization grants access to the system.

**The consensus among SDP network vendors**

Generally, with most zero-trust and SDP VPN network vendors, the agent is only formed once valid device and user authentication has been carried out. The authentication methods used to validate the device and user can be separate. A device that needs to identify itself to the network can be authenticated with X.509 certificates.

A user can be authenticated by other means, such as a setting from an LDAP server if the zero-trust solution has that as an integration point. The authentication methods between the device and users don’t have to be tightly coupled, providing flexibility.

SDP Security with SDP Network: X.509 certificates

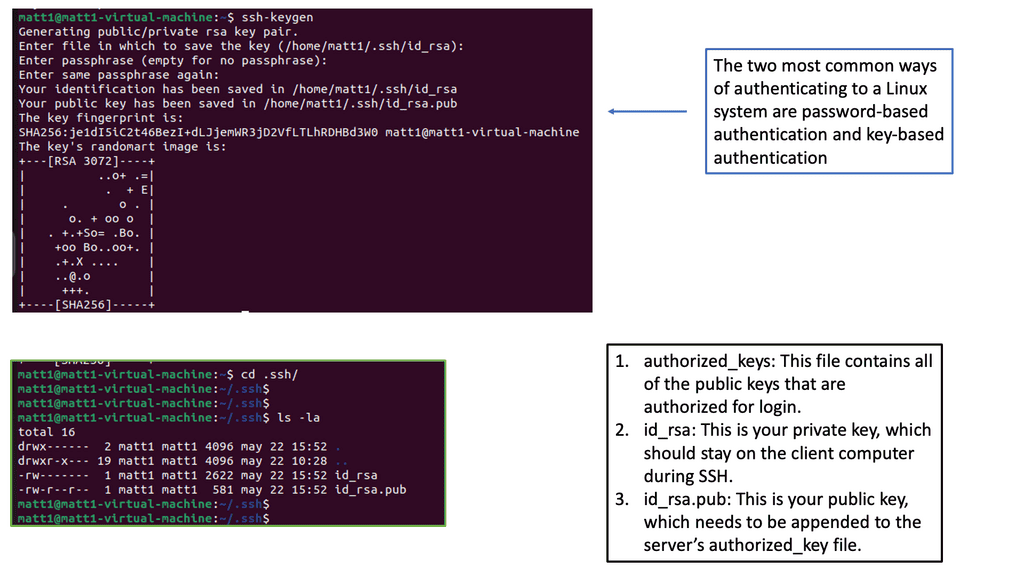
IP addresses are used for connectivity, not authentication, and don’t have any fields to implement authentication. The authentication must be handled higher up the stack. So, we need to use something else to define identity, and that would be the use of certificates. X.509 certificates are a digital certificate standard that allows identity to be verified through a chain of trust and is commonly used to secure device authentication. X.509 certificates can carry a wealth of information within the standard fields that can fulfill the requirements to carry particular metadata.

To provide identity and bootstrap encrypted communications, X.509 certificates use two cryptographic keys, mathematically related pairs consisting of public and private keys. The most common are RSA (Rivest–Shamir–Adleman) key pairs.

The private key is secret and held by the certificate’s owner, and the public key, as the names suggest, is not secret and distributed. The public key can encrypt the data; the private key can decrypt it, and vice versa. If the correct private key is not held, it is impossible to decrypt encrypted data using the public key.

SDP Security with SDP Network: Private key storage

Before we discuss the public key, let’s examine how we secure the private key. Device authentication will fail if bad actors access the private key. Once the device presents a signed certificate, one way to secure the private key is to configure access rights. However, if a compromise occurs, we are left in the undesirable world of elevated access, exposing the unprotected key.

The best way to secure and store private device keys is to use crypto processors, such as a trusted platform module (TPM). A cryptoprocessor is essentially a chip embedded in the device.

The private keys are bound to the hardware without being exposed to the system’s operating system, which is far more vulnerable to compromise than the actual hardware. TPM binds the private software key to the hard, creating robust device authentication.

SDP Security with SDP Network: Public Key Infrastructure (PKI)

How do we ensure that we have the correct public key? This is the role of the public key infrastructure (PKI). There are many types of PKI, with certificate authorities (CA) being the most popular. In cryptography, a certificate authority is an entity that issues digital certificates.

A certificate can be a pointless blank paper unless it is somehow trusted. This is done by digitally signing the certificate to endorse the validity. It is the responsibility of the certificate authorities to ensure all details of the certificate are correct before signing it. PKI is a framework that defines a set of roles and responsibilities used to distribute and validate public keys securely in an untrusted network.

For this, a PKI leverages a registration authority (RA). You may wonder what the difference between an RA and a CA is. The RA interacts with the subscribers to provide CA services. The CA subsumes the RA, which is responsible for all RA actions.

The registration authority accepts requests for digital certificates and authenticates the entity making the request. This binds the identity to the public key embedded in the certificate, cryptographically signed by the trusted 3rd party.

Not all certificate authorities are secure!

However, not all certificate authorities are bulletproof against attack. Back in 2011, DigiNotar was at the mercy of a security breach. The bad actor took complete control of all eight certificate-issuing servers, and they issued rogue certificates that had not yet been identified. It is estimated that over 300,000 users had their private data exposed by rogue certificates.

Browsers immediately blacklist DigiNotar’s certificates, but it does highlight the issues of using a 3rd party. While Public Key Infrastructure is used at large on the public internet backing X.509 certificates, it’s not recommended for zero trust SDP. At the end of the day, when you think about it, you are still using 3rd party for a pretty important task. It would be best if you were looking to implement a private PKI system for a zero-trust approach to networking and security.

If you are not looking for a fully automated process, you could implement a temporary one-time password (TOTP). This allows for human control over the signing of the certificates. Remember that much trust must be placed in whoever is responsible for this step.

SDP Closing Points:

– As businesses continue to face increasingly sophisticated cyber threats, the importance of implementing robust network security measures cannot be overstated. Software Defined Perimeter offers a comprehensive solution that addresses the limitations of traditional network architectures.

– By adopting SDP, organizations can enhance their security posture, improve network flexibility, simplify management, mitigate DDoS attacks, and meet regulatory requirements. Embracing this innovative approach to network security can safeguard sensitive data and provide peace of mind in an ever-evolving digital landscape.

– Organizations must adopt innovative security solutions to protect their valuable assets as cyber threats evolve. Software-defined perimeter offers a dynamic and user-centric approach to network security, providing enhanced protection against unauthorized access and data breaches.

– With enhanced security, granular access control, simplified network architecture, scalability, and regulatory compliance, SDP is gaining traction as a trusted security framework in today’s complex cybersecurity landscape. Embracing SDP can help organizations stay one step ahead of the ever-evolving threat landscape and safeguard their critical data and resources.

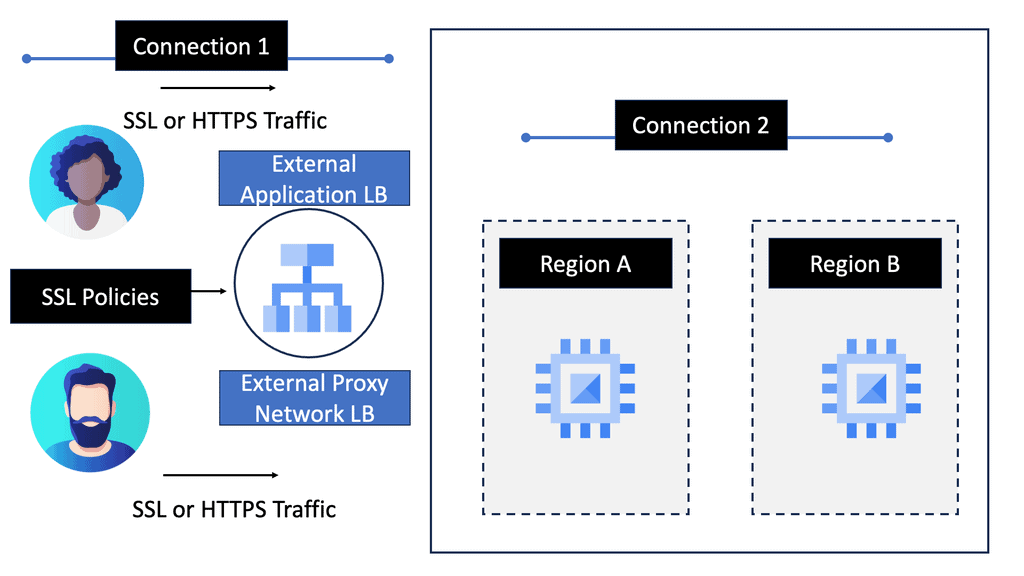
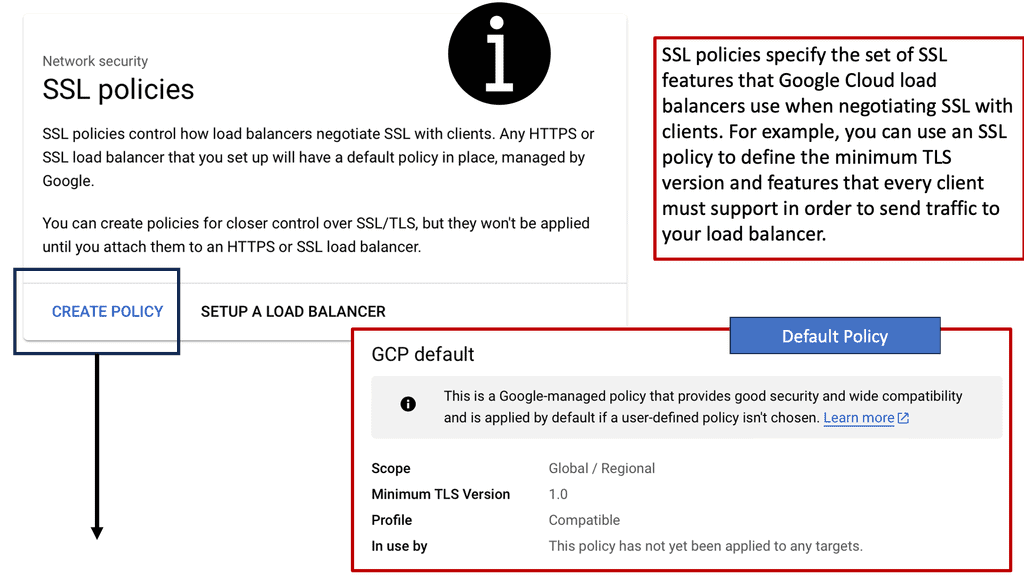
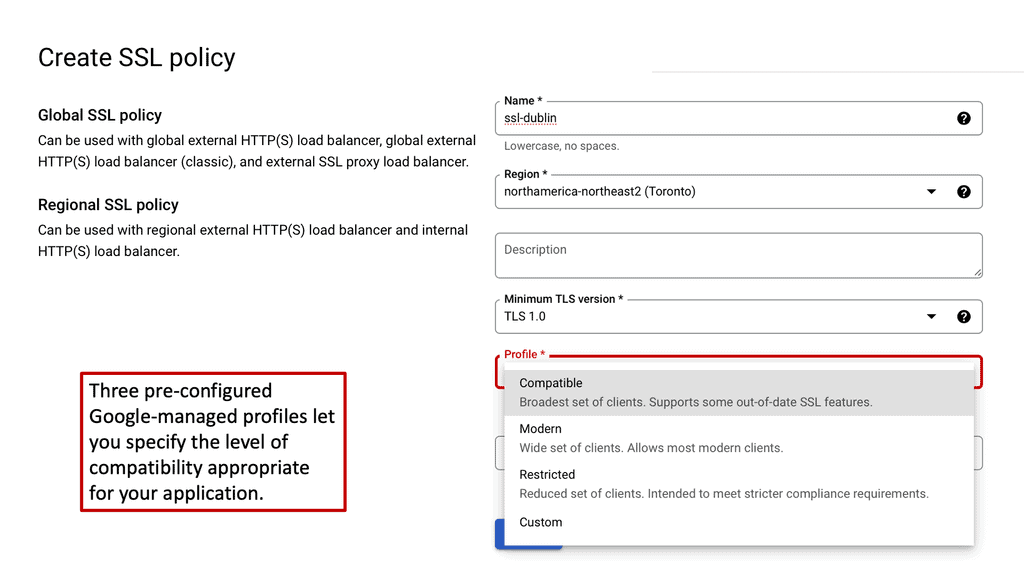
Example Technology: SSL Policies

**What Are SSL Policies?**

SSL policies are configurations that determine the security settings for SSL/TLS connections between clients and servers. These policies ensure that data is encrypted during transmission, protecting it from unauthorized access. On Google Cloud, SSL policies allow you to specify which SSL/TLS protocols and cipher suites can be used for your services. This flexibility enables you to balance security and performance based on your specific requirements.


SSL Policies

Closing Points on SDP Network

At its core, SDP operates on a zero-trust model, where network access is granted based on user identity and device verification rather than mere IP addresses. This ensures that each connection is authenticated before any access is granted. The process begins with a secure handshake between the user’s device and the SDP controller, which verifies the user’s identity against a predefined set of policies. Once authenticated, the user is granted access to specific network resources based solely on their role, ensuring a minimal access approach. This not only enhances security but also simplifies network management.

The adoption of SDP brings numerous benefits. Firstly, it significantly reduces the attack surface by making network resources invisible to unauthorized users. This means that potential attackers cannot even see the resources, let alone access them. Secondly, SDP provides a seamless and secure experience for users, as it adapts to their needs without compromising security. Additionally, SDP is highly scalable and can be easily integrated with existing security frameworks, making it a cost-effective solution for businesses of all sizes.

While the advantages of SDP are compelling, there are challenges to consider. Implementing SDP requires an initial investment in terms of time and resources to set up the infrastructure and train personnel. Organizations must also ensure that their identity and access management (IAM) systems are robust and capable of supporting SDP’s zero-trust model. Furthermore, as with any technology, staying updated with the latest developments and threats is crucial to maintaining a secure environment.

SDP NETWORK • PKI + DYNAMIC ACCESS

SDP PKI & Dynamic Tunnel Lab

Explore how device identity, user authentication and policy evaluation can precede creation of an application-specific encrypted connection.

Scenario: A managed device wants to access a protected Finance application. The SDP system must validate the device identity, authenticate the user, apply policy and then establish an application-specific tunnel.
Identity & Access Inputs
Dynamic Gateway Selection
Gateway A — London
Available application gateway
24 ms
Gateway B — Dublin
Available application gateway
11 ms
Gateway C — Frankfurt
Available application gateway
31 ms
Tunnel Status
NOT ESTABLISHED
Verify identity and policy before selecting a tunnel.
SDP Connection Lifecycle
DEVICE
CERTIFICATE
USER
AUTH
POLICY
CHECK
CONTROLLER
DECISION
DYNAMIC
TUNNEL
APPLICATION
Connection Trace
[SDP] Waiting for connection request...
[PKI] Device identity has not yet been validated.
[CONTROLLER] No application-specific tunnel has been provisioned.
Engineering Takeaway

PKI can establish strong device identity, but a certificate alone does not determine application authorization. The SDP controller combines device identity, user authentication and policy before provisioning application-specific access. The resulting tunnel can use authenticated encryption such as TLS or mTLS; the exact tunnel architecture depends on the SDP implementation.