SASE & Zero Trust: From Network Perimeter to Identity-Driven Security
Enterprise networks have changed. Users work from anywhere, applications increasingly run across multiple clouds, and business traffic no longer follows a predictable path through a central corporate data centre. Security therefore cannot depend on network location alone.
Secure Access Service Edge (SASE) brings networking and security closer to users, devices and applications through cloud-delivered services. Zero Trust adds the decision model: access is evaluated using identity, device posture, context, risk and policy rather than simply assuming that a trusted network location means a trusted user or session.
This guide treats SASE as an engineering architecture rather than a single product. It follows a request from the network edge through identity and policy decisions, into the security services that enforce those decisions, and finally into the telemetry and response systems used when behaviour becomes suspicious.
SASE & Zero Trust Engineering Path
SASE Architecture & the New Enterprise Network
SASE Architecture & the New Enterprise Network
SASE Architecture & the New Enterprise Network
Enterprise networks have changed fundamentally. Users no longer work from a small number of corporate offices, applications no longer reside exclusively inside private data centres, and business traffic increasingly crosses the public Internet before reaching cloud or SaaS services. SASE provides an architectural model for delivering networking and security capabilities closer to those users, devices and applications.
SASE is not a single security product. It is an architectural approach that combines distributed networking, cloud-delivered security enforcement and policy-driven access control so that security decisions can follow users, devices and applications rather than depending entirely on a traditional network perimeter.
The Internet Is Becoming the Enterprise Network
Traditional enterprise architecture was built around a relatively stable boundary. Users connected to offices, offices connected to private WAN infrastructure, and security controls were concentrated around the data centre or Internet edge. Firewalls, proxies, VPN concentrators and intrusion-prevention systems therefore occupied predictable positions in the network.
Modern organisations operate differently. Employees may connect from homes, branch offices, mobile networks, partner locations or temporary workspaces. Applications may be hosted in public cloud, private cloud, SaaS platforms or distributed application environments. The traffic path between a user and an application is therefore no longer determined simply by physical network location.
This creates a fundamental architectural problem: security controls must remain effective even when the user, device, application and network are distributed.
From the Data Centre Perimeter to Distributed Enforcement
A traditional security model often assumes that traffic can be brought back through a central enforcement point. This can provide strong control, but it can also introduce unnecessary routing complexity, additional latency and operational dependency on a small number of network locations.
SASE changes the architectural question from “How do we bring the user to the security perimeter?” to “How do we deliver the appropriate security controls close to the user and application?”
That distinction is important. SASE does not mean that the enterprise stops using firewalls, routing, segmentation or private connectivity. Instead, these capabilities become part of a broader distributed architecture in which policy and security enforcement can be delivered through cloud-based points of presence and other strategically positioned enforcement locations.
What SASE Combines
At its architectural core, SASE brings together two traditionally separate domains: network connectivity and security services.
| Domain | Typical Capability | Engineering Role |
|---|---|---|
| Networking | SD-WAN / intelligent routing | Selects appropriate paths and connectivity based on application and network conditions. |
| Security | SWG | Applies security policy to Internet and web traffic. |
| Security | FWaaS | Provides distributed firewall policy without requiring a physical firewall at every location. |
| Access | ZTNA | Controls access to private applications using identity, device and policy context. |
| Data | CASB / DLP | Applies application and data protection controls to cloud traffic and sensitive information. |
| Visibility | Telemetry and analytics | Provides the evidence required to monitor performance, security events and policy decisions. |
Networking and Security Become Policy-Driven
One of the most important changes introduced by SASE is the relationship between connectivity and security policy. Instead of treating routing, security and application access as completely independent systems, the architecture can make decisions using a common set of signals.
Identity can describe who is making the request. Context can include device posture, location, application, network conditions and other relevant signals. Policy determines what should be permitted. Enforcement then applies the resulting decision to the traffic or access request.
This is the architectural bridge between SASE and Zero Trust. SASE provides the distributed networking and security architecture; Zero Trust provides the decision philosophy in which access is continuously evaluated rather than being implicitly trusted because a request originated from a particular network.
SD-WAN as Part of the SASE Architecture
SD-WAN is often associated with the networking side of SASE. Its role is to provide application-aware connectivity across available transport paths such as broadband, private circuits and cellular connectivity.
Rather than treating every packet as equivalent, an SD-WAN architecture can identify applications and use policy to select an appropriate path. Performance measurements such as latency, loss and jitter can also influence path selection.
However, SD-WAN alone is not SASE. SD-WAN primarily addresses connectivity and traffic steering, while SASE extends the architecture into security enforcement, identity-aware access, cloud security and distributed policy control.
Security Service Edge
The security side of the architecture is commonly described using the term Security Service Edge (SSE). SSE focuses on cloud-delivered security services such as secure web access, zero-trust application access and cloud/data security controls.
In practical architectures, the networking and security components can therefore be viewed as complementary layers. SD-WAN provides connectivity and traffic steering, while SSE provides distributed security enforcement. Together, they form an important part of the broader SASE model.
Why Points of Presence Matter
A distributed SASE architecture depends on strategically located enforcement points, commonly delivered through provider points of presence (PoPs). The purpose is not simply to create more locations. The objective is to reduce unnecessary traffic tromboning while providing security enforcement near users and destinations.
Consider a user in one region accessing a SaaS application hosted in another region. A poorly designed architecture might force that traffic through a distant corporate data centre before allowing it to reach the SaaS service. A distributed architecture can instead select an appropriate security enforcement location and then connect toward the destination.
The engineering challenge is therefore not simply geographic proximity. The design must consider latency, security policy, application requirements, data sovereignty, availability, inspection requirements and operational visibility.
SASE Is Not a Single Traffic Path
A common mistake is to imagine SASE as a fixed chain in which every packet must pass through every security service. Real architectures are more selective.
An Internet request may require secure web gateway inspection. A private application request may require ZTNA enforcement. A SaaS transaction involving sensitive data may require CASB or DLP controls. Another request may require only a subset of these controls.
The correct mental model is therefore policy-driven service selection, not a mandatory linear chain.
Do not design SASE as “all traffic passes through all services.” Design it as “policy determines which security services are relevant to this request.”
Traditional Perimeter vs Distributed SASE
| Traditional Perimeter | Distributed SASE Model |
|---|---|
| Security concentrated around offices and data centres. | Security services distributed closer to users and applications. |
| Network location strongly influences trust. | Identity, device, context and policy influence access decisions. |
| Remote users often connect through central VPN infrastructure. | Users can receive policy-driven access through distributed enforcement. |
| Cloud traffic may be forced through legacy inspection points. | Cloud and Internet traffic can be inspected at appropriate distributed enforcement locations. |
| Security appliances are often tied to physical sites. | Security capabilities can be delivered as cloud services. |
SASE Deployment Is an Architectural Journey
SASE should not be treated as a requirement to replace an entire enterprise network immediately. Most organisations already have significant investments in routing, firewalls, VPNs, identity platforms, endpoint controls, proxies and cloud infrastructure.
A practical migration therefore introduces capabilities incrementally. An organisation may begin with SD-WAN, move Internet security toward cloud-delivered enforcement, introduce ZTNA for selected applications, integrate identity and device signals, and progressively consolidate policy and telemetry.
Map users, devices, applications, data and existing security enforcement points before deciding which SASE capabilities to introduce.
The objective is not simply to replace hardware with cloud services. Policy must become portable, identity-aware and consistently enforceable.
Network connectivity alone cannot determine whether access should be permitted. Identity and device context must become part of the decision.
Distributed enforcement creates more policy decision points, making consistent telemetry and centralised analysis essential for operations.
The Engineering Model
The most useful way to understand SASE is therefore not as a product category, but as a change in where networking and security decisions are made.
The enterprise moves from a model dominated by network location and centralised perimeter enforcement toward a model in which identity, context, policy and distributed enforcement work together.
SASE provides the architectural foundation for a distributed enterprise: connectivity becomes application-aware, security enforcement moves closer to users and applications, and policy can incorporate identity and context rather than relying primarily on network location.
SASE Architecture Flow
Zero Trust Identity & Adaptive Access
Zero Trust Identity & Adaptive Access
Zero Trust Identity & Adaptive Access
Once security enforcement is distributed across users, devices, cloud applications and Internet services, network location can no longer be treated as a sufficient indication of trust. Zero Trust changes the access model by requiring every request to be evaluated using identity, device state, context, risk and policy.
A successful authentication proves that an identity has been authenticated. It does not automatically prove that the identity should receive unrestricted access to every resource.
Authentication Is Not Authorisation
One of the most important concepts in Zero Trust architecture is the distinction between authentication and authorisation.
Authentication answers the question: “Who are you?” Authorisation answers a different question: “What are you allowed to access?”
A user may successfully authenticate with a valid password, passkey or multi-factor authentication method and still be denied access to a sensitive application. The access decision may depend on the user's role, device security state, location, application sensitivity, requested operation or current risk level.
Identity Becomes a Primary Security Signal
In a traditional perimeter model, network location can provide a strong implicit signal. A device connected to the corporate LAN may be considered more trusted than a device on an external network.
Zero Trust reduces that assumption. The identity making the request becomes a primary security signal, but it is evaluated alongside other evidence rather than being treated as sufficient by itself.
User, service account or workload identity making the request.
Device posture, management state, security controls and compliance.
Location, time, network characteristics, application and request context.
Signals indicating unusual, suspicious or potentially compromised behaviour.
Rules defining which combinations of signals should permit access.
The control that actually allows, restricts, challenges or denies the request.
Multi-Factor Authentication
Multi-factor authentication strengthens authentication by requiring more than one category of evidence. The objective is to reduce the impact of compromised passwords and other single-factor credentials.
Modern deployments can include phishing-resistant mechanisms such as passkeys and FIDO2/WebAuthn, alongside other authentication factors where appropriate. The important architectural point is that MFA strengthens the authentication stage; it does not remove the need for subsequent authorisation and risk evaluation.
MFA should not be treated as a universal “trusted” flag. A user who completed MFA can still present a risky device, an unusual access pattern or a request for a resource they are not authorised to use.
Device Posture Becomes Part of the Decision
Identity alone provides an incomplete picture. A valid identity using an unmanaged or compromised endpoint may represent significantly greater risk than the same identity using a healthy, managed device.
Device posture can therefore become another input to policy. Examples include whether the endpoint is managed, whether security controls are active, whether the operating system meets the required baseline and whether the device has recently generated security alerts.
This creates a more useful decision model: the same user may receive different access depending on the state of the device making the request.
Context Changes the Meaning of an Authentication Event
Context adds another layer of evidence. A login from a normal location during expected working hours may be routine. A login for the same identity from an unusual location followed immediately by access to a sensitive application may require additional verification.
Context can include geographic location, time, network characteristics, application, resource sensitivity and the sequence of actions associated with the session.
The goal is not to block every unusual event. The goal is to use contextual evidence to determine when the normal access decision should change.
Risk-Based Access Decisions
Zero Trust architectures can combine multiple signals into a risk assessment. Risk should be treated as dynamic rather than as a permanent property of an identity.
For example, a user may begin with a normal risk level and receive ordinary access. A later event, such as an impossible-travel indicator, suspicious authentication activity or endpoint security alert, can increase the risk associated with the session.
The resulting policy response does not necessarily have to be an immediate denial. Different levels of risk can trigger different enforcement actions.
| Condition | Potential Risk | Example Response |
|---|---|---|
| Known identity + healthy device + expected context | Low | Allow normal access. |
| Known identity + unfamiliar device | Moderate | Require additional verification or restrict access. |
| Known identity + unusual context | Elevated | Step-up authentication or limit sensitive actions. |
| Identity + suspicious authentication behaviour | High | Restrict access and initiate investigation. |
| Compromise indicators + sensitive resource request | Critical | Deny, revoke session/token and potentially isolate the endpoint. |
Adaptive Authentication
Adaptive authentication allows the authentication experience to respond to context and risk. A low-risk request may proceed normally, while a higher-risk request can require stronger verification.
This creates a more useful model than treating every authentication event identically. The security system can increase friction when evidence indicates elevated risk while avoiding unnecessary interruption for routine activity.
A typical decision sequence might therefore look like:
Least Privilege
Zero Trust also changes how authorisation is designed. Instead of granting broad access because a user belongs to a trusted network or security group, policies should provide only the permissions required for the task.
Least privilege can be applied to users, administrators, service accounts and workloads. Access should be limited by resource, action, scope and duration wherever practical.
Just-in-Time Access
Privileged access can be particularly dangerous when it remains permanently enabled. Just-in-time access reduces exposure by granting elevated privileges only when required and for an appropriate period.
Identity-Driven Segmentation
Segmentation can also move beyond IP addresses and VLAN boundaries. Policies can use identity, application and resource context to determine which services a user or workload can reach.
This does not make traditional network segmentation obsolete. Instead, identity-aware controls add another layer of precision to the segmentation model.
Continuous Verification
Zero Trust is often summarised as “never trust, always verify,” but the useful engineering interpretation is more precise: trust should not be assumed from network location, and access decisions should be capable of changing when relevant evidence changes.
A session that was acceptable five minutes ago may become unacceptable after a new security signal appears. This is why identity telemetry, endpoint telemetry, authentication events and application activity need to feed into the broader security architecture.
Establish the identity associated with the request using an appropriate authentication mechanism.
Combine identity, device, context and available risk signals.
Determine which resource and actions the identity should be permitted to access.
Respond when new evidence changes the risk or policy context of an active session.
Zero Trust Does Not Mean “No Trust”
Zero Trust does not mean that every request must be manually approved. That would be operationally impractical at enterprise scale.
Instead, trust is transformed into a policy-controlled and continuously evaluated decision. Automated systems use identity, device, context and risk signals to determine whether access should be allowed and under what conditions.
This distinction matters because a mature Zero Trust architecture should improve security without creating unnecessary friction. Low-risk activity should remain efficient, while higher-risk activity receives stronger controls.
Identity as the Control Plane
In a distributed SASE architecture, identity increasingly acts as a control-plane signal connecting users, devices, applications and security policy.
The identity layer can provide the context required for access decisions, while SASE enforcement points apply those decisions close to the user or application. This creates a direct relationship between who is requesting access and where and how that access is enforced.
Section 01 established the distributed SASE architecture. Section 02 adds the identity and decision layer. The next engineering question is therefore: once a decision has been made, which security services should actually process the request?
Zero Trust replaces implicit trust based on network location with policy-driven access decisions based on identity, device, context and risk. Authentication establishes identity; authorisation determines access; adaptive controls change enforcement when the evidence changes.
Zero Trust Access Decision Engine
Change the identity, device, context and application conditions. Watch the Zero Trust policy engine calculate risk and determine whether the request should be allowed, stepped up, limited or denied.
Engineering Readout
Zero Trust does not assume that a valid identity automatically represents a trusted session. Identity, device, context and application sensitivity are evaluated together.
Engineering Challenge
What happens when the identity is valid but the device becomes unmanaged and the application is highly sensitive?
SASE Security Service Path
SASE Security Service Path
SASE Security Service Path
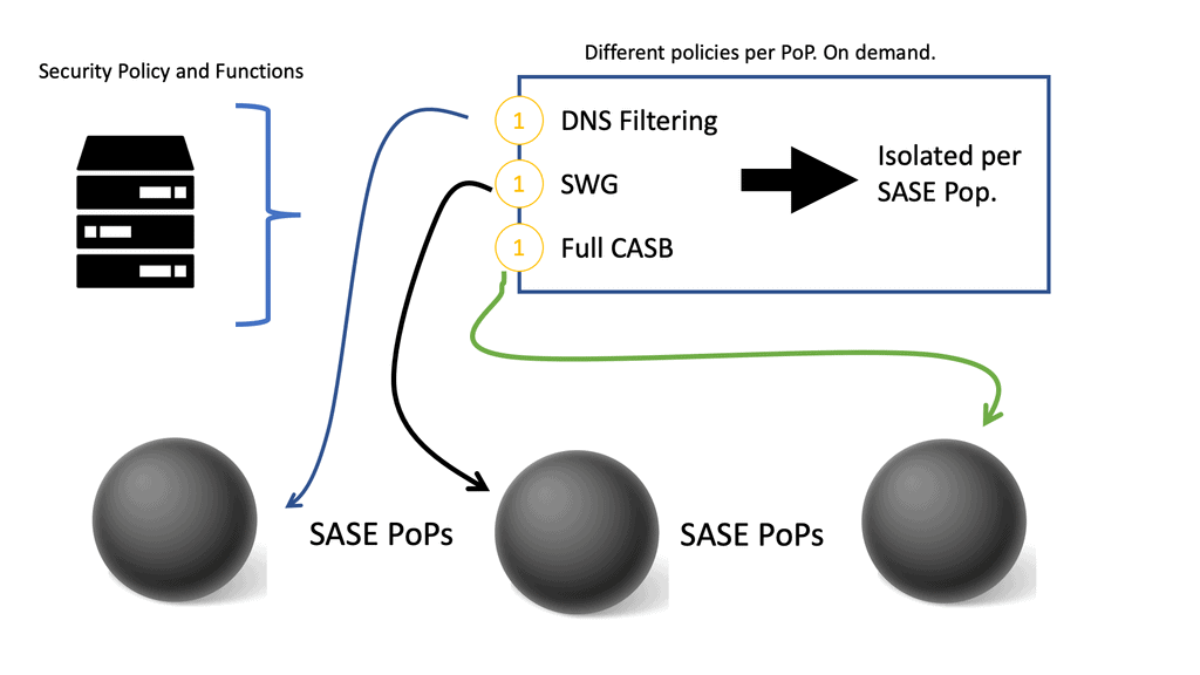
The first two sections established the architecture and the access decision. The next engineering question is what happens to the request after those decisions are made. SASE provides a distributed set of security services that can inspect, control, route and protect traffic according to the requirements of the request.
A SASE service path should not be designed as a mandatory chain where every request passes through every security service. Policy determines which controls are relevant to the identity, device, destination, application, data and risk associated with the request.
From Access Decision to Security Enforcement
Section 02 introduced the Zero Trust decision model: IDENTITY → DEVICE → CONTEXT → RISK → POLICY → DECISION.
Section 03 extends that model into the traffic plane. Once the system understands who is making the request and what the policy allows, the architecture must determine which security services should process the traffic before it reaches its destination.
This diagram represents the available security functions rather than a compulsory sequence. A particular request may use only one or two of these services, while a sensitive transaction may require several controls.
DNS Security
DNS is often one of the first security control points encountered when a user or device attempts to access an Internet destination. DNS security can identify malicious domains, known command-and-control infrastructure, phishing destinations and other categories that policy may prohibit.
Blocking a malicious destination at the DNS layer can prevent the connection from progressing further. This makes DNS an efficient early enforcement point, although it should not be treated as a replacement for deeper traffic and application controls.
Secure Web Gateway
A Secure Web Gateway (SWG) applies security policy to web traffic. Depending on architecture and policy, it can provide URL filtering, malware protection, application controls, acceptable-use enforcement and other inspection capabilities.
The important SASE concept is that the gateway does not have to be a physical appliance located at a central corporate Internet edge. The capability can be delivered through distributed cloud enforcement points closer to the user.
Firewall as a Service
Firewall as a Service (FWaaS) extends firewall policy into a distributed service model. Instead of requiring dedicated firewall appliances at every location, organisations can apply centrally managed policy through cloud-delivered enforcement.
Firewall policy can still control source, destination, protocol, application and other attributes. The architectural difference is that enforcement becomes less dependent on the physical location of a particular appliance.
Cloud Access Security Broker
CASB capabilities address security requirements associated with cloud applications. Cloud services create a visibility challenge because users can access SaaS applications directly from many locations and devices.
CASB controls can help identify cloud applications, apply policy, monitor usage and enforce security requirements around cloud data and application activity.
CASB should therefore be understood as a set of cloud security capabilities rather than simply another network hop that every packet must traverse.
Data Loss Prevention
DLP focuses on protecting sensitive information rather than simply determining whether a destination is safe. The control can evaluate data being uploaded, downloaded, shared or transmitted and compare it against organisational policy.
This becomes particularly important when users interact with SaaS platforms, cloud storage, collaboration systems and other Internet-accessible services.
Network security asks whether traffic should be allowed. Data security asks whether the specific information being transmitted should be allowed to leave its current security boundary.
Zero Trust Network Access
ZTNA provides a different access model for private applications. Instead of placing a user on a broad network and allowing that user to discover reachable resources, ZTNA can provide access to specific applications based on identity and policy.
This creates a significant architectural distinction between network access and application access.
A user may be authorised to access one application without receiving general network-level connectivity to the surrounding infrastructure. This supports least privilege and reduces the attack surface exposed to compromised identities and devices.
Understanding the Security Service Categories
Blocks or redirects access to known malicious or prohibited destinations.
Early destination controlApplies security policy to web and Internet traffic.
Web security enforcementApplies distributed firewall policy to network traffic.
Network policy enforcementProvides visibility and policy controls for cloud applications.
Cloud application controlEvaluates sensitive information against data protection policy.
Data protectionProvides identity-aware access to authorised private applications.
Application access controlNot Every Request Needs Every Service
The most important operational concept in this section is selective enforcement. A SASE architecture should determine which services are relevant rather than automatically forcing all traffic through every available control.
| Request | Likely Relevant Controls | Primary Objective |
|---|---|---|
| Internet | DNS Security, SWG, FWaaS | Protect general Internet access and enforce security policy. |
| SaaS | DNS Security, SWG, CASB, DLP | Control cloud application usage and sensitive data movement. |
| Private App | ZTNA, identity policy, device posture | Provide least-privilege application access. |
| Sensitive Data | DLP, CASB, application controls | Determine whether specific information can be transferred. |
| Malicious DNS | DNS Security | Stop the request before a connection is established. |
Encrypted Traffic Changes the Inspection Model
Modern applications rely heavily on encrypted protocols, particularly TLS. Encryption protects confidentiality, but it also changes how security controls obtain visibility into traffic.
Depending on architecture, policy and legal requirements, security services may use metadata, destination intelligence, endpoint telemetry, application-aware controls or controlled decryption and inspection.
Decryption is therefore not automatically required for every connection. It is an architectural decision that must consider security value, privacy, regulatory requirements, application compatibility and performance.
Security Service Chaining
Security service chaining describes the process of directing traffic through the appropriate sequence of security functions. In a SASE architecture, this can become policy-driven rather than being hard-coded to a physical topology.
For example, an ordinary Internet request may require DNS security and web filtering. A sensitive SaaS transaction may additionally require cloud application and DLP controls. A private application request may instead be directed toward an identity-aware ZTNA service.
Microsegmentation and Application-Level Access
SASE and Zero Trust architectures increasingly move segmentation away from a purely network-centric model. Traditional segmentation often relies on VLANs, subnets, firewall zones and IP addresses.
Identity-aware application access allows policy to become more granular. A user may be permitted to access a particular application without receiving unrestricted access to the network segment hosting that application.
This reduces the amount of infrastructure exposed to a compromised identity and supports the principle of least privilege introduced in Section 02.
Four Common Enforcement Scenarios
DNS intelligence identifies a known malicious destination. The request is blocked before the user establishes the connection.
The identity is valid, but the endpoint fails the required device posture. Policy can restrict or deny access rather than treating authentication as sufficient.
A user requests a private application. ZTNA evaluates identity and policy and exposes only the authorised application rather than broad network access.
A user attempts to upload protected information to a cloud service. DLP and application policy determine whether the transaction should be permitted.
The Enforcement Plane
The SASE enforcement plane is therefore best understood as a collection of specialised security functions controlled by a common policy model. Each service provides a different type of protection, and the architecture determines which combination is appropriate for the request.
This separation is important because it prevents SASE from becoming another rigid perimeter architecture. The security decision follows the request rather than forcing the request through a fixed physical path.
Section 02 determined whether access should be allowed. Section 03 determines which enforcement controls should process that access. The final question is operational: how do we observe these decisions, detect abnormal behaviour and respond when the security model is challenged?
SASE security services form a policy-driven enforcement plane. DNS Security, SWG, FWaaS, CASB, DLP and ZTNA each address different security requirements, but not every request requires every service. The correct architecture selects controls according to identity, device, destination, application, data and risk.
SASE Visibility, Detection & Response
SASE Visibility, Detection & Response
SASE Visibility, Detection & Response
Distributed security changes the operational problem. Once networking, identity and security enforcement are spread across users, endpoints, cloud applications and SASE points of presence, security teams need a unified view of what is happening across those control points. Visibility is therefore not an optional addition to SASE; it is required to operate the architecture effectively.
A security decision is only as useful operationally as the evidence available to explain why it happened, what happened next and whether the risk changed.
From Enforcement to Continuous Telemetry
Sections 01–03 established the SASE architecture, identity decision model and security enforcement plane. Those layers generate a large amount of operational evidence.
Authentication systems generate identity events. Endpoint platforms generate device telemetry. DNS services generate destination queries. SWGs and firewalls generate traffic and policy events. ZTNA systems generate application-access decisions. Cloud applications generate their own audit information.
The challenge is to combine those signals into a coherent operational picture.
What Telemetry Does SASE Generate?
Authentication attempts, MFA events, session changes, privilege activity and identity-risk signals.
Device posture, endpoint alerts, process activity and security-control status.
Domain queries, blocked destinations, threat classifications and unusual lookup behaviour.
Source, destination, application, transport and traffic-volume information.
SaaS activity, private-application access and application-level policy events.
Allow, deny, step-up, restrict and other enforcement outcomes with decision context.
Identity Telemetry
Identity events are particularly valuable because they can connect otherwise separate security observations to a specific user, administrator, service account or workload.
A suspicious DNS request becomes more useful when it can be correlated with the identity that generated it. An unusual application access event becomes more significant when the same identity recently experienced an MFA anomaly.
This is one of the key operational advantages of the SASE and Zero Trust model: security events can be interpreted in the context of identity rather than existing as isolated network events.
Endpoint Telemetry
The endpoint provides another critical source of evidence. A device can transition from healthy to suspicious during an active session, changing the risk associated with requests generated by that device.
Endpoint security alerts, device-management state and posture information can therefore influence access policy. This creates a feedback loop between the endpoint security layer and the SASE enforcement layer.
DNS and Network Behaviour
DNS and network telemetry provide visibility into where devices are attempting to communicate and how those communication patterns change over time.
A single connection may not appear particularly suspicious. A sequence involving unusual DNS queries, new destinations, unexpected application protocols and abnormal traffic volumes may provide much stronger evidence of compromise.
This is why behavioural analysis generally benefits from correlating multiple signals rather than relying on one isolated event.
SIEM and Security Analytics
A Security Information and Event Management (SIEM) platform can aggregate and correlate telemetry from identity systems, endpoints, network controls, cloud applications and SASE services.
The value of centralised analytics is not simply storing more logs. The objective is to identify relationships between events that would otherwise be difficult to see.
| Signal | Individual Meaning | Correlated Meaning |
|---|---|---|
| Login | Identity authenticated successfully. | Potentially normal, depending on context and subsequent activity. |
| MFA Event | Authentication factor was challenged or completed. | Repeated unexpected challenges may indicate credential abuse or attack activity. |
| DNS | Device queried an unusual domain. | More significant when combined with endpoint or identity anomalies. |
| Application | User accessed a resource. | Potentially suspicious when the resource is unusual for that identity or follows other risk events. |
| Endpoint | Security control detected suspicious activity. | Can justify changing the access decision for sessions originating from the device. |
Behavioural Analytics
Behavioural analytics attempts to identify deviations from expected activity. The objective is not to define one permanent baseline for every user, but to understand patterns sufficiently well to identify meaningful anomalies.
Examples include unusual access times, unexpected applications, unfamiliar destinations, abnormal data volumes, repeated authentication failures or access to resources that are inconsistent with normal activity.
Behavioural signals should contribute to risk evaluation rather than automatically becoming proof of compromise. An unusual event can have legitimate explanations, which is why correlation and investigation remain important.
Compromised Identity Detection
One of the most important SASE security scenarios is the compromised identity. An attacker may possess valid credentials, meaning traditional authentication alone may not detect the attack.
Detection therefore depends on identifying changes in behaviour and correlating evidence across multiple systems.
Lateral Movement
Compromised credentials become particularly dangerous when they provide broad access to internal applications and infrastructure. If access controls are based primarily on network location, an attacker who obtains a valid foothold may be able to discover and reach many additional resources.
Identity-aware application access and microsegmentation reduce this exposure by limiting which resources the identity can reach. The goal is not simply to detect lateral movement after it happens, but to reduce the available movement paths in the first place.
Threat Hunting
Threat hunting uses available telemetry to search proactively for suspicious patterns rather than waiting for a single security alert to trigger an investigation.
In a SASE environment, useful hunting questions might include:
Identify users whose application access, authentication or destination patterns differ significantly from their normal activity.
Correlate endpoint alerts and posture changes with active SASE sessions and access requests.
Investigate new domains, unexpected applications and abnormal network destinations.
Look for repeated denies, step-up requests and unusual attempts to reach protected applications or data.
Response and Containment
Detection is only useful if the organisation can respond. SASE and Zero Trust architectures can provide multiple enforcement points where a response can be applied.
| Response | Purpose | Example Trigger |
|---|---|---|
| Monitor | Increase observation without immediately interrupting access. | Low-confidence anomaly. |
| Step-Up | Require stronger authentication before continuing. | Elevated identity or contextual risk. |
| Restrict | Reduce available resources or actions. | Suspicious session with insufficient evidence for full denial. |
| Revoke | Terminate sessions or invalidate tokens. | Strong evidence of identity compromise. |
| Isolate | Limit communication from a compromised endpoint. | Endpoint security confirms active compromise. |
SOAR and Automated Response
Security Orchestration, Automation and Response (SOAR) can connect detection events to predefined response workflows. Automation is particularly useful when the response is well understood and the confidence level is high.
For example, a confirmed compromised identity might trigger token revocation, session termination, privileged-access removal and an incident-management workflow.
Automation should nevertheless be designed carefully. Aggressive automated responses based on weak signals can create operational disruption, lock out legitimate users or hide the original investigation context.
Performance Visibility Is Also Security Visibility
SASE operations are not limited to security events. Network performance can directly influence the user experience and the effectiveness of distributed enforcement.
Latency, packet loss, application response time and path changes can help engineers determine whether a problem originates from the endpoint, local network, Internet path, SASE enforcement point, cloud provider or application.
This is where network-observability capabilities can complement security telemetry. Security and performance teams need enough shared evidence to distinguish a security event from an ordinary application or connectivity problem.
Policy Maintenance
A mature SASE architecture is not finished when the initial policy is deployed. Applications change, users change roles, new threats appear, cloud services are introduced and network conditions evolve.
Policies therefore require continuous review. Security teams should understand which rules are frequently triggered, which rules are never used, where exceptions have accumulated and whether the original business requirement still exists.
The goal is not to create the largest possible policy set. The goal is to create policies that are understandable, measurable, enforceable and aligned with current business requirements.
The Complete SASE Security Loop
The four sections of this guide can now be connected into a single engineering model.
This is the real engineering value of the SASE model. Connectivity, identity, policy enforcement and security operations are no longer isolated layers. They form a continuous control loop in which telemetry can influence future access decisions and enforcement.
What SASE Changes Operationally
| Traditional Model | SASE-Oriented Model |
|---|---|
| Security events are often tied to individual appliances. | Telemetry is correlated across identity, endpoint, network and cloud controls. |
| Network location strongly influences security assumptions. | Identity, context and risk influence access decisions. |
| Incident response often begins after a major alert. | Continuous telemetry supports earlier detection and investigation. |
| Segmentation primarily uses network boundaries. | Identity and application-level controls can reduce reachable resources. |
| Security policy is frequently tied to physical infrastructure. | Policy can be distributed across cloud-delivered enforcement points. |
Engineering the SASE Operating Model
A successful SASE deployment therefore requires more than selecting networking and security products. The organisation must define how identity, device posture, policy, telemetry and response interact across the entire architecture.
Engineers need to understand not only whether a request was allowed or denied, but why the decision was made, which signals influenced it, which security services processed the request and what happened afterwards.
That is what turns SASE from a collection of cloud security services into an operational security architecture.
SASE becomes operationally powerful when identity, endpoint, DNS, network, application and policy telemetry are correlated into a continuous detection and response loop. The architecture should not only enforce access; it should explain decisions, detect changing risk and provide mechanisms to contain compromised identities, devices and sessions.
SASE Incident Investigation
Correlate identity, device, DNS, application and access telemetry to determine whether a session has become suspicious. Investigate the evidence chain, then select the response that best contains the incident.
Engineering Readout
A single authentication event does not prove compromise. SASE operations correlate identity, device, DNS, application and policy telemetry to determine whether behaviour has become suspicious.
Engineering Challenge
Investigate the complete evidence chain. When multiple independent signals indicate compromise, which response prevents the session from continuing to access protected resources?